
cisa news
21 stories
U.S. CISA adds Fortinet FortiMail flaw to its Known Exploited Vulnerabilities catalog
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical Fortinet FortiMail vulnerability, identified as CVE-2026-104286, to its Known Exploited Vulnerabilities (KEV) catalog. The flaw, which carries a CVSS score of 9.8, is a path traversal vulnerability that attackers are reportedly exploiting in the wild.
CISA Adds 5 Exploited Flaws in Artifactory, ScreenConnect, RouterOS to KEV
The Cybersecurity and Infrastructure Security Agency (CISA) has updated its Known Exploited Vulnerabilities (KEV) catalog, adding five new flaws that have been observed under active exploitation. These vulnerabilities impact products from JFrog, ConnectWise, and MikroTik, specifically affecting Artifactory, ScreenConnect, and RouterOS platforms. The inclusion in the KEV catalog mandates that…
CISA Urges Clearer Breach Reporting Amid Rising Cyber Incidents
The Cybersecurity and Infrastructure Security Agency (CISA) has reportedly issued new guidance, signaling a push for enhanced clarity in organizational breach reporting. This advisory indicates a move towards potentially stricter regulations concerning how entities disclose and manage cyber incidents, with a particular focus on improving transparency in incident response and breach…
CISA: WatchGuard RCE flaw now exploited in ransomware attacks
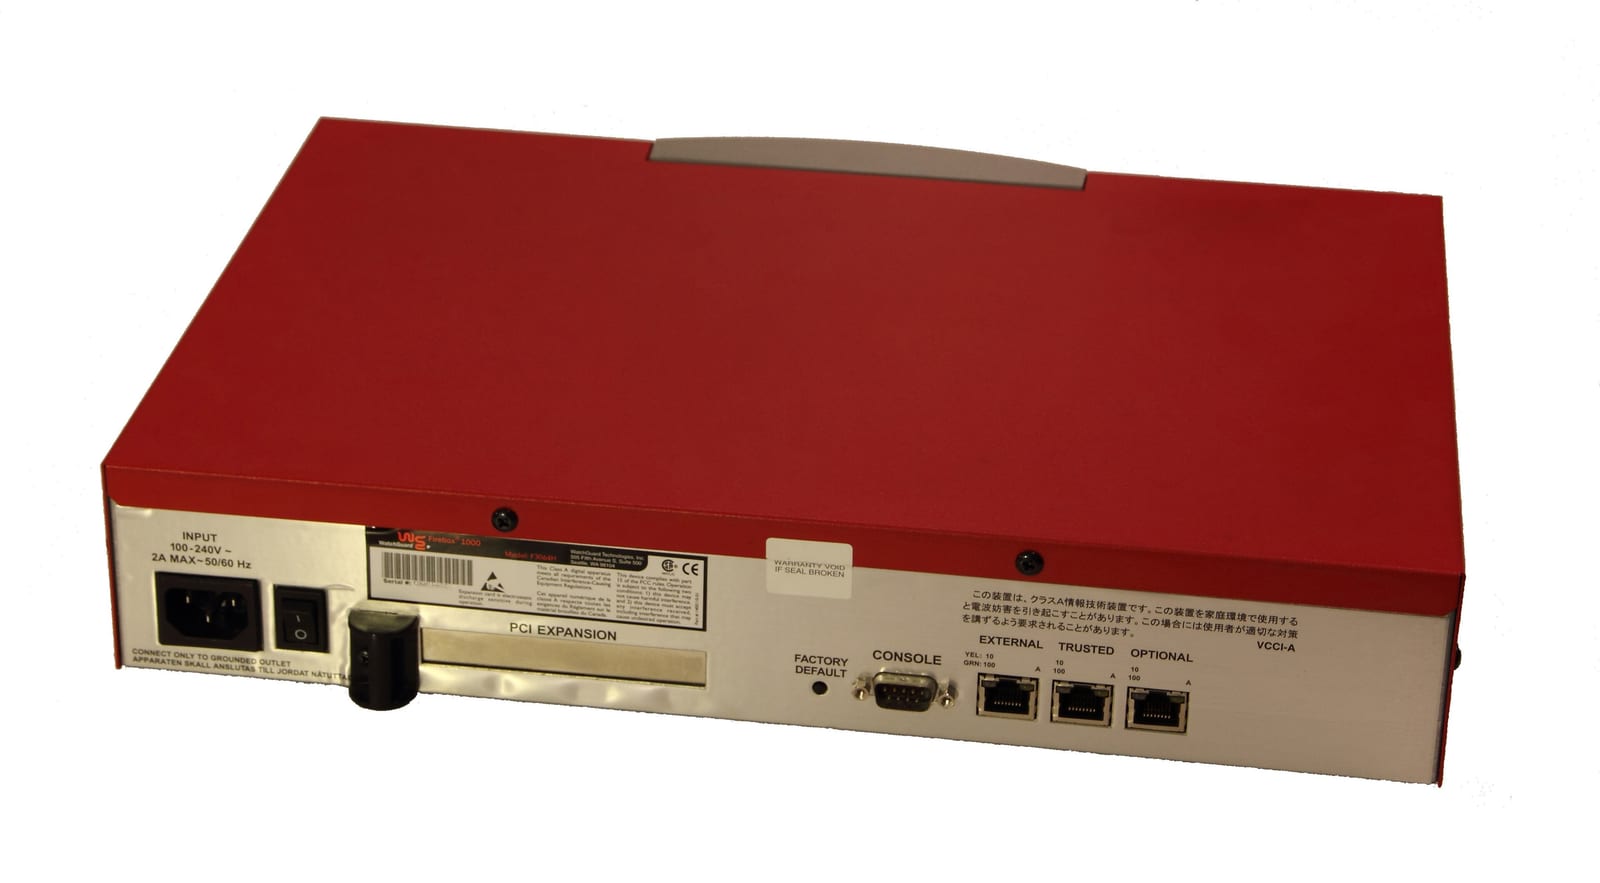
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has confirmed that a critical remote code execution (RCE) vulnerability in WatchGuard Firebox firewalls, tracked as CVE-2025-14733, is now being exploited by ransomware groups. CISA added this flaw to its Known Exploited Vulnerabilities (KEV) catalog in December, at which point it was already being actively exploited.
Microsoft Patches Record 973 Vulnerabilities Amidst Active Exploitation
Microsoft has released patches for an unprecedented 973 vulnerabilities as part of its latest Patch Tuesday update, a new record for the company. Among these, two specific vulnerabilities, identified as CVE-2026-81963 and CVE-2026-85880, are confirmed by the U.S. Cybersecurity and Infrastructure Security Agency (CISA) to be actively exploited in the wild.
Hackers now exploit critical Gitea flaw in code injection attacks
A critical vulnerability in Gitea, a self-hosted Git service, is now being actively exploited by attackers, according to the U.S. Cybersecurity and Infrastructure Security Agency (CISA). The flaw, tracked as CVE-2026-60004, is a code injection vulnerability that allows an authenticated user with repository write access to execute arbitrary shell commands on affected servers.
U.S. CISA adds Zimbra Collaboration Suite (ZCS) flaw to its Known Exploited Vulnerabilities catalog
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical vulnerability in Zimbra Collaboration Suite (ZCS), identified as CVE-2026-73570, to its Known Exploited Vulnerabilities (KEV) catalog. This move mandates that all U.S. federal civilian executive branch (FCEB) agencies address the flaw by August 24, 2026, to protect their networks, and private organizations…
CISA Urges Immediate Patching of Exploited TrueConf Vulnerabilities
The Cybersecurity and Infrastructure Security Agency (CISA) has issued a directive urging organizations to immediately patch critical vulnerabilities found in TrueConf software. This advisory comes as the Head Mare hacktivist group is reportedly actively exploiting these flaws to facilitate the distribution of PhantomCore malware. The directive underscores the urgency for all entities…
U.S. CISA adds an MLflow flaw to its Known Exploited Vulnerabilities catalog
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical server-side request forgery (SSRF) vulnerability in MLflow, tracked as CVE-2026-64849, to its Known Exploited Vulnerabilities (KEV) catalog. This designation indicates that the flaw is actively being exploited in the wild.
U.S. CISA adds Metabase, Windows, and Cisco Secure Firewall flaws to its Known Exploited Vulnerabilities catalog
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added three new vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, mandating federal agencies to address them promptly. The newly cataloged flaws include a critical SQL injection vulnerability in Metabase, a use-after-free flaw in Microsoft Windows' Ancillary Function Driver for WinSock, and a heap…
Ransomware Gangs Exploit SonicWall SMA1000 Vulnerabilities
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has confirmed that ransomware groups are actively exploiting two recently patched vulnerabilities in SonicWall SMA1000 secure remote access gateways. These flaws, identified as CVE-2026-15409 and CVE-2026-15410, include a maximum-severity server-side request forgery (SSRF) vulnerability.
CISA Adds Progress LoadMaster Command Injection Flaw to KEV Catalog
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical vulnerability in Progress LoadMaster products, identified as CVE-2026-8037, to its Known Exploited Vulnerabilities (KEV) catalog. This addition mandates that federal agencies address the flaw by August 10, 2026.
CISA Issues Fresh SBOM Guidance. Did They Get It Right?
The Cybersecurity and Infrastructure Security Agency (CISA) has reportedly issued updated guidance concerning Software Bill of Materials (SBOMs), incorporating roughly two dozen modifications intended to improve their overall comprehensiveness. These revisions are presented as an effort to provide more detailed information within SBOMs. However, some observers have expressed reservations,…
CISA Adds Fortinet and Microsoft Flaws to Exploited Vulnerabilities List
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added three new vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, requiring federal agencies to address them by July 19, 2026. The newly listed flaws include one affecting Microsoft SharePoint and two impacting Fortinet FortiSandbox products.

Attackers using Langflow flaw for credential harvesting (CVE-2026-55255)
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical vulnerability in the Langflow AI framework to its Known Exploited Vulnerabilities catalog. This flaw, identified as CVE-2026-55255, has been observed being actively exploited in the wild by threat actors.
CISA orders feds to prioritize patching Langflow auth bypass flaw
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has mandated that federal agencies prioritize patching a critical authentication bypass vulnerability affecting the Langflow visual framework. The directive, issued as Binding Operational Directive (BOD) 26-04, requires agencies to secure their systems by Friday.
U.S. CISA adds Adobe ColdFusion, Joomlack Page Builder, Langflow, and JoomShaper SP Page Builder flaws to its Known Exploited Vulnerabilities catalog
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added four vulnerabilities affecting Adobe ColdFusion, Joomlack Page Builder, Langflow, and JoomShaper SP Page Builder to its Known Exploited Vulnerabilities (KEV) catalog. This directive mandates that federal agencies patch these vulnerabilities by July 10, 2026, to mitigate risks from active exploitation. Private…
CISA Deploys Anthropic’s Mythos AI to Hunt Vulnerabilities in U.S. Government Code
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) is utilizing Anthropic's advanced artificial intelligence model, Mythos, to proactively identify vulnerabilities within federal government code. This initiative aims to detect and address security weaknesses before they can be exploited by malicious actors, including foreign intelligence services and cybercriminal organizations.
CISA orders feds to patch max severity ColdFusion flaw by Friday
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has mandated that federal agencies patch a critical vulnerability in Adobe ColdFusion by Friday. This directive, issued under Binding Operational Directive 26-04, targets a flaw designated CVE-2026-48282, which is actively being exploited by malicious actors.
CISA Adds 4 Actively Exploited Adobe, Joomla, and Langflow Flaws to KEV
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added four vulnerabilities to its catalog of Known Exploited Vulnerabilities (KEV). These newly identified weaknesses, which affect products from Adobe, Joomla, and Langflow, are reportedly being actively exploited in the wild.
CISA Reportedly Using Anthropic’s Mythos to Scan Government Software for Flaws
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) is reportedly employing artificial intelligence to enhance its security reviews of government software. Specifically, the agency is said to be utilizing Anthropic's Mythos AI tool for the purpose of scanning software for vulnerabilities.