
cloud news
289 stories · page 1 of 7Rackspace Spot breach let hackers access customer Kubernetes secrets
Rackspace has confirmed a security breach affecting its Rackspace Spot cloud platform, a service designed for managing containerized applications through Kubernetes. The unauthorized access occurred on November 17, 2026, spanning a window from approximately 00:20 to 22:00 UTC. The company discovered the intrusion on November 18 following a report from a customer and subsequently verified that…
U.S. CISA adds Cisco Expressway, SAP NetWeaver, Broadcom VMware vCenter, and Apache Roller flaws to its Known Exploited Vulnerabilities catalog
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has updated its Known Exploited Vulnerabilities (KEV) catalog to include four distinct security flaws. These additions, confirmed by the agency to be under active exploitation, include vulnerabilities affecting Cisco Expressway, SAP NetWeaver, Broadcom VMware vCenter, and Apache Roller. Under Binding Operational Directive 22-01,…
Hackers Exploit Critical VMware, Cisco, and Apache Flaws as Espionage Attacks Emerge
The Cybersecurity and Infrastructure Security Agency (CISA) has added four critical vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, confirming that threat actors are actively leveraging these flaws in ongoing espionage campaigns. The affected products include Apache Roller, Cisco Expressway, SAP NetWeaver, and Broadcom VMware vCenter. Among the entries is a high-severity…

CVE-2026-23871: WhatsApp Bug Helped Scammers Make Messages Look Legitimate
WhatsApp has released security updates addressing three vulnerabilities, one of which was actively exploited in a scam campaign designed to increase the perceived legitimacy of fraudulent messages. The company identified this specific flaw, tracked as CVE-2026-23871, while investigating and disrupting an ongoing fraud operation.

Dialing for Data: Inside the Com’s High-Profile Heists
Security researchers have identified a persistent and evolving campaign of vishing-led cyberattacks targeting data-intensive industries across the United States, the United Kingdom, and Australia. Since August 2026, a network of threat actors associated with the Com collective has conducted a series of data theft and extortion operations. These attacks primarily target the financial,…
US companies’ use of Chinese open weight AI draws rebuke from House chairmen
A joint investigation by the House Homeland Security Committee and the Select Committee on the Chinese Communist Party has issued a stern warning regarding the integration of Chinese-developed open-weight artificial intelligence models into American corporate infrastructure. The 50-page report identifies a growing trend among both Fortune 500 companies and Silicon Valley startups to utilize…
How Cloudflare WAF protects against ruby2shell (CVE-2026-132825)
Cloudflare has officially confirmed the deployment of protective measures against a critical vulnerability identified as CVE-2026-132825, colloquially referred to by the security community as ruby2shell. This vulnerability concerns a remote code execution flaw that targets web applications built on the Ruby programming language. By exploiting specific weaknesses in how certain Ruby-based…
How Cloudflare WAF helps protect against phpAfterShell and other critical PHP flaws
Cloudflare has recently highlighted the role of its Web Application Firewall (WAF) in mitigating risks associated with critical vulnerabilities in PHP-based environments, specifically citing the threat posed by tools like phpAfterShell. These types of exploits target the ubiquity of PHP in web development, leveraging common weaknesses to gain unauthorized access to server environments. By…
Linux KVM Flaw CVE-2026-99312 Lets Guest VMs Access Host Memory on AMD Hosts
A critical security vulnerability, tracked as CVE-2026-99312, has been identified in the Linux Kernel Virtual Machine (KVM) hypervisor. The flaw allows a guest virtual machine to bypass isolation boundaries and access memory belonging to the host system. Researchers demonstrated the exploit by successfully reading approximately 127 GB of memory from a cloud server while operating from within…
N-able Blames Service Disruption on Cyberattack
N-able has confirmed that a recent multi-day service disruption affecting its Mail Assure and SpamExperts Hosted Cloud products was the result of a targeted cyberattack. The outage, which began on November 16, 2026, initially prompted the company to cite a combination of platform configuration issues and service dependencies as the cause. However, on November 18, the firm officially…
nginx2root: Five new nginx vulnerabilities, and how Cloudflare protects origins from the worst of them
Five new vulnerabilities affecting the NGINX web server have been identified, prompting security teams to emphasize the importance of origin protection and timely patching. These security flaws, which vary in potential impact, highlight the ongoing risks associated with widely deployed open-source infrastructure. While the specific details of the vulnerabilities are being analyzed by the…
CVE-2026-123890: Critical Authentication Bypass in VMware vCenter
Broadcom has issued an emergency security advisory, VMSA-2026-0009, to address a critical authentication bypass vulnerability identified as CVE-2026-123890. The flaw resides within the VMware Directory Service component of vCenter Server and carries a CVSSv3 severity score of 9.8. By exploiting this vulnerability, an attacker with network access to a target vCenter deployment can bypass…
PHP Releases Patches to Fix 18 Vulnerabilities
The PHP Foundation has released security updates addressing 18 distinct vulnerabilities across multiple supported versions of the language. This batch of patches, released on November 19, 2026, follows a period of heightened security activity for the platform, occurring only one month after the disclosure of two critical flaws collectively referred to as PHP2Shell. While these newly disclosed…
Credential stealer slipped into Microsoft’s official Python agent framework
Two malicious versions of Microsoft’s official agent-framework package were uploaded to the Python Package Index (PyPI) on November 17, 2026, exposing developers to a sophisticated credential-stealing campaign. The affected releases, versions 1.26.1 and 1.26.2, were identified by researchers at StepSecurity, OX Security, and Socket. These versions were designed to execute a malicious payload…
Chrome patches six Critical flaws, two found with AI’s help
Google has released a comprehensive security update for the Chrome browser, addressing a total of 204 vulnerabilities across its desktop and mobile platforms. The patches, which began rolling out on November 17, cover critical memory-safety issues that could potentially allow for arbitrary code execution. Users are encouraged to update their software immediately to mitigate these risks, as the…
AI agents inherit employee access, and nobody’s watching how they use it
A new report from Nudge Security highlights a growing security blind spot as artificial intelligence agents become deeply embedded in corporate workflows. These agents, which are increasingly being built within project management software, customer relationship management (CRM) systems, and automation platforms, often operate using the credentials of the employees who created them. This…
PHP Warns of Critical Security Flaws Affecting All Supported Versions, Fixes Coming November 19
The maintainers of the PHP programming language have issued a security advisory warning of critical vulnerabilities affecting all currently supported versions of the software. The project has scheduled a coordinated release of patches for November 19, 2026, with the updates expected to be published between 2:00 p.m. and 2:30 p.m. UTC.
Palo Alto Networks to Buy AI Startup Applied Compute for $4.5 Billion
Palo Alto Networks has entered into a definitive agreement to acquire the artificial intelligence infrastructure startup Applied Compute for $4.5 billion. The transaction, which is structured as an all-stock deal, is currently subject to standard closing conditions and regulatory approvals. The company anticipates the acquisition will conclude during its fiscal third quarter of 2027.
NGINX2Root: Five nginx Flaws, Led by CVE-2026-123007. How to Find, Mitigate, and Patch Now
A collection of five security vulnerabilities, collectively dubbed NGINX2Root, was disclosed on November 18, 2026, affecting various versions of NGINX Open Source and NGINX Plus. The most severe of these, CVE-2026-123007, is a memory corruption flaw within the server’s HTTP/2 implementation. F5, the maintainer of NGINX, has assigned this lead vulnerability a CVSS v4.0 score of 9.2.
Azure Linux 4 puts the OS behind Microsoft’s cloud services on your VMs at no extra license fee
Microsoft has officially launched Azure Linux 4, making its internal, cloud-native operating system available for general use on customer virtual machines and scale sets. Previously utilized exclusively to power the infrastructure behind Microsoft’s own cloud services, including Azure Kubernetes Service, App Service, and Azure Cosmos DB, the distribution is now accessible to the public. The…
TapMap: Free, open-source network map
TapMap, a newly released open-source desktop application, provides users with a visual method to monitor active network connections by plotting them on an interactive world map. The tool functions by scanning a user's open sockets, extracting remote IP addresses, and cross-referencing them against a local GeoIP database. Once processed, the application displays these connections within a…
Cloud keys leaked in Docker Hub images are stolen within seconds
Researchers from Stony Brook University have demonstrated that sensitive cloud credentials and API keys inadvertently included in public Docker Hub images are being harvested by automated scanners within seconds of being published. Billy Tsouvalas and Nick Nikiforakis conducted a four-month study involving 300 honeypot images across eight public container registries. By planting decoy…
AI Framework Autonomously Weaponized Flaws in Real Attacks, Google Says
Google’s Threat Intelligence Group has identified a significant evolution in cyber warfare, confirming that threat actors are now deploying multi-agent artificial intelligence frameworks to conduct autonomous, machine-speed intrusions. For the first time, researchers have observed a framework, dubbed exploit_agent, capable of independently discovering vulnerabilities, developing exploits, and…
Anthropic Cuts Disclosure Deadline to 30 Days For Serious Bugs
Anthropic has announced a significant shift in its vulnerability disclosure policy, reducing the time frame vendors are granted to address security flaws before the company makes them public. Effective January 1, 2027, the company’s Frontier Red Team will enforce a 30-day disclosure deadline for vulnerabilities classified as high or critical severity. This update represents a substantial…
Microsoft gives admins one policy to manage Windows patches and fixes for PCs that won’t boot
Microsoft has introduced a unified policy management feature within the Windows Autopatch service, designed to streamline how administrators handle quality updates, .NET Framework updates, and critical system recovery fixes. This update, integrated directly into the Microsoft Intune admin center, allows IT teams to manage these distinct update categories through a single administrative…
40% of organizations struggle to retrace AI agents’ actions
A significant portion of modern enterprises is struggling to maintain oversight of autonomous systems, with 40% of organizations reporting an inability to retrace the actions taken by AI agents within their environments. This visibility gap is particularly pronounced in the financial sector, where 46% of firms report difficulty reconstructing agent activity. The challenge is largely attributed…
N-able Patches 17 N-central Flaws as Attackers Exploit Earlier Bugs to Deploy Crypto Miners
N-able has released a critical security update for its N-central platform, addressing 17 distinct vulnerabilities. The release, designated as N-central 2026.4 Hotfix 3, follows reports that attackers are actively exploiting previously identified flaws within the Remote Monitoring and Management and Unified Endpoint Management software to deploy unauthorized cryptocurrency mining operations.
AI Cuts Vulnerability Discovery from Nine Months to 90 Hours
Forescout Technologies has released findings demonstrating that artificial intelligence can drastically reduce the time required to identify software vulnerabilities. In a report titled Finding Critical Infrastructure Bugs with Off-the-Shelf AI, the company detailed how it utilized publicly available AI models to scan 10 popular TCP/IP stacks. By employing a custom AI-assisted research…
AI uncovers flaws in discontinued devices with no vendor left to patch them
Security researchers at Forescout have demonstrated that artificial intelligence can significantly lower the barrier to entry for discovering vulnerabilities in embedded software. By leveraging AI models alongside traditional security scanning tools, the team identified 99 vulnerabilities across 10 different TCP/IP stacks, which are essential components for network communication in industrial,…
The Microsoft Outage Left 15 Hotel Guests Poisoned by Chlorine
A recent cloud service disruption at Microsoft has been linked to a safety incident at the Hotel Ling Bao in Phantasialand, Germany, where 15 guests suffered from chlorine poisoning. The incident, which occurred during a global Microsoft 365 outage spanning November 12 to 14, 2026, highlights the risks associated with relying on cloud-based email systems for critical industrial safety monitoring.
TSMC employee data breach linked to cloud provider
Taiwan Semiconductor Manufacturing Company (TSMC) has confirmed that personal information belonging to its current and former employees has been exposed online. The breach came to light after a threat actor began auctioning a 6.9GB dataset, which they claimed contained 46,000 individual records. The company, which serves as the world’s largest contract chipmaker for major technology firms like…
U.S. CISA adds Check Point and UnrealIRCd flaws to its Known Exploited Vulnerabilities catalog
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has officially added two high-severity vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence that both are being actively leveraged in malicious campaigns. Federal Civilian Executive Branch agencies are required to remediate these flaws by November 16, 2026, in accordance with Binding Operational…
Kitesurf is now open source
The browser automation tool Kitesurf has officially transitioned to an open-source model. This shift allows developers and security researchers to access, inspect, and modify the underlying codebase, which was previously proprietary. By moving to an open-source framework, the project aims to foster community-driven development and increase transparency regarding how the browser-based…
Adapting to AI penetration testing orchestrators: The Modern Security Model
The integration of artificial intelligence into penetration testing workflows has emerged as a significant shift in the modern cybersecurity landscape, moving beyond manual assessment toward automated, orchestrator-driven security models. This evolution is characterized by the deployment of AI-based agents capable of executing complex security tasks, such as vulnerability scanning, threat…
PostgreSQL Patches 52 Flaws, Including 22-Year-Old Bug Enabling Authenticated RCE
PostgreSQL has released security updates addressing 52 vulnerabilities, most notably a critical type confusion flaw that has persisted in the codebase for 22 years. Tracked as CVE-2026-6460, this vulnerability carries a CVSS score of 8.8 and allows an authenticated user with the ability to create database objects to execute arbitrary code on the underlying server. Because the database process…
MDR Pricing: Comparing Asset-Based and Ingestion-Based Costs
Security leaders evaluating Managed Detection and Response (MDR) services often face a complex choice between two primary pricing models: asset-based and ingestion-based. While both approaches aim to provide security monitoring, they rely on fundamentally different metrics that can significantly alter the scope of protection, data visibility, and long-term costs. A direct comparison requires…
German parliament passes law giving spy agencies hacking, sabotage powers
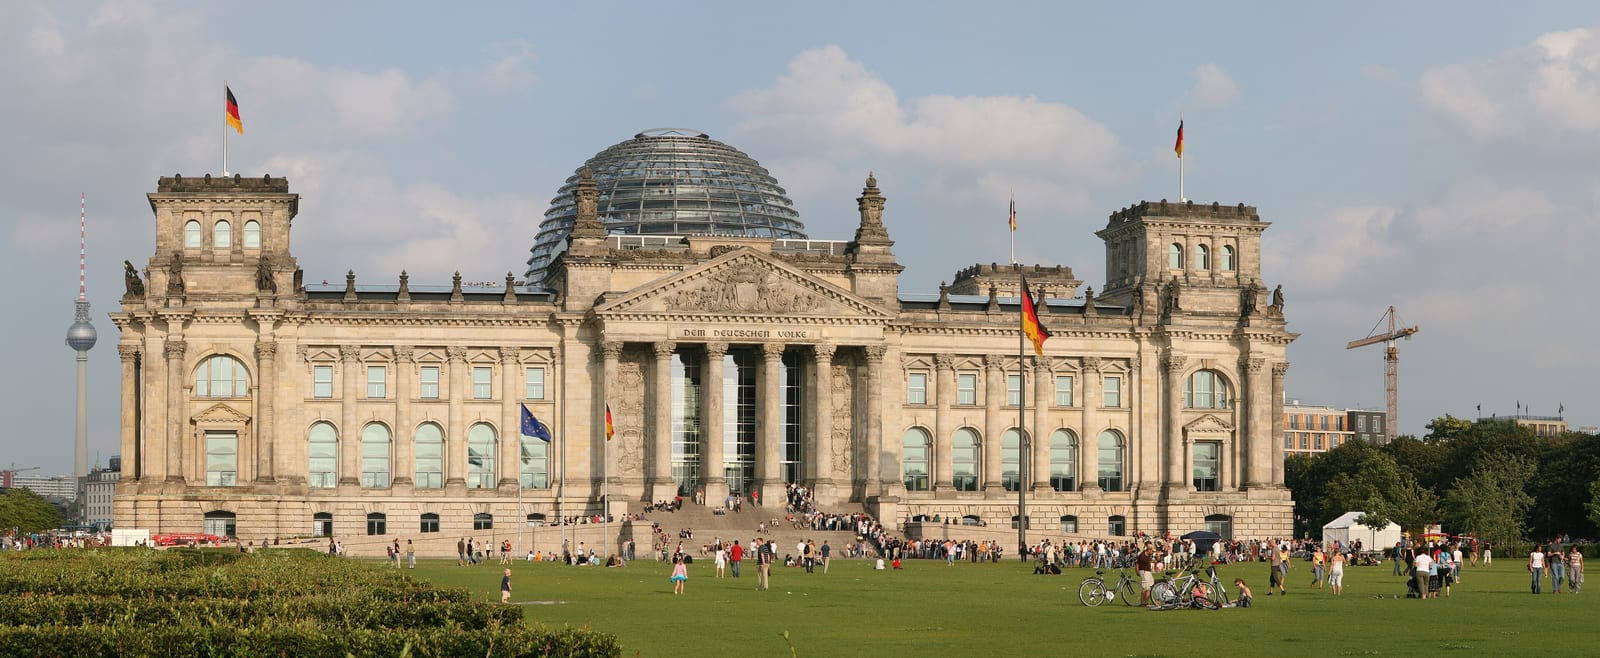
The German Bundestag has passed significant legislation that grants the country’s intelligence agencies expanded authority to conduct cyber operations, including hacking and supply chain sabotage. Approved by a vote of 308 to 190, the bill represents the most substantial reform of German intelligence laws in the postwar era. The legislation empowers the Federal Intelligence Service (BND) to…
56 AWS API calls in 141 milliseconds: Inside an AI-run intrusion
A sophisticated intrusion campaign leveraging the CyberStrikeAI platform has been identified targeting Amazon Web Services (AWS) environments. Between September 30 and October 16, 2026, an attacker utilized a single server to navigate four distinct AWS accounts, employing eight separate identities to execute a series of malicious actions. The campaign is notable for its use of machine-speed…
TSMC confirms employee data breach tied to cloud service provider
Taiwan Semiconductor Manufacturing Company (TSMC) has officially confirmed that a data breach involving one of its third-party cloud service providers resulted in the unauthorized access of sensitive information belonging to its current and former employees. The semiconductor giant disclosed the incident in a formal filing with the Securities and Exchange Commission on Thursday, clarifying…
FBI Says North Korean Hackers Stole Over $400 Million in Crypto Using Deepfake Video Calls
The Federal Bureau of Investigation has reported that threat actors linked to the Democratic People's Republic of Korea are responsible for the theft of more than $400 million in cryptocurrency. The illicit activity, identified by the government as part of a social engineering campaign codenamed FaceStealer, has occurred over the last 18 months. These findings were released alongside a…
Ransomware attack on Belarusian cloud firm disrupts businesses for days
ActiveCloud, a prominent Belarusian provider of cloud hosting and IT infrastructure services, confirmed it was the target of a ransomware attack earlier this week. The breach resulted in significant operational disruptions, rendering corporate websites, email systems, and virtual server environments inaccessible for a wide range of businesses across Belarus and Russia. The company first…
Introducing Spend Management: Spending limits and alerts for Cloudflare
Cloudflare has officially introduced a new spend management feature designed to provide customers with greater oversight and control over their platform expenditures. This update allows users to establish specific spending limits and configure automated alerts, addressing a long-standing need for more granular financial governance within cloud infrastructure environments.
AI Doesn’t Have to Go Rogue to Break the World
The rapid advancement of artificial intelligence has introduced a new category of systemic risk that extends far beyond traditional cybersecurity concerns. While public discourse often focuses on the potential for AI to be weaponized by malicious actors or to act with sentient malice, the more immediate and destabilizing threat lies in the autonomous discovery of exploits within complex…
Google pushes second Chrome update this week
Google has released a significant security update for the Chrome browser on Windows, Mac, and Linux, marking the second such release within a single week. This update advances the browser to version 157.0.8103.78 for Linux and versions 157.0.8103.78 and 157.0.8103.79 for Windows and Mac users. The patch addresses a total of 83 security vulnerabilities, five of which have been categorized as…
Hackers Exploit N-central Flaws to Infect 21 Servers, Including 19 Running Hotfix 2
N-able has confirmed that attackers are actively exploiting vulnerabilities within its N-central remote monitoring and management platform. The incident has resulted in the compromise of 21 servers, with 19 of those systems running the platform’s second hotfix. In response to the breach, the vendor has begun restricting specific features and integrations to prevent further exploitation while…
Self-hosted Claude Managed Agents keeps agent credentials in your environment
Anthropic has introduced a self-hosted deployment option for its Claude Managed Agents platform, allowing enterprise customers to bring the agent harness, sandboxes, session history, and credential management within their own cloud or on-premise infrastructure. Previously, while customers could host the isolated sandbox environments where agent code executes, Anthropic maintained control over…
Google Cloud Warns Three AMD Turin CPU Flaws Could Leak Data Across Processes in VMs
Google Cloud has issued a security advisory regarding three side-channel vulnerabilities identified in AMD Turin processors. These flaws present a risk of unauthorized data exposure across processes running within the same virtual machine (VM). While Google has already implemented infrastructure-level mitigations to prevent cross-VM and VM-to-host data leakage, users are now required to take…
AWS Emulator: Open-source tool for testing AWS apps locally, built by autonomous AI agents
Amazon Web Services has introduced AWS Emulator, an open-source tool designed to allow developers to simulate various cloud services directly on local machines, development servers, or within continuous integration pipelines. A notable aspect of this release is the company’s assertion that the entire codebase was generated and maintained by autonomous AI agents without human intervention in…