
malware news
268 stories · page 1 of 6
BADBOX 3.0 botnet returns with record-breaking 40 billion daily ad requests
The BADBOX botnet has re-emerged in a third iteration, reaching unprecedented levels of activity by generating approximately 40 billion fraudulent advertising bid requests every day. Researchers at HUMAN, who identified and worked to disrupt this latest variant, report that BADBOX 3.0 now stands as the largest ad-fraud operation documented by daily volume. This surge in activity accounts for…
Fake GTA VI Streaming Client Installs Data-Stealing Malware on Windows PCs
Security researchers at Bitdefender have issued an alert regarding a malicious campaign that leverages the high anticipation for the upcoming Grand Theft Auto VI title to distribute data-stealing malware. The campaign targets Windows gamers by enticing them to download a fake streaming client that purports to provide early access to the game. Once executed, the software functions as a vehicle…
Bazuka Android Malware Uses Fake Screen Overlays to Hide Credential Theft and Device Control
Security researchers have identified a new Android malware framework dubbed Bazuka, which leverages sophisticated screen overlay techniques to facilitate credential theft and unauthorized device control. Discovered by mobile security firm ThreatFabric during an investigation into NFC-relay banking Trojans, the malware is notable for its integration of large language model (LLM) capabilities to…
Fake GTA VI PC client spreads malware through a ClickFix attack
Researchers have uncovered a malicious campaign leveraging the high anticipation for Grand Theft Auto VI to distribute information-stealing malware. The attackers are utilizing a technique known as a ClickFix attack, which relies on social engineering to trick victims into manually executing a harmful PowerShell command rather than exploiting a software vulnerability. Because Rockstar Games…
In Other News: Norwegian Energy Firm Cyberattacks, Supercomputer Hack, New Nightmare Eclipse Exploit
The cybersecurity landscape saw a surge in activity this week, characterized by significant data breaches at major financial and technology firms, targeted attacks on critical infrastructure, and the emergence of new zero-day vulnerabilities.
Suspected North Korea-Aligned Group Hides C2 on Solana Blockchain
Security researchers have identified a campaign by a financially motivated threat actor that leverages the Solana blockchain to facilitate command-and-control (C2) communications. The group, tracked as UAT-12643, utilizes a Go-based remote access trojan (RAT) known as Overlord to maintain persistence on infected Windows systems and exfiltrate sensitive data.

Microsoft's official Python agent framework hijacked to distribute malware
Microsoft has confirmed that its official Python agent-framework package was compromised, leading to the distribution of malicious code through the Python Package Index (PyPI). The incident involved the unauthorized upload of versions 1.26.1 and 1.26.2, which were pushed to the repository using Microsoft’s official publisher account. Security researchers identified the breach, noting that the…
BubbleLoader malware turns copies of WinRAR and Windows Media Player into carriers
Security researchers at ReversingLabs have identified a sophisticated malware loader dubbed BubbleLoader that compromises legitimate Windows software to deliver secondary malicious payloads. By modifying the entry points of well-known applications, the loader turns otherwise benign programs into vehicles for executing hidden code. Confirmed hosts for this malware include WinRAR, Windows Media…
Attackers Used Optimizely to A/B Test Malware on Top Websites
On November 16, 2026, a significant supply chain attack compromised the Optimizely experimentation platform, allowing unauthorized parties to inject malicious JavaScript into the websites of at least 178 major organizations. The breach enabled attackers to serve malicious payloads directly to visitors of high-traffic destinations, including CNN, the BBC, Equifax, Ledger, and Zoom. Because…
Japan takes Fugaku supercomputer offlline after cyberattack
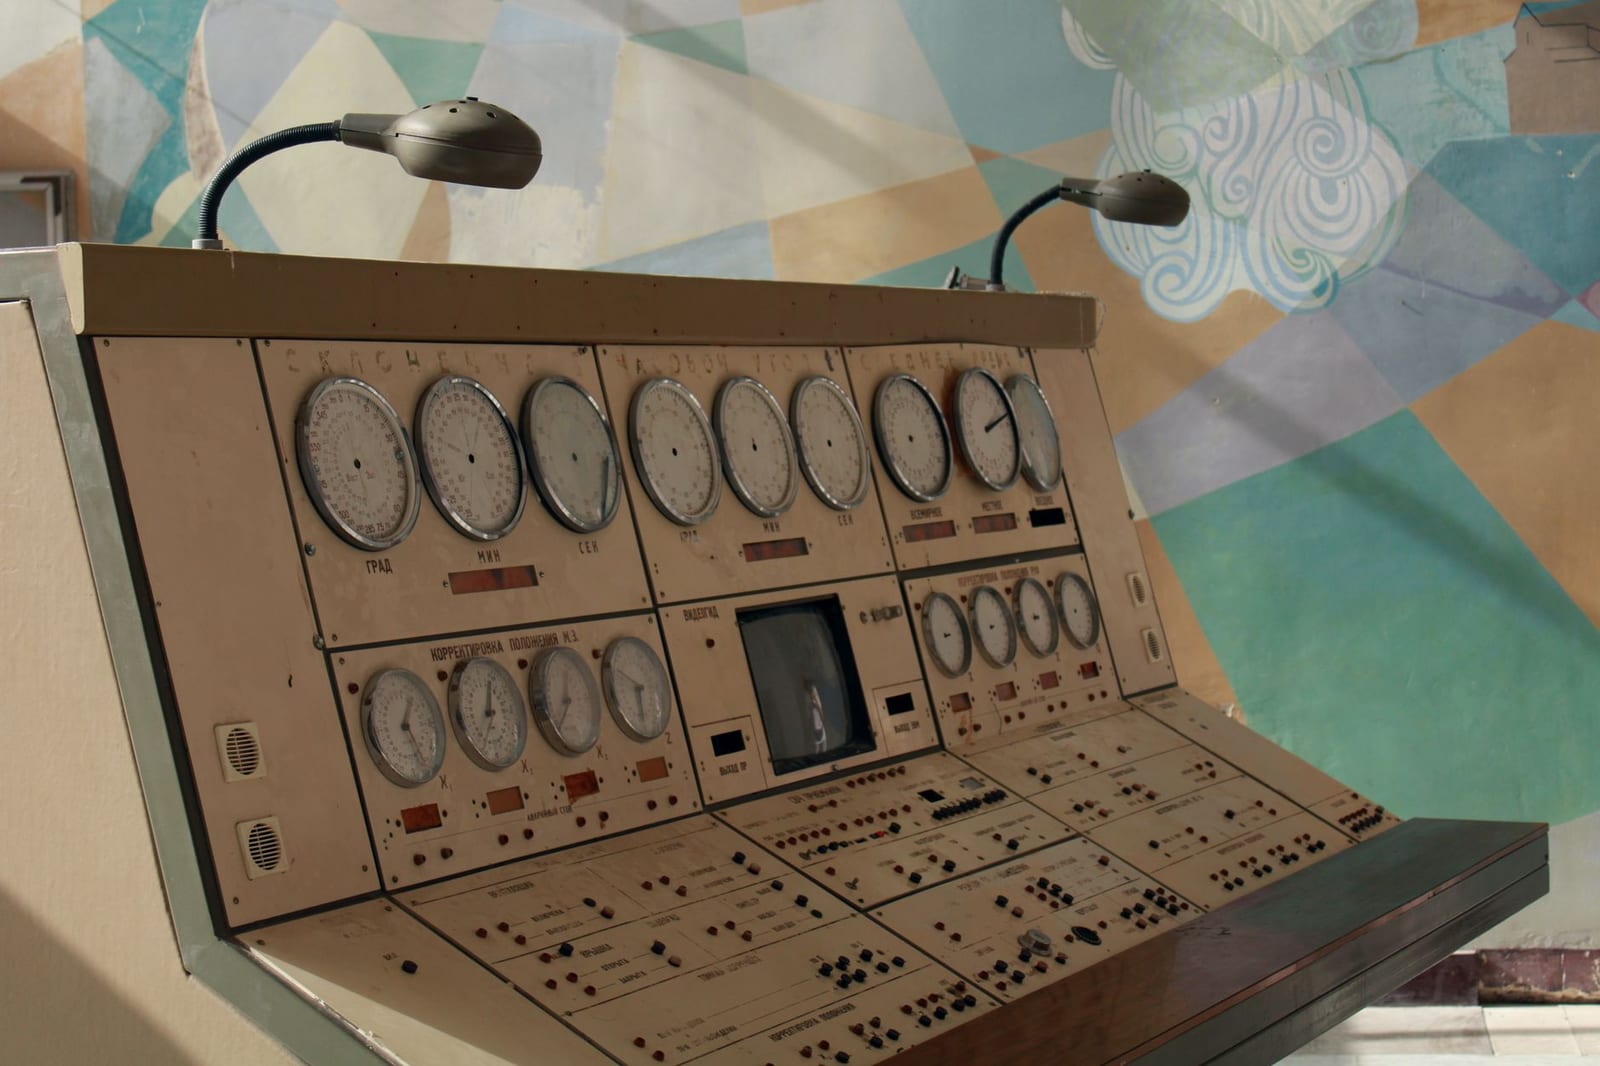
The RIKEN Center for Computational Science in Japan has suspended operations of the Fugaku supercomputer following the discovery of a significant security breach. The facility, which manages both the 537-petaflops Fugaku system and the 64-petaflops Rikyu supercomputer, initiated a shutdown on November 14 after identifying unauthorized activity within its network.
Optimizely supply chain attack infects major brands' sites with malware
A significant supply chain attack has compromised the digital experience platform Optimizely, resulting in the injection of malicious JavaScript into the websites of numerous high-profile organizations. By embedding unauthorized code into customer projects, attackers successfully leveraged Optimizely’s content delivery network to distribute malware to visitors of major sites, including Zoom,…
ArcticRAT Android Malware Uses Grok AI to Analyse Stolen Banking Texts
ArcticRAT, a recently identified strain of Android malware, has been observed leveraging Grok AI to automate the analysis of stolen banking communications. The malware is designed to gain unauthorized access to an infected device, where it systematically inspects installed applications and monitors incoming SMS alerts to extract sensitive financial information.
SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 123
The cybersecurity landscape has faced a surge in significant incidents over the past week, ranging from large-scale data breaches to coordinated international law enforcement operations against malware infrastructure. Among the most notable developments is a massive data breach at Maileva, a subsidiary of the French postal service La Poste, which reportedly exposed the personal information of…
Stolen Fireworks AI Key Led to Cursor Data Breach and Trojanized Claude Code Extension
The compromise of the official Claude Code extension hosted on the Cursor marketplace has been traced back to the theft of an access key originating from a security incident at Fireworks AI. According to a recent update from Cursor, an unauthorized actor obtained an access key that had been issued to Fireworks AI. This key, which was exposed following a breach at the third-party provider,…
SCKit abuses ScreenConnect to deploy remote access and target technician sessions
A sophisticated threat actor is actively exploiting ConnectWise ScreenConnect instances to deploy a malicious toolkit identified as SCKit. This campaign specifically targets managed service providers (MSPs) by compromising endpoints and utilizing a component known as RelayTrap to infect the workstations of IT support technicians. By compromising these high-privilege accounts, the attackers…
Check Point gateways hacked via PHP2Shell to deploy VMware ESXi wiper
Check Point has confirmed that its Security Gateway products were targeted in a sophisticated campaign involving the exploitation of critical vulnerabilities to deploy data-wiping malware on VMware ESXi hosts. The attacks, which began on October 30, utilized a chain of exploits to gain initial access, escalate privileges, and move laterally through corporate networks. The campaign was…
DOJ: Gootloader used in at least 44 ransomware attacks costing $29 million since 2018
The United States Department of Justice has disclosed the results of a major international law enforcement operation aimed at dismantling the infrastructure supporting Gootloader, a persistent malware strain that has facilitated widespread cyberattacks since 2018. According to federal officials, the operation successfully removed Gootloader from more than 100 compromised servers and seized…
Fake GTA 6 download goes after Steam logins and crypto wallet data
Cybersecurity researchers at Cynet have identified a sophisticated malware campaign leveraging the high anticipation surrounding the upcoming release of Grand Theft Auto VI. With the game officially scheduled for a November 19 launch exclusively on consoles, any claims of a PC version or early access build are fraudulent. Attackers are exploiting this gap in availability by hosting malicious…
Gootloader Malware Disrupted After Infecting 25,000 Computers
A coordinated international law enforcement operation has successfully disrupted the Gootloader malware infrastructure, resulting in the seizure of multiple U.S. domain names and the removal of malicious software from more than 100 computer servers. The initiative, which was conducted under court authorization, targeted a botnet that has been active since 2018 and is estimated to have…
Quantum Systems drones back in the air after malware scare
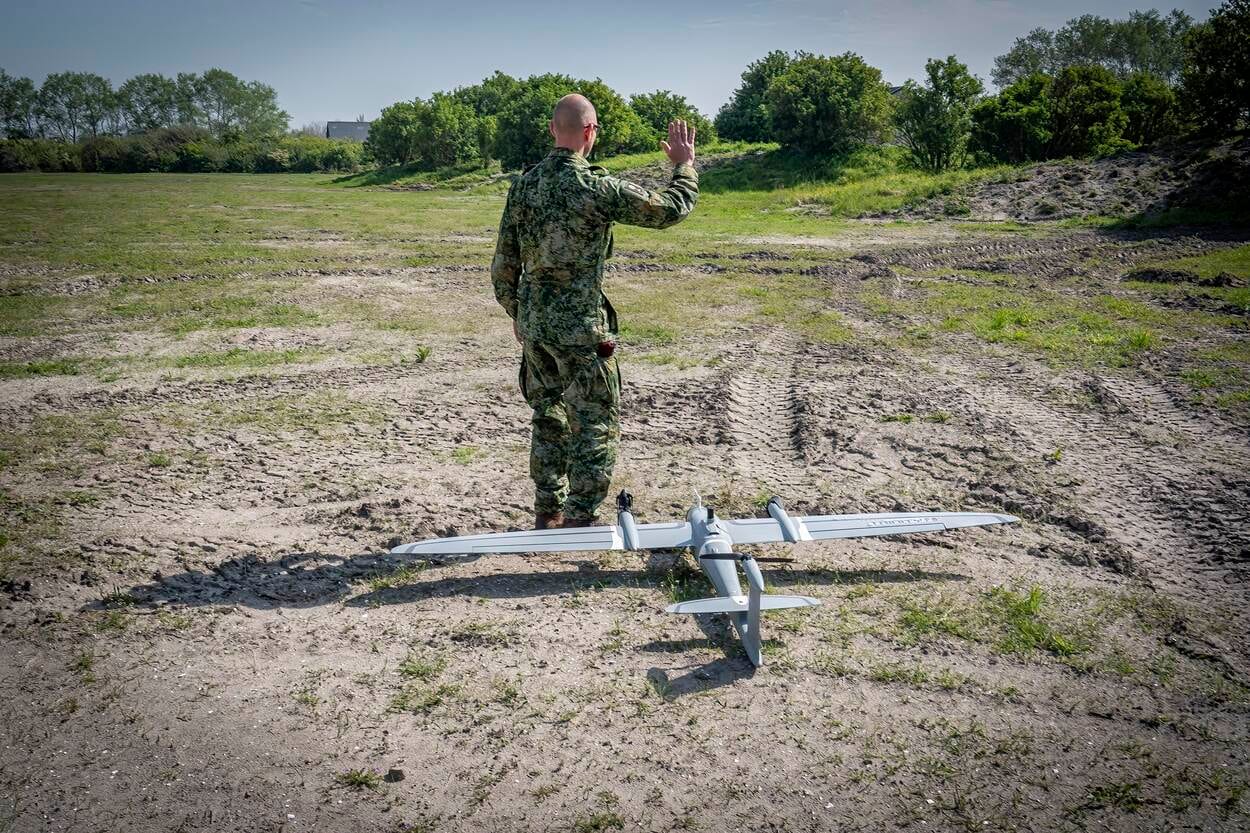
Quantum Systems has confirmed that its fleet of unmanned aerial vehicles is back in operation following a temporary grounding by the German military. The manufacturer, which provides drone technology to both the Bundeswehr and the Ukrainian armed forces, stated that it identified a cybersecurity incident in late October. According to the company, the threat was successfully contained through…
Fake Zillow pages use ClickFix NetSupport RAT to target apartment hunters
Researchers at EfficientIP have identified a sophisticated social engineering campaign that leverages fraudulent Zillow apartment-review pages to deploy the NetSupport remote access trojan (RAT) onto Windows systems. The campaign, which first appeared in August 2026, targets individuals searching for rental properties by tricking them into executing malicious PowerShell commands. By…
New worm-like 'SCKit' malware targets MSPs in ScreenConnect attacks
A new malware toolkit identified as SCKit has been deployed in a series of coordinated attacks targeting managed service providers (MSPs) via the ScreenConnect remote access platform. The campaign, which occurred recently, involved the unauthorized installation of rogue remote-access clients on customer endpoints. According to data from security researchers, the initial wave of attacks…
Police dismantle Gootloader, CastleRAT, StealC malware infrastructure
Law enforcement agencies from nine countries have successfully dismantled the core infrastructure supporting the Gootloader, CastleRAT, and StealC malware operations. This coordinated effort, conducted under the umbrella of Operation Endgame, resulted in the seizure of 257 domains and 235 servers. The operation involved police forces from Bulgaria, Canada, Denmark, Germany, Moldova, the…
Your Endpoint Management Platform Could Be Your Biggest Security Risk
Endpoint management platforms have become a double-edged sword for modern IT departments. While these systems are indispensable for deploying patches, managing configurations, and executing remote scripts across thousands of devices, their inherent administrative authority makes them prime targets for malicious actors. Because these platforms are designed to be trusted by the endpoints they…
Check your GitHub repos: A secret stealer hit tens of thousands of them
A sophisticated credential-stealing campaign has compromised tens of thousands of GitHub repositories since November 10, 2026. Security researchers at Aikido identified the operation, dubbed wfx-loot, which leverages stolen GitHub credentials to inject malicious payloads into automated workflows. The attacker’s primary objective is to harvest GitHub Actions secrets, cloud infrastructure…
Active ScreenConnect attacks breach MSPs, impact dozens of organizations
ConnectWise is currently investigating an active malware campaign targeting managed service providers (MSPs) that leverages the company’s ScreenConnect remote access and support platform. The campaign, which began gaining traction around 17:47 UTC on November 11, 2026, involves the unauthorized deployment of rogue remote-access clients to devices managed by MSPs. Cybersecurity researchers at…
IT threat evolution in Q3 2026. Non-mobile statistics
The third quarter of 2026 saw a significant volume of cyber threats targeting non-mobile systems, characterized by a surge in ransomware activity and the continued exploitation of critical vulnerabilities in enterprise infrastructure. According to data collected by Kaspersky, security products blocked more than 311 million web-based attacks between July and September. During this period, the…
IT threat evolution in Q3 2026. Mobile statistics
The third quarter of 2026 saw a notable evolution in mobile threat landscapes, characterized by a decrease in the total volume of attacks alongside an increase in the sophistication of malicious software targeting Android and iOS devices. According to data collected by security researchers, the number of blocked attacks involving mobile malware, adware, and unwanted software fell to…
Russian cloud firm Beget rebuilds from scratch after data wiper attack
Russian cloud services provider Beget is currently engaged in a massive infrastructure recovery effort following a destructive cyberattack that occurred on the night of November 1. The company, which provides web hosting, domain registration, and cloud services to over 200,000 customers, confirmed that an unauthorized actor gained access to its primary management systems and deployed…
Hackers Exploiting ‘SSHole’ Authentication Bypass in OpenSSH
A high-severity authentication bypass vulnerability in OpenSSH, colloquially dubbed SSHole and tracked as CVE-2026-123158, is currently being exploited in the wild. The flaw affects systems running OpenSSH that utilize the musl libc library with the Pluggable Authentication Module (PAM) disabled. Security researchers and threat intelligence firms have confirmed that exploitation attempts began…
Product showcase: What the Malwarebytes Claude connector reveals about unexpected texts
Malwarebytes has launched a new connector for Anthropic’s Claude AI, designed to help users verify the legitimacy of suspicious communications directly within the chat interface. The integration allows users to input potentially malicious links, phone numbers, or email addresses, which the AI then cross-references against the Malwarebytes threat database. This tool is accessible to both free…
SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 122
The current cybersecurity landscape is marked by a surge in sophisticated malware campaigns and critical infrastructure vulnerabilities. Recent reports highlight a diverse array of threats, ranging from state-sponsored espionage to supply chain compromises affecting financial and healthcare institutions. Among the most notable developments is the discovery of a previously unknown advanced…
Week in review: Refrigeration cyberattacks hit European retailers again, Patch Tuesday forecast
European retail operations are facing a renewed wave of cyberattacks targeting refrigeration infrastructure, leading to significant food spoilage across the continent. This latest incident follows a series of similar attacks three weeks ago that specifically impacted French supermarkets by forcing temperature controls to malfunction, effectively turning refrigeration units into ovens. In a…
Fake security tools on GitHub push backdoors and infostealers
A long-running campaign targeting cybersecurity professionals and developers has been identified, involving the distribution of malicious repositories on GitHub that deploy backdoors and information-stealing malware. While the threat actor behind this operation initially focused on luring cryptocurrency enthusiasts with fake blockchain games and cheat tools over the past two years, they have…
Midnight Mimosa Malware Found Preinstalled on Low-Cost Android Phones
Recent reports indicate that a new malware strain, dubbed "Midnight Mimosa," has been discovered preinstalled on certain low-cost Android smartphones. This finding suggests that some devices may be compromised with malicious software embedded directly into their firmware before they even reach consumers, posing a significant supply chain security risk.
UAC-0099 Targets Ukrainian Government Personnel With ASHVEIN RAT Hiding Commands in HTML
A Russia-aligned threat actor, UAC-0099, has reportedly been observed deploying a new .NET-based infostealer and remote access trojan (RAT) named ASHVEIN. This malware has been specifically used in attacks targeting Ukrainian government personnel. The cybersecurity firm TrendAI is tracking this activity cluster under the designation Earth Sirrush, which was previously known as SHADOW-EARTH-065.
Chasing AMMYY at Splunk .conf
A recent report detailed the detection of Flawed AMMYY RAT traffic at the Splunk .conf event, an incident uncovered through the combined capabilities of Cisco's Encrypted Visibility Engine (EVE) and Endace PCAP. The key takeaway from this discovery was the ability to identify this malicious activity without the need to decrypt TLS-encrypted communications, highlighting advancements in network…
ClickFix Attacks Evolve to Better Hide Malicious Payloads
Recent reports indicate a significant evolution in ClickFix attack methodologies, with cybercriminals now employing more sophisticated techniques to mask their malicious payloads. The updated tactics reportedly involve the use of DNS TXT records and browser cache pre-fetching, strategies designed to make the early detection of these threats considerably more difficult for security systems and…
ClingSTUN Linux Backdoor Abuses Public STUN Infrastructure
Fortinet's FortiGuard Labs has detailed a new Linux backdoor, dubbed ClingSTUN, which leverages legitimate public Session Traversal Utilities for NAT (STUN) infrastructure to mask its command and control (C2) communications. The malware primarily targets unpatched Internet of Things (IoT) devices, functioning as a back-connect proxy that turns compromised systems into remotely controlled nodes.
ClingSTUN Malware Turns IoT Devices Into Proxy Nodes
A recently discovered Linux backdoor, named ClingSTUN, has been observed actively compromising Internet of Things (IoT) devices. The malware reportedly exploits a significant number of known vulnerabilities, specifically 24 distinct flaws, to gain initial access to these devices. Once compromised, ClingSTUN employs a novel technique involving legitimate public STUN servers to obfuscate its…
SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 117
The Warlock ransomware group has continued to leverage year-old vulnerabilities in Microsoft SharePoint to target critical infrastructure organizations, including water and telecom operators. This ongoing campaign was highlighted in a recent security newsletter, which also detailed several other significant cybersecurity developments.
The EDR blind spot: 3 ways browser attacks evade endpoint telemetry
Endpoint Detection and Response (EDR) systems, while crucial for detecting host-level code execution, may not fully address the evolving landscape of browser-based attacks, according to recent analysis. Many modern threats leverage browser sessions and cloud applications, performing malicious actions that do not generate the typical endpoint artifacts EDR solutions are designed to monitor.…
Android 17 Advanced Protection Locks Accessibility Services to Verified Accessibility Tools
Android 17 is set to introduce a new security enhancement under its Advanced Protection feature, which will significantly restrict how accessibility services can be utilized. The reported change indicates that only applications specifically designated and verified as legitimate Accessibility Tools will be granted access to these powerful services. This move directly addresses a long-standing…
Botnets, adversarial attacks and data poisoning top leaders’ AI threat list
A recent survey of nearly 4,000 business and technology leaders across 71 countries indicates that while companies are increasing their investment in artificial intelligence, they feel least prepared to defend against AI-specific threats. Among security and technology executives, half identified attacks targeting AI systems as a top-five gap in their preparedness, surpassing other threats.
ScreenConnect Client (Ab)used by Attackers, (Thu, Oct 1st)
A recent report indicates that threat actors have been observed leveraging the legitimate ScreenConnect client in their attacks. This activity suggests a trend where attackers opt for readily available and trusted software to achieve their objectives, rather than developing or deploying sophisticated custom malware. The report, published on Thursday, October 1st, highlights the abuse of a…
Many expect AI in the SOC to make entry jobs harder to get
The increasing integration of artificial intelligence into Security Operations Centers (SOCs) is reshaping the cybersecurity career landscape, particularly for entry-level positions. While AI tools are largely welcomed by current security staff for automating repetitive tasks, concerns are emerging about their potential impact on skill development and the accessibility of junior analyst roles.
US sanctions 10 over ATM malware scheme tied to Tren de Aragua
The U.S. Treasury Department has imposed sanctions on ten individuals and several companies, all tied to a sophisticated ATM malware scheme that has reportedly siphoned over $40 million from financial institutions. The Office of Foreign Assets Control (OFAC) announced the sanctions, linking the "jackpotting" operation to Tren de Aragua, a Venezuelan criminal organization, and identifying the…
Custom ChatGPTs push ClickFix attacks to deploy RAT malware
A novel attack campaign is leveraging custom variants of OpenAI's ChatGPT, promoted through sponsored Google search results, to direct users to malicious websites. These sites employ "ClickFix" social engineering tactics to deliver remote access trojan (RAT) malware. The campaign was identified by Huntress, a managed detection and response firm, which noted that dozens of users have been affected.