
breach news
295 stories · page 1 of 7Rackspace Spot breach let hackers access customer Kubernetes secrets
Rackspace has confirmed a security breach affecting its Rackspace Spot cloud platform, a service designed for managing containerized applications through Kubernetes. The unauthorized access occurred on November 17, 2026, spanning a window from approximately 00:20 to 22:00 UTC. The company discovered the intrusion on November 18 following a report from a customer and subsequently verified that…
FBI reportedly hacked again, this time targeting nationwide police database
The Federal Bureau of Investigation is currently investigating a potential security breach involving the National Crime Information Center, a critical database used by law enforcement agencies across the United States. The system serves as a central repository for sensitive records, including outstanding arrest warrants, information on missing and wanted persons, and data regarding stolen…
n0n extortion gang leaks data of JPMorgan Chase, Visa, and Mastercard customers
The extortion group known as n0n has leaked sensitive customer information belonging to JPMorgan Chase, Visa, and Mastercard following a series of security breaches at third-party service providers. The threat actor, which security researchers believe operates out of Russia, published the stolen data on its dark web portal after the financial institutions refused to meet a 48-hour deadline for…
Bell Canada says 'agentic' hacker stole enterprise customer data
Bell Canada has confirmed a significant cybersecurity breach that occurred on November 17, 2026, resulting in the theft of enterprise customer data. The telecommunications provider stated that an unauthorized party gained access to several internal systems, most notably a pre-production environment of the Maximo platform, which the company utilizes for the ordering and provisioning of…
SBC Medical Group Data Breach Impacts Over 2 Million
SBC Medical Group Holdings, a California-based firm providing operational and management support to medical clinics, has disclosed a significant data breach affecting over 2 million individuals. The organization confirmed that unauthorized actors gained access to an internal platform it manages, leading to the compromise of extensive databases containing sensitive customer and employee…
JPMorgan Confirms Customer Data Breach Following Third-Party Compromise
JPMorgan Chase has confirmed that a data breach involving its customers occurred following a cyber-attack on third-party vendors utilized by the financial institution. The company issued a public statement on November 19, 2026, clarifying that the incident resulted in unauthorized access to marketing data. According to the bank, the compromised information may include customer names and email…

Chase, Visa, Mastercard confirm third-party cyberattacks that may have exposed customers' info
JPMorgan Chase, Visa, and Mastercard have confirmed that they are investigating cybersecurity incidents involving third-party service providers. These acknowledgments follow public claims made by an extortion group known as n0n, which asserted responsibility for compromising the three financial institutions earlier this week. The threat actor, which reportedly emerged in September and has…
Rakuten Securities Breach Could Impact 15 Million Customers
Rakuten Securities, a major Japanese online brokerage firm, has disclosed a significant data breach that potentially impacts nearly 16 million customer accounts. The company, a subsidiary of the Rakuten Group, issued a formal apology on November 17, 2026, after identifying unauthorized access to its internal systems. According to the firm, the breach was first detected on November 16, though…
Russian APT Poses as Employee of Hacked Firm to Breach Another US Organization
The Russian-linked advanced persistent threat (APT) group known as Star Blizzard has successfully breached a second U.S. organization by weaponizing data and identities stolen from a previous victim. According to analysis from Google Threat Intelligence, the group—which is also tracked under aliases including Callisto, Cold Relic, Cold River, UNC4057, and Gossamer Bear—leveraged information…
Java4Shell (CVE-2026-114938): Frequently asked questions about OpenJDK remote code execution vulnerability
A critical memory corruption vulnerability, identified as CVE-2026-114938 and nicknamed Java4Shell, has been disclosed in the OpenJDK platform. The flaw resides within the Java Base64 decoding mechanism, specifically affecting a performance optimization shortcut designed for certain x86-64 processors. By sending a specially crafted Base64 string, an attacker can trigger a buffer overflow,…
Cloud keys leaked in Docker Hub images are stolen within seconds
Researchers from Stony Brook University have demonstrated that sensitive cloud credentials and API keys inadvertently included in public Docker Hub images are being harvested by automated scanners within seconds of being published. Billy Tsouvalas and Nick Nikiforakis conducted a four-month study involving 300 honeypot images across eight public container registries. By planting decoy…
Website management platform Optimizely confirms hackers put malicious code into customer sites
Optimizely, a prominent provider of website management and experimentation software, has confirmed a security breach that allowed unauthorized actors to inject malicious JavaScript into customer websites. The incident, which was identified and subsequently contained by the company, involved the exploitation of a vulnerability within the Optimizely Web Experimentation platform. This tool is…
Uber notifies drivers of data breach affecting nearly 150,000 people
Uber has officially confirmed a significant data breach affecting 149,346 of its drivers. The company began issuing formal notification letters to the impacted individuals on November 10, 2026, following a security incident that originated within the infrastructure of a third-party service provider. According to the disclosures filed with the Maine Office of the Attorney General, the exposed…
Japan's Fugaku supercomputer has decidedly un-super security
The RIKEN Center for Computational Science in Japan has confirmed a significant security breach involving its Fugaku supercomputer, currently ranked as the ninth most powerful system in the world. The incident, which occurred between November 10 and November 13, 2026, forced the organization to take the massive machine offline to prevent further unauthorized activity. RIKEN officials have…
Uber says nearly 150,000 impacted by third-party breach
Uber has confirmed that a security breach at an unnamed third-party service provider resulted in the exposure of personal information for 149,346 individuals across the United States. The rideshare company began notifying state regulators after learning on October 9 that internal credentials belonging to the vendor had been stolen and subsequently used to gain unauthorized access to an…
The Hidden Cost of Identity Technical Debt
Organizations are increasingly grappling with the accumulation of identity technical debt, a systemic issue defined by the backlog of unmanaged identities, excessive permissions, and fragmented governance controls. This debt arises from a series of incremental, often pressured decisions—such as granting emergency access or provisioning service accounts during migrations—that are rarely…
FBI warns ARTEX AI hacking tool is powering global cyberattacks
The Federal Bureau of Investigation has issued a formal advisory regarding the widespread exploitation of ARTEX, an autonomous penetration testing framework powered by artificial intelligence. Since August 2026, the tool has been utilized by various threat actors to automate cyberattacks across multiple critical sectors, including government, defense, finance, healthcare, and technology. The…
TSMC employee data breach linked to cloud provider
Taiwan Semiconductor Manufacturing Company (TSMC) has confirmed that personal information belonging to its current and former employees has been exposed online. The breach came to light after a threat actor began auctioning a 6.9GB dataset, which they claimed contained 46,000 individual records. The company, which serves as the world’s largest contract chipmaker for major technology firms like…
Data Breach at La Poste Subsidiary Maileva Affects 22 Million People in France
A significant data breach at Maileva, a subsidiary of the French postal service La Poste, has resulted in the exposure of personal information belonging to approximately 22 million individuals. The incident, which occurred in mid-September 2026, involves the unauthorized access of names and postal addresses. Maileva functions as a document processing platform under the Docaposte umbrella,…
Week in review: Secret stealer hits GitHub repos, Claude Code turned into remote-controlled implant
A widespread credential-harvesting campaign has compromised tens of thousands of GitHub repositories since November 10, 2026. Security researchers identified the operation, dubbed wfx-loot, which relies on stolen GitHub credentials to inject malicious payloads into existing repositories. In at least 1,800 confirmed instances, the injected code successfully executed, exfiltrating GitHub Actions…
Stolen Fireworks AI Key Led to Cursor Data Breach and Trojanized Claude Code Extension
The compromise of the official Claude Code extension hosted on the Cursor marketplace has been traced back to the theft of an access key originating from a security incident at Fireworks AI. According to a recent update from Cursor, an unauthorized actor obtained an access key that had been issued to Fireworks AI. This key, which was exposed following a breach at the third-party provider,…
Cursor confirms security breach led to malicious Claude Code extension
The AI-powered code editor Cursor has confirmed a significant security breach that resulted in the distribution of malicious software through its marketplace. The incident, which occurred on October 29, involved the compromise of credentials belonging to the AI infrastructure provider Fireworks AI. These credentials allowed unauthorized actors to access internal Cursor systems, leading to the…
City of Osaka warns of data breach impacting 1 million as Japan reels from dozens of cyber incidents
The city of Osaka has officially confirmed a significant data breach involving a third-party technology provider, resulting in the exposure of over 1 million email addresses. The incident centers on the Arara email distribution service, which is utilized by TKC Corporation, a contractor responsible for maintaining the city’s online administrative services platform. According to the city…
Adapting to AI penetration testing orchestrators: The Modern Security Model
The integration of artificial intelligence into penetration testing workflows has emerged as a significant shift in the modern cybersecurity landscape, moving beyond manual assessment toward automated, orchestrator-driven security models. This evolution is characterized by the deployment of AI-based agents capable of executing complex security tasks, such as vulnerability scanning, threat…
In Other News: New CISA Director Nominee, Connected Car Hacking, Baker Tilly Data Breach
The accounting firm Baker Tilly has confirmed a data breach involving the theft of sensitive client information, including Social Security numbers. The incident originated from a platform managed by an unnamed third-party service provider and occurred in early September. While the firm has not disclosed the total number of individuals affected, regulatory filings in Texas indicate that the…
TSMC confirms employee data breach tied to cloud service provider
Taiwan Semiconductor Manufacturing Company (TSMC) has officially confirmed that a data breach involving one of its third-party cloud service providers resulted in the unauthorized access of sensitive information belonging to its current and former employees. The semiconductor giant disclosed the incident in a formal filing with the Securities and Exchange Commission on Thursday, clarifying…
How one AI agent exposed five critical enterprise security gaps
The rapid proliferation of AI agents within corporate environments has created a significant visibility gap, as employees increasingly deploy automation tools without oversight from security or IT departments. Recent industry data indicates a disconnect between perceived and actual control: while a majority of security professionals believe they have strong visibility into AI agents, a much…
Ransomware attack on Belarusian cloud firm disrupts businesses for days
ActiveCloud, a prominent Belarusian provider of cloud hosting and IT infrastructure services, confirmed it was the target of a ransomware attack earlier this week. The breach resulted in significant operational disruptions, rendering corporate websites, email systems, and virtual server environments inaccessible for a wide range of businesses across Belarus and Russia. The company first…
Attackers in Binance Breach Targeted Known Weakness, Missing Controls
Attackers behind the recent breach of Binance successfully exploited a known vulnerability while simultaneously navigating a lack of sufficient internal controls. The incident highlights the persistent difficulty of securing high-frequency blockchain environments, where the speed of asset movement often outpaces traditional security monitoring and automated intervention systems.
354 dark web vendors and buyers arrested in Operation TorNado
Law enforcement agencies across 14 countries have concluded a lengthy international crackdown known as Operation TorNado, resulting in the arrest of 354 individuals involved in dark web illicit trade. The operation, which spanned from May 2025 to October 2026, targeted vendors and buyers who had previously utilized five major dark web marketplaces that had already ceased operations: Archetyp,…
Picus puts AI agents on the offensive with autonomous pentesting
Picus Security has introduced a new capability titled Picus Autonomous Penetration Testing, designed to integrate artificial intelligence agents into offensive security operations. This launch marks a transition for the company from traditional automated testing toward an agentic model capable of simulating adversary behavior in production environments. The platform is built upon five years of…
Google Cloud Warns Three AMD Turin CPU Flaws Could Leak Data Across Processes in VMs
Google Cloud has issued a security advisory regarding three side-channel vulnerabilities identified in AMD Turin processors. These flaws present a risk of unauthorized data exposure across processes running within the same virtual machine (VM). While Google has already implemented infrastructure-level mitigations to prevent cross-VM and VM-to-host data leakage, users are now required to take…
Inside an AI Attack Against a US Retailer
A US retailer recently suffered a security breach after an attacker successfully shifted from manual exploitation techniques to the use of AI-generated scripts. According to reports, the initial attempt to compromise the organization’s systems using hand-typed commands proved unsuccessful. However, the adversary’s pivot to automated, AI-assisted scripting allowed them to bypass existing…
Japan Pushes Emergency Funding for Cybersecurity as AI-Assisted Breaches Rise
The Japanese government is moving to secure emergency funding aimed at bolstering national cybersecurity infrastructure in response to a surge in sophisticated, AI-assisted digital breaches. The proposed financial package seeks to modernize the nation’s defensive posture by expanding human resources and enhancing the operational capabilities of state agencies tasked with monitoring and…
Baker Tilly notifies clients of data breach at third-party provider
The accounting and advisory firm Baker Tilly has begun notifying clients of a data breach involving sensitive personal information that was stored on a platform managed by an unnamed third-party service provider. The firm, which provides a wide range of tax, auditing, and business advisory services globally, confirmed that it first became aware of the security incident on September 6, 2026.…
Active ScreenConnect attacks breach MSPs, impact dozens of organizations
ConnectWise is currently investigating an active malware campaign targeting managed service providers (MSPs) that leverages the company’s ScreenConnect remote access and support platform. The campaign, which began gaining traction around 17:47 UTC on November 11, 2026, involves the unauthorized deployment of rogue remote-access clients to devices managed by MSPs. Cybersecurity researchers at…
Notion says Fireworks breach exposed customer AI chat transcripts
Notion, a prominent digital workspace platform, has confirmed that a security breach at its AI infrastructure provider, Fireworks AI, resulted in the unauthorized exposure of customer AI chat transcripts. The incident originated within the infrastructure of Fireworks AI, which supports Notion’s AI features, including the Insights tool that allows administrators to monitor team usage of…
WhiteArmor Demands $5 Million from Maersk, Claims Theft of 100GB of Data
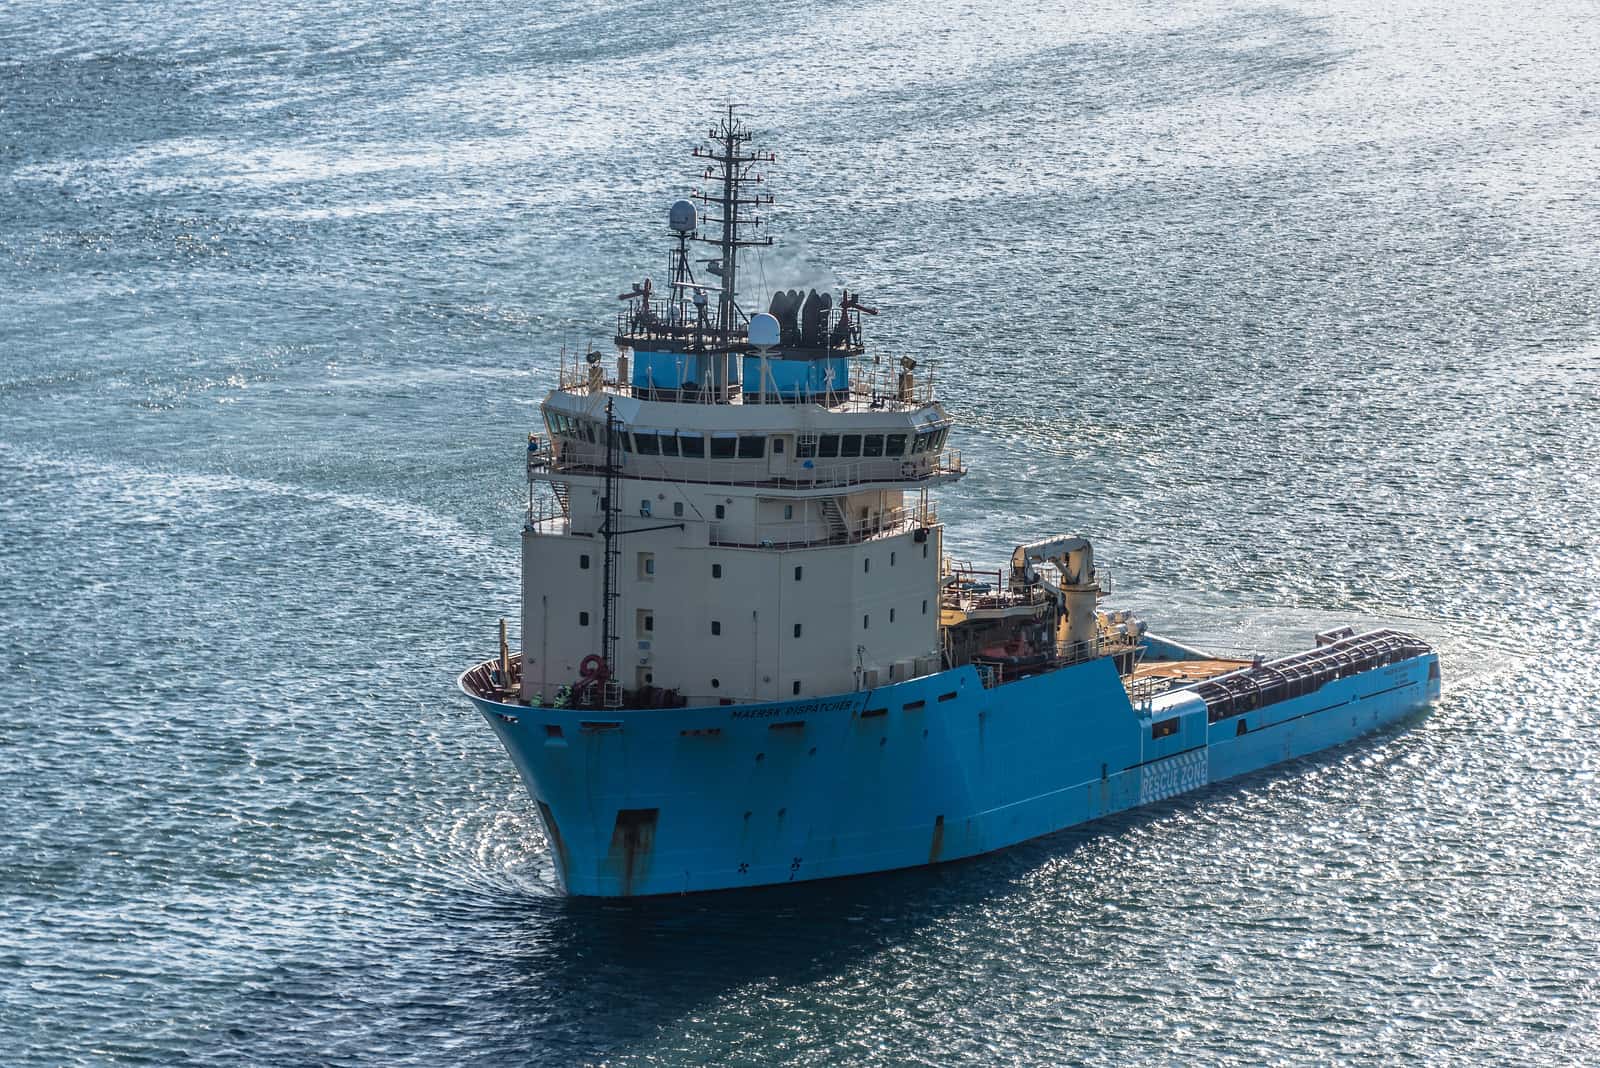
A.P. Moller-Maersk, the global shipping and logistics conglomerate, has confirmed that it is investigating a security incident involving unauthorized access to a local legacy system. The company disclosed the breach on November 11, 2026, noting that the affected infrastructure was inherited through a previous corporate acquisition. Maersk stated that it took immediate action to secure the…
An Instagram ad was all it took: Leaked exploit kits are hitting employees’ iPhones
Criminals are increasingly leveraging leaked exploit kits to compromise iPhones, creating significant security risks for corporate environments where employees use personal devices for work. According to the 2026 Advanced Mobile Threat Report from iVerify, two specific toolkits, DarkSword and Coruna, are being deployed through malicious advertisements and compromised websites to target iOS…
Fireworks AI gets burned twice as customer data exposure widens
Fireworks AI has disclosed a second, more severe security breach occurring in October, significantly expanding the scope of customer data exposure beyond what was initially reported. This latest incident, which the company confirmed began on October 23, originated from a compromise at a third-party cloud provider that hosted the company’s research and development infrastructure. According to…
Binance Investigates ShinyHunters Breach Claims
Binance is currently investigating claims made by the threat actor group ShinyHunters, which alleges it has successfully breached the cryptocurrency exchange’s systems. On November 4, 2026, the group posted an advertisement on the PwsForums platform, asserting that it had obtained approximately 335.9 million records. The attackers are demanding a payment of $900,000, threatening to leak the…
Fireworks AI discloses new breach after cloud provider hack
Fireworks AI, a startup specializing in high-performance infrastructure for deploying open-source artificial intelligence models, has disclosed a significant security breach involving its development environment. The incident, which occurred on October 23, originated from a compromise at an unnamed third-party cloud provider that hosted the company’s research and development machines.…
SEGA newsletter data breach exposes 2.2 million email addresses
Japanese gaming company SEGA has confirmed that a data breach at its third-party newsletter provider, ARARA, resulted in the exposure of 2.2 million subscriber email addresses. The incident impacts 11 distinct newsletters associated with SEGA and its subsidiary, SEGA Fave. While the majority of the compromised data consists of email addresses, SEGA noted that 92,300 of the affected records…
U.S. urges critical infrastructure orgs to secure refrigeration systems ASAP after EU supermarket and blood bank attacks
U.S. federal agencies have issued an urgent directive for critical infrastructure organizations to secure industrial refrigeration and cold-chain monitoring systems. This alert follows a series of cyberattacks that targeted supermarkets and blood banks across Europe, resulting in spoiled inventory and, in some instances, the triggering of fire hazards. The advisory, released jointly by the…
York University breach exposed personal information dating to 2007
York University has confirmed a significant cybersecurity breach involving unauthorized access to personal information collected through various online forms. The incident, which was identified by the institution on October 25, 2026, compromised data spanning a nearly two-decade period, with affected records dating back to 2007. The breach impacted 14 distinct websites operated by university…
Data breach at hearing aid giant Amplifon impacts thousands
Amplifon, a global hearing healthcare provider headquartered in Milan, Italy, has confirmed that a cyberattack resulted in the unauthorized access of sensitive personal and medical data belonging to thousands of its U.S. customers. The company, which operates across 28 countries, began notifying state regulators of the incident in early November 2026. According to filings submitted to…
Hackers Exploit Qubole's Trusted AWS Access to Breach Customer Accounts and Steal Data
Attackers successfully compromised multiple customer AWS accounts between October 14 and October 26 by leveraging trusted access credentials associated with the Qubole data lake platform. According to reports from the cloud security firm Wiz, the unauthorized parties utilized credentials belonging to an AWS account that Qubole maintains to interact with and manage customer environments. While…
Italy’s Meloni Blames Pro-Russian Hackers for Leak of Foreign Minister’s Data on the Dark Web
Italian Foreign Minister Antonio Tajani confirmed on November 9, 2026, that his personal information has been disseminated across the dark web. Tajani, who also serves as a vice premier, stated that the ongoing exposure of his private data has subjected both him and his family to direct threats and intimidation. According to his account, the perpetrators are actively seeking additional…