
patch news
415 stories · page 1 of 9
PHP 8.6: Things are gonna get a lot more strict around here
The PHP development team has officially released PHP 8.6, marking the latest iteration of the widely used server-side scripting language. This release arrives following a turbulent period for the platform, which has faced a surge of security vulnerabilities since October. These flaws, which allowed unauthenticated attackers to trigger remote code execution (RCE) or crash PHP workers,…

CVE-2026-23871: WhatsApp Bug Helped Scammers Make Messages Look Legitimate
WhatsApp has released security updates addressing three vulnerabilities, one of which was actively exploited in a scam campaign designed to increase the perceived legitimacy of fraudulent messages. The company identified this specific flaw, tracked as CVE-2026-23871, while investigating and disrupting an ongoing fraud operation.

China's 'Armory Castle' Lays Siege to VMware vCenter Zero-Day
A China-nexus threat actor identified as Armory Castle has been linked to the exploitation of a zero-day vulnerability affecting VMware vCenter. The activity was observed during the most recent cycle of security updates for the platform, suggesting the group maintained access to the vulnerability while the vendor was actively patching other known flaws in the software.
How Cloudflare WAF helps protect against phpAfterShell and other critical PHP flaws
Cloudflare has recently highlighted the role of its Web Application Firewall (WAF) in mitigating risks associated with critical vulnerabilities in PHP-based environments, specifically citing the threat posed by tools like phpAfterShell. These types of exploits target the ubiquity of PHP in web development, leveraging common weaknesses to gain unauthorized access to server environments. By…
A Technical Guide to Mitigate Java4Shell with TruRisk Eliminate
A critical heap out-of-bounds write vulnerability, tracked as CVE-2026-114938 and referred to as Java4Shell, has been identified in the HotSpot AVX-512 Base64 decoder. The flaw resides in the way the Java Virtual Machine (JVM) handles specific Base64-encoded inputs on x86-64 processors equipped with AVX-512 VBMI instructions. While researchers have demonstrated that this vulnerability can lead…
VMware vCenter zero-day exploited for months before patch (CVE-2026-123890)
Broadcom has issued a security patch for a critical vulnerability in VMware vCenter Server, identified as CVE-2026-123890. The flaw, which carries a maximum CVSS severity score of 9.8, allows a remote, unauthenticated attacker to gain administrative access to the vCenter Server. This vulnerability affects vCenter Server, SDDC Manager, and VMware Tools for Windows, including deployments within…
Linux KVM Flaw CVE-2026-99312 Lets Guest VMs Access Host Memory on AMD Hosts
A critical security vulnerability, tracked as CVE-2026-99312, has been identified in the Linux Kernel Virtual Machine (KVM) hypervisor. The flaw allows a guest virtual machine to bypass isolation boundaries and access memory belonging to the host system. Researchers demonstrated the exploit by successfully reading approximately 127 GB of memory from a cloud server while operating from within…
Windows 11 KB5132057 update released with 28 changes and fixes
Microsoft has released the KB5132057 optional cumulative update for Windows 11, specifically targeting versions 25H2 and 26H2. This release serves as a preview update, allowing IT administrators and users to evaluate a suite of 28 quality improvements and feature adjustments before they are integrated into the broader Patch Tuesday release scheduled for next month. Notably, this update does…
New Unpatched Windows 0-Day FastUnlock Lets Someone Holding a Locked PC Run Programs on It
A newly disclosed zero-day technique, identified as FastUnlock, allows an individual with physical access to a locked Windows computer to execute programs without requiring a valid user login. The discovery was reported by a researcher operating under the handles MSNightmare and Nightmare Eclipse, with additional analysis provided by the endpoint-security firm ThreatLocker. While the…
VMware patches vCenter zero-day exploited in attacks since September
Broadcom has released emergency security updates for VMware vCenter Server to address a critical authentication bypass vulnerability, identified as CVE-2026-123890. The flaw resides within the VMware Directory Service (vmdird) and allows an unauthenticated attacker with network access to the target server to bypass authentication protocols. By successfully exploiting this vulnerability, an…

ASUS warns of critical hard-coded key flaw in Control Center Express
ASUS has issued urgent security updates for its Control Center Express platform to address a trio of critical vulnerabilities that could grant remote attackers full administrative control over management consoles and the hardware they monitor. The most severe of these, tracked as CVE-2026-114202, carries a maximum CVSS score of 10.0. This flaw stems from the use of a hard-coded cryptographic…
CVE-2026-123890: Critical Authentication Bypass in VMware vCenter
Broadcom has issued an emergency security advisory, VMSA-2026-0009, to address a critical authentication bypass vulnerability identified as CVE-2026-123890. The flaw resides within the VMware Directory Service component of vCenter Server and carries a CVSSv3 severity score of 9.8. By exploiting this vulnerability, an attacker with network access to a target vCenter deployment can bypass…
Why Most Apps Don’t Scale (and How to Fix Them)
Many modern applications marketed as having scaling issues are actually suffering from fundamental architectural inefficiencies rather than genuine traffic-driven bottlenecks. While developers often blame sudden spikes in user activity for performance degradation, recent analysis suggests that the root cause is frequently found in how applications handle data processing tasks.
NGINX2Root: F5 patches five critical NGINX vulnerabilities
F5 has released security updates to address five critical vulnerabilities within the NGINX web server, a collection of flaws collectively identified by researchers at Xint as NGINX2Root. These vulnerabilities, which primarily affect the handling of HTTP/2 and other core protocols, could potentially allow for remote code execution under specific conditions. While the vulnerabilities are…
PHP Releases Patches to Fix 18 Vulnerabilities
The PHP Foundation has released security updates addressing 18 distinct vulnerabilities across multiple supported versions of the language. This batch of patches, released on November 19, 2026, follows a period of heightened security activity for the platform, occurring only one month after the disclosure of two critical flaws collectively referred to as PHP2Shell. While these newly disclosed…
Chrome patches six Critical flaws, two found with AI’s help
Google has released a comprehensive security update for the Chrome browser, addressing a total of 204 vulnerabilities across its desktop and mobile platforms. The patches, which began rolling out on November 17, cover critical memory-safety issues that could potentially allow for arbitrary code execution. Users are encouraged to update their software immediately to mitigate these risks, as the…
PHP Warns of Critical Security Flaws Affecting All Supported Versions, Fixes Coming November 19
The maintainers of the PHP programming language have issued a security advisory warning of critical vulnerabilities affecting all currently supported versions of the software. The project has scheduled a coordinated release of patches for November 19, 2026, with the updates expected to be published between 2:00 p.m. and 2:30 p.m. UTC.
NGINX2Root: Five nginx Flaws, Led by CVE-2026-123007. How to Find, Mitigate, and Patch Now
A collection of five security vulnerabilities, collectively dubbed NGINX2Root, was disclosed on November 18, 2026, affecting various versions of NGINX Open Source and NGINX Plus. The most severe of these, CVE-2026-123007, is a memory corruption flaw within the server’s HTTP/2 implementation. F5, the maintainer of NGINX, has assigned this lead vulnerability a CVSS v4.0 score of 9.2.
Get ready for another critical PHP security release to drop
The PHP Foundation has announced plans to release a critical security update this Thursday between 14:00 and 14:30 UTC. This upcoming patch is intended to address several vulnerabilities, including at least one remote code execution (RCE) flaw. The foundation has advised administrators to prepare for immediate deployment once the updates are available, noting that while the bugs are classified…
AI found more critical bugs in another widely used technology running 225M websites
F5 has issued an emergency security update for the open-source NGINX web server to address 10 newly discovered vulnerabilities. These flaws affect a significant portion of the internet, as NGINX currently powers approximately 225 million websites. The vendor has urged all administrators to upgrade their systems to version 1.31.9 immediately to mitigate the risks.

Consensus mounts that tech outages were fueled by patching of AI-discovered vulnerabilities
A series of significant technical outages affecting aviation, banking, and communications infrastructure over the past week has prompted a federal investigation into the stability of critical systems. While initial concerns focused on the possibility of coordinated cyberattacks, officials from the Trump administration, including Secretary of Homeland Security Markwayne Mullin, Director of…

Apache Roller RCE Flaw CVE-2026-129448 Under Active Attack
The Apache Software Foundation has issued an urgent security advisory regarding a critical remote code execution (RCE) vulnerability in Apache Roller, an open-source Java-based blogging platform. The flaw, assigned the identifier CVE-2026-129448 and carrying a maximum CVSS severity score of 9.8, is currently being exploited in the wild.
Trump administration officials size-up a bad stretch for tech
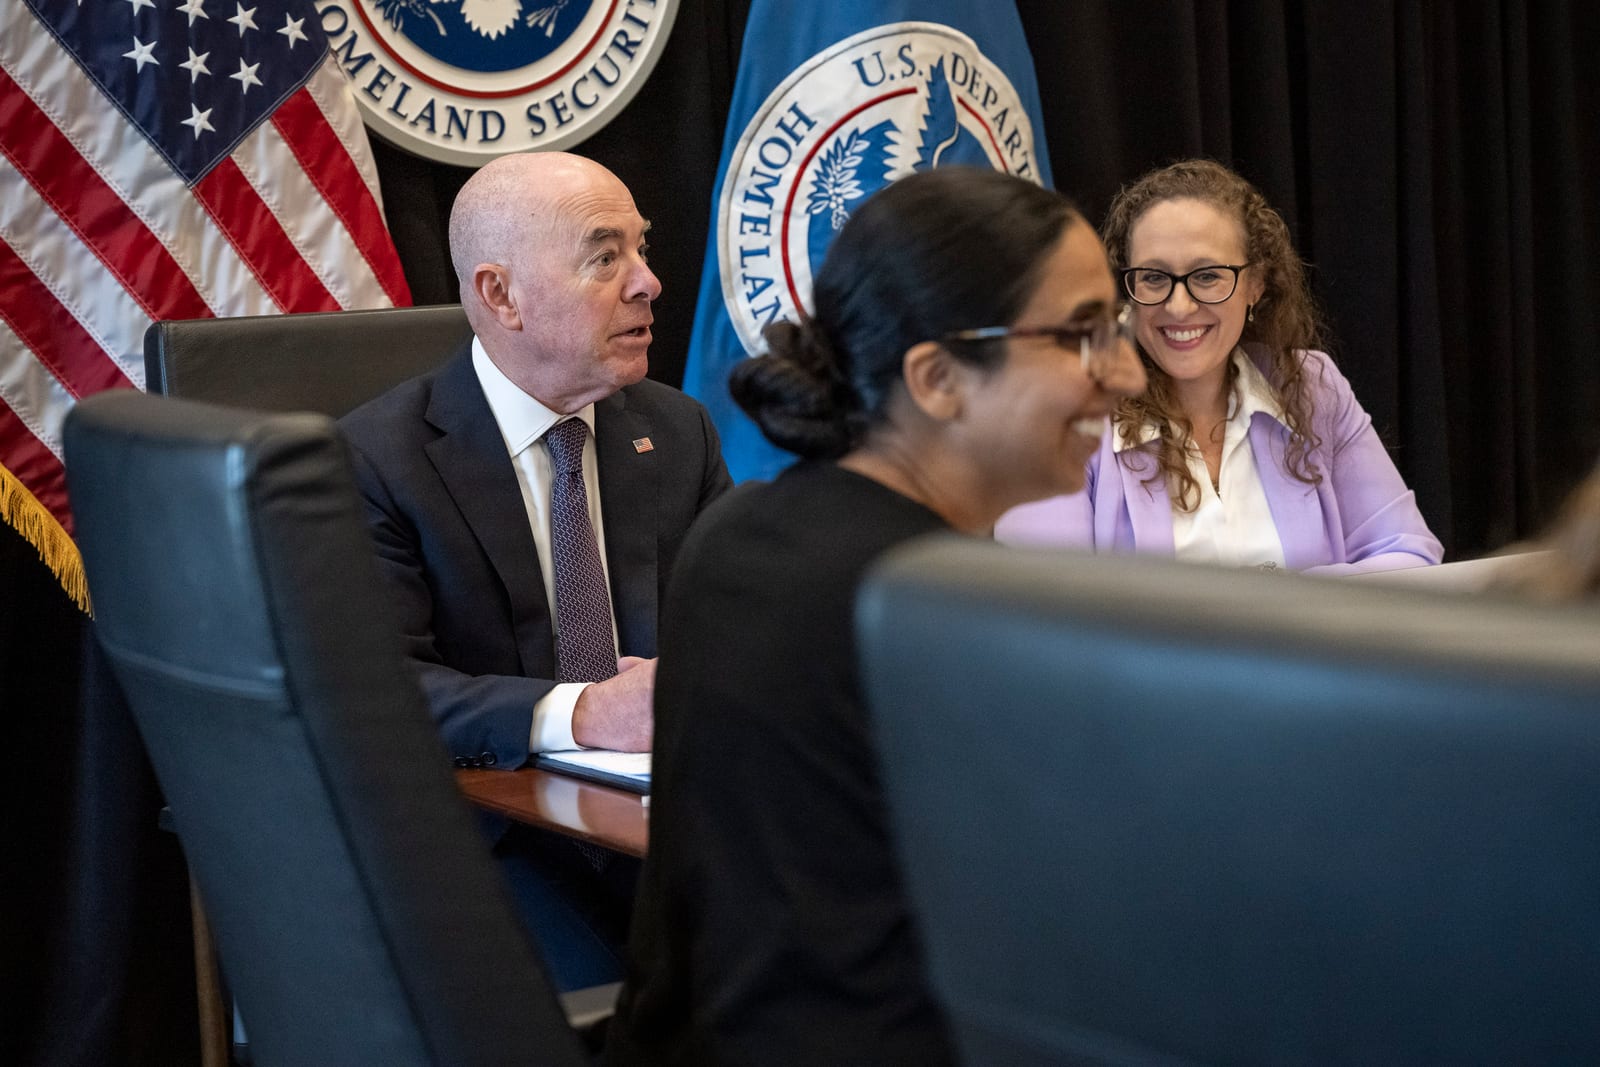
Senior Trump administration officials testified before the House Homeland Security Committee on November 18, 2026, to address a wave of high-profile service disruptions that have affected both public infrastructure and national security agencies over the past ten days. During the hearing, Director of National Intelligence Jay Clayton, Homeland Security Secretary Markwayne Mullin, and FBI…
Cognizant and Qualys Redefine AI-Era Managed Security Service
Cognizant and Qualys have announced a strategic expansion of their partnership, aiming to address the accelerated threat landscape driven by the rise of frontier artificial intelligence. By integrating Cognizant’s managed security services with the full Qualys Enterprise TruRisk Management (ETM) portfolio, the companies intend to move beyond traditional detection toward a model of autonomous,…
AI Pentesting Checklist for Web Apps: 15 Questions to Ask Before Choosing a Vendor
Security teams are increasingly turning to AI-driven penetration testing tools to keep pace with an environment where exploitation often occurs before a patch is even available. Recent industry data indicates that a significant portion of vulnerabilities are actively targeted on or before their public disclosure day, creating a narrow window for organizations to identify and remediate…
Oracle reveals fix-this-ASAP-grade Java4Shell bug that allows attacks on many third-party apps
Oracle has released a series of security updates as part of its November patch cycle, including a fix for a high-severity memory-corruption vulnerability in OpenJDK. Tracked as CVE-2026-114938 and dubbed Java4Shell by the researchers who discovered it, the flaw resides in the optimized machine-level code used by the OpenJDK Base64 decoder.
Java4Shell (CVE-2026-114938): Frequently asked questions about OpenJDK remote code execution vulnerability
A critical memory corruption vulnerability, identified as CVE-2026-114938 and nicknamed Java4Shell, has been disclosed in the OpenJDK platform. The flaw resides within the Java Base64 decoding mechanism, specifically affecting a performance optimization shortcut designed for certain x86-64 processors. By sending a specially crafted Base64 string, an attacker can trigger a buffer overflow,…
How to Find, Mitigate, and Patch the Critical Java4Shell Flaw (CVE-2026-114938) Now
A critical memory-corruption vulnerability, designated CVE-2026-114938 and dubbed Java4Shell, has been identified within the OpenJDK Base64 decoder. The flaw, which carries a CVSS v4.0 severity rating of 9.2, stems from handwritten assembly code designed to accelerate Base64 decoding using AVX-512 instructions. Because Base64 encoding is frequently used for login headers, authentication…
Oracle November 2026 Critical Security Patch Update Addresses 640 CVEs (CVE-2026-114938)
Oracle released its Critical Security Patch Update (CSPU) on November 17, 2026, addressing a total of 640 unique vulnerabilities across 21 different product families. This release cycle, which Oracle introduced in May 2026 to provide more frequent security updates between its standard quarterly cycles, includes 655 individual patches. Of these, 62 have been assigned a critical severity rating,…
Tor releases emergency update amid ongoing DDoS attack
The Tor Project has issued an emergency security update for its network relay software in response to a persistent and widespread distributed denial-of-service (DDoS) attack. The update, designated as version 0.4.9.17, is intended to bolster the resilience of relays against a flood of traffic that has disrupted operations across the privacy network. According to the project, the ongoing attack…
N-able Kills Legacy APIs, Patches 17 N-central Zero-Days
N-able has released a critical security update for its N-central remote monitoring and management platform, addressing 17 vulnerabilities that were recently disclosed and, in some instances, actively exploited by threat actors. The patches, bundled into N-central 2026.4 Hotfix 3, follow the public release of exploit code that targeted legacy components within the software.
Researchers Detail iPhone Flaw That Let Apps Record Audio Despite Denied Microphone Permission
Researchers have detailed a security vulnerability in Apple’s audio service that allowed applications on iPhones and iPads to capture audio recordings even after users explicitly denied microphone access permissions. The flaw bypassed the operating system's privacy controls, effectively rendering the "Don't Allow" prompt ineffective for affected applications.
Google finds AI agent writing and launching exploits with no human in the loop
Google Threat Intelligence Group and Mandiant have identified a significant shift in the cybersecurity landscape, confirming that threat actors are now utilizing autonomous AI agents to execute full-scale cyber intrusions without human intervention. This development marks the first time researchers have observed LLM-powered frameworks capable of independently identifying vulnerabilities,…
NATO’s AI cyber defense work hits up to 300 billion OpenAI tokens a month
The NATO Communications and Information Agency (NCIA) has integrated OpenAI’s cybersecurity models into the core infrastructure of the alliance, resulting in a monthly consumption of up to 300 billion raw input and output tokens. This deployment is facilitated through Daybreak, a specialized program designed by OpenAI to provide vetted cybersecurity professionals with access to advanced models…
ConnectWise Warns ScreenConnect Attacks Continue as SCKit Targets Unpatched Systems
ConnectWise has concluded its investigation into unauthorized access incidents affecting its ScreenConnect remote management platform. The company is urging all customers to ensure their technician client software is updated to version 26.6.5 or later to remediate the vulnerability. Despite these efforts, reports indicate that malicious activity targeting on-premises environments persists,…
Microsoft gives admins one policy to manage Windows patches and fixes for PCs that won’t boot
Microsoft has introduced a unified policy management feature within the Windows Autopatch service, designed to streamline how administrators handle quality updates, .NET Framework updates, and critical system recovery fixes. This update, integrated directly into the Microsoft Intune admin center, allows IT teams to manage these distinct update categories through a single administrative…
40% of organizations struggle to retrace AI agents’ actions
A significant portion of modern enterprises is struggling to maintain oversight of autonomous systems, with 40% of organizations reporting an inability to retrace the actions taken by AI agents within their environments. This visibility gap is particularly pronounced in the financial sector, where 46% of firms report difficulty reconstructing agent activity. The challenge is largely attributed…
N-able Patches 17 N-central Flaws as Attackers Exploit Earlier Bugs to Deploy Crypto Miners
N-able has released a critical security update for its N-central platform, addressing 17 distinct vulnerabilities. The release, designated as N-central 2026.4 Hotfix 3, follows reports that attackers are actively exploiting previously identified flaws within the Remote Monitoring and Management and Unified Endpoint Management software to deploy unauthorized cryptocurrency mining operations.
Google Project Zero cuts bug disclosures to 30 days amid AI threats
Google Project Zero, the security research division responsible for identifying critical vulnerabilities in major software and hardware platforms, has announced a significant shift in its vulnerability disclosure policy. The team is moving away from its long-standing 90-day disclosure window, plus a potential 30-day grace period, in favor of a compressed timeline. This decision is driven by…
Google Project Zero to Cut Disclosure Deadline to 30 Days by 2028
Google’s Project Zero has announced a significant shift in its vulnerability disclosure policy, moving away from its long-standing "90 + 30" framework toward a more aggressive timeline. Under the new policy, known as Full X, the research team will publish technical details regarding discovered vulnerabilities exactly X days after notifying the affected vendor, regardless of whether a patch has…
Rspamd 4.3.0 stops forwarded mail from softening DMARC rejects
The maintainers of the open-source spam filtering system Rspamd have released version 4.3.0, addressing a series of critical security vulnerabilities and functional defects. This update resolves multiple flaws that previously allowed unauthenticated attackers to disrupt the software’s operation or bypass authentication checks. Administrators are advised to review their local configurations, as…
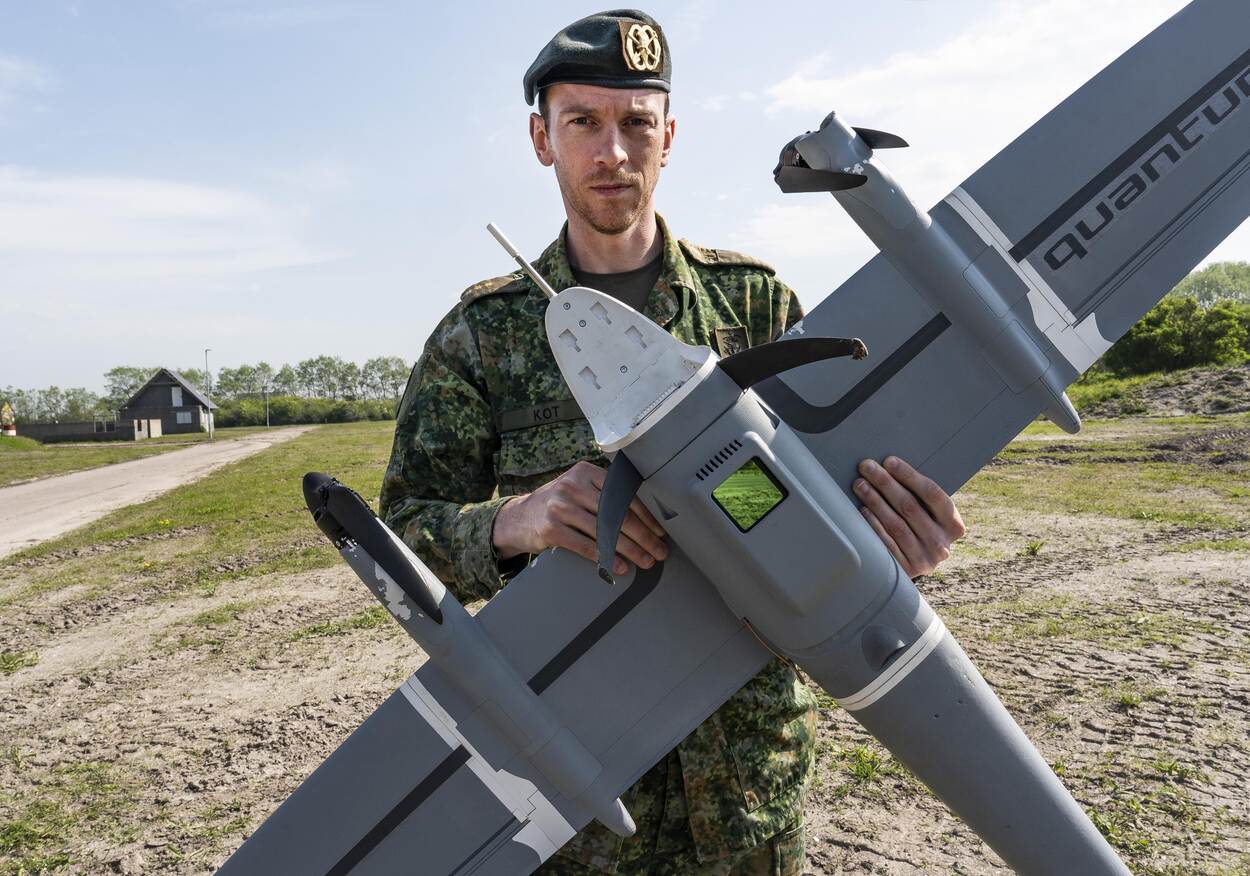
German Military Grounds Quantum Systems Drones Following Reported Cyberattack
The German defense firm Quantum Systems has confirmed that it was the target of a cyberattack in late October 2026. The company, which specializes in the production of reconnaissance and interceptor drones, stated that its internal security teams identified and contained the breach shortly after it began. While the firm has engaged both internal and external cybersecurity experts to…
Tor Updates DoS Defenses Again as Relay Attacks Continue
The Tor Project has released version 0.4.9.17 of its core software, marking a rapid escalation in the organization’s efforts to mitigate a persistent distributed denial-of-service (DDoS) campaign targeting its volunteer-run relay network. This latest update, announced on November 13, 2026, specifically addresses vulnerabilities in how the network’s built-in denial-of-service protections handle…
Microsoft pushes Windows emergency updates to fix activation failures
Microsoft has released a series of emergency out-of-band updates to address widespread Windows activation and licensing failures triggered by the company's November 2026 security patches. The issue specifically impacts enterprise environments that rely on the Software Licensing Management Tool, or Slmgr.vbs, to automate licensing processes.
Google Project Zero will disclose bugs after 90 days, fixed or not
Google’s Project Zero has announced a significant shift in its vulnerability disclosure policy, moving toward a more aggressive timeline for releasing technical details to the public. Under the new framework, dubbed Full X, the research team will disclose discovered vulnerabilities exactly X days after reporting them to a vendor, regardless of whether a patch has been developed or deployed.…
AI uncovers flaws in discontinued devices with no vendor left to patch them
Security researchers at Forescout have demonstrated that artificial intelligence can significantly lower the barrier to entry for discovering vulnerabilities in embedded software. By leveraging AI models alongside traditional security scanning tools, the team identified 99 vulnerabilities across 10 different TCP/IP stacks, which are essential components for network communication in industrial,…
YARA-X 1.23.0 Release, (Sun, Nov 15th)
The latest release of YARA-X, version 1.23.0, has been officially deployed, introducing a series of updates aimed at refining the tool's performance and stability. According to the release documentation, this iteration incorporates four distinct functional improvements alongside a collection of 16 bug fixes designed to address previously identified issues within the codebase.
Stolen Fireworks AI Key Led to Cursor Data Breach and Trojanized Claude Code Extension
The compromise of the official Claude Code extension hosted on the Cursor marketplace has been traced back to the theft of an access key originating from a security incident at Fireworks AI. According to a recent update from Cursor, an unauthorized actor obtained an access key that had been issued to Fireworks AI. This key, which was exposed following a breach at the third-party provider,…