
rce news
15 stories
SolarWinds Patches ARM Hard-Coded Key Flaw Enabling Unauthenticated RCE
SolarWinds has released a patch for a critical vulnerability in its Access Rights Manager (ARM) software. The flaw, designated CVE-2026-28299, enables unauthenticated remote code execution. This issue stems from the presence of a hard-coded static key within the software. All versions of ARM preceding 2026.2.1 are affected by this vulnerability.
CISA: WatchGuard RCE flaw now exploited in ransomware attacks
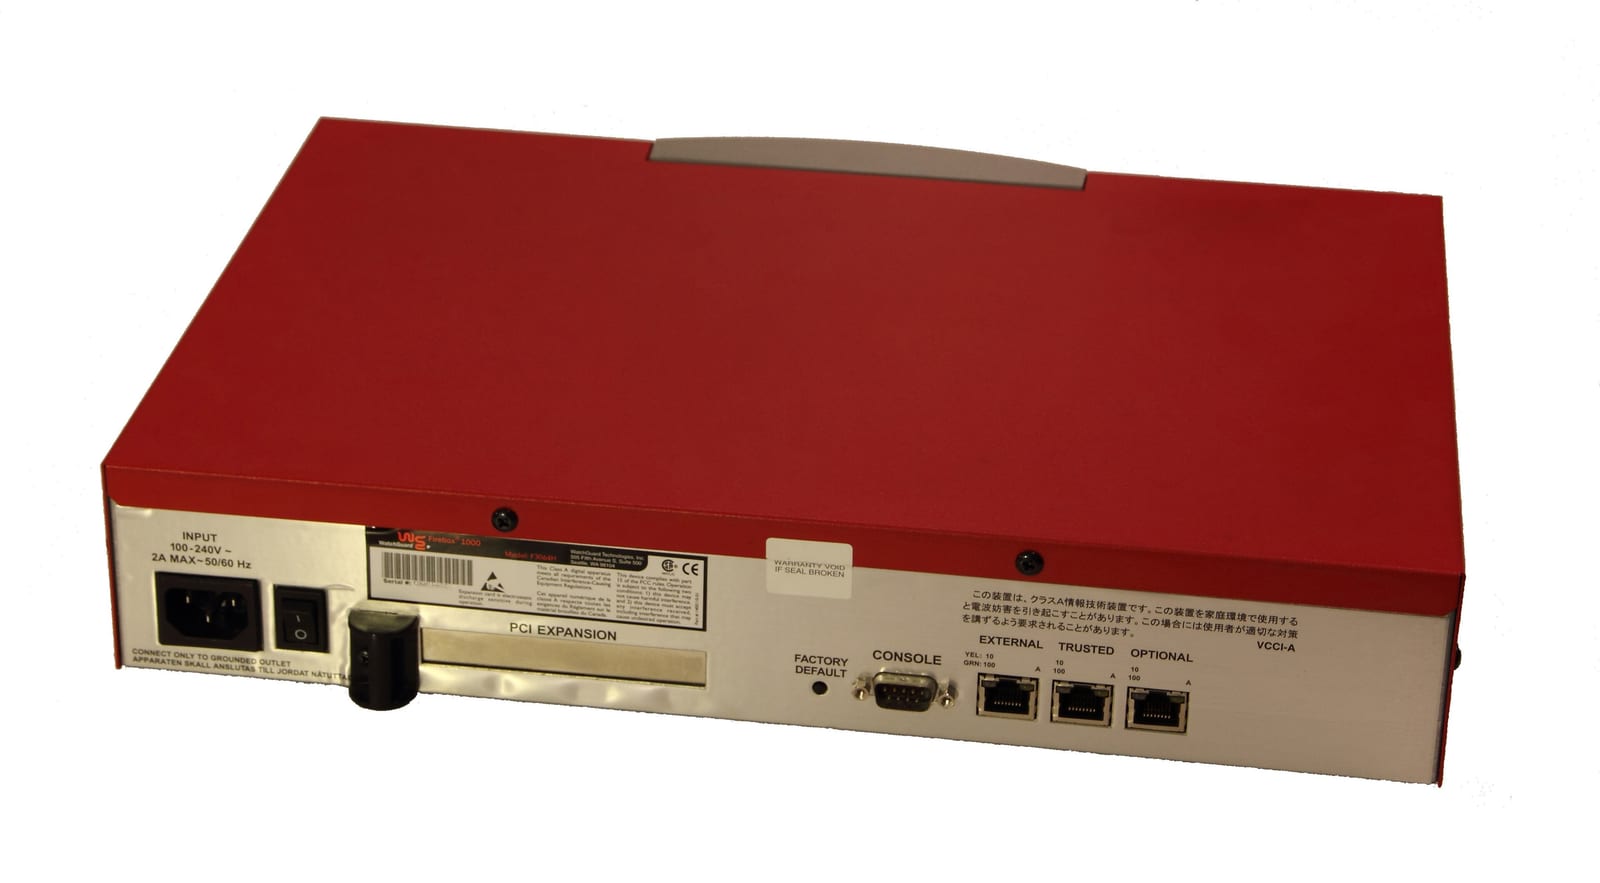
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has confirmed that a critical remote code execution (RCE) vulnerability in WatchGuard Firebox firewalls, tracked as CVE-2025-14733, is now being exploited by ransomware groups. CISA added this flaw to its Known Exploited Vulnerabilities (KEV) catalog in December, at which point it was already being actively exploited.
HPE Patches Critical RCE Vulnerabilities in AOS-CX
Hewlett Packard Enterprise (HPE) has issued security updates to mitigate critical remote code execution (RCE) vulnerabilities identified in its ArubaOS-CX operating system. These vulnerabilities, which have been assigned the identifier CVE-2026-73749, pose a significant risk, as reflected by their CVSS score of 9.8.
Rapid7 Analysis: Microsoft SharePoint Remote Code Execution (CVE-2026-63520)
A remote code execution (RCE) vulnerability, identified as CVE-2026-63520, has been disclosed in Microsoft SharePoint, allowing an authenticated attacker to execute arbitrary code on a vulnerable server. When chained with an authentication bypass vulnerability, CVE-2026-55040, the exploit becomes unauthenticated.
Cl0p Targets 40+ Organizations Through PTC Windchill Flaw
The Cl0p ransomware group claims to have compromised over 40 organizations by exploiting a critical vulnerability in PTC's Windchill and FlexPLM product lifecycle management (PLM) software. This vulnerability, identified as CVE-2026-12569, is a remote code execution (RCE) flaw with a CVSS score of 9.3, stemming from the deserialization of untrusted data. It affects all CPS versions and…
Isolated-vm Flaw Lets Sandboxed JavaScript Escape to Host for Potential RCE
A significant security vulnerability has been identified in the isolated-vm Node.js library, which could allow sandboxed JavaScript code to escape its intended isolation and potentially achieve arbitrary code execution on the host system. The flaw specifically impacts the ExternalCopy component of the library.
Forminator WordPress Plugin Vulnerable to Remote Code Execution
A critical remote code execution (RCE) vulnerability has been reported in the Forminator WordPress plugin, a tool utilized by over 600,000 websites. The flaw reportedly allows unauthenticated attackers to execute arbitrary code on affected sites. This vulnerability carries a high severity rating, indicating a significant risk to the integrity and security of websites employing the plugin.
Metasploit Wrap Up: Lot of summer shells and fit http profiles
Metasploit has released a significant update, introducing thirteen new modules that address a variety of vulnerabilities, including several remote code execution (RCE) flaws. The update also brings enhancements to the framework's capabilities, such as support for HTTP malleable profiles and improved functionality for Windows on ARM architectures.
ClamAV Vulnerability Allows Remote Code Execution
Cisco has released an update for ClamAV to address a critical vulnerability that could allow remote code execution. The flaw, identified as CVE-2026-20215, affects the open-source antivirus engine and stems from an integer overflow during the parsing of 7z archive files.
CISA Adds Progress LoadMaster Command Injection Flaw to KEV Catalog
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical vulnerability in Progress LoadMaster products, identified as CVE-2026-8037, to its Known Exploited Vulnerabilities (KEV) catalog. This addition mandates that federal agencies address the flaw by August 10, 2026.
Rapid7 Analysis: Unauthenticated Remote Code Execution in JetBrains TeamCity (CVE-2026-63077)
On July 27, 2026, JetBrains issued a security advisory for CVE-2026-63077, a critical unsafe deserialization vulnerability affecting its TeamCity product. This flaw allows an unauthenticated attacker to achieve remote code execution by exploiting the agent polling protocol. An attacker capable of reaching a TeamCity server via HTTP or HTTPS can execute operating system commands with the…
Critical RCE Vulnerability in WordPress Core Affects Millions of Sites
A critical unauthenticated remote code execution vulnerability, identified as CVE-2026-63030, has been discovered in WordPress Core, affecting millions of websites globally. The vulnerability allows an attacker to execute arbitrary code without authentication through the WordPress REST API batch endpoint, potentially leading to a complete compromise of the affected website and its data.
Cloudflare WAF Shields WordPress From Critical RCE and SQL Injection Flaws
Cloudflare has confirmed that its Web Application Firewall (WAF) successfully mitigated attacks targeting two critical vulnerabilities in WordPress and its plugins. The vulnerabilities, identified as CVE-2023-50387 and CVE-2024-21724, could lead to remote code execution (RCE) and SQL injection, respectively.
Microsoft SharePoint Server RCE Vulnerability Exploited in the Wild
Microsoft has confirmed active exploitation of a critical remote code execution (RCE) vulnerability, CVE-2026-58644, affecting on-premises deployments of its SharePoint Server. The vulnerability, which stems from the deserialization of untrusted data (CWE-502), allows an unauthenticated attacker to execute arbitrary code with a CVSS v3.1 score of 9.8 (Critical).
Weekly Metasploit Update: Modules for SMB-to-Meterpreter, Peyara Remote Mouse RCE exploit, and more
Metasploit Framework has received an update, version 6.4.142, introducing new modules and enhancements. Among the additions is a module that allows for the upgrade of existing SMB sessions to Meterpreter sessions, a capability that can be initiated via the command `sessions -u session_id` or by loading the `windows/manage/smb_to_meterpreter` module. This feature, developed by Dean Welch,…