LIVE · cybersecurity feed
Live wire
CVE-2026-103898 · Wpmet wp_social_login_and_register_social_counter Flaw Exploited Upon DisclosureCVE-2026-116512 · weDevs wp_project_manager Flaw Exploited Before CVE PublicationCVE-2026-119096 · Uncanny Toolkit for LearnDash Improper Authentication Exploited on DisclosureCVE-2010-20125 · DedeCMS Vulnerability CVE-2010-20125 Exploited On Day Of DisclosureCVE-2015-20130 · Netsweeper Improper Neutralization Flaw Exploited Upon DisclosureCVE-2025-31704 · Dahua Intelligent Connection Center Flaw Exploited on Day of DisclosureCVE-2026-103039 · Gravity Forms Deserialization Flaw Exploited Upon DisclosureCVE-2026-118539 · Drupal Commerce Core Access Bypass Exploited Before CVE PublicationThe Fridge-Hacking Spree Is an Internet-of-Things Wake-Up CallCVE-2026-19868 · U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog
vulnerability

Anthropic Fast-Tracks AI Bug Reports to OSS Maintainers, Taps 11 Firms for OT Security

Anthropic has reportedly initiated a program to fast-track AI-generated vulnerability reports to open-source software (OSS) maintainers. This new system, dubbed "OSS Scanner," is designed to automatically generate and dispatch bug reports. The reports are sent directly to maintainers who have opted into the program, raising questions about the review process for these AI-generated findings.

ZeroDay News ·

Source: SecurityWeek

Anthropic has reportedly initiated a program to fast-track AI-generated vulnerability reports to open-source software (OSS) maintainers. This new system, dubbed "OSS Scanner," is designed to automatically generate and dispatch bug reports. The reports are sent directly to maintainers who have opted into the program, raising questions about the review process for these AI-generated findings.

The core mechanism of the OSS Scanner involves an unreviewed, model-generated process for identifying potential vulnerabilities. While the specific AI model or scanning techniques employed were not detailed, it can be inferred that the system leverages artificial intelligence to analyze open-source codebases for common security weaknesses. The output of this analysis is then formatted into a bug report and sent to the relevant project maintainers. The "unreviewed" aspect suggests that human verification of the AI's findings may not occur before the reports are disseminated.

The affected parties are open-source software projects and their maintainers who choose to opt into this reporting system. The scope of projects covered by the OSS Scanner is likely broad, encompassing a wide array of open-source libraries, frameworks, and applications. Products in this category commonly rely on community contributions and often have varying levels of dedicated security auditing.

For maintainers, receiving automated vulnerability reports could potentially accelerate the discovery and patching of security flaws. However, the lack of human review for these AI-generated reports introduces a risk of false positives, which could consume valuable maintainer time and resources in investigating non-existent issues. This class of automated reporting systems typically requires careful tuning to balance the detection rate with the accuracy of findings.

Typical mitigation guidance for maintainers receiving such reports would involve a robust internal process for triaging and validating incoming bug reports, regardless of their source. This includes reproducing reported issues, verifying their impact, and prioritizing fixes based on severity. For AI-generated reports specifically, maintainers might need to develop additional heuristics or tools to quickly filter out potential false positives.

In a broader context, this initiative reflects a growing trend of leveraging artificial intelligence in cybersecurity, particularly for automated vulnerability discovery and reporting. While AI offers the promise of scaling security efforts and identifying flaws more rapidly, the effectiveness and trustworthiness of such systems depend heavily on their accuracy and the human oversight integrated into their workflows. The balance between automation efficiency and the potential for noise or misinformation remains a critical consideration in the deployment of AI in security.

Separately, the report also mentions Anthropic's engagement with 11 firms for Operational Technology (OT) security, though no further details regarding this initiative were provided. This suggests a broader security focus for the company beyond just software vulnerabilities.
vulnerabilityai
ShareXLinkedInWhatsAppFacebook

More News

view all →
CVE-2026-103898high

Wpmet wp_social_login_and_register_social_counter Flaw Exploited Upon Disclosure

The Wpmet wp_social_login_and_register_social_counter plugin vulnerability CVE-2026-103898 was identified as exploited on the same day it was published.

CVE-2026-116512high

weDevs wp_project_manager Flaw Exploited Before CVE Publication

The weDevs wp_project_manager plugin was identified as under exploitation one day before the CVE was officially published, leaving users with no patch window.

CVE-2026-119096high

Uncanny Toolkit for LearnDash Improper Authentication Exploited on Disclosure

The Uncanny Toolkit for LearnDash plugin was identified as exploited on the same day its CVE was published, leaving no window for remediation.

CVE-2010-20125high

DedeCMS Vulnerability CVE-2010-20125 Exploited On Day Of Disclosure

The DedeCMS vulnerability CVE-2010-20125 was identified as exploited on the same day it was published, leaving no window for remediation.

breach

Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches

A series of cyberattacks between late September and early October 2026 resulted in the compromise of seven South Korean financial institutions. The breaches led to the exposure of sensitive personal, employment, income, and loan-related data belonging to approximately 66,000 individuals and 2,200 corporations. Security researchers have linked these incidents to the use of an open-source…

finance

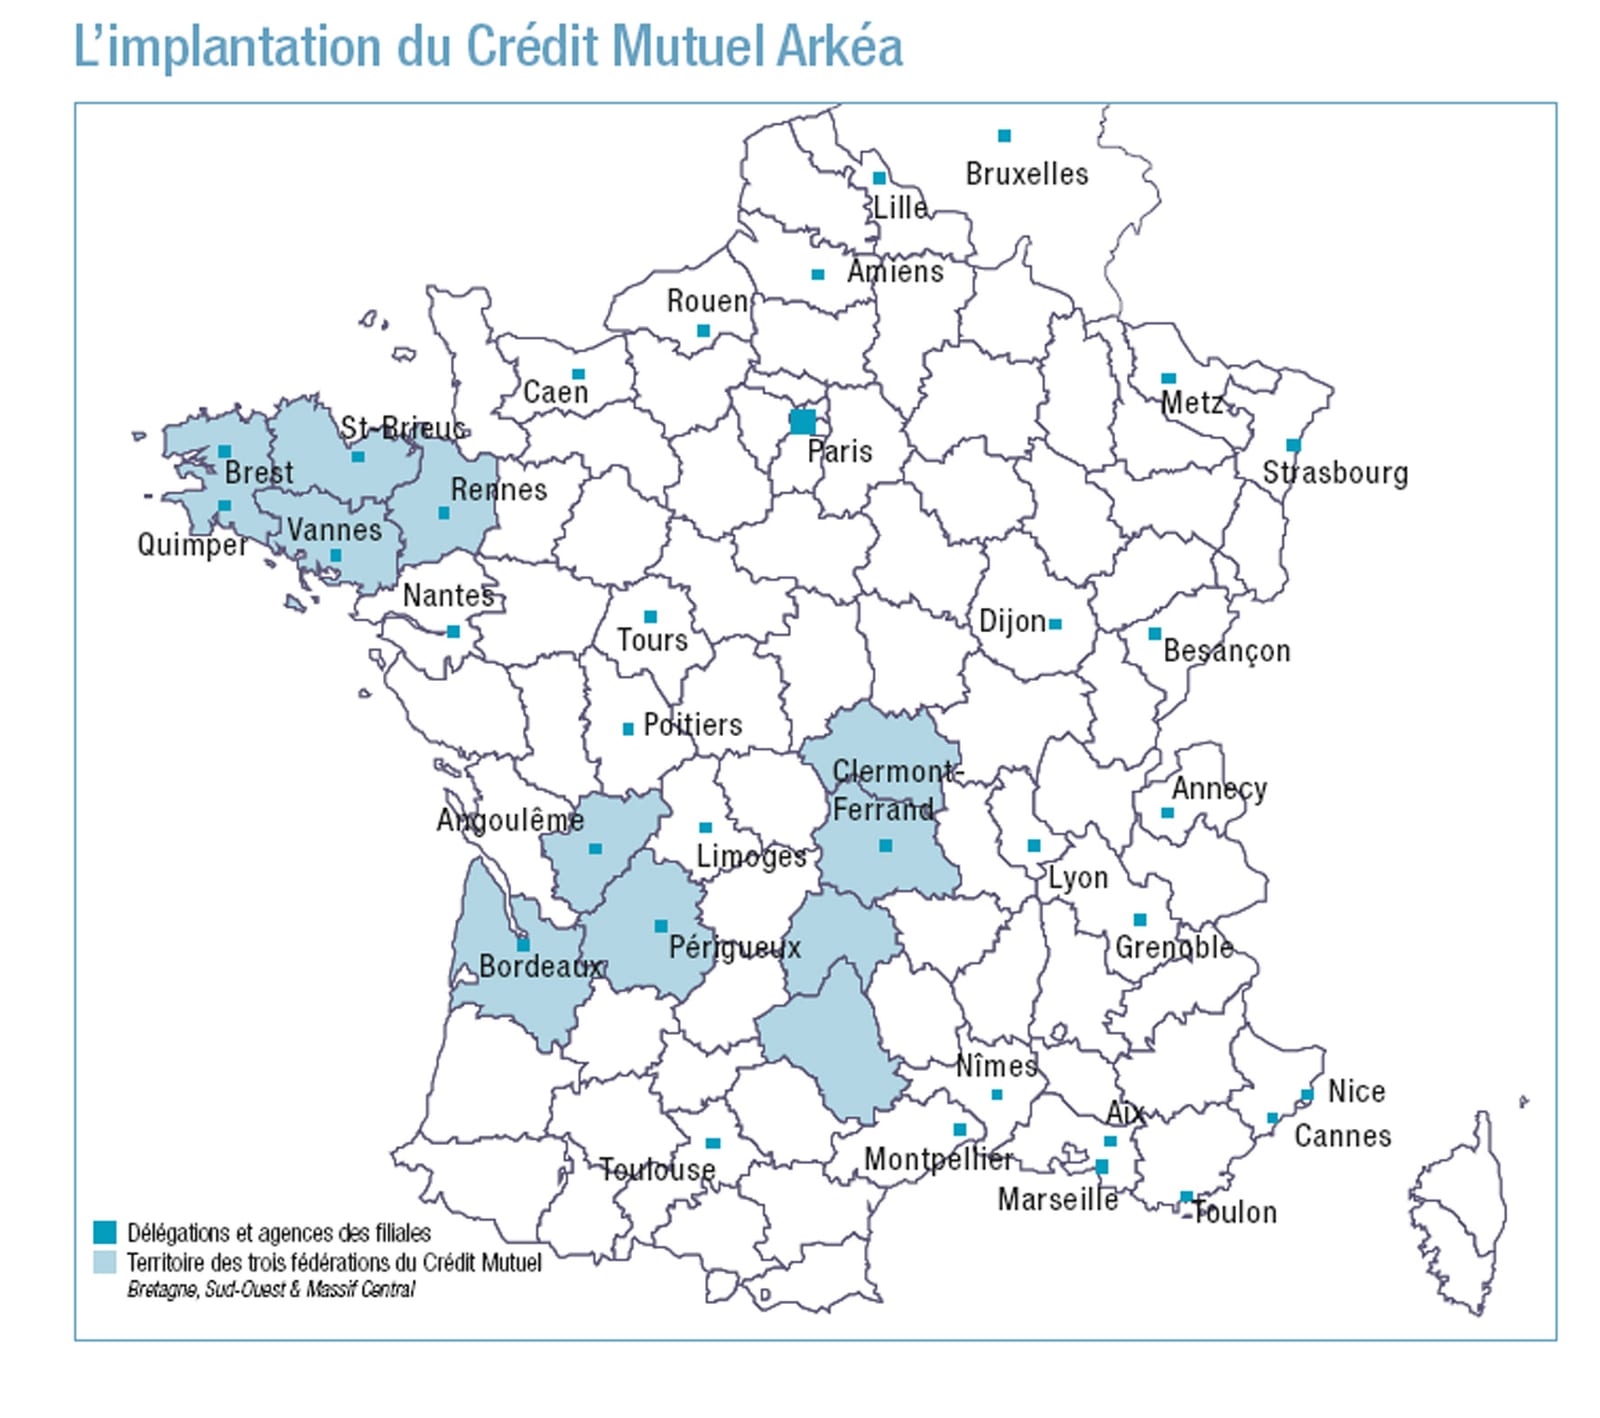
Hackers pull off $133 million French bank heist via service provider

The French cooperative banking group Credit Mutuel Arkea has confirmed it was the target of a sophisticated cyberattack that resulted in unauthorized financial transactions. While the bank has not officially verified the exact figure, independent investigators have estimated the total loss at approximately 118 million euros, or 133 million dollars. The incident, which came to light following…