
LIVE · cybersecurity feed
Live wire
phishing

Bogus recruiters go after high-value corporate credentials on mobile

A sophisticated phishing campaign is targeting high-value corporate credentials through fake job recruitment schemes, leveraging a technique known as browser-in-the-browser (BitB) to deceive victims. The attackers impersonate human resources staff from well-known companies, crafting convincing interview scheduling flows designed to steal corporate passwords.

ZeroDay News ·

Source: Help Net Security

A sophisticated phishing campaign is targeting high-value corporate credentials through fake job recruitment schemes, leveraging a technique known as browser-in-the-browser (BitB) to deceive victims. The attackers impersonate human resources staff from well-known companies, crafting convincing interview scheduling flows designed to steal corporate passwords.

Researchers tracking the activity observed that the phishing kit employs strict pre-qualification logic, rejecting personal email addresses and only accepting corporate credentials. This deliberate targeting ensures that threat actors gain access to high-value enterprise accounts, which can then provide immediate access to OAuth tokens, internal communications, and cloud applications, facilitating rapid lateral movement within an organization.

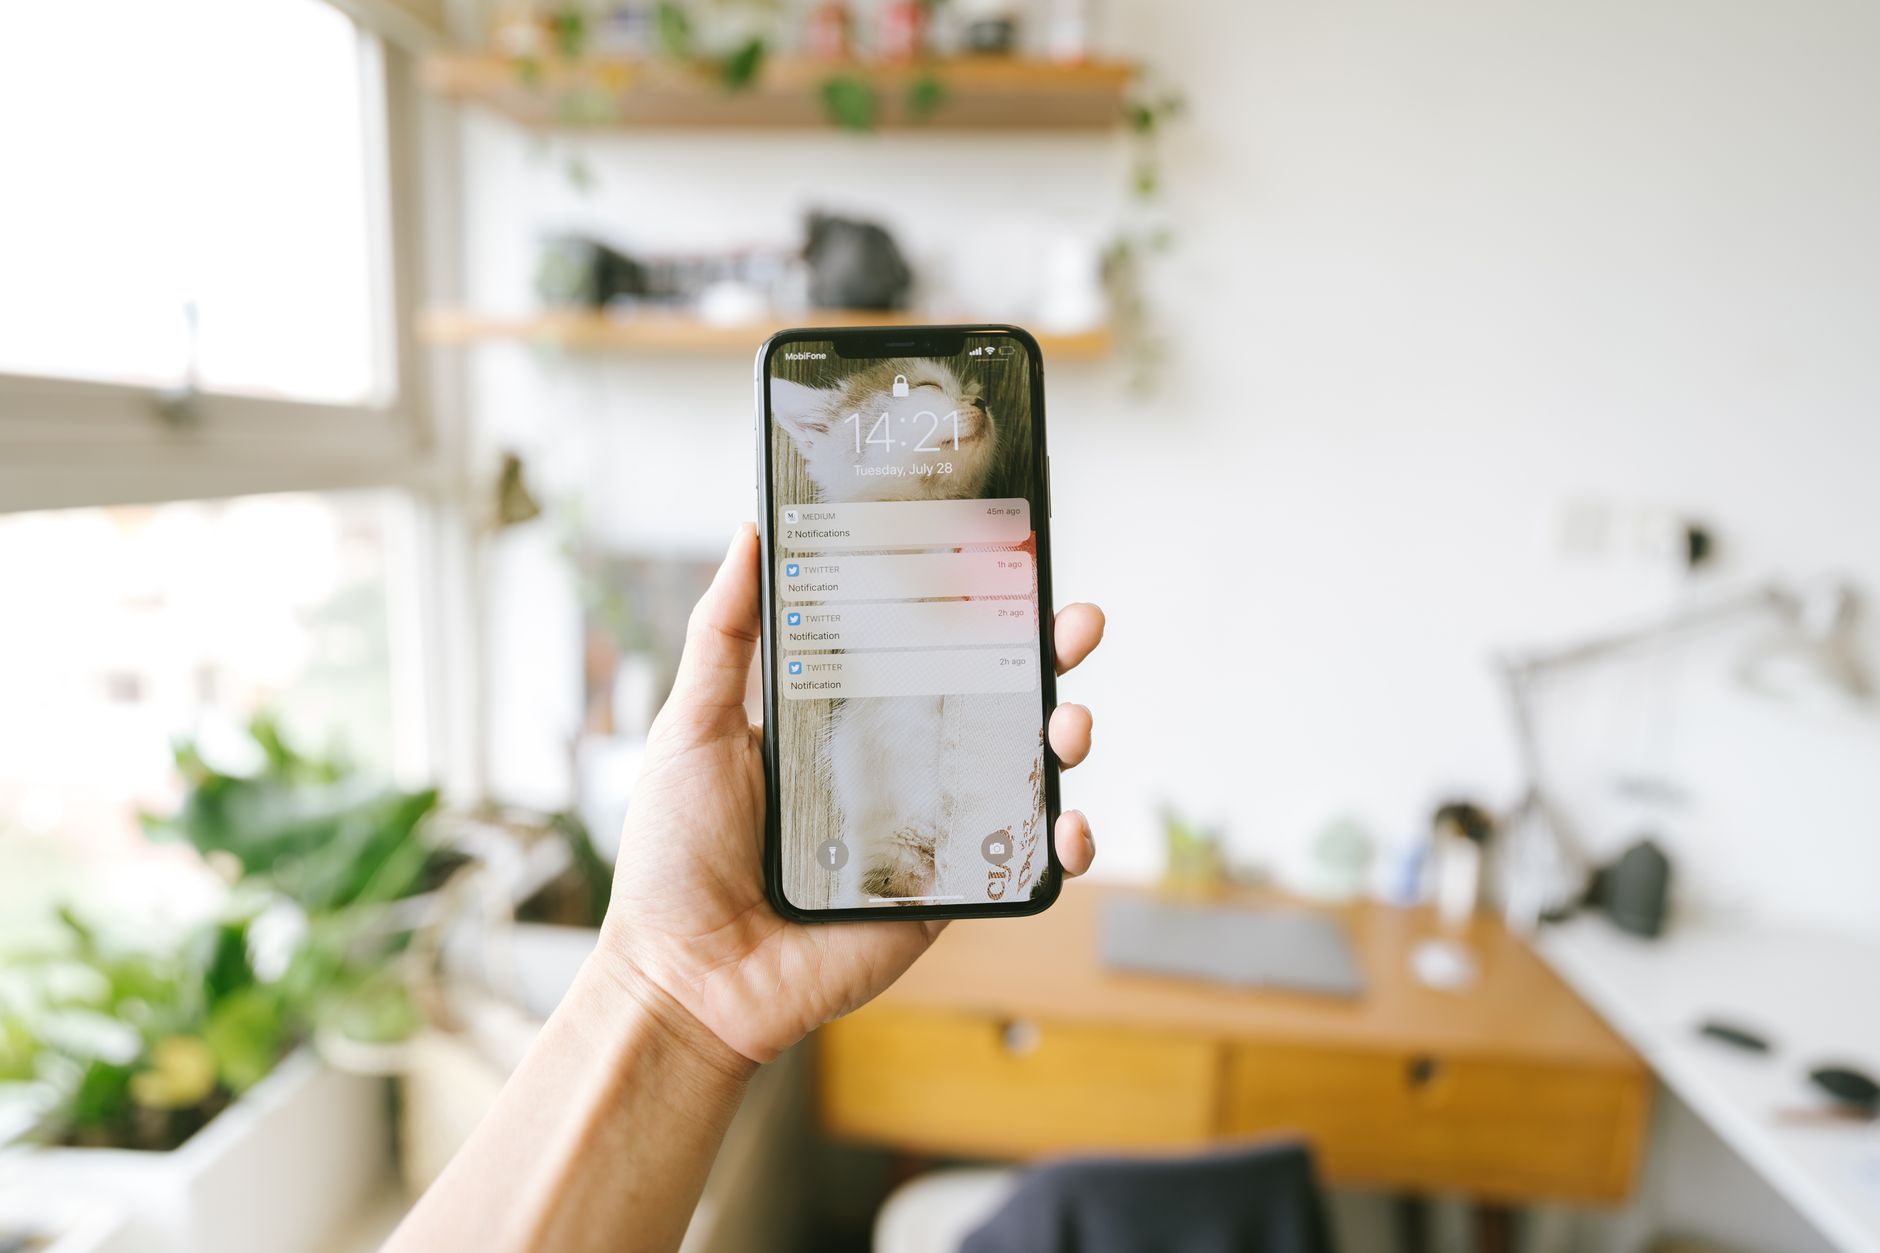
While the BitB technique can mimic an entire browser window, including the address bar, on desktop systems to make a fake login page appear genuine, its application differs on mobile devices. On phones, where there is no visible browser window or address bar to begin with, the kit switches to a full-screen fake login page, removing any visual cues a victim might use to verify authenticity.

The campaign has been active for at least a year, with researchers tracking numerous domains impersonating major brands. These domains often follow patterns such as "[company]-careers.com" or "[company]-global.com." The infrastructure supporting these malicious domains shows less variation than might be expected, frequently utilizing the same hosting and cloud providers. Amazon Web Services and SEDO GmbH were identified as common providers at the Autonomous System Number (ASN) level.

Domain blocklists often struggle to keep pace with the rapid registration of new lookalike domains on these shared networks, creating a window of vulnerability before fake sites are flagged. Researchers have published 46 previously undisclosed indicators of compromise related to this activity.

The impersonated brands span a wide range of industries, including e-commerce, luxury goods, aviation, and retail. Companies whose names have been caught up in the scheme include Amazon, Louis Vuitton, Apple, FIFA, Emirates Group, Boeing, Heineken, Deloitte, Central Network Retail Group, and Lego.

Defending against these targeted campaigns necessitates a shift in security focus beyond traditional desktop-centric web gateways. Securing corporate identities at the mobile touchpoint is crucial to mitigate the risks posed by these evolving phishing tactics.


phishing
ShareXLinkedInWhatsAppFacebook

More News

view all →
security

Canadian cybersecurity executive arrested in federal extortion case

A Canadian cybersecurity executive was arrested in Pennsylvania on Thursday, facing federal charges of conspiracy to commit extortion. Edward Dubrovsky, 54, a co-founder and former Chief Operating Officer of CYPFER, a firm specializing in ransomware negotiation, is charged with conspiring to threaten the confidentiality of information for extortion and conspiring to commit Hobbs Act extortion,…

breach

Criminal IP Introduces AITEM as the Next Evolution of Attack Surface Management

AI SPERA, the company behind the cyber threat intelligence platform Criminal IP, has announced AITEM (AI-Powered Threat Exposure Management), an expansion of its Attack Surface Management (ASM) offerings. AITEM aims to move beyond traditional asset discovery to provide a more comprehensive approach to understanding, prioritizing, and responding to security exposures. The platform is scheduled…

ai

AI Is Getting Really Good at Messing With Cybercriminals

Anti-cybercrime initiatives are increasingly deploying artificial intelligence to disrupt scammers by engaging them with lifelike bots, which the criminals mistake for genuine victims. This strategy aims to waste scammers' time and resources while gathering intelligence on their operations.

ransomware

FBI Arrests Ransomware Negotiation Firm Co-Founder in ShinyHunters Probe

The Federal Bureau of Investigation (FBI) has reportedly arrested Edward Dubrovsky, a co-founder of the ransomware negotiation firm Cypfer and currently associated with CyberSteward. The arrest is said to be part of the ongoing ShinyHunters investigation, specifically in connection with an incident involving FBI job applicant data.

ai

The Third-Party Agent Problem: Why Security Built for AI You Chose Misses the Agents You Didn't

A new report highlights a significant blind spot in enterprise security architectures concerning the proliferation of third-party AI agents. The forthcoming 2026 State of Agent Security Report indicates that current security models, often designed to protect AI systems directly chosen and deployed by an organization, frequently fail to account for AI capabilities embedded within third-party…

security

Insider Cyber Extortion Plot Against Industrial Firm Lands Engineer in Prison

A former core infrastructure engineer has been sentenced to prison for an attempted cyber extortion plot against an industrial firm. The engineer reportedly deleted administrative accounts and reset hundreds of user passwords, subsequently demanding a ransom of 20 Bitcoin to prevent further disruption to the company's servers.



