
LIVE · cybersecurity feed
Live wire
breach

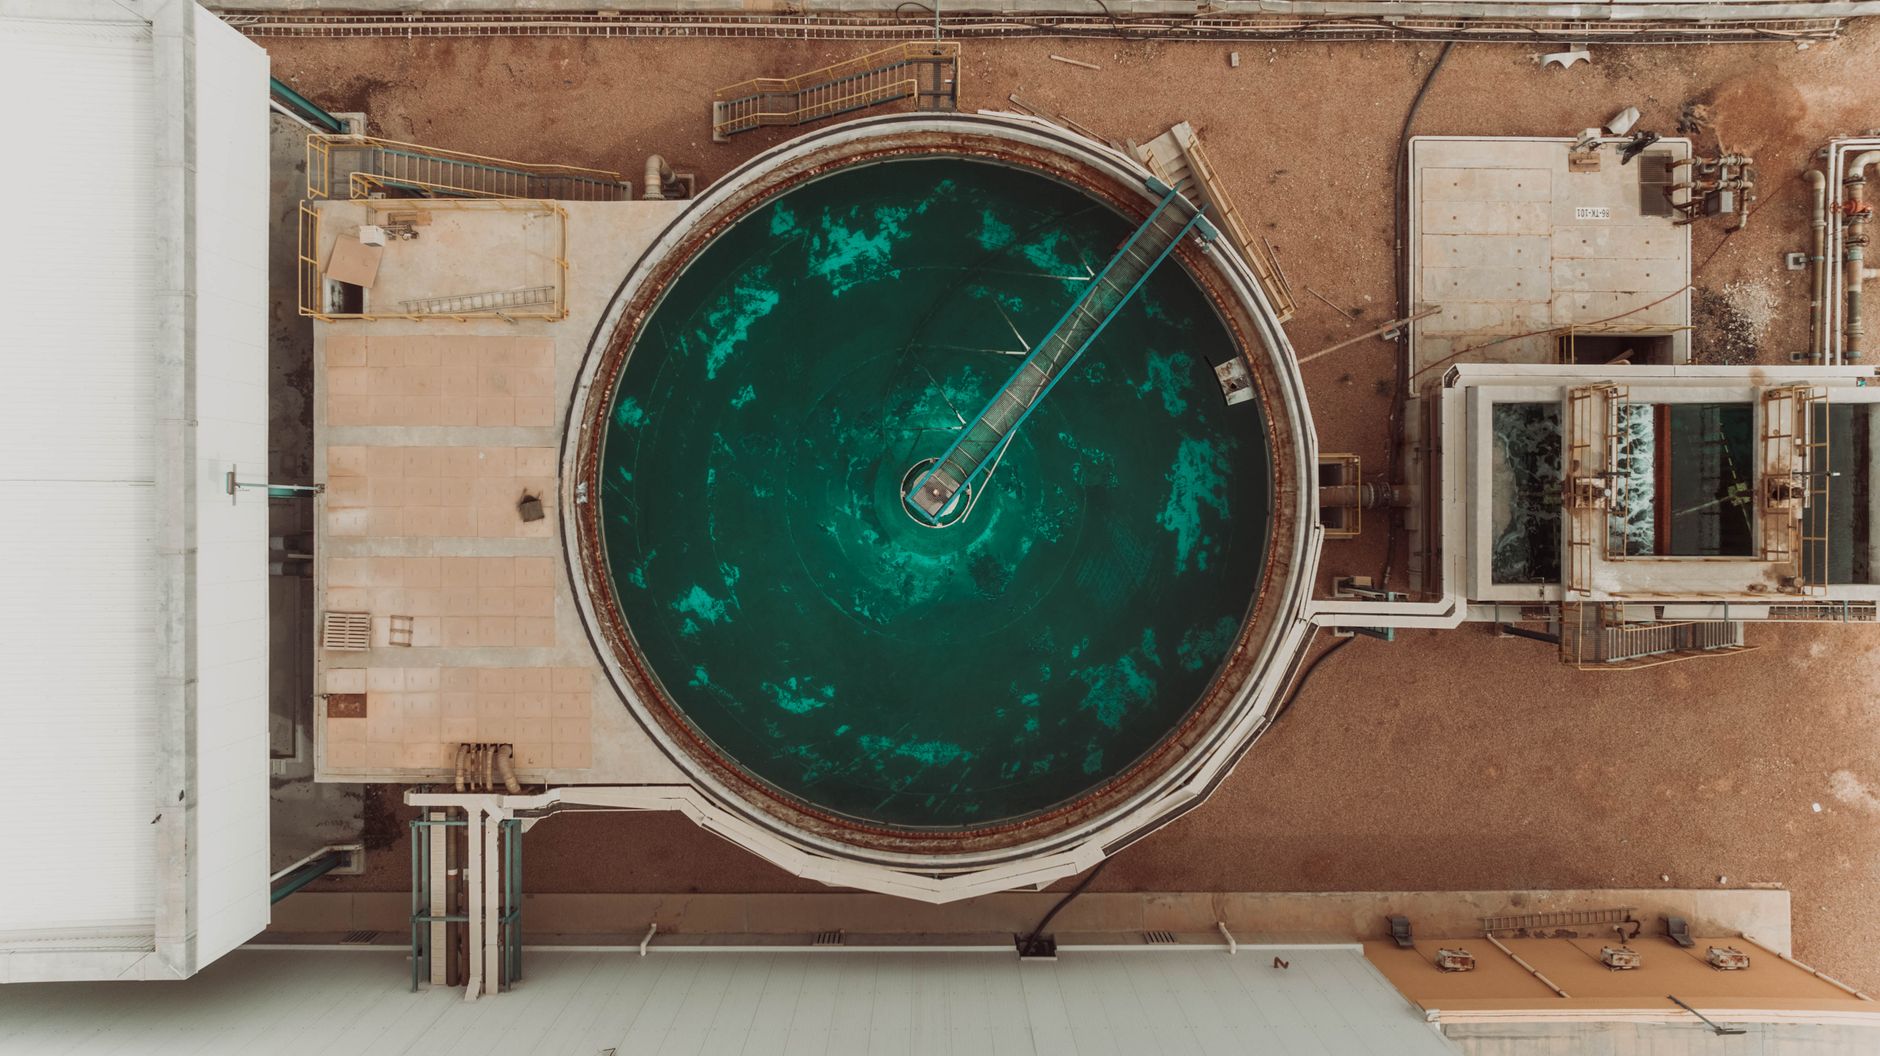
CISA warns of cyberattacks disrupting U.S. water utilities

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent alert regarding a significant increase in cyberattacks targeting internet-exposed programmable logic controllers (PLCs) within the water and wastewater systems sector. This warning follows a series of disruptions affecting over 30 community water systems in Minnesota, with attacks commencing last Sunday and…

ZeroDay News ·

Source: BleepingComputer

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent alert regarding a significant increase in cyberattacks targeting internet-exposed programmable logic controllers (PLCs) within the water and wastewater systems sector. This warning follows a series of disruptions affecting over 30 community water systems in Minnesota, with attacks commencing last Sunday and continuing into Monday.

CISA's bulletin details that threat actors are exploiting exposed PLCs to change passwords, locking out operators, and modifying IP addresses to disconnect devices from the internet, among other actions that disrupt operations. The agency emphasizes that organizations of all sizes, including those with mature cybersecurity programs, are being targeted.

A key concern highlighted by CISA is the presence of undocumented cellular modems, often installed by operators, vendors, or system integrators, which expose operational technology (OT) to the public internet. Such exposure can lead to defacement, configuration changes, operational disruptions, and even physical damage.

CISA strongly recommends the immediate removal of these internet-facing assets. Where direct removal is not feasible, organizations should implement secure access methods such as VPN connections or gateway devices. Additionally, the agency advises changing all default passwords and restricting access to an IP address allow-list. For owners of Rockwell Automation MicroLogix 1400 PLCs, CISA points to vendor guidance for recovering access if passwords have been altered.

Cybersecurity search firm Censys has quantified this exposure, identifying over 4,100 internet-exposed Rockwell Automation/Allen-Bradley hosts, 4,100 Siemens hosts, and more than 2,000 Schneider Electric hosts. Censys clarifies that while these devices are reachable over the public internet, this does not necessarily mean they are actively targeted or compromised. Many of the MicroLogix 1400 controllers mentioned by CISA appear to be running end-of-sale (EoS) firmware versions.

Censys also corroborated the issue of undocumented cellular modems, noting that nearly half of the exposed Rockwell devices are accessible via major cellular and internet service provider networks, including Verizon Business, AT&T, T-Mobile, Comcast, Charter, and Starlink. The firm has provided an expanded set of indicators of compromise (IoCs) and threat-hunting guidance in its report.

Earlier this week, Minnesota IT Services (MNIT) activated the state's cybersecurity incident response plan in response to what it described as a "coordinated cyberattack targeting operational technology at more than 30 Minnesota community water systems." Multiple municipalities reported equipment malfunctions caused by the attacks, forcing some utilities to temporarily switch to manual operations. MNIT has shared threat intelligence from affected systems and offered guidance to help utilities restore normal operations.


breach
ShareXLinkedInWhatsAppFacebook

More News

view all →
breach

Criminal IP Introduces AITEM as the Next Evolution of Attack Surface Management

AI SPERA, the company behind the cyber threat intelligence platform Criminal IP, has announced AITEM (AI-Powered Threat Exposure Management), an expansion of its Attack Surface Management (ASM) offerings. AITEM aims to move beyond traditional asset discovery to provide a more comprehensive approach to understanding, prioritizing, and responding to security exposures. The platform is scheduled…

security

Canadian cybersecurity executive arrested in federal extortion case

A Canadian cybersecurity executive was arrested in Pennsylvania on Thursday, facing federal charges of conspiracy to commit extortion. Edward Dubrovsky, 54, a co-founder and former Chief Operating Officer of CYPFER, a firm specializing in ransomware negotiation, is charged with conspiring to threaten the confidentiality of information for extortion and conspiring to commit Hobbs Act extortion,…

ai

AI Is Getting Really Good at Messing With Cybercriminals

Anti-cybercrime initiatives are increasingly deploying artificial intelligence to disrupt scammers by engaging them with lifelike bots, which the criminals mistake for genuine victims. This strategy aims to waste scammers' time and resources while gathering intelligence on their operations.

ransomware

FBI Arrests Ransomware Negotiation Firm Co-Founder in ShinyHunters Probe

The Federal Bureau of Investigation (FBI) has reportedly arrested Edward Dubrovsky, a co-founder of the ransomware negotiation firm Cypfer and currently associated with CyberSteward. The arrest is said to be part of the ongoing ShinyHunters investigation, specifically in connection with an incident involving FBI job applicant data.

ai

The Third-Party Agent Problem: Why Security Built for AI You Chose Misses the Agents You Didn't

A new report highlights a significant blind spot in enterprise security architectures concerning the proliferation of third-party AI agents. The forthcoming 2026 State of Agent Security Report indicates that current security models, often designed to protect AI systems directly chosen and deployed by an organization, frequently fail to account for AI capabilities embedded within third-party…

security

Insider Cyber Extortion Plot Against Industrial Firm Lands Engineer in Prison

A former core infrastructure engineer has been sentenced to prison for an attempted cyber extortion plot against an industrial firm. The engineer reportedly deleted administrative accounts and reset hundreds of user passwords, subsequently demanding a ransom of 20 Bitcoin to prevent further disruption to the company's servers.



