
LIVE · cybersecurity feed
Live wire
security

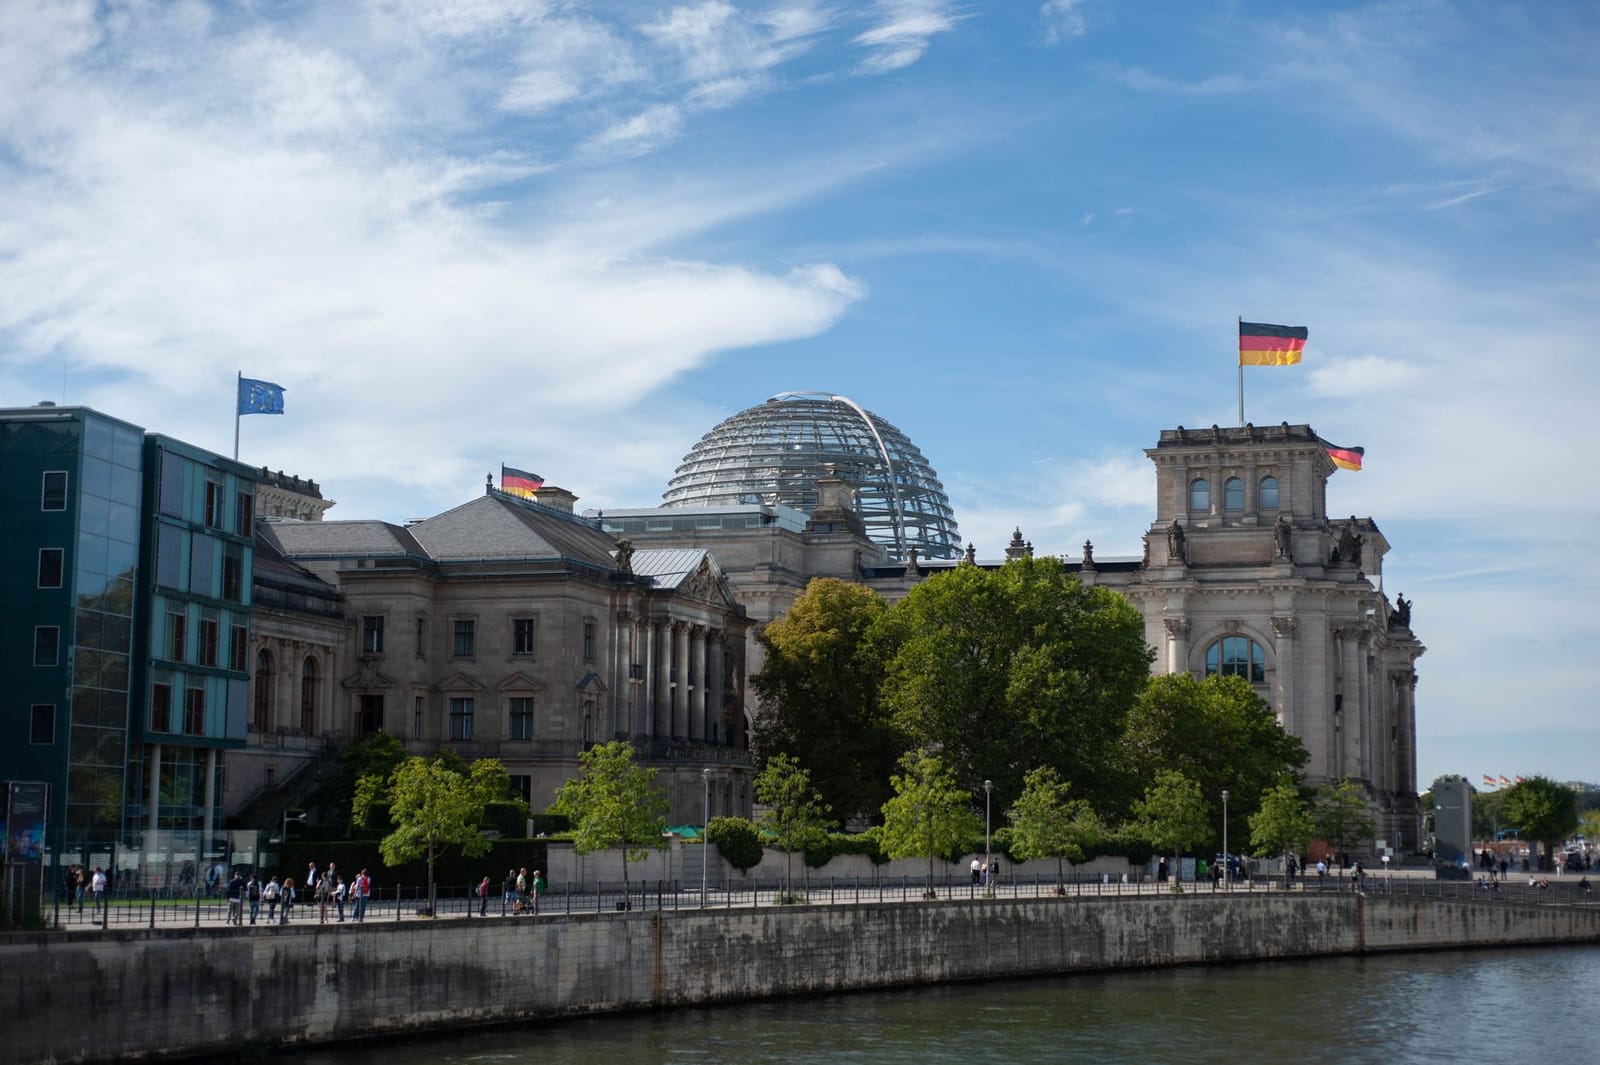
European parliament members call for slowdown of Serbia’s EU entry over spyware use

Twenty-nine members of the European Parliament (MEPs) are calling for a slowdown in Serbia's accession to the European Union, citing concerns over the Serbian government's alleged use of spyware against student activists and other targets. The MEPs' letter, issued on Friday, follows a report by the SHARE Foundation, Amnesty International, and The Citizen Lab at the University of Toronto, which…

ZeroDay News ·

Source: CyberScoop

Twenty-nine members of the European Parliament (MEPs) are calling for a slowdown in Serbia's accession to the European Union, citing concerns over the Serbian government's alleged use of spyware against student activists and other targets. The MEPs' letter, issued on Friday, follows a report by the SHARE Foundation, Amnesty International, and The Citizen Lab at the University of Toronto, which detailed the discovery of both Pegasus and NoviSpy spyware infections on the phones of Serbian student activists.

While the joint investigation did not attribute responsibility for the Pegasus infections, it stated that evidence related to the NoviSpy infections pointed to Serbian government authorities. The MEPs characterized the alleged surveillance as a "direct state attack on democracy," asserting that the regime of Aleksandar Vučić is employing illegal digital surveillance to systematically dismantle political opposition ahead of upcoming elections.

Among their demands, the MEPs are advocating for Serbia's EU accession process to be paused until an investigation into the country's spyware usage is completed. They also propose that accession be made contingent on demonstrable improvements in rule-of-law accountability. Additionally, the MEPs urged European Commission President Ursula von der Leyen to cancel a planned visit to Serbia.

The spyware allegations add to existing pressures on Belgrade. Enlargement Commissioner Marta Kos had already canceled her own visit to Serbia on Friday, reportedly due to outrage among European leaders over Serbia's response to the death of former Bosnian Serb army commander Ratko Mladić and alleged glorification of the war criminal.

One MEP who signed the letter, Hannah Neumann, indicated that while the spyware issue is significant, it is not the sole reason for the increased scrutiny. She noted that the European Parliament has been critical of the Serbian government for some time regarding its history of spyware use, and the latest revelations represent "another straw."

The MEPs' letter emphasized that "appeasement has failed" and called on the European Commission to demonstrate that compliance with fundamental democratic standards is a "non-negotiable requirement." The Serbian government did not respond to requests for comment regarding the allegations.

The calls for action against Serbia come amidst broader discussions within the EU regarding spyware abuses. Recent revelations of spyware found on the device of a member of the European Parliament's PEGA Committee have prompted renewed calls for the implementation of recommendations from that committee to address such issues across the continent.


ShareXLinkedInWhatsAppFacebook

More News

view all →
security

Canadian cybersecurity executive arrested in federal extortion case

A Canadian cybersecurity executive was arrested in Pennsylvania on Thursday, facing federal charges of conspiracy to commit extortion. Edward Dubrovsky, 54, a co-founder and former Chief Operating Officer of CYPFER, a firm specializing in ransomware negotiation, is charged with conspiring to threaten the confidentiality of information for extortion and conspiring to commit Hobbs Act extortion,…

breach

Criminal IP Introduces AITEM as the Next Evolution of Attack Surface Management

AI SPERA, the company behind the cyber threat intelligence platform Criminal IP, has announced AITEM (AI-Powered Threat Exposure Management), an expansion of its Attack Surface Management (ASM) offerings. AITEM aims to move beyond traditional asset discovery to provide a more comprehensive approach to understanding, prioritizing, and responding to security exposures. The platform is scheduled…

ai

AI Is Getting Really Good at Messing With Cybercriminals

Anti-cybercrime initiatives are increasingly deploying artificial intelligence to disrupt scammers by engaging them with lifelike bots, which the criminals mistake for genuine victims. This strategy aims to waste scammers' time and resources while gathering intelligence on their operations.

ransomware

FBI Arrests Ransomware Negotiation Firm Co-Founder in ShinyHunters Probe

The Federal Bureau of Investigation (FBI) has reportedly arrested Edward Dubrovsky, a co-founder of the ransomware negotiation firm Cypfer and currently associated with CyberSteward. The arrest is said to be part of the ongoing ShinyHunters investigation, specifically in connection with an incident involving FBI job applicant data.

ai

The Third-Party Agent Problem: Why Security Built for AI You Chose Misses the Agents You Didn't

A new report highlights a significant blind spot in enterprise security architectures concerning the proliferation of third-party AI agents. The forthcoming 2026 State of Agent Security Report indicates that current security models, often designed to protect AI systems directly chosen and deployed by an organization, frequently fail to account for AI capabilities embedded within third-party…

security

Insider Cyber Extortion Plot Against Industrial Firm Lands Engineer in Prison

A former core infrastructure engineer has been sentenced to prison for an attempted cyber extortion plot against an industrial firm. The engineer reportedly deleted administrative accounts and reset hundreds of user passwords, subsequently demanding a ransom of 20 Bitcoin to prevent further disruption to the company's servers.



