LIVE · cybersecurity feed
Live wire
shinyhuntersmedium

FBI Arrests Suspected ShinyHunters Operative

The Federal Bureau of Investigation (FBI) has reportedly arrested an individual suspected of involvement with the data-scraping group known as ShinyHunters. This development, while not yet widely covered, has been noted by industry observers as a significant event in the ongoing efforts against cybercrime.

ZeroDay News ·

Source: Dark Reading

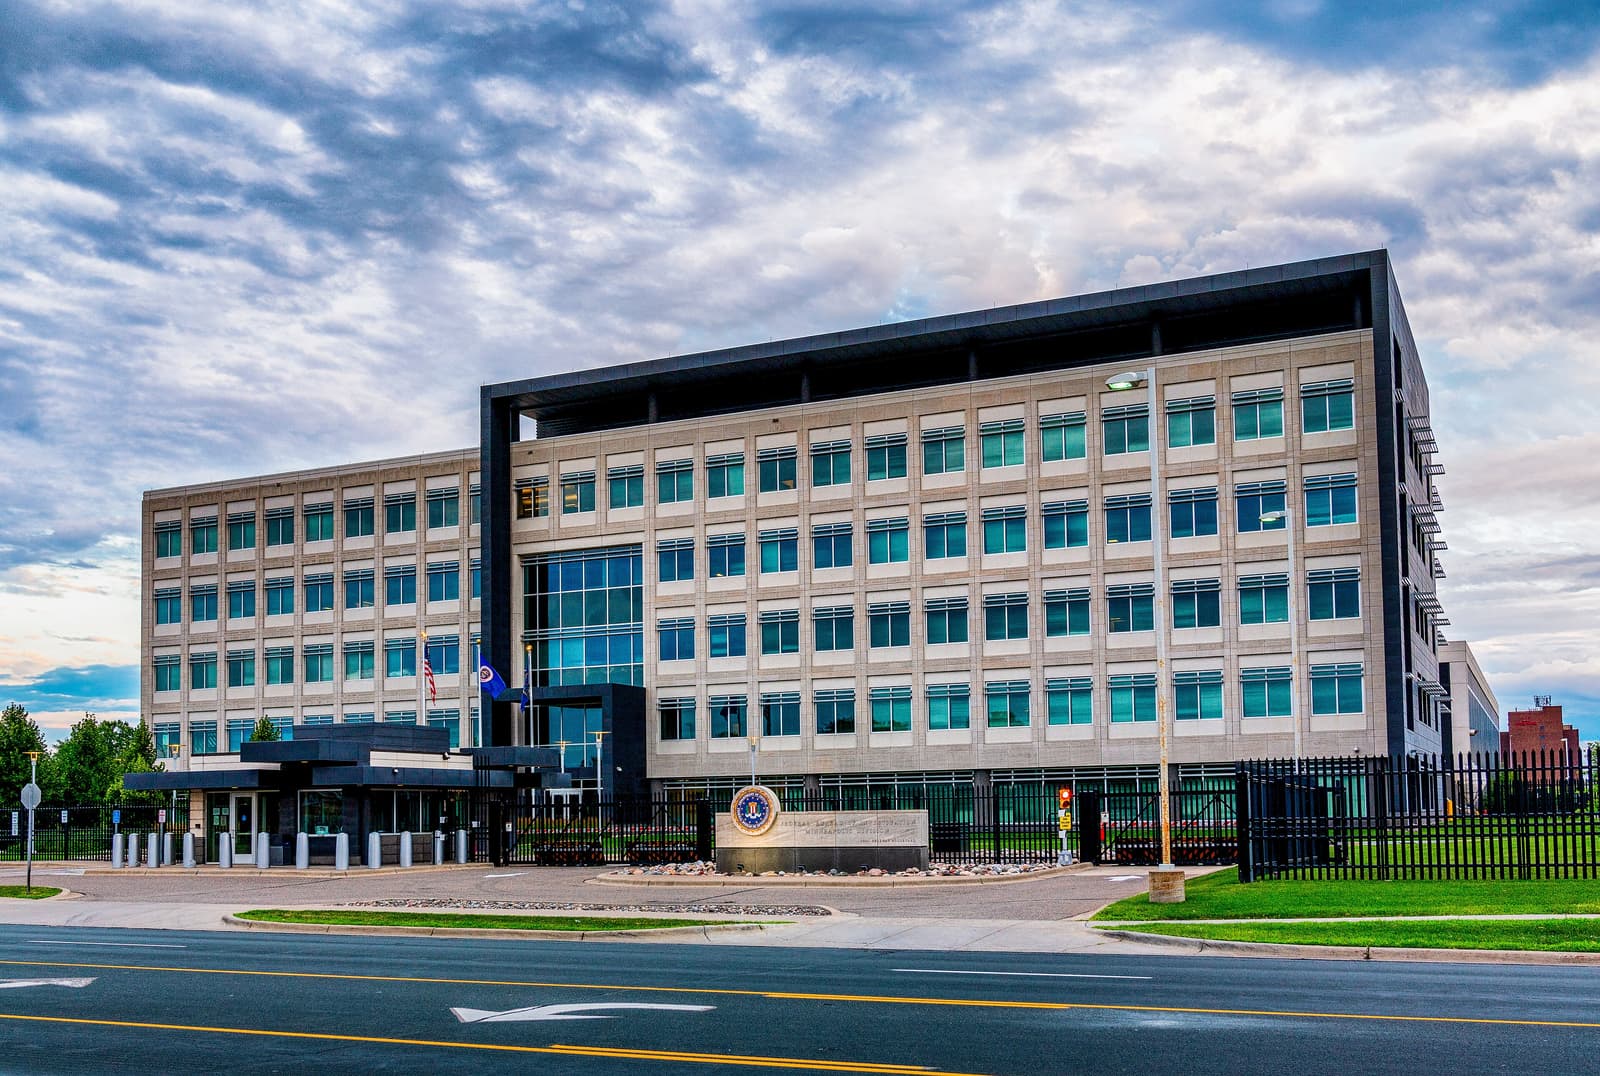
Photo: Tony Webster from Minneapolis, Minnesota, United States (CC BY-SA 2.0) via Wikimedia Commons

The Federal Bureau of Investigation (FBI) has reportedly arrested an individual suspected of involvement with the data-scraping group known as ShinyHunters. This development, while not yet widely covered, has been noted by industry observers as a significant event in the ongoing efforts against cybercrime.

ShinyHunters is a well-known cybercriminal group that has been active for several years, primarily focusing on data breaches and subsequent sale of stolen information. Their typical modus operandi involves compromising corporate networks, often through various initial access vectors such as phishing, exploiting unpatched vulnerabilities, or credential stuffing. Once inside, they exfiltrate large databases containing sensitive customer or employee information, which can include names, email addresses, passwords, and sometimes financial data.

The stolen data is then frequently advertised and sold on dark web forums and marketplaces. The monetization of these datasets is a core component of such groups' operations, with prices varying based on the volume, sensitivity, and recency of the information. Buyers of such data can range from other cybercriminals looking to conduct further attacks (e.g., credential stuffing, targeted phishing) to entities interested in competitive intelligence.

Law enforcement agencies, including the FBI, commonly employ a range of investigative techniques to identify and apprehend individuals associated with cybercriminal groups. These methods can include tracking cryptocurrency transactions, analyzing digital footprints left on compromised systems or dark web forums, leveraging intelligence from informants, and international cooperation with other law enforcement bodies. The arrest of an alleged operative suggests a potential breakthrough in understanding the group's internal structure and operational methods.

For organizations, the threat posed by groups like ShinyHunters underscores the critical importance of robust cybersecurity defenses. This includes implementing multi-factor authentication, regular patching and vulnerability management, employee security awareness training, and comprehensive network monitoring to detect and respond to unauthorized access attempts swiftly. Data encryption, both in transit and at rest, also serves as a vital control to mitigate the impact of successful data exfiltration.

This reported arrest highlights the persistent efforts by law enforcement to dismantle sophisticated cybercriminal organizations that pose a significant threat to businesses and individuals globally. Such actions aim to disrupt the financial incentives driving these groups and to hold accountable those involved in large-scale data theft and illicit data trade. It also serves as a reminder that while cyberattacks are digital, the individuals behind them are subject to real-world legal consequences.
shinyhuntersfbiarrestdata scraping
ShareXLinkedInWhatsAppFacebook

More News

view all →
ransomware

FBI Arrests Founder of Ransomware Negotiation Firm

Federal agents have arrested a Canadian cybersecurity professional in Pennsylvania, linking him to an ongoing investigation into the ShinyHunters hacking group. Edward Dubrovsky, co-founder of the Canadian firm CyberSteward, was taken into custody on October 8, facing charges of conspiracy to threaten to impair the confidentiality of information with intent to extort money, and interference…

saashigh

ASOS Breach Reveals the Risks in Customer-Facing SaaS

A recent security incident involving the British online fashion retailer ASOS has brought to light the inherent risks associated with customer-facing Software-as-a-Service (SaaS) platforms. The breach reportedly showcased how the compromise of a single user identity could serve as an initial access vector, subsequently allowing attackers to achieve broad penetration into a company's internal…

patch

Hackers abuse Google Ads, Bing redirects to push Claude ClickFix attacks

A new malvertising campaign, dubbed "Adception" by security researchers at Push Security, is leveraging Google Ads and Bing redirects to distribute fake Claude installers that deploy "ClickFix" attacks. The campaign was identified after researchers observed malicious Google ads targeting users searching for "claude mac."

cybersecurity

AI Fuels Cybersecurity Mergers and Acquisitions

The cybersecurity industry is currently undergoing a substantial wave of mergers and acquisitions (M&A), with 117 deals reported in the most recent quarter. A key driver behind this heightened activity appears to be the increasing integration of artificial intelligence (AI) across various sectors, leading to a broader range of companies seeking to acquire cybersecurity capabilities.

cloud

AWS AgentCore security undone by prompt requesting credentials

Researchers have identified a critical vulnerability in Amazon Bedrock AgentCore that could allow an attacker to compromise all agents within an AWS account and region by exploiting insufficient network isolation and overly permissive default IAM roles. The flaw, disclosed by Zenity Labs, centers on an attacker's ability to extract temporary AWS credentials from an agent through a single prompt.

security

Credential-Stealing GitHub Actions Workflows Planted in Tens of Thousands of Repositories

Cybersecurity researchers have reported an active credential-theft campaign leveraging GitHub Actions workflows, which has led to the compromise of tens of thousands of repositories. The campaign reportedly exploited two high-profile open-source maintainer accounts to propagate a malicious workflow into over 340 repositories directly. One notable instance involved the account of Takashi Kitao,…