LIVE · cybersecurity feed
Live wire
security

Friday Squid Blogging: On Squid Egg Sacs

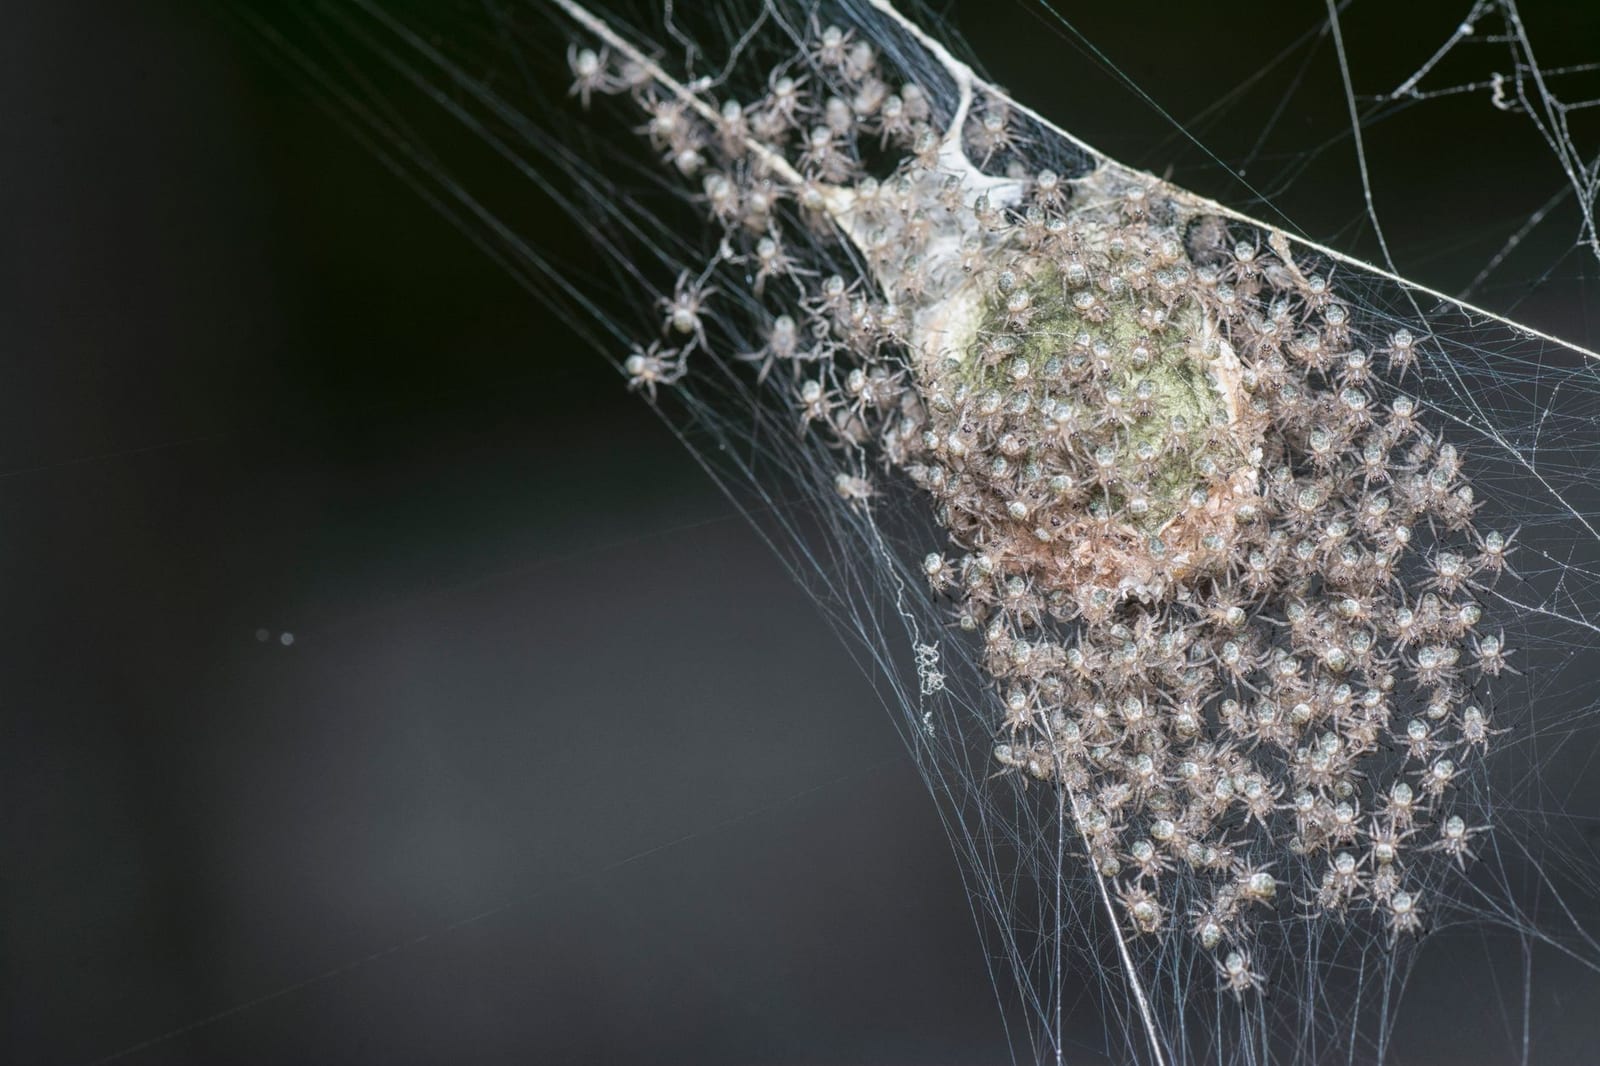
A recent blog post discussed the biological topic of squid egg sacs, while also serving as an open thread for readers to discuss security news not covered elsewhere on the site. The post itself focused on the natural history of squid reproduction, specifically the structures known as egg sacs.

ZeroDay News ·

Source: Schneier on Security

A recent blog post discussed the biological topic of squid egg sacs, while also serving as an open thread for readers to discuss security news not covered elsewhere on the site. The post itself focused on the natural history of squid reproduction, specifically the structures known as egg sacs.

The dual nature of the post—part biological essay, part open forum for cybersecurity discussion—is a common practice on some technical blogs. This approach allows the primary content creator to maintain a regular publishing schedule with diverse topics, while simultaneously fostering community engagement around relevant industry news. Readers are invited to share and discuss security incidents, vulnerabilities, or research that may not have received dedicated coverage.

In the context of cybersecurity, such open threads often become informal aggregators of breaking news or niche findings. Participants might share links to new CVEs, reports of ongoing campaigns, analyses of recent exploits, or discussions about emerging threat actors. This decentralized form of information sharing can be valuable for professionals seeking a broader perspective on the current threat landscape beyond curated headlines.

The moderation policy mentioned in the summary typically outlines the rules of engagement for comments, ensuring discussions remain constructive and relevant. This is crucial in technical communities where detailed and accurate information is paramount, and where misinformation or off-topic discussions can detract from the utility of the forum. Policies often cover acceptable language, relevance to the topic (even if broadly defined as "security news"), and prohibitions against spam or personal attacks.

For security professionals monitoring such discussions, these open threads can offer early warnings about developing threats or provide diverse perspectives on known issues. While not a primary source of validated intelligence, they can act as a pulse check on community concerns and highlight areas of interest that warrant further investigation through official channels and reputable security advisories.

The practice of combining seemingly unrelated topics with an open discussion forum reflects a broader trend in online communities where diverse interests converge. In this instance, a biological subject provides a consistent publishing anchor, while the open thread mechanism ensures the platform remains a dynamic hub for timely cybersecurity discourse, leveraging the collective knowledge of its readership.


ShareXLinkedInWhatsAppFacebook

More News

view all →
security

Canadian cybersecurity executive arrested in federal extortion case

A Canadian cybersecurity executive was arrested in Pennsylvania on Thursday, facing federal charges of conspiracy to commit extortion. Edward Dubrovsky, 54, a co-founder and former Chief Operating Officer of CYPFER, a firm specializing in ransomware negotiation, is charged with conspiring to threaten the confidentiality of information for extortion and conspiring to commit Hobbs Act extortion,…

breach

Criminal IP Introduces AITEM as the Next Evolution of Attack Surface Management

AI SPERA, the company behind the cyber threat intelligence platform Criminal IP, has announced AITEM (AI-Powered Threat Exposure Management), an expansion of its Attack Surface Management (ASM) offerings. AITEM aims to move beyond traditional asset discovery to provide a more comprehensive approach to understanding, prioritizing, and responding to security exposures. The platform is scheduled…

ai

AI Is Getting Really Good at Messing With Cybercriminals

Anti-cybercrime initiatives are increasingly deploying artificial intelligence to disrupt scammers by engaging them with lifelike bots, which the criminals mistake for genuine victims. This strategy aims to waste scammers' time and resources while gathering intelligence on their operations.

ransomware

FBI Arrests Ransomware Negotiation Firm Co-Founder in ShinyHunters Probe

The Federal Bureau of Investigation (FBI) has reportedly arrested Edward Dubrovsky, a co-founder of the ransomware negotiation firm Cypfer and currently associated with CyberSteward. The arrest is said to be part of the ongoing ShinyHunters investigation, specifically in connection with an incident involving FBI job applicant data.

ai

The Third-Party Agent Problem: Why Security Built for AI You Chose Misses the Agents You Didn't

A new report highlights a significant blind spot in enterprise security architectures concerning the proliferation of third-party AI agents. The forthcoming 2026 State of Agent Security Report indicates that current security models, often designed to protect AI systems directly chosen and deployed by an organization, frequently fail to account for AI capabilities embedded within third-party…

security

Insider Cyber Extortion Plot Against Industrial Firm Lands Engineer in Prison

A former core infrastructure engineer has been sentenced to prison for an attempted cyber extortion plot against an industrial firm. The engineer reportedly deleted administrative accounts and reset hundreds of user passwords, subsequently demanding a ransom of 20 Bitcoin to prevent further disruption to the company's servers.



