LIVE · cybersecurity feed
Live wire
AI found more critical bugs in another widely used technology running 225M websitesCVE-2026-129448 · Apache Roller RCE Flaw CVE-2026-129448 Under Active AttackCognizant and Qualys Redefine AI-Era Managed Security ServiceJava4Shell Vulnerability Allows Remote Attacks on Major Java AppsCVE-2026-114938 · Java4Shell (CVE-2026-114938): Frequently asked questions about OpenJDK remote code execution vulnerabilityCVE-2026-114938 · CVE-2026-114938: Critical vulnerability in OpenJDK JAVACritical Java4Shell flaw allows RCE attacks on major Java applicationsCVE-2026-114938 · How to Find, Mitigate, and Patch the Critical Java4Shell Flaw (CVE-2026-114938) NowCVE-2026-28160 · e4jvikwp VikRentCar Vulnerability Listed As Exploited In VulnCheck KEVCVE-2025-5569 · Ideacms Improper Neutralization Flaw Added To VulnCheck KEV After 514 Days
cloud

German parliament passes law giving spy agencies hacking, sabotage powers

The German Bundestag has passed significant legislation that grants the country’s intelligence agencies expanded authority to conduct cyber operations, including hacking and supply chain sabotage. Approved by a vote of 308 to 190, the bill represents the most substantial reform of German intelligence laws in the postwar era. The legislation empowers the Federal Intelligence Service (BND) to…

ZeroDay News ·

Source: The Record

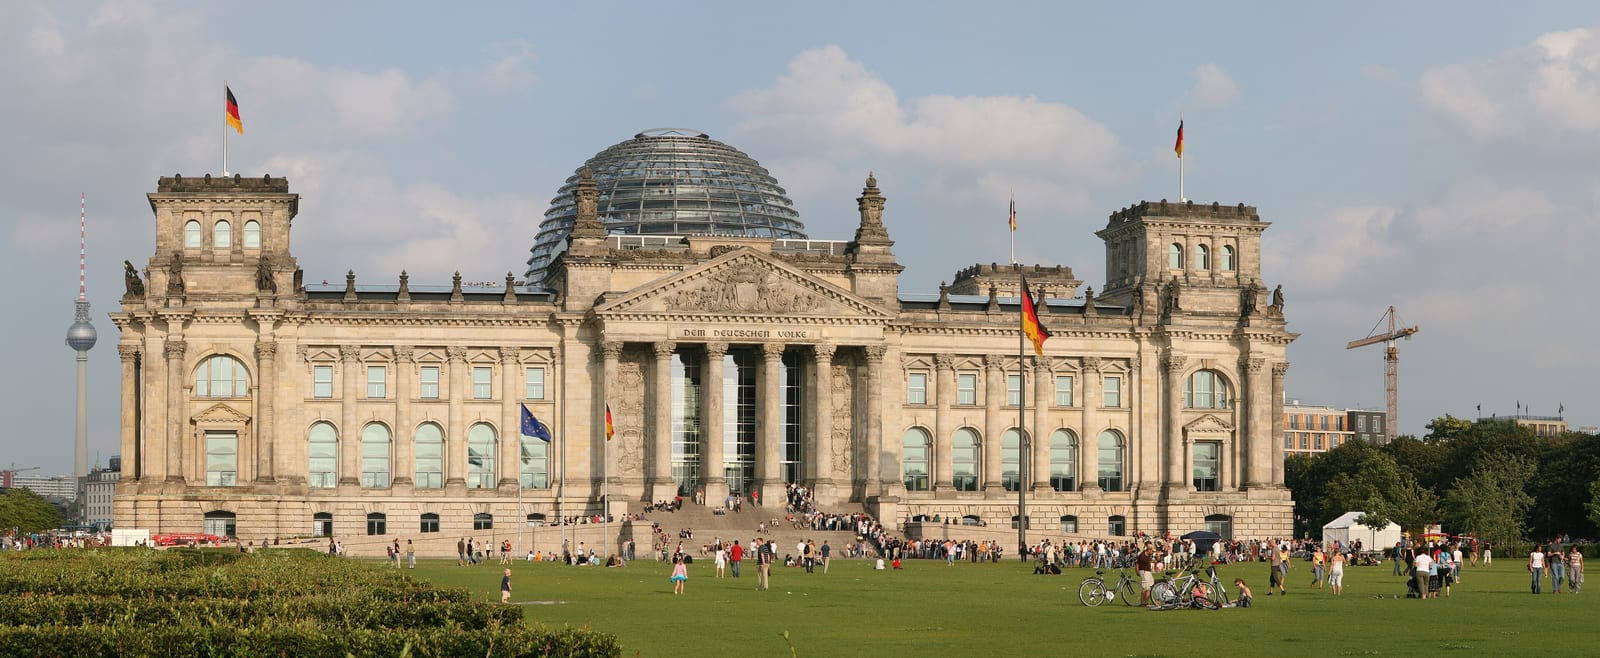
Photo: Daniel Schwen (CC BY-SA 4.0) via Wikimedia Commons

The German Bundestag has passed significant legislation that grants the country’s intelligence agencies expanded authority to conduct cyber operations, including hacking and supply chain sabotage. Approved by a vote of 308 to 190, the bill represents the most substantial reform of German intelligence laws in the postwar era. The legislation empowers the Federal Intelligence Service (BND) to take active measures against foreign threats, such as disabling servers operated by state-sponsored hacking groups or sabotaging infrastructure like drone factories and chemical weapons laboratories.

The reform also affects the Federal Office for the Protection of the Constitution (BfV), Germany’s domestic intelligence agency. While the BfV is granted new covert powers, such as the ability to block or reroute data traffic and investigate organized crime groups linked to extremism, it remains strictly prohibited from using physical force, a responsibility reserved for law enforcement. Both agencies are now authorized to utilize artificial intelligence for large-scale data analysis and to perform biometric image matching against online materials.

Government officials have justified these expanded powers by citing a rapidly evolving threat landscape, including frequent covert operations by foreign powers that disguise espionage as business or sabotage as accidental failure. The legislation is intended to bring Germany’s intelligence capabilities into alignment with those of its European partners. Despite these changes, the government confirmed that the new powers stop short of those held by agencies in countries like France or the United States, as the law explicitly forbids measures intended to endanger human life or physical safety.

Last-minute amendments to the bill introduced specific operational constraints and new requirements. Telecommunications providers can now be ordered to preserve traffic data for future access, a power that remains narrower than similar data retention mandates in the United Kingdom or France. Additionally, the BND’s capacity to retain metadata from bulk surveillance has been extended from 12 to 13 months. Safeguards were also added to protect the privacy of German citizens, specifically shielding personal messages and queries made to search engines or chatbots from BND surveillance.

Oversight mechanisms have been strengthened to account for these new authorities. Any hacking operations or active measures conducted within Germany now require advance approval from the Independent Control Council, which has been expanded from six to twelve members to provide more robust, court-like supervision. Furthermore, the bill includes protections for medical professionals, although some critics have pointed out that similar safeguards for journalists and lawyers remain less comprehensive.

The legislation has faced political friction, particularly regarding a provision that allows the BfV to restrict information-sharing with individual state intelligence offices if federal security interests are deemed at risk. This measure has been labeled by members of the Alternative for Deutschland (AfD) party as a targeted effort to undermine state-level offices. The BfV currently monitors the AfD as a suspected extremist group, though the legal status of that classification is subject to ongoing court challenges.

The push for these reforms follows a period of heightened tension between Berlin and foreign actors. German authorities have previously attributed cyberattacks on national air traffic control systems and disinformation campaigns targeting federal elections to foreign state-backed entities. By authorizing the BND to act when other avenues are exhausted, the government aims to provide a more direct response to the digital threats facing the nation’s critical infrastructure and democratic processes.


cloud
ShareXLinkedInWhatsAppFacebook

More News

view all →
vulnerabilitycritical

AI found more critical bugs in another widely used technology running 225M websites

F5 has issued an emergency security update for the open-source NGINX web server to address 10 newly discovered vulnerabilities. These flaws affect a significant portion of the internet, as NGINX currently powers approximately 225 million websites. The vendor has urged all administrators to upgrade their systems to version 1.31.9 immediately to mitigate the risks.

vulnerability

Consensus mounts that tech outages were fueled by patching of AI-discovered vulnerabilities

A series of significant technical outages affecting aviation, banking, and communications infrastructure over the past week has prompted a federal investigation into the stability of critical systems. While initial concerns focused on the possibility of coordinated cyberattacks, officials from the Trump administration, including Secretary of Homeland Security Markwayne Mullin, Director of…

ai

Coinbase blocks $4.7 million in transfers to Elon Musk deepfake scam

Coinbase successfully intercepted $4.7 million in cryptocurrency transfers associated with a sophisticated deepfake scam targeting users during a high-profile Tesla event. The incident occurred during a demonstration of Tesla's flying car technology, which was broadcast via a fraudulent YouTube livestream. The stream, which drew an audience of over 500,000 viewers, utilized AI-generated video…

ai

Strike Graph Launches Integration AI to Automate Continuous Compliance Evidence Using Any Existing Tool

Strike Graph has announced the launch of a new agentic AI solution designed to automate the collection of compliance evidence across an organization’s existing software stack. By leveraging direct API integrations, the platform aims to streamline the evidence-gathering process, mapping data points to more than 30 different compliance frameworks simultaneously to eliminate redundant manual…

ai

Judge signs off on sale of Spirit Airlines’ data to Google

A federal bankruptcy judge in New York has officially approved the sale of Spirit Airlines’ corporate data to Google, a transaction valued at $10 million. The deal, which follows the airline’s cessation of operations in May, involves the transfer of a massive dataset to the tech giant for the stated purpose of training artificial intelligence models. The repository includes approximately 100…

ransomware

AttackIQ Research Reveals How Iranian Cyber Groups Hand Off Network Access to Enable Destructive Attacks

New research from AttackIQ highlights a sophisticated operational model used by Iranian state-sponsored threat groups, characterized by the strategic hand-off of network access to facilitate destructive cyber operations. The analysis, which examines the activities of 20 distinct groups, suggests that these actors are increasingly blurring the lines between traditional espionage, ransomware…


