
LIVE · cybersecurity feed
Live wire
nation-state

Hacker hijacks Brazil’s national alert system, sending “misanthropy” to millions of phones

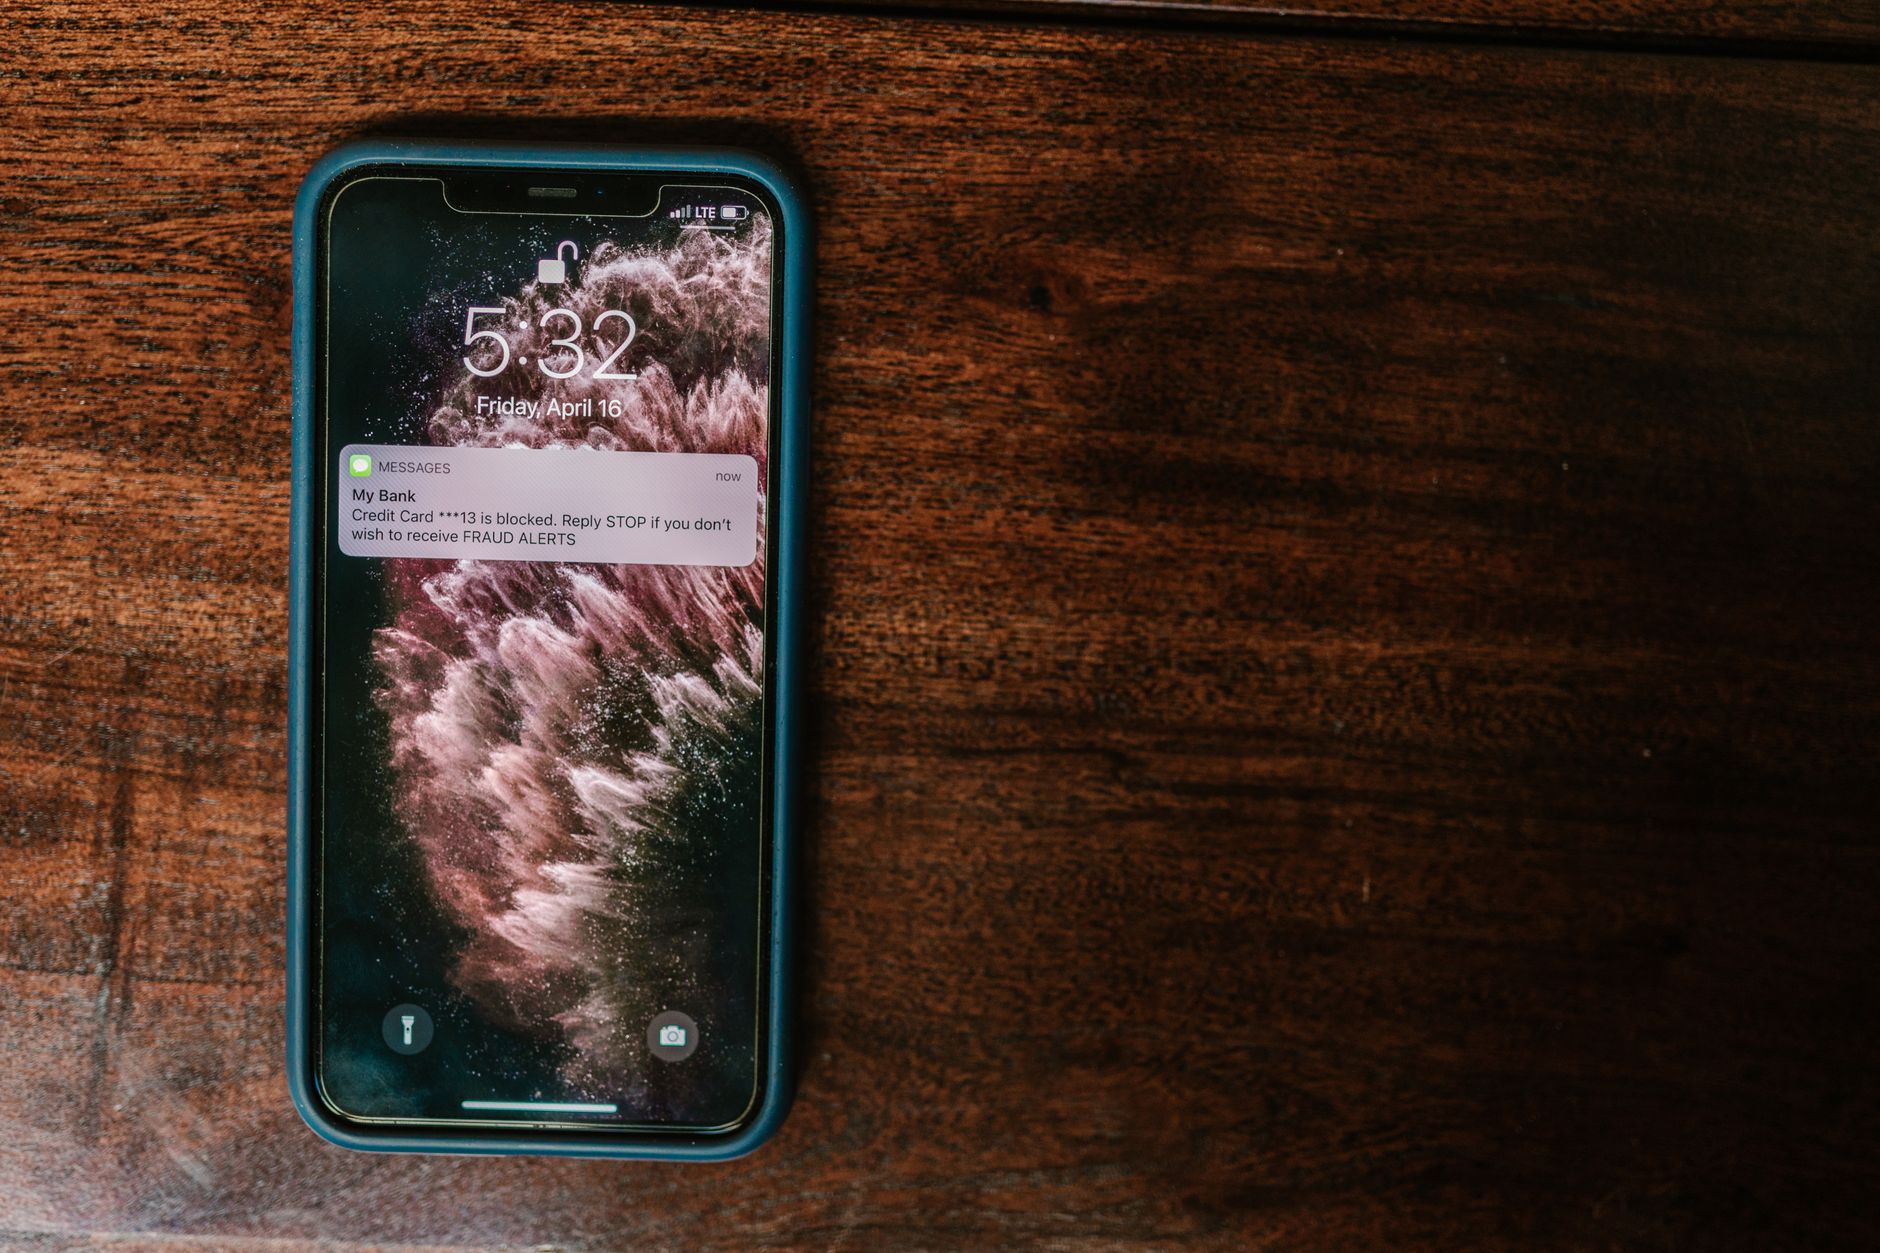
Millions of mobile phone users in Brazil received fake emergency alerts on the night of June 19-20, 2026, after an intruder gained access to the nation's Civil Defence alert system. The unauthorized messages, which bypassed silent mode and displayed prominently on device screens, contained the word "misantropi4" in place of critical information.

ZeroDay News ·

Source: Graham Cluley

Millions of mobile phone users in Brazil received fake emergency alerts on the night of June 19-20, 2026, after an intruder gained access to the nation's Civil Defence alert system. The unauthorized messages, which bypassed silent mode and displayed prominently on device screens, contained the word "misantropi4" in place of critical information.

The incident began around 11:40 pm on June 19 in Paraná state, with a total of ten fake alerts being disseminated over the following couple of hours. Nine of these were sent via the Cell Broadcast system, a technology designed to push alerts to a wide area, and one was sent via traditional SMS. The alerts were categorized as "Extreme Alert," the highest severity level, typically reserved for imminent natural disasters.

States including São Paulo, Rio de Janeiro, and the Federal District were among those affected. Civil defence agencies in each affected state quickly issued statements confirming that they had not issued any such alerts and that no actual emergency conditions warranted them.

Brazil's National Civil Defence confirmed that the alert platform was taken offline at 1:30 am on June 20 following the security breach. Officials stated that while there was no evidence of "structural damage" to the system's infrastructure, they could not determine the exact number of devices that received the false notifications.

According to Wolnei Wolff, National Secretary of Protection and Civil Defence, the attackers managed to re-enter the system even after an initial attempt to block their access. No suspects have been identified in connection with the incident.

Brazil's Cell Broadcast system was implemented in recent years and was expanded nationwide in October 2025. The messages sent by the intruder translated to "misanthropy," meaning hatred or aversion to humanity.

Fortunately, the fake alerts did not include dangerous instructions, such as calls to evacuate or links to malicious websites. However, the incident has raised concerns about the erosion of public trust in emergency alert systems. The effectiveness of such systems relies on public belief in their authenticity, and repeated false alarms, whether accidental or malicious, can lead individuals to disregard genuine warnings.


nation-state
ShareXLinkedInWhatsAppFacebook

More News

view all →
security

Canadian cybersecurity executive arrested in federal extortion case

A Canadian cybersecurity executive was arrested in Pennsylvania on Thursday, facing federal charges of conspiracy to commit extortion. Edward Dubrovsky, 54, a co-founder and former Chief Operating Officer of CYPFER, a firm specializing in ransomware negotiation, is charged with conspiring to threaten the confidentiality of information for extortion and conspiring to commit Hobbs Act extortion,…

breach

Criminal IP Introduces AITEM as the Next Evolution of Attack Surface Management

AI SPERA, the company behind the cyber threat intelligence platform Criminal IP, has announced AITEM (AI-Powered Threat Exposure Management), an expansion of its Attack Surface Management (ASM) offerings. AITEM aims to move beyond traditional asset discovery to provide a more comprehensive approach to understanding, prioritizing, and responding to security exposures. The platform is scheduled…

ai

AI Is Getting Really Good at Messing With Cybercriminals

Anti-cybercrime initiatives are increasingly deploying artificial intelligence to disrupt scammers by engaging them with lifelike bots, which the criminals mistake for genuine victims. This strategy aims to waste scammers' time and resources while gathering intelligence on their operations.

ransomware

FBI Arrests Ransomware Negotiation Firm Co-Founder in ShinyHunters Probe

The Federal Bureau of Investigation (FBI) has reportedly arrested Edward Dubrovsky, a co-founder of the ransomware negotiation firm Cypfer and currently associated with CyberSteward. The arrest is said to be part of the ongoing ShinyHunters investigation, specifically in connection with an incident involving FBI job applicant data.

ai

The Third-Party Agent Problem: Why Security Built for AI You Chose Misses the Agents You Didn't

A new report highlights a significant blind spot in enterprise security architectures concerning the proliferation of third-party AI agents. The forthcoming 2026 State of Agent Security Report indicates that current security models, often designed to protect AI systems directly chosen and deployed by an organization, frequently fail to account for AI capabilities embedded within third-party…

security

Insider Cyber Extortion Plot Against Industrial Firm Lands Engineer in Prison

A former core infrastructure engineer has been sentenced to prison for an attempted cyber extortion plot against an industrial firm. The engineer reportedly deleted administrative accounts and reset hundreds of user passwords, subsequently demanding a ransom of 20 Bitcoin to prevent further disruption to the company's servers.



