
LIVE · cybersecurity feed
Live wire
quantum computinghigh

Hardware Makers Implement Post-Quantum Cryptography as Security Threats Near

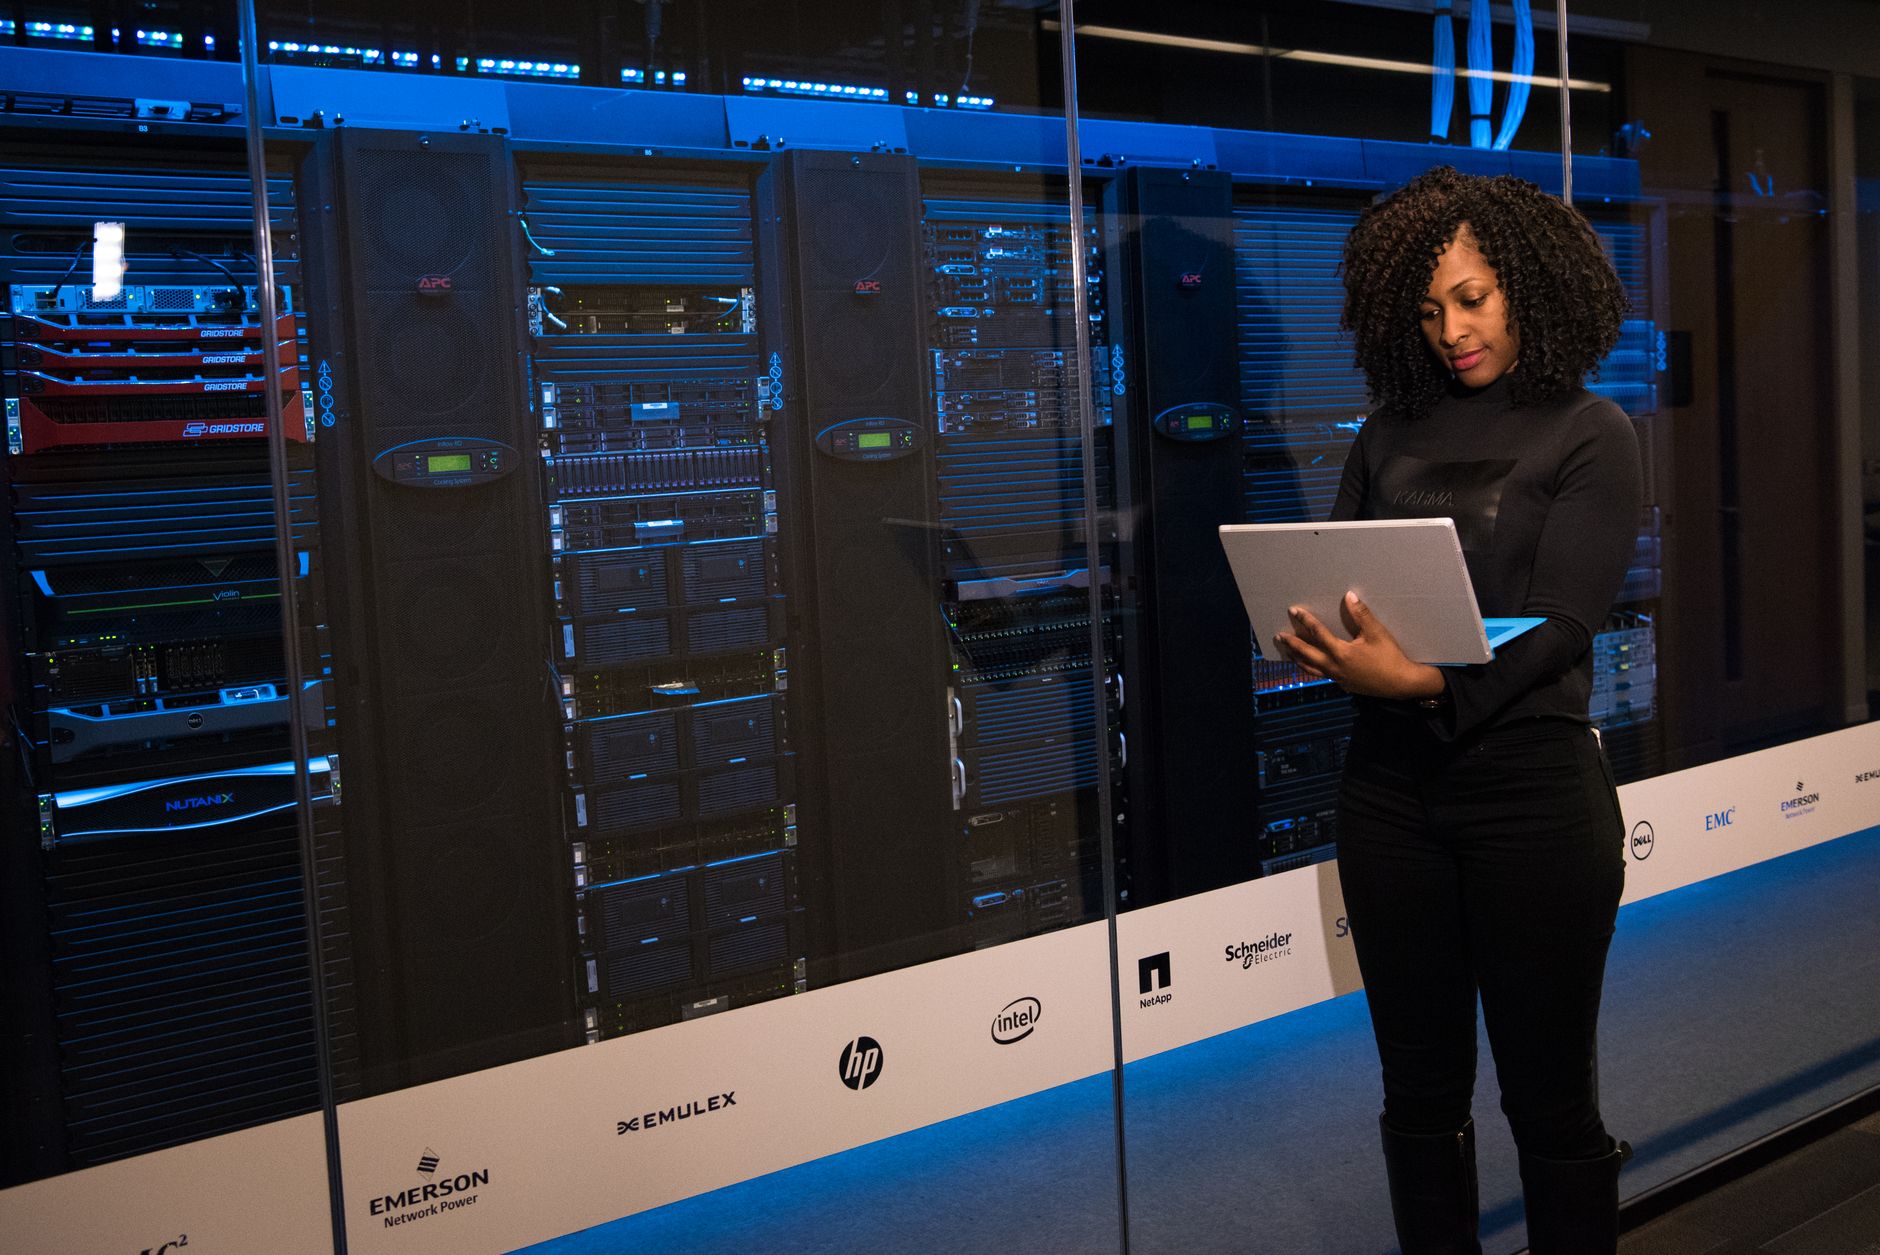
Hardware manufacturers are reportedly beginning to integrate post-quantum cryptography (PQC) into their products, a move driven by the anticipation of future security threats from quantum computers. This proactive shift aims to fortify current encryption methods against the advanced computational power that quantum machines are expected to wield, which could potentially break many of the…

ZeroDay News ·

Source: Dark Reading

Hardware manufacturers are reportedly beginning to integrate post-quantum cryptography (PQC) into their products, a move driven by the anticipation of future security threats from quantum computers. This proactive shift aims to fortify current encryption methods against the advanced computational power that quantum machines are expected to wield, which could potentially break many of the cryptographic algorithms widely used today.

The core concern revolves around the potential for sufficiently powerful quantum computers to efficiently solve mathematical problems that underpin current public-key cryptography, such as RSA and elliptic curve cryptography (ECC). These algorithms rely on the computational difficulty of factoring large numbers or solving discrete logarithms. While classical computers find these problems intractable for large key sizes, quantum algorithms like Shor's algorithm could theoretically solve them in polynomial time, rendering current protections obsolete.

PQC algorithms are designed to be resistant to attacks from both classical and quantum computers. These new cryptographic primitives typically rely on different mathematical problems, often drawn from areas like lattice-based cryptography, code-based cryptography, multivariate polynomial cryptography, and hash-based cryptography. The implementation involves replacing or augmenting existing cryptographic modules within hardware components, such as secure enclaves, trusted platform modules (TPMs), and network interface cards, to ensure that data at rest and in transit remains secure even against quantum adversaries.

The scope of this implementation effort is broad, encompassing a wide range of hardware from consumer devices to enterprise servers and critical infrastructure components. Any system that relies on public-key cryptography for secure communication, digital signatures, or key exchange will eventually need to transition to PQC. This includes secure boot processes, firmware updates, VPN connections, and encrypted storage solutions.

Typical mitigation guidance for this class of issue involves a multi-stage approach. Initially, organizations are advised to conduct cryptographic inventories to identify all instances of vulnerable algorithms. Following this, a "crypto-agility" strategy is recommended, enabling systems to easily update or swap out cryptographic algorithms as new standards emerge or threats evolve. Finally, the actual deployment of PQC involves rigorous testing and validation to ensure interoperability, performance, and security across diverse hardware and software environments.

The push for PQC implementation reflects a broader industry recognition of the long-term security landscape. While fully capable fault-tolerant quantum computers are not yet widely available, the "harvest now, decrypt later" threat model suggests that encrypted data captured today could be stored and decrypted by future quantum machines. This necessitates a forward-looking approach to cryptography, ensuring that the digital infrastructure of tomorrow is resilient against emerging computational paradigms.


quantum computingcryptographycybersecurityencryption
ShareXLinkedInWhatsAppFacebook

More News

view all →
security

Canadian cybersecurity executive arrested in federal extortion case

A Canadian cybersecurity executive was arrested in Pennsylvania on Thursday, facing federal charges of conspiracy to commit extortion. Edward Dubrovsky, 54, a co-founder and former Chief Operating Officer of CYPFER, a firm specializing in ransomware negotiation, is charged with conspiring to threaten the confidentiality of information for extortion and conspiring to commit Hobbs Act extortion,…

breach

Criminal IP Introduces AITEM as the Next Evolution of Attack Surface Management

AI SPERA, the company behind the cyber threat intelligence platform Criminal IP, has announced AITEM (AI-Powered Threat Exposure Management), an expansion of its Attack Surface Management (ASM) offerings. AITEM aims to move beyond traditional asset discovery to provide a more comprehensive approach to understanding, prioritizing, and responding to security exposures. The platform is scheduled…

ai

AI Is Getting Really Good at Messing With Cybercriminals

Anti-cybercrime initiatives are increasingly deploying artificial intelligence to disrupt scammers by engaging them with lifelike bots, which the criminals mistake for genuine victims. This strategy aims to waste scammers' time and resources while gathering intelligence on their operations.

ransomware

FBI Arrests Ransomware Negotiation Firm Co-Founder in ShinyHunters Probe

The Federal Bureau of Investigation (FBI) has reportedly arrested Edward Dubrovsky, a co-founder of the ransomware negotiation firm Cypfer and currently associated with CyberSteward. The arrest is said to be part of the ongoing ShinyHunters investigation, specifically in connection with an incident involving FBI job applicant data.

ai

The Third-Party Agent Problem: Why Security Built for AI You Chose Misses the Agents You Didn't

A new report highlights a significant blind spot in enterprise security architectures concerning the proliferation of third-party AI agents. The forthcoming 2026 State of Agent Security Report indicates that current security models, often designed to protect AI systems directly chosen and deployed by an organization, frequently fail to account for AI capabilities embedded within third-party…

security

Insider Cyber Extortion Plot Against Industrial Firm Lands Engineer in Prison

A former core infrastructure engineer has been sentenced to prison for an attempted cyber extortion plot against an industrial firm. The engineer reportedly deleted administrative accounts and reset hundreds of user passwords, subsequently demanding a ransom of 20 Bitcoin to prevent further disruption to the company's servers.



