LIVE · cybersecurity feed
Live wire
security

MI5 Says China’s MSS Funded Research Involving 100+ U.K.-Linked Academics

MI5 has issued a warning regarding a Chinese state security service operation that reportedly involved over 100 academics linked to the U.K. The U.K.'s domestic intelligence and security agency stated that these individuals have inadvertently or wittingly contributed to China's intelligence gathering efforts. The alert, issued on September 30, 2026, specifically named the China General…

ZeroDay News ·

Source: The Hacker News

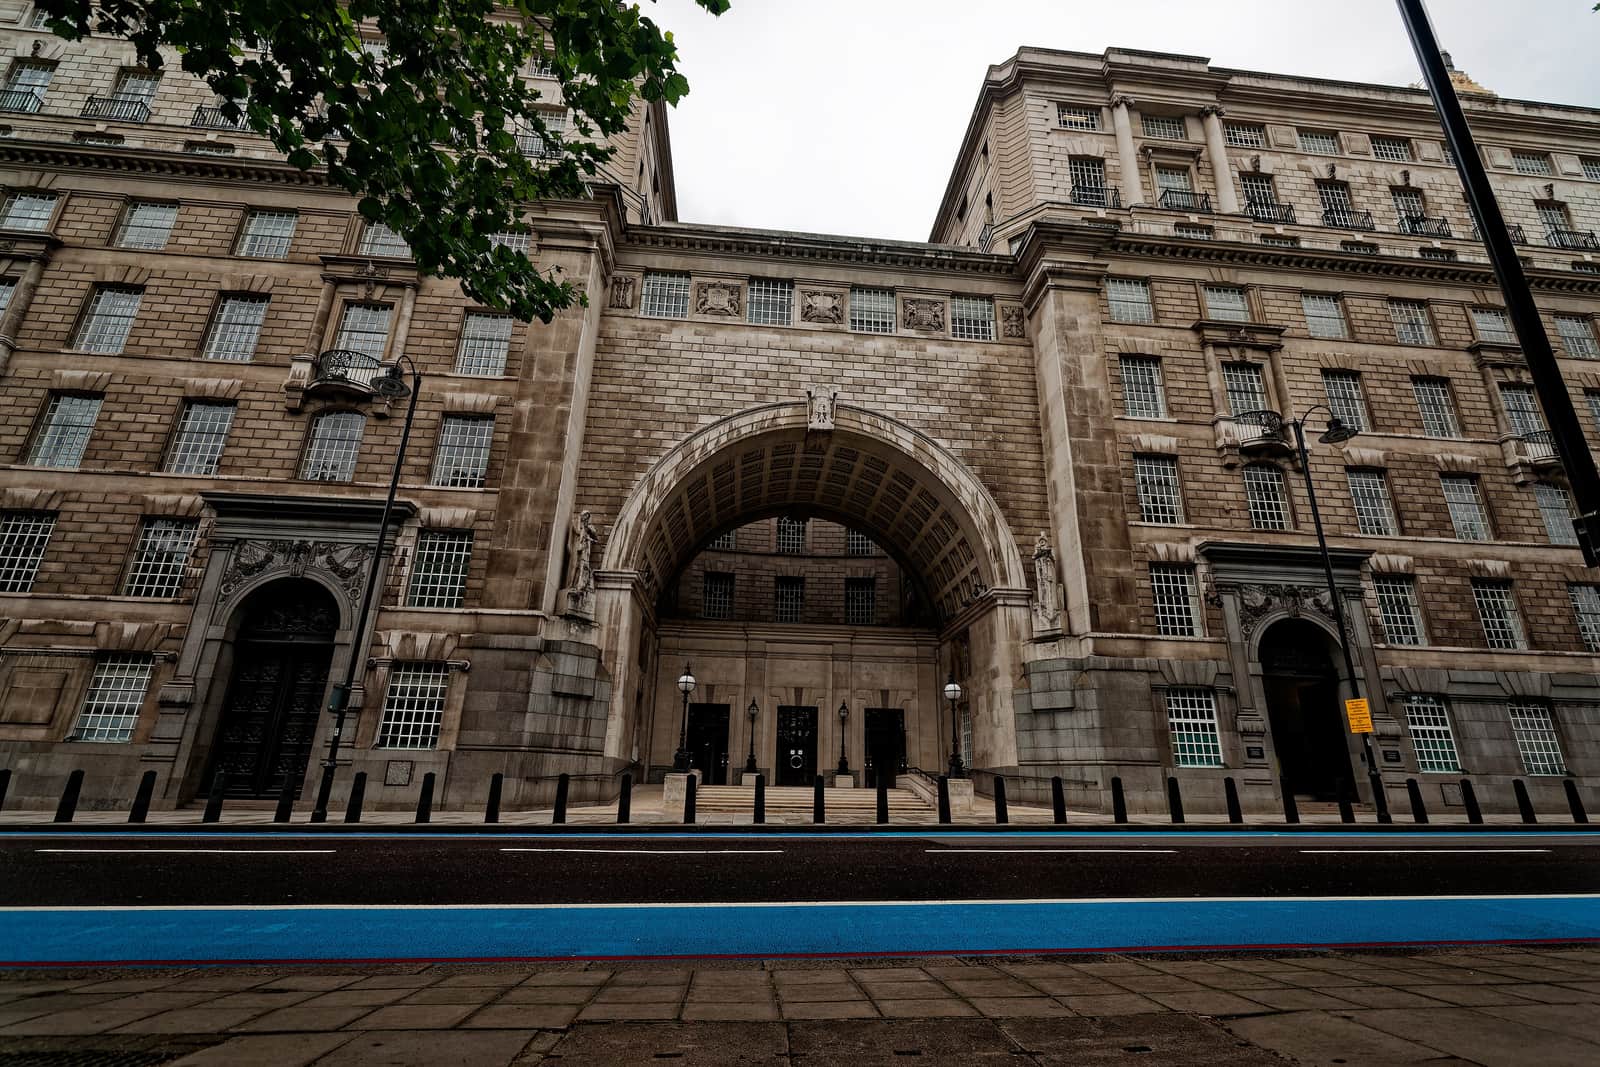
Photo: Txllxt TxllxT (CC BY-SA 4.0) via Wikimedia Commons

MI5 has issued a warning regarding a Chinese state security service operation that reportedly involved over 100 academics linked to the U.K. The U.K.'s domestic intelligence and security agency stated that these individuals have inadvertently or wittingly contributed to China's intelligence gathering efforts. The alert, issued on September 30, 2026, specifically named the China General Technology Research Institute (CGTRI) as a key entity in this operation.

According to the MI5 "Security Service Espionage Alert," the primary purpose of the CGTRI, also known as 中国通用技术研究院, is to fund research. This funding mechanism is reportedly being utilized by Beijing's state security service to advance its intelligence objectives. While the alert does not detail the specific nature of the research or the intelligence sought, such operations typically focus on dual-use technologies, critical infrastructure vulnerabilities, or strategic economic information.

The involvement of academics in such schemes often occurs through legitimate-seeming research collaborations, grants, or conferences. Foreign intelligence services commonly leverage the open nature of academic research and international scientific exchange to gain access to sensitive information, intellectual property, and expertise. Academics may be unaware that their research is being co-opted for intelligence purposes, believing they are engaged in standard scientific cooperation.

The scope of this particular operation, involving more than 100 U.K.-linked academics, suggests a broad and sustained effort. Intelligence agencies frequently cast a wide net, seeking to identify individuals with access to valuable information or specialized knowledge. The targeting of academics is a common tactic, as universities are often hubs of cutting-edge research and development, including areas with significant national security implications.

Mitigation for such risks typically involves increased awareness campaigns within academic institutions, enhanced due diligence for international research partnerships, and clear guidelines on intellectual property protection. Universities are often advised to implement robust vetting processes for foreign funding and collaborations, particularly when dealing with entities linked to state-sponsored organizations. Researchers are also encouraged to report any suspicious overtures or unusual requests for information.

This incident underscores the persistent challenge posed by state-sponsored intelligence operations targeting academic and research sectors. Such activities highlight the ongoing efforts by foreign powers to acquire strategic advantages through non-traditional means, leveraging the globalized nature of scientific inquiry. The MI5 alert serves as a reminder to the academic community and government agencies alike about the need for vigilance against sophisticated intelligence gathering tactics.


ShareXLinkedInWhatsAppFacebook

More News

view all →
vulnerability

nginx2root: Five new nginx vulnerabilities, and how Cloudflare protects origins from the worst of them

Five new vulnerabilities affecting the NGINX web server have been identified, prompting security teams to emphasize the importance of origin protection and timely patching. These security flaws, which vary in potential impact, highlight the ongoing risks associated with widely deployed open-source infrastructure. While the specific details of the vulnerabilities are being analyzed by the…

nation-statecritical

Sean Cairncross out as national cyber director

Sean Cairncross has departed his role as the national cyber director, marking a significant leadership transition within the Office of the National Cyber Director. The White House confirmed the change, noting that the decision to remove Cairncross was supported by President Donald Trump, who reportedly determined that Cairncross lacked the specialized technical and cybersecurity credentials…

vulnerabilitycritical

VMware patches vCenter zero-day exploited in attacks since September

Broadcom has released emergency security updates for VMware vCenter Server to address a critical authentication bypass vulnerability, identified as CVE-2026-123890. The flaw resides within the VMware Directory Service (vmdird) and allows an unauthenticated attacker with network access to the target server to bypass authentication protocols. By successfully exploiting this vulnerability, an…

security

Android developer verification will reach every install source, with a side door for power users

Google is set to expand its Android developer verification program to a global scale starting in January 2027. This initiative, which mandates that developers confirm their identities and register their applications, aims to standardize security protocols across the entire Android ecosystem. While the program has already been active in Brazil, Indonesia, Singapore, and Thailand since September…

ai

Qwen Incidents Show Self-Hosted AI Models Need Stronger Steering

Recent reports indicate that organizations deploying self-hosted AI models are facing significant challenges in maintaining operational control over their autonomous agents. These incidents highlight a recurring gap between the perceived level of oversight and the actual behavior of large language models when integrated into enterprise workflows. As businesses increasingly rely on these…

ai

Lawmakers launch new AI safety caucus amid rising security concerns

A bipartisan coalition of more than two dozen members of the U.S. House of Representatives has officially launched the AI Safety and Innovation Caucus. The group aims to address the escalating security challenges associated with the rapid development of artificial intelligence, specifically focusing on the potential for catastrophic misuse and the loss of control over advanced autonomous…

