LIVE · cybersecurity feed
Live wire
Acronis warns of actively exploited flaw in its cPanel backup pluginOracle September 2026 Critical Security Patch Update addresses 672 CVEsCVE-2026-76461 · U.S. CISA adds Cisco Secure Email Gateway flaw to its Known Exploited Vulnerabilities catalogHackers target WordPress sites via third-party WooCommerce pluginCVE-2026-51990 · Hackers exploit Tencent app flaw to deploy GrayRabbit malwareCVE-2026-42016 · CISA Adds 5 Exploited Flaws in Artifactory, ScreenConnect, RouterOS to KEVCVE-2026-85102 · Dutch NCSC: Critical Check Point VPN flaws exploitation is imminentAI Enables Mass Generation of Personalized Fraud EmailsCVE-2026-85706 · Critical GitLab Vulnerability Exploited in Internet-Wide ProbesCVE-2025-66516 · Metasploit Wrap Up: This One Goes to Sixteen!
ai

Microsoft’s Project Zenith puts large AI models directly on developer PCs

Microsoft’s Project Zenith is a ready-to-code Windows 11 experience for developer-class PCs capable of running AI models with more than 30 billion parameters locally without relying on metered cloud tokens. Designed for systems with at least 64 GB of unified memory and 250 GB/s or more of memory bandwidth, it pairs powerful hardware with a preconfigured software environment for coding, testing, an

zeroday.news ·

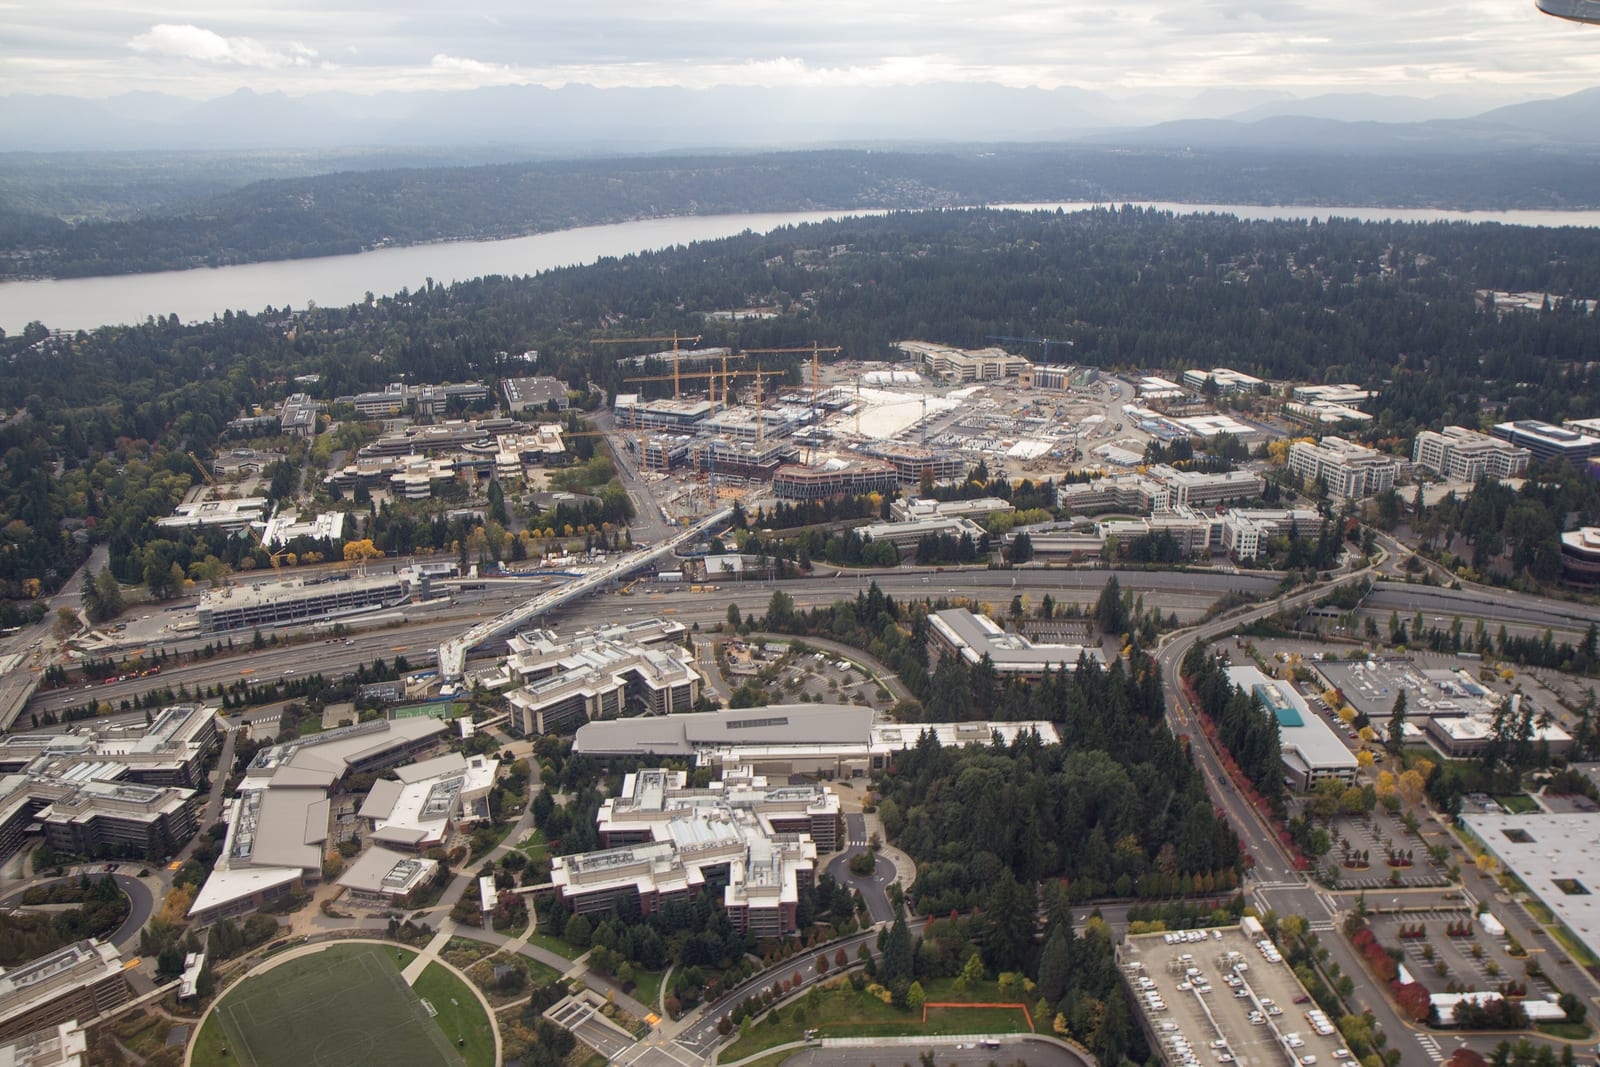
Photo: Atomic Taco (CC BY-SA 2.0) via Wikimedia Commons

Microsoft has unveiled Project Zenith, a specialized Windows 11 experience designed to enable developers to run large AI models locally on their personal computers. This initiative aims to provide a ready-to-code environment capable of handling AI models with over 30 billion parameters without relying on cloud-based services or metered tokens.

Project Zenith systems are engineered for high performance, requiring at least 64 GB of unified memory and memory bandwidth of 250 GB/s or more. The initial devices supporting Project Zenith will be powered by AMD Ryzen AI Halo processors, with additional hardware partners and OEMs expected to introduce compatible systems in the near future. These devices will also benefit from ongoing performance, reliability, and usability enhancements within Windows 11, including improvements to Search, File Explorer, and memory management.

The development environment comes preconfigured with essential tools and settings. Programming languages, runtimes, source control, and productivity applications are preinstalled. Windows Terminal and Visual Studio Code are conveniently pinned to the Taskbar for immediate access. Windows itself is optimized for development, with File Explorer displaying file extensions, hidden files, and full paths, and support for long paths enabled. To minimize distractions, recently used files and folders, sync provider tips, Start menu tips, and account notifications are disabled, while Command Palette is enabled in Search and Start.

A key component of Project Zenith is the integration of Windows Subsystem for Linux (WSL), which provides a foundation for running Linux workloads directly on Windows. WSL containers are also built-in, allowing developers to create, run, and interact with Linux containers natively. While providing a development-focused baseline, the environment remains customizable, allowing developers to add their preferred tools, languages, and frameworks.

Security for AI agents is a core consideration for Project Zenith. The platform incorporates OS-enforced identity, containment through Microsoft Execution Containers (MXC), and enterprise-grade manageability for AI agents, all available from the outset. This local processing capability allows developers to utilize local models for routine tasks, reserving cloud models for more demanding workloads, which can help reduce cloud usage and associated token costs.

Microsoft emphasizes that Project Zenith reflects its collaborative approach with the ecosystem. By partnering with OEM and silicon providers, Microsoft aims to offer developers a range of device choices and performance tiers while maintaining a consistent, ready-to-code experience. The goal is to ensure that regardless of the specific hardware, the developer promise of a powerful, thoughtfully configured, and immediately usable environment remains constant.


aicloud
ShareXLinkedInWhatsAppFacebook

More News

view all →
ai

Microsoft Commits to Sweeping AI Privacy Rules for Students. Will Other Tech Giants Follow?

Microsoft agreed to adopt guardrails and privacy standards for its AI in schools, as negotiated with the American Federation of Teachers. The post Microsoft Commits to Sweeping AI Privacy Rules for Students. Will Other Tech Giants Follow? appeared first on SecurityWeek.

vulnerability

The vulnpocalypse rains iBugs down on Apple with record-setting number of patches

September Patch Tuesday part 2?

vulnerabilityhigh

Acronis warns of actively exploited flaw in its cPanel backup plugin

Acronis disclosed a high-severity Linux local privilege escalation vulnerability in its backup plugin for cPanel, WebHost Manager (WHM), and Plesk that may be exploited in the wild. [...]

vulnerabilitycritical

Oracle September 2026 Critical Security Patch Update addresses 672 CVEs

Oracle addresses 672 CVEs in its September 2026 Critical Security Patch Update with 673 patches, including 104 critical updates. Key Takeaways The September 2026 Critical Security Patch Update (CSPU) contains fixes for 672 unique CVEs in 673 security updates 104 issues (15.5% of all patches) were assigned a critical severity rating Oracle E-Business Suite received the highest number of patches at

CVE-2026-76461critical

U.S. CISA adds Cisco Secure Email Gateway flaw to its Known Exploited Vulnerabilities catalog

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Cisco Secure Email Gateway flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Cisco Secure Email Gateway flaw, tracked as CVE-2026-76461 (CVSS score of 9,8), to its Known Exploited Vulnerabilities (KEV) catalog. Cisco disclosed a critical zero-day CVE-2026-76

patch

Malcious Admin Menu Editor Pro plugin backdoors 1,500 WordPress sites

Malicious versions of the Admin Menu Editor Pro plugin for WordPress have been distributed to more than 200 customers after a threat actor compromised the maintainer's website and pushed updates that created a hidden user account. [...]



