LIVE · cybersecurity feed
Live wire
AI found more critical bugs in another widely used technology running 225M websitesCVE-2026-129448 · Apache Roller RCE Flaw CVE-2026-129448 Under Active AttackCognizant and Qualys Redefine AI-Era Managed Security ServiceJava4Shell Vulnerability Allows Remote Attacks on Major Java AppsCVE-2026-114938 · Java4Shell (CVE-2026-114938): Frequently asked questions about OpenJDK remote code execution vulnerabilityCVE-2026-114938 · CVE-2026-114938: Critical vulnerability in OpenJDK JAVACritical Java4Shell flaw allows RCE attacks on major Java applicationsCVE-2026-114938 · How to Find, Mitigate, and Patch the Critical Java4Shell Flaw (CVE-2026-114938) NowCVE-2026-28160 · e4jvikwp VikRentCar Vulnerability Listed As Exploited In VulnCheck KEVCVE-2025-5569 · Ideacms Improper Neutralization Flaw Added To VulnCheck KEV After 514 Days
ransomware

Shipping giant Maersk says recent cyber incident affected legacy system

Shipping giant Maersk has confirmed that it recently identified a cyber incident involving a legacy system inherited from a previous corporate acquisition. The company stated that the breach is contained to a specific local environment and maintains that there is no evidence of unauthorized access spreading to the broader Maersk infrastructure. According to the firm, systems utilized by…

ZeroDay News ·

Source: The Record

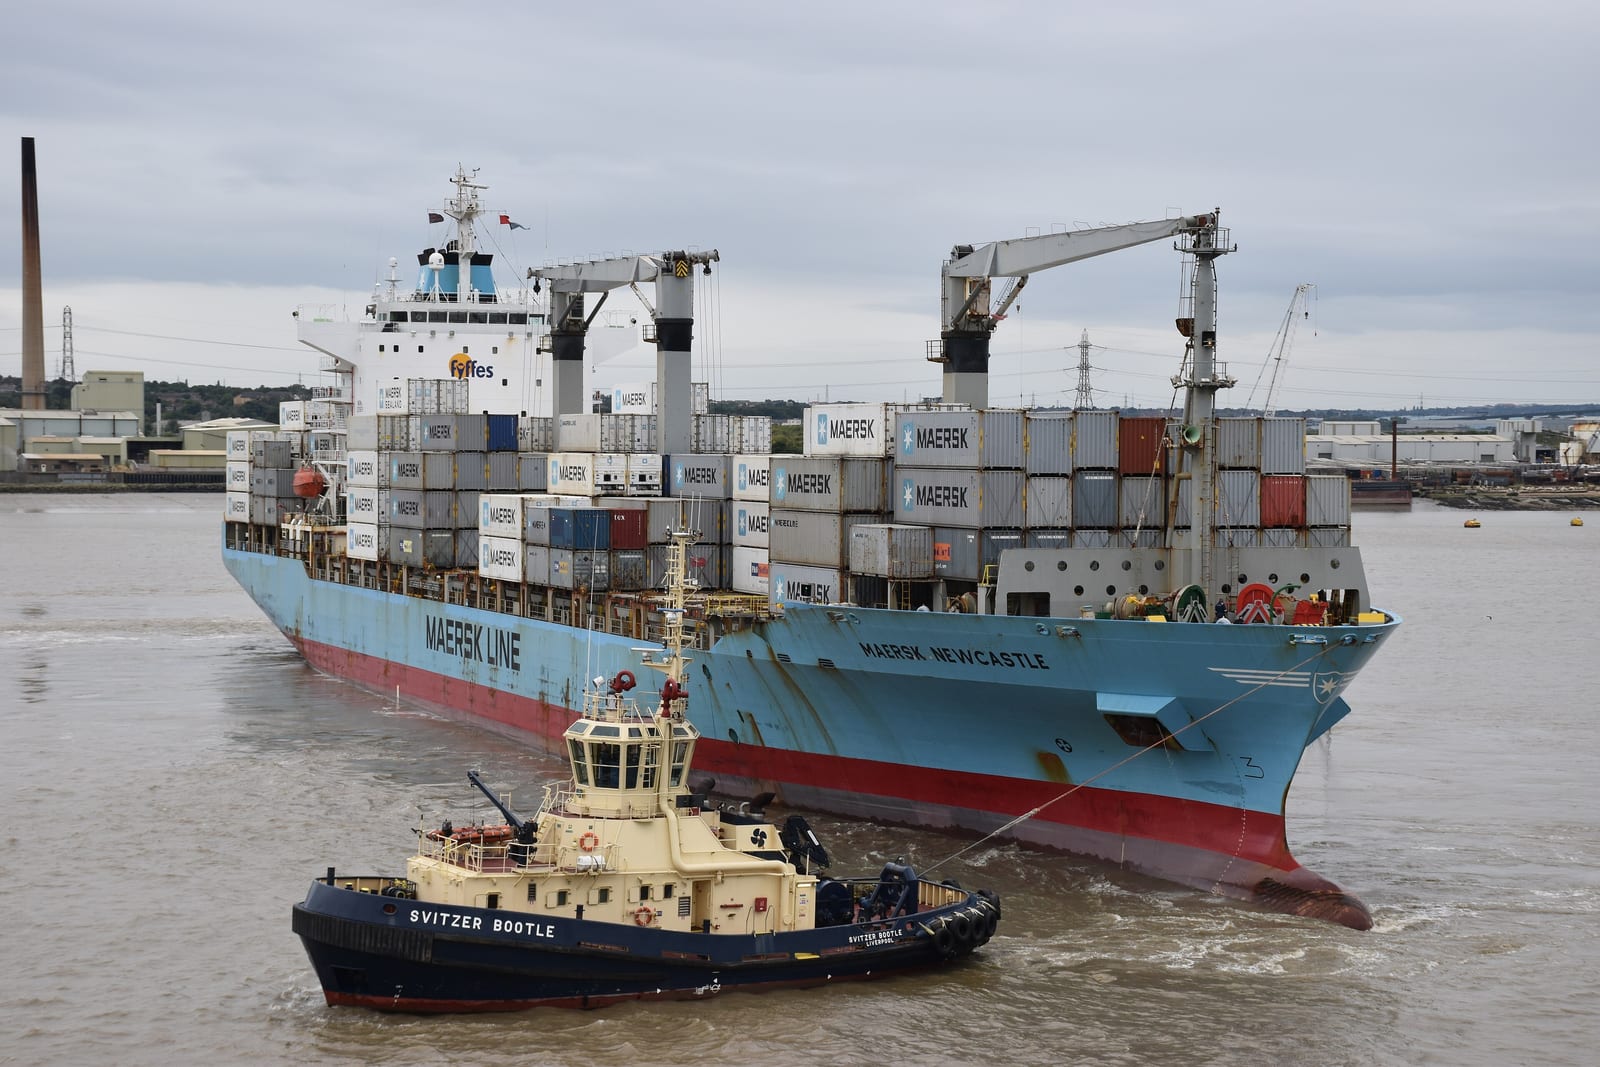
Photo: Niels Johannes (CC BY-SA 4.0) via Wikimedia Commons

Shipping giant Maersk has confirmed that it recently identified a cyber incident involving a legacy system inherited from a previous corporate acquisition. The company stated that the breach is contained to a specific local environment and maintains that there is no evidence of unauthorized access spreading to the broader Maersk infrastructure. According to the firm, systems utilized by customers and partners, including those connected via APIs or Electronic Data Interchange, remain unaffected by the event.

The incident comes shortly after a threat actor group known as WhiteArmor publicly asserted that it had successfully compromised LF Logistics. Maersk completed its acquisition of the Hong Kong-based logistics firm in 2022. While Maersk has acknowledged the security event involving its legacy infrastructure, it has not explicitly confirmed that the WhiteArmor claim and the internal incident are the same event.

The WhiteArmor group has alleged that it exfiltrated approximately 100 gigabytes of data from LF Logistics. The attackers are reportedly demanding a ransom payment of $5 million, setting a 30-day deadline for the firm to comply. The group claims the stolen cache contains sensitive information regarding warehouse operations, customer records, and driver details. As of now, Maersk has not verified these claims, stating instead that its internal investigation has yielded no indications that sensitive data was disclosed or compromised.

Maersk has emphasized that it does not expect the incident to result in any operational disruptions for its global client base. The company’s current assessment suggests the impact is strictly isolated, and it has reported no signs of lateral movement within its network. This incident marks another challenge for the shipping industry, which has seen an uptick in digital targeting as organizations increasingly rely on complex, interconnected logistics software.

The broader maritime and logistics sector has faced a series of high-profile cyberattacks in recent weeks. Most notably, the Santos Port Authority in Brazil has been grappling with the aftermath of a ransomware attack that began on the second Friday of November. That incident resulted in a power outage and forced port officials to transition to manual processes for billing, cargo loading, and route scheduling.

Recovery efforts at the Santos Port Authority are ongoing, with officials reporting that approximately 70% of their systems have been restored using backups as of Thursday. Brazilian federal authorities have launched an investigation into the attack, which caused significant delays at one of South America’s busiest shipping hubs. The situation in Brazil highlights the ongoing vulnerability of critical port infrastructure as these facilities modernize their digital operations.

The logistics industry has become a frequent target for ransomware syndicates over the past five years, with major hubs in the United States, Europe, and Asia experiencing similar disruptions. In 2024, the Port of Seattle faced a significant cyber incident that impacted both its seaport and airport operations during the Labor Day holiday period. In that instance, the port authority opted not to meet the ransom demands of the attackers.

Maersk, which has previously navigated its own ransomware-related challenges, remains one of the largest shipping entities in the world, reporting $54 billion in revenue for 2025. The company continues to monitor its legacy systems following the discovery of the breach. While the firm maintains that the incident is isolated, the intersection of its statement with the claims made by WhiteArmor regarding LF Logistics remains a focal point for security analysts monitoring the situation.


ransomware
ShareXLinkedInWhatsAppFacebook

More News

view all →
ransomware

AttackIQ Research Reveals How Iranian Cyber Groups Hand Off Network Access to Enable Destructive Attacks

New research from AttackIQ highlights a sophisticated operational model used by Iranian state-sponsored threat groups, characterized by the strategic hand-off of network access to facilitate destructive cyber operations. The analysis, which examines the activities of 20 distinct groups, suggests that these actors are increasingly blurring the lines between traditional espionage, ransomware…

vulnerabilitycritical

AI found more critical bugs in another widely used technology running 225M websites

F5 has issued an emergency security update for the open-source NGINX web server to address 10 newly discovered vulnerabilities. These flaws affect a significant portion of the internet, as NGINX currently powers approximately 225 million websites. The vendor has urged all administrators to upgrade their systems to version 1.31.9 immediately to mitigate the risks.

vulnerability

Consensus mounts that tech outages were fueled by patching of AI-discovered vulnerabilities

A series of significant technical outages affecting aviation, banking, and communications infrastructure over the past week has prompted a federal investigation into the stability of critical systems. While initial concerns focused on the possibility of coordinated cyberattacks, officials from the Trump administration, including Secretary of Homeland Security Markwayne Mullin, Director of…

ai

Coinbase blocks $4.7 million in transfers to Elon Musk deepfake scam

Coinbase successfully intercepted $4.7 million in cryptocurrency transfers associated with a sophisticated deepfake scam targeting users during a high-profile Tesla event. The incident occurred during a demonstration of Tesla's flying car technology, which was broadcast via a fraudulent YouTube livestream. The stream, which drew an audience of over 500,000 viewers, utilized AI-generated video…

ai

Strike Graph Launches Integration AI to Automate Continuous Compliance Evidence Using Any Existing Tool

Strike Graph has announced the launch of a new agentic AI solution designed to automate the collection of compliance evidence across an organization’s existing software stack. By leveraging direct API integrations, the platform aims to streamline the evidence-gathering process, mapping data points to more than 30 different compliance frameworks simultaneously to eliminate redundant manual…

ai

Judge signs off on sale of Spirit Airlines’ data to Google

A federal bankruptcy judge in New York has officially approved the sale of Spirit Airlines’ corporate data to Google, a transaction valued at $10 million. The deal, which follows the airline’s cessation of operations in May, involves the transfer of a massive dataset to the tech giant for the stated purpose of training artificial intelligence models. The repository includes approximately 100…


