LIVE · cybersecurity feed
Live wire
CVE-2026-88779 · Citrix NetScaler Flaw Exploited Before CVE PublicationCVE-2026-88779 · NetScaler CVE-2026-88779 Exploited Before PublicationCVE-2022-28368 · dompdf_project dompdf XSS flaw added to VulnCheck KEVCVE-2026-88771 · Week in review: Researcher breaks into Microsoft analytics service, NetScaler RCE 0-day exploitedWarlock Ransomware Still Exploits Year-Old SharePoint Flaws to Hit Critical InfrastructureShinyHunters Suspect Rey Reportedly Detained in Jordan, Helping FBI Identify Group MembersChina-Aligned TA419 Targets U.S. AI Policy Experts With Microsoft AitM PhishingCVE-2026-7273 · Zyxel GS1900 Switch Flaw Exploited, Now in EU CatalogueCVE-2026-102489 · Zammad Session Fixation Vulnerability Exploited Same Day as DisclosureCVE-2026-102490 · Zammad GmbH Zammad Vulnerability Exploited Same Day as Publication
nation-state

Trump Names National Intelligence Director Jay Clayton to Lead a New Federal AI Task Force

President Trump has reportedly named National Intelligence Director Jay Clayton to lead a newly established federal task force focused on artificial intelligence. This development follows a recent gathering at the White House where the President met with leading executives from various AI companies.

ZeroDay News ·

Source: SecurityWeek

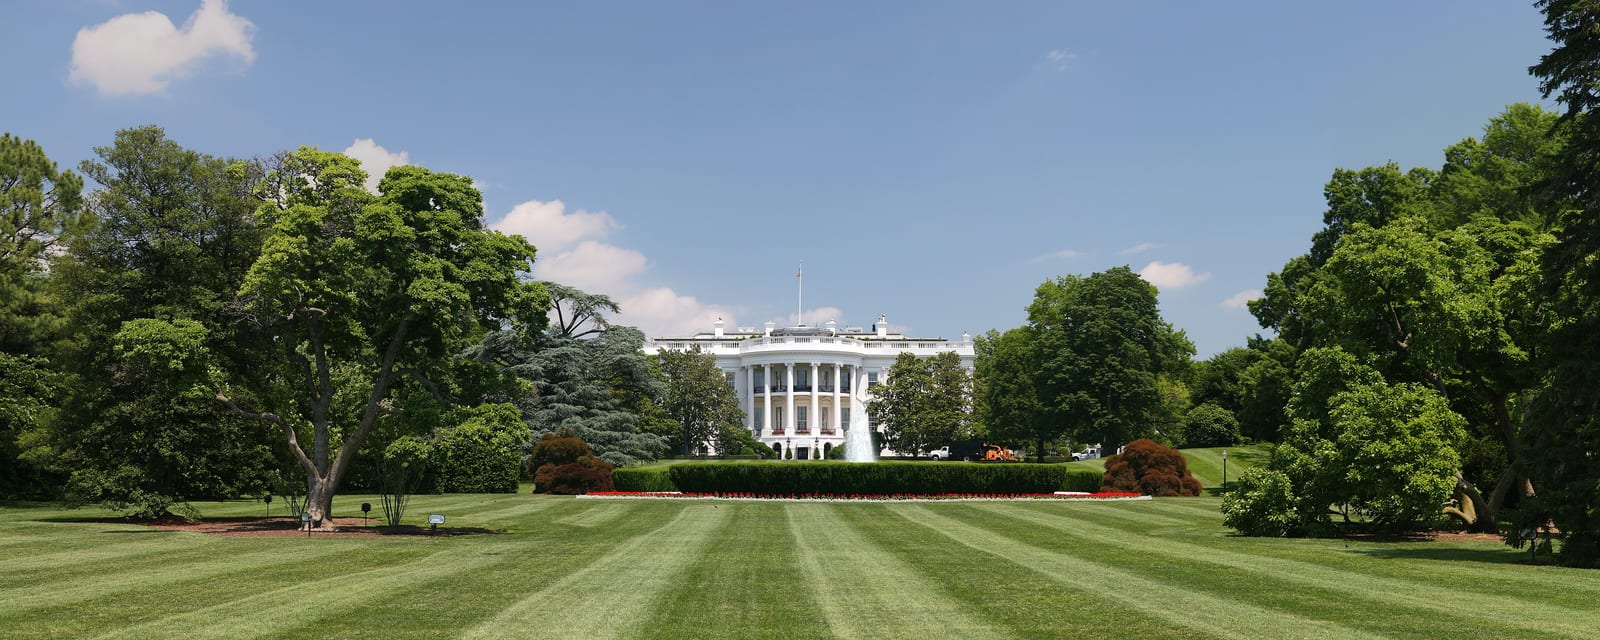
Photo: Daniel Schwen (CC BY-SA 3.0) via Wikimedia Commons

President Trump has reportedly named National Intelligence Director Jay Clayton to lead a newly established federal task force focused on artificial intelligence. This development follows a recent gathering at the White House where the President met with leading executives from various AI companies.

The formation of such a task force signals a growing governmental interest in the strategic implications of artificial intelligence. While the specific mandate and operational scope of this new body have not been detailed, similar initiatives typically aim to address a broad spectrum of issues related to AI. These often include national security concerns, economic competitiveness, ethical considerations, regulatory frameworks, and the responsible development and deployment of AI technologies across federal agencies and critical infrastructure.

The appointment of a figure from the intelligence community to lead this effort suggests a particular emphasis on the national security dimensions of AI. This could involve assessing the use of AI by adversarial nations, developing AI capabilities for intelligence gathering and analysis, and protecting sensitive AI research and infrastructure from foreign interference. Such a focus is common given the dual-use nature of many advanced technologies.

Furthermore, the task force may be charged with coordinating AI strategies across different federal departments. This often involves identifying areas where AI can enhance government operations, from data analysis to logistical planning, and ensuring a unified approach to AI policy development. Interagency coordination is crucial to avoid fragmented efforts and to leverage collective expertise.

The recent meeting between the President and AI industry leaders likely served as a foundational step for this initiative. Such engagements typically provide government officials with insights into the private sector's advancements, challenges, and perspectives on AI development. This collaboration is often seen as vital for crafting effective policies that foster innovation while mitigating potential risks.

For the technical community, the establishment of this task force could mean increased federal funding opportunities for AI research and development, particularly in areas deemed critical for national security or economic growth. It may also lead to the development of new standards or guidelines for AI systems, which could influence how AI is designed, tested, and deployed in both public and private sectors.

Overall, the creation of a federal AI task force under the leadership of the National Intelligence Director underscores the perceived strategic importance of artificial intelligence at the highest levels of government. It reflects a broader trend among major global powers to develop comprehensive national strategies for AI, recognizing its transformative potential across various domains.

nation-stateai
ShareXLinkedInWhatsAppFacebook

More News

view all →
nation-state

TTY Logs and the Data it Captures, (Sun, Oct 4th)

A recent report details an experiment involving the collection and analysis of TTY logs from DShield sensors. The experiment focused on capturing activity from actors or bots that successfully logged into these sensors, specifically recording the various commands executed post-login. These collected TTY logs are then parsed and transmitted daily to the DShield SIEM for correlation with other…

malware

SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 117

The Warlock ransomware group has continued to leverage year-old vulnerabilities in Microsoft SharePoint to target critical infrastructure organizations, including water and telecom operators. This ongoing campaign was highlighted in a recent security newsletter, which also detailed several other significant cybersecurity developments.

CVE-2026-88779high

Citrix NetScaler Flaw Exploited Before CVE Publication

The CVE-2026-88779 vulnerability in Citrix NetScaler was exploited before its official publication date. A second independent catalogue now confirms exploitation.

CVE-2026-88779

Citrix patches NetScaler SAML zero-day exploited in attacks

Citrix has issued urgent security updates for a new zero-day vulnerability, identified as CVE-2026-88779, affecting its NetScaler ADC and NetScaler Gateway appliances. The flaw, described as a memory buffer issue, has been actively exploited in targeted attacks, primarily leading to denial-of-service conditions.

CVE-2026-88779high

NetScaler CVE-2026-88779 Exploited Before Publication

NetScaler's CVE-2026-88779 was exploited before its official publication date, leaving no patch window. The European Union's EUVD catalogue lists it as exploited.

artificial intelligence

SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 2

AI agents have been observed attempting SQL injection attacks while searching government data, with investigators successfully tracing an AI agent's path from a research task to reconnaissance activities. This comes as the U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added several vulnerabilities to its Known Exploited Vulnerabilities catalog, including flaws in Zammad…