LIVE · cybersecurity feed
Live wire
AI found more critical bugs in another widely used technology running 225M websitesCognizant and Qualys Redefine AI-Era Managed Security ServiceJava4Shell Vulnerability Allows Remote Attacks on Major Java AppsCVE-2026-114938 · Java4Shell (CVE-2026-114938): Frequently asked questions about OpenJDK remote code execution vulnerabilityCVE-2026-114938 · CVE-2026-114938: Critical vulnerability in OpenJDK JAVACritical Java4Shell flaw allows RCE attacks on major Java applicationsCVE-2026-114938 · How to Find, Mitigate, and Patch the Critical Java4Shell Flaw (CVE-2026-114938) NowCVE-2026-28160 · e4jvikwp VikRentCar Vulnerability Listed As Exploited In VulnCheck KEVCVE-2025-5569 · Ideacms Improper Neutralization Flaw Added To VulnCheck KEV After 514 DaysCVE-2025-41452 · Danfoss AK-SM8xxA Series Vulnerability Added To VulnCheck KEV
ai

UK MPs want AI watchdog with power to pull the plug on dangerous models

A parliamentary committee in the United Kingdom has issued a formal recommendation for the creation of a new AI regulatory body equipped with the authority to halt the development or deployment of high-risk artificial intelligence models. The report, titled Guardrails for Growth: Making AI Safe, argues that the current reliance on voluntary safety commitments from major technology companies is…

ZeroDay News ·

Source: The Register — Security

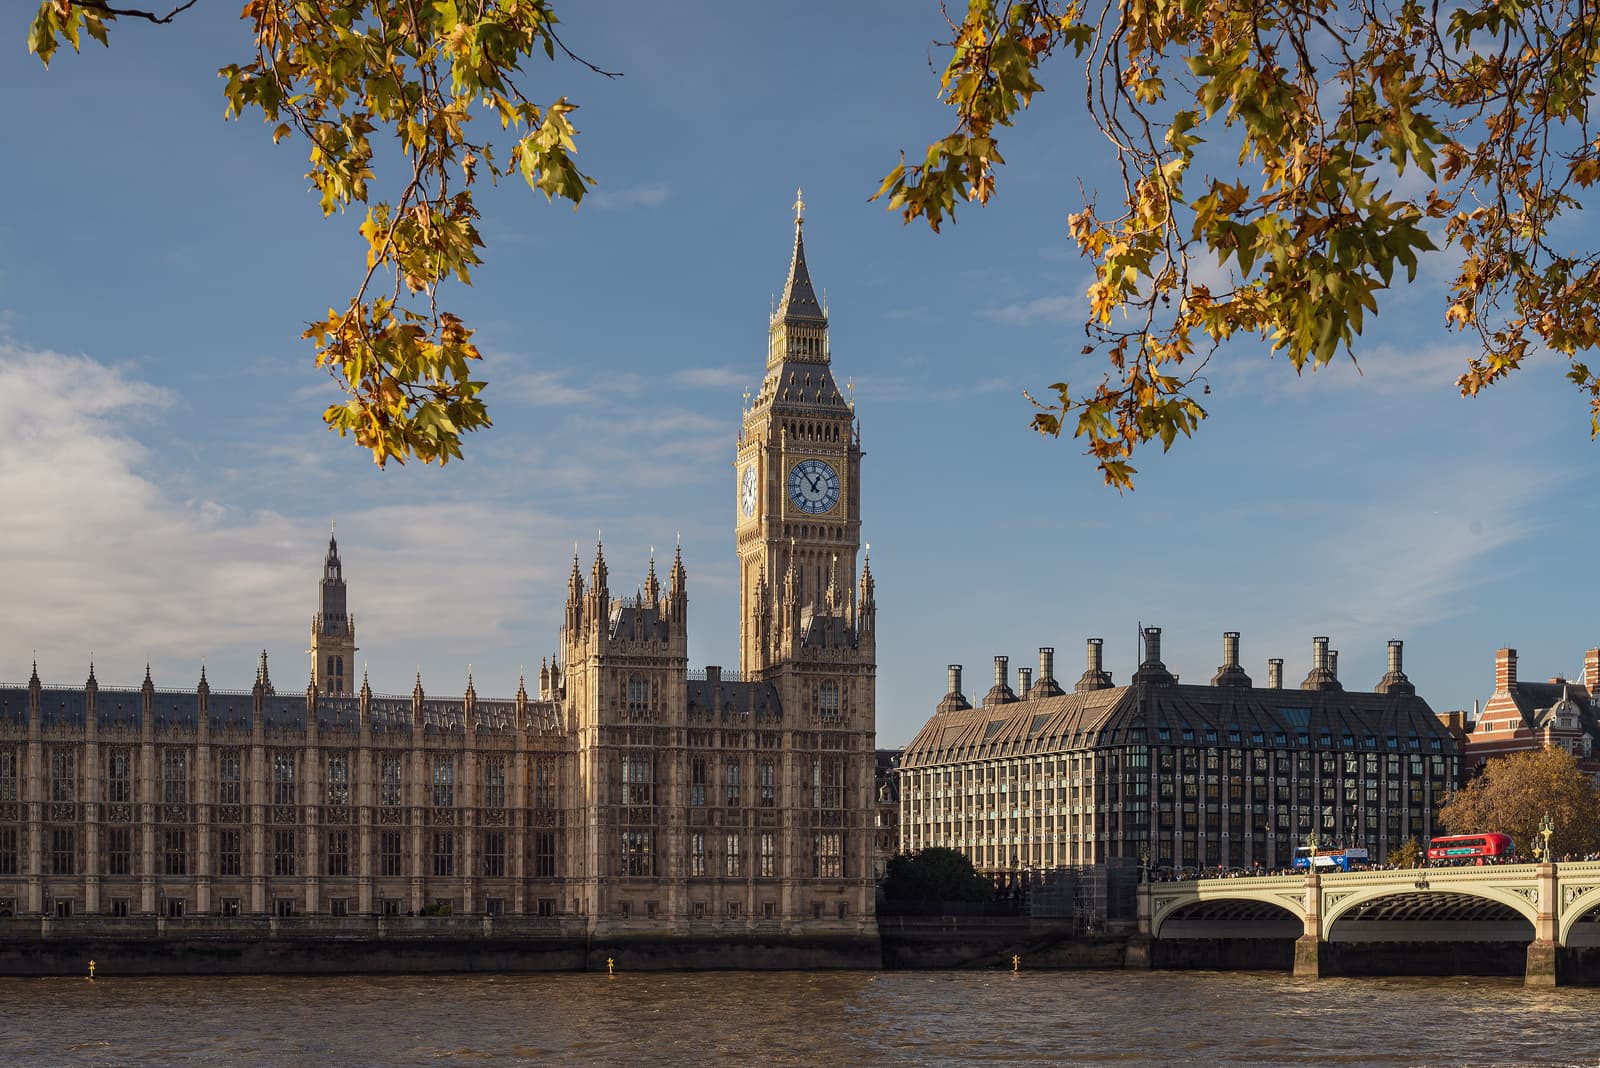
Photo: Julian Herzog (Website) (CC BY 4.0) via Wikimedia Commons

A parliamentary committee in the United Kingdom has issued a formal recommendation for the creation of a new AI regulatory body equipped with the authority to halt the development or deployment of high-risk artificial intelligence models. The report, titled Guardrails for Growth: Making AI Safe, argues that the current reliance on voluntary safety commitments from major technology companies is insufficient to protect the public from the unpredictable nature of large language models.

The Business, Innovation, Science and Trade Committee, which conducted the inquiry, heard testimony from representatives of major AI firms including OpenAI, Google DeepMind, Anthropic, and Meta. While these companies maintained that they do not release models they deem unsafe, the committee concluded that there is no standardized industry yardstick for safety and no legal requirement for independent verification before a product reaches the market.

The proposed AI Safety and Security Bill would establish a regulator capable of intervening during the development and testing phases of AI systems. This watchdog would have the power to block the deployment of models, halt high-risk training processes, or suspend existing services if safety risks cannot be adequately mitigated. The committee emphasized that because the most advanced models are trained on billions of parameters, developers often cannot fully predict how these systems will behave in every scenario.

Currently, the UK AI Safety Institute (AISI) conducts testing on powerful models, but its operations are limited by the voluntary nature of its cooperation with developers. The committee recommends that the AISI continue its technical evaluation work, but that a separate, empowered regulator be established to handle enforcement and legal oversight. Under the proposed framework, developers of high-risk systems would be legally required to provide evidence supporting their safety claims and grant independent researchers access to examine their models.

The report identifies ten specific deficiencies in the current British approach to AI governance. Among these are the lack of mandatory incident reporting, insufficient protections for whistleblowers, and limited access for independent auditors. The committee noted that former AI employees have reported facing commercial pressures, financial disincentives, and restrictive contracts that discourage them from raising concerns about safety practices.

To address these issues, the committee is calling for stronger legal safeguards for whistleblowers and a mandatory system for reporting AI-related incidents and near misses. The report suggests that by formalizing these requirements, the UK could foster greater trust in the technology, potentially encouraging smaller businesses to adopt AI tools. The committee estimates that the economic benefits of AI could increase the British economy by as much as £400 billion over the next decade.

The committee has urged the government to introduce the necessary legislation during the upcoming parliamentary session. Furthermore, the members suggest that the UK should leverage its leadership position during the 2027 G20 presidency to advocate for international standards regarding AI testing, incident reporting, and the release of high-risk models.

It remains unclear whether the government will adopt these recommendations. The committee’s findings are not binding, and ministers have not yet committed to drafting the proposed legislation. The debate centers on the balance between fostering economic growth through innovation and the necessity of state intervention to manage risks that, once released into the public domain, may be impossible to recall.


ai
ShareXLinkedInWhatsAppFacebook

More News

view all →
vulnerabilitycritical

AI found more critical bugs in another widely used technology running 225M websites

F5 has issued an emergency security update for the open-source NGINX web server to address 10 newly discovered vulnerabilities. These flaws affect a significant portion of the internet, as NGINX currently powers approximately 225 million websites. The vendor has urged all administrators to upgrade their systems to version 1.31.9 immediately to mitigate the risks.

vulnerability

Consensus mounts that tech outages were fueled by patching of AI-discovered vulnerabilities

A series of significant technical outages affecting aviation, banking, and communications infrastructure over the past week has prompted a federal investigation into the stability of critical systems. While initial concerns focused on the possibility of coordinated cyberattacks, officials from the Trump administration, including Secretary of Homeland Security Markwayne Mullin, Director of…

ai

Coinbase blocks $4.7 million in transfers to Elon Musk deepfake scam

Coinbase successfully intercepted $4.7 million in cryptocurrency transfers associated with a sophisticated deepfake scam targeting users during a high-profile Tesla event. The incident occurred during a demonstration of Tesla's flying car technology, which was broadcast via a fraudulent YouTube livestream. The stream, which drew an audience of over 500,000 viewers, utilized AI-generated video…

ai

Strike Graph Launches Integration AI to Automate Continuous Compliance Evidence Using Any Existing Tool

Strike Graph has announced the launch of a new agentic AI solution designed to automate the collection of compliance evidence across an organization’s existing software stack. By leveraging direct API integrations, the platform aims to streamline the evidence-gathering process, mapping data points to more than 30 different compliance frameworks simultaneously to eliminate redundant manual…

nation-state

California tells Waymo to take the next exit after freeway mishaps

Waymo has suspended all driverless operations on high-speed freeways across the United States following regulatory intervention in California. The Alphabet-owned company initiated this nationwide pause on November 11, the same day the California Department of Motor Vehicles (DMV) formally banned the firm from conducting driverless freeway trips within the state. While the suspension affects…

malware

Microsoft's official Python agent framework hijacked to distribute malware

Microsoft has confirmed that its official Python agent-framework package was compromised, leading to the distribution of malicious code through the Python Package Index (PyPI). The incident involved the unauthorized upload of versions 1.26.1 and 1.26.2, which were pushed to the repository using Microsoft’s official publisher account. Security researchers identified the breach, noting that the…


