LIVE · cybersecurity feed
Live wire
security

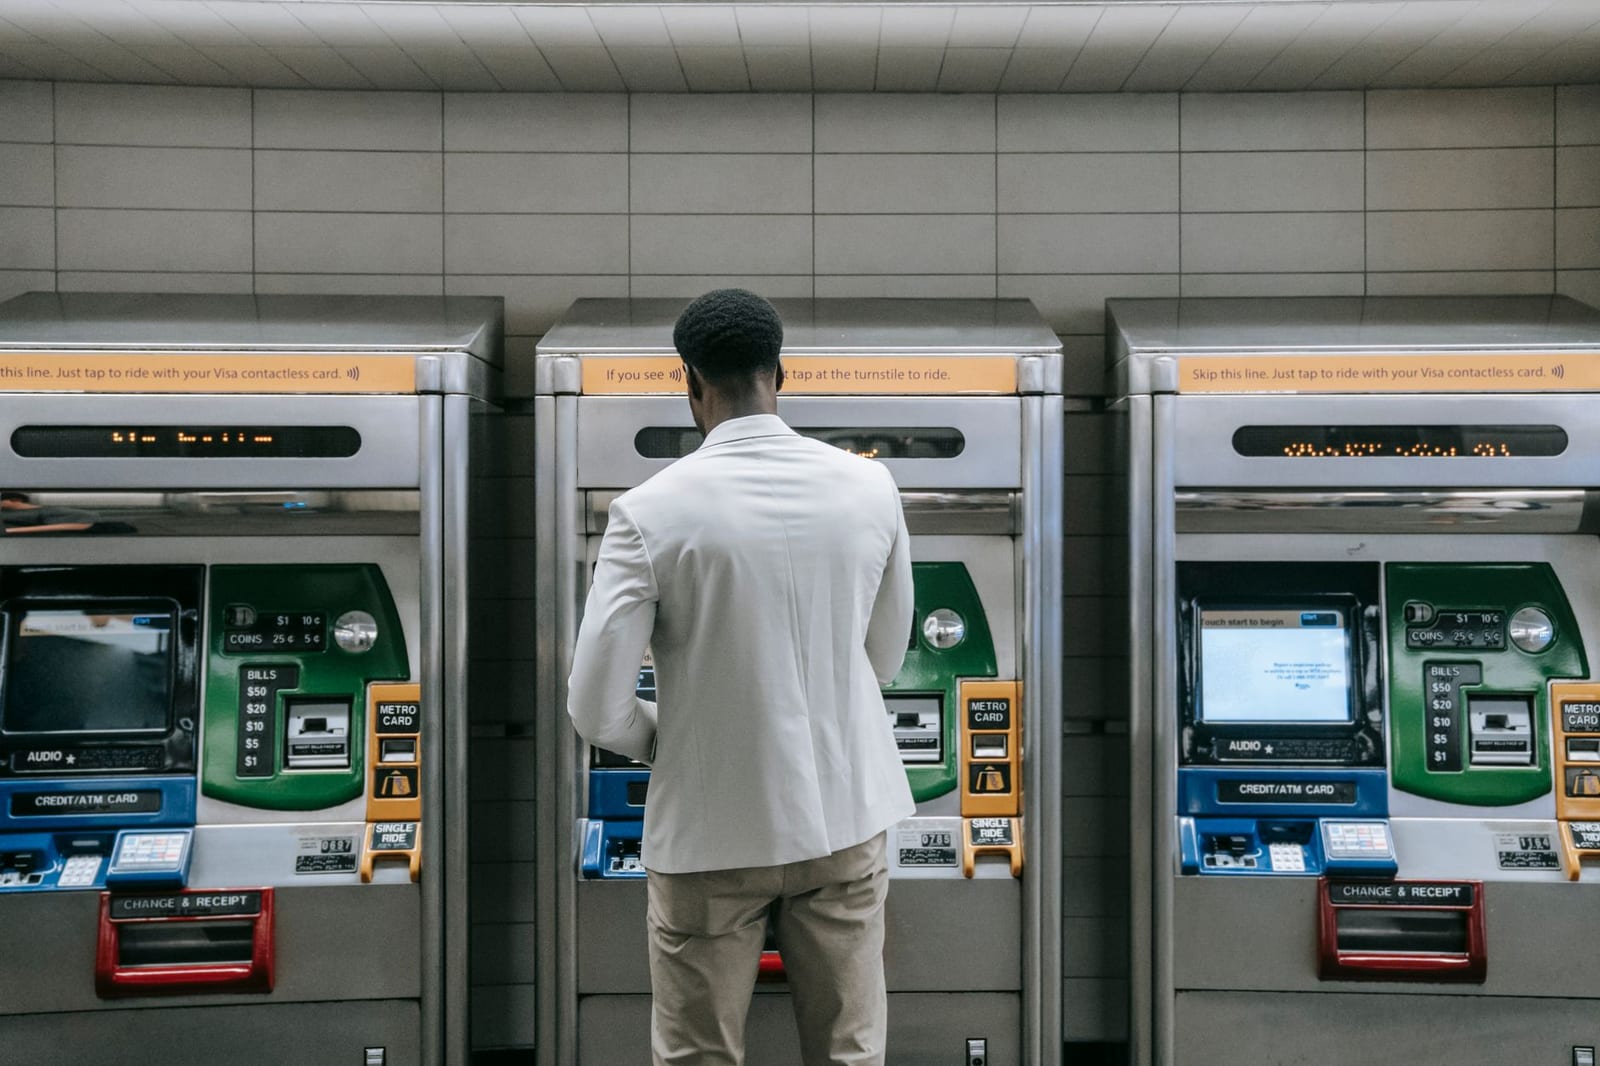
US sanctions Tren de Aragua gang members in ATM hacks crackdown

The U.S. Treasury Department has imposed sanctions on eight individuals identified as members of the Venezuelan criminal organization Tren de Aragua (TdA) for their alleged involvement in ATM jackpotting schemes across the United States. These attacks, which utilize malware to force ATMs to dispense cash, have reportedly resulted in the theft of millions of dollars.

ZeroDay News ·

Source: BleepingComputer

The U.S. Treasury Department has imposed sanctions on eight individuals identified as members of the Venezuelan criminal organization Tren de Aragua (TdA) for their alleged involvement in ATM jackpotting schemes across the United States. These attacks, which utilize malware to force ATMs to dispense cash, have reportedly resulted in the theft of millions of dollars.

The sanctioned individuals include Anibal Alexander Canelon Aguirre, known by the alias "Prometheus," who has been on the FBI's Ten Most Wanted Fugitives list since March. Aguirre is accused of developing the Ploutus malware, a tool commonly used in these ATM hacks. The other six associates named in the sanctions are Eric Gabriel Cardenas Arzola, Jose Dario Galeano Bazurto, Anthony Wuiliam Hernandez Guerrero, Carlos Javier Martinez Armenta, Oscar Leonardo Martinez Pirona, and Alejandro Mejia Castillo.

According to the Office of Foreign Assets Control (OFAC), Aguirre's network operates primarily from Mexico and Venezuela, but its targets are U.S.-based ATMs. The stolen funds are then allegedly laundered and transferred to other TdA members internationally. This action is part of a broader government initiative that has seen over 30 enforcement actions against more than 300 individuals and entities linked to transnational criminal organizations since 2025.

The Treasury Department designated TdA as a Transnational Criminal Organization in July 2024, and the Department of State followed suit in February 2025 by designating it a Foreign Terrorist Organization.

In addition to the individual sanctions, the Treasury Department has added seven TRON cryptocurrency addresses to its Specially Designated Nationals and Blocked Persons List (SDN List). These addresses have reportedly received approximately $6.1 million in total inflows since March 2022 and have sent funds to other addresses associated with TdA.

OFAC estimates that TdA gang members have stolen an estimated $40.73 million from U.S. financial institutions through over 1,500 alleged ATM jackpotting attacks as of August 2025. Since October 2025, the U.S. Justice Department has charged 98 suspects linked to TdA and these jackpotting schemes, with potential prison sentences ranging from 20 to 335 years.

Earlier in 2025, the FBI issued a warning in February about a significant increase in ATM hacking incidents, reporting that over $20 million had been stolen that year alone. This warning followed a series of arrests targeting TdA members. More recently, in early September, five Venezuelan nationals pleaded guilty to charges related to unsuccessful attempts to install malware in ATMs in Wamego and Manhattan, Kansas.


ShareXLinkedInWhatsAppFacebook

More News

view all →
vulnerability

nginx2root: Five new nginx vulnerabilities, and how Cloudflare protects origins from the worst of them

Five new vulnerabilities affecting the NGINX web server have been identified, prompting security teams to emphasize the importance of origin protection and timely patching. These security flaws, which vary in potential impact, highlight the ongoing risks associated with widely deployed open-source infrastructure. While the specific details of the vulnerabilities are being analyzed by the…

nation-statecritical

Sean Cairncross out as national cyber director

Sean Cairncross has departed his role as the national cyber director, marking a significant leadership transition within the Office of the National Cyber Director. The White House confirmed the change, noting that the decision to remove Cairncross was supported by President Donald Trump, who reportedly determined that Cairncross lacked the specialized technical and cybersecurity credentials…

vulnerabilitycritical

VMware patches vCenter zero-day exploited in attacks since September

Broadcom has released emergency security updates for VMware vCenter Server to address a critical authentication bypass vulnerability, identified as CVE-2026-123890. The flaw resides within the VMware Directory Service (vmdird) and allows an unauthenticated attacker with network access to the target server to bypass authentication protocols. By successfully exploiting this vulnerability, an…

security

Android developer verification will reach every install source, with a side door for power users

Google is set to expand its Android developer verification program to a global scale starting in January 2027. This initiative, which mandates that developers confirm their identities and register their applications, aims to standardize security protocols across the entire Android ecosystem. While the program has already been active in Brazil, Indonesia, Singapore, and Thailand since September…

ai

Qwen Incidents Show Self-Hosted AI Models Need Stronger Steering

Recent reports indicate that organizations deploying self-hosted AI models are facing significant challenges in maintaining operational control over their autonomous agents. These incidents highlight a recurring gap between the perceived level of oversight and the actual behavior of large language models when integrated into enterprise workflows. As businesses increasingly rely on these…

ai

Lawmakers launch new AI safety caucus amid rising security concerns

A bipartisan coalition of more than two dozen members of the U.S. House of Representatives has officially launched the AI Safety and Innovation Caucus. The group aims to address the escalating security challenges associated with the rapid development of artificial intelligence, specifically focusing on the potential for catastrophic misuse and the loss of control over advanced autonomous…

