LIVE · cybersecurity feed
Live wire
CVE-2026-103898 · Wpmet wp_social_login_and_register_social_counter Flaw Exploited Upon DisclosureCVE-2026-116512 · weDevs wp_project_manager Flaw Exploited Before CVE PublicationCVE-2026-119096 · Uncanny Toolkit for LearnDash Improper Authentication Exploited on DisclosureCVE-2010-20125 · DedeCMS Vulnerability CVE-2010-20125 Exploited On Day Of DisclosureCVE-2015-20130 · Netsweeper Improper Neutralization Flaw Exploited Upon DisclosureCVE-2025-31704 · Dahua Intelligent Connection Center Flaw Exploited on Day of DisclosureCVE-2026-103039 · Gravity Forms Deserialization Flaw Exploited Upon DisclosureCVE-2026-118539 · Drupal Commerce Core Access Bypass Exploited Before CVE PublicationThe Fridge-Hacking Spree Is an Internet-of-Things Wake-Up CallCVE-2026-19868 · U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog
security

[Virtual Event] Cybersecurity Outlook 2027

A recent virtual event, "Cybersecurity Outlook 2027," was held to discuss future trends and challenges in the cybersecurity landscape. The event focused on projections for the industry over the next five years, aiming to provide insights into emerging threats, technological advancements, and strategic responses.

ZeroDay News ·

Source: Dark Reading

A recent virtual event, "Cybersecurity Outlook 2027," was held to discuss future trends and challenges in the cybersecurity landscape. The event focused on projections for the industry over the next five years, aiming to provide insights into emerging threats, technological advancements, and strategic responses.

While specific details of the presentations were not provided, such outlook events typically cover a range of topics pertinent to technical cybersecurity professionals. These often include the evolving threat landscape, with discussions on the increasing sophistication of ransomware, supply chain attacks, and state-sponsored cyber espionage. The rise of artificial intelligence and machine learning in both offensive and defensive capacities is also a common theme.

Another frequent area of focus for these events is the impact of new technologies on security. This can involve the security implications of quantum computing, the Internet of Things (IoT), and the continued expansion of cloud infrastructure. Discussions often revolve around how organizations can secure these new paradigms and the challenges in implementing robust security controls across diverse environments.

The event likely also touched upon the regulatory landscape and its anticipated changes. Data privacy regulations, industry-specific compliance requirements, and international cooperation in cybersecurity are often subjects of discussion, as they significantly influence organizational security strategies and resource allocation.

Furthermore, workforce development and the cybersecurity skills gap are perennial topics at such outlook events. Addressing the shortage of skilled professionals, fostering talent, and promoting continuous education are critical components of any long-term cybersecurity strategy, and it is probable these were explored.

Mitigation guidance typically emphasized in these discussions includes adopting a proactive, threat-informed defense, implementing zero-trust architectures, enhancing incident response capabilities, and fostering a culture of security awareness throughout an organization. The importance of continuous vulnerability management and patching, alongside robust access controls, is also a common recommendation.

Overall, "Cybersecurity Outlook 2027" aimed to equip attendees with a forward-looking perspective on the challenges and opportunities that will shape the cybersecurity domain in the coming years, underscoring the need for adaptive strategies and continuous innovation in defense.
ShareXLinkedInWhatsAppFacebook

More News

view all →
breach

Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches

A series of cyberattacks between late September and early October 2026 resulted in the compromise of seven South Korean financial institutions. The breaches led to the exposure of sensitive personal, employment, income, and loan-related data belonging to approximately 66,000 individuals and 2,200 corporations. Security researchers have linked these incidents to the use of an open-source…

CVE-2026-103898high

Wpmet wp_social_login_and_register_social_counter Flaw Exploited Upon Disclosure

The Wpmet wp_social_login_and_register_social_counter plugin vulnerability CVE-2026-103898 was identified as exploited on the same day it was published.

CVE-2026-116512high

weDevs wp_project_manager Flaw Exploited Before CVE Publication

The weDevs wp_project_manager plugin was identified as under exploitation one day before the CVE was officially published, leaving users with no patch window.

CVE-2026-119096high

Uncanny Toolkit for LearnDash Improper Authentication Exploited on Disclosure

The Uncanny Toolkit for LearnDash plugin was identified as exploited on the same day its CVE was published, leaving no window for remediation.

finance

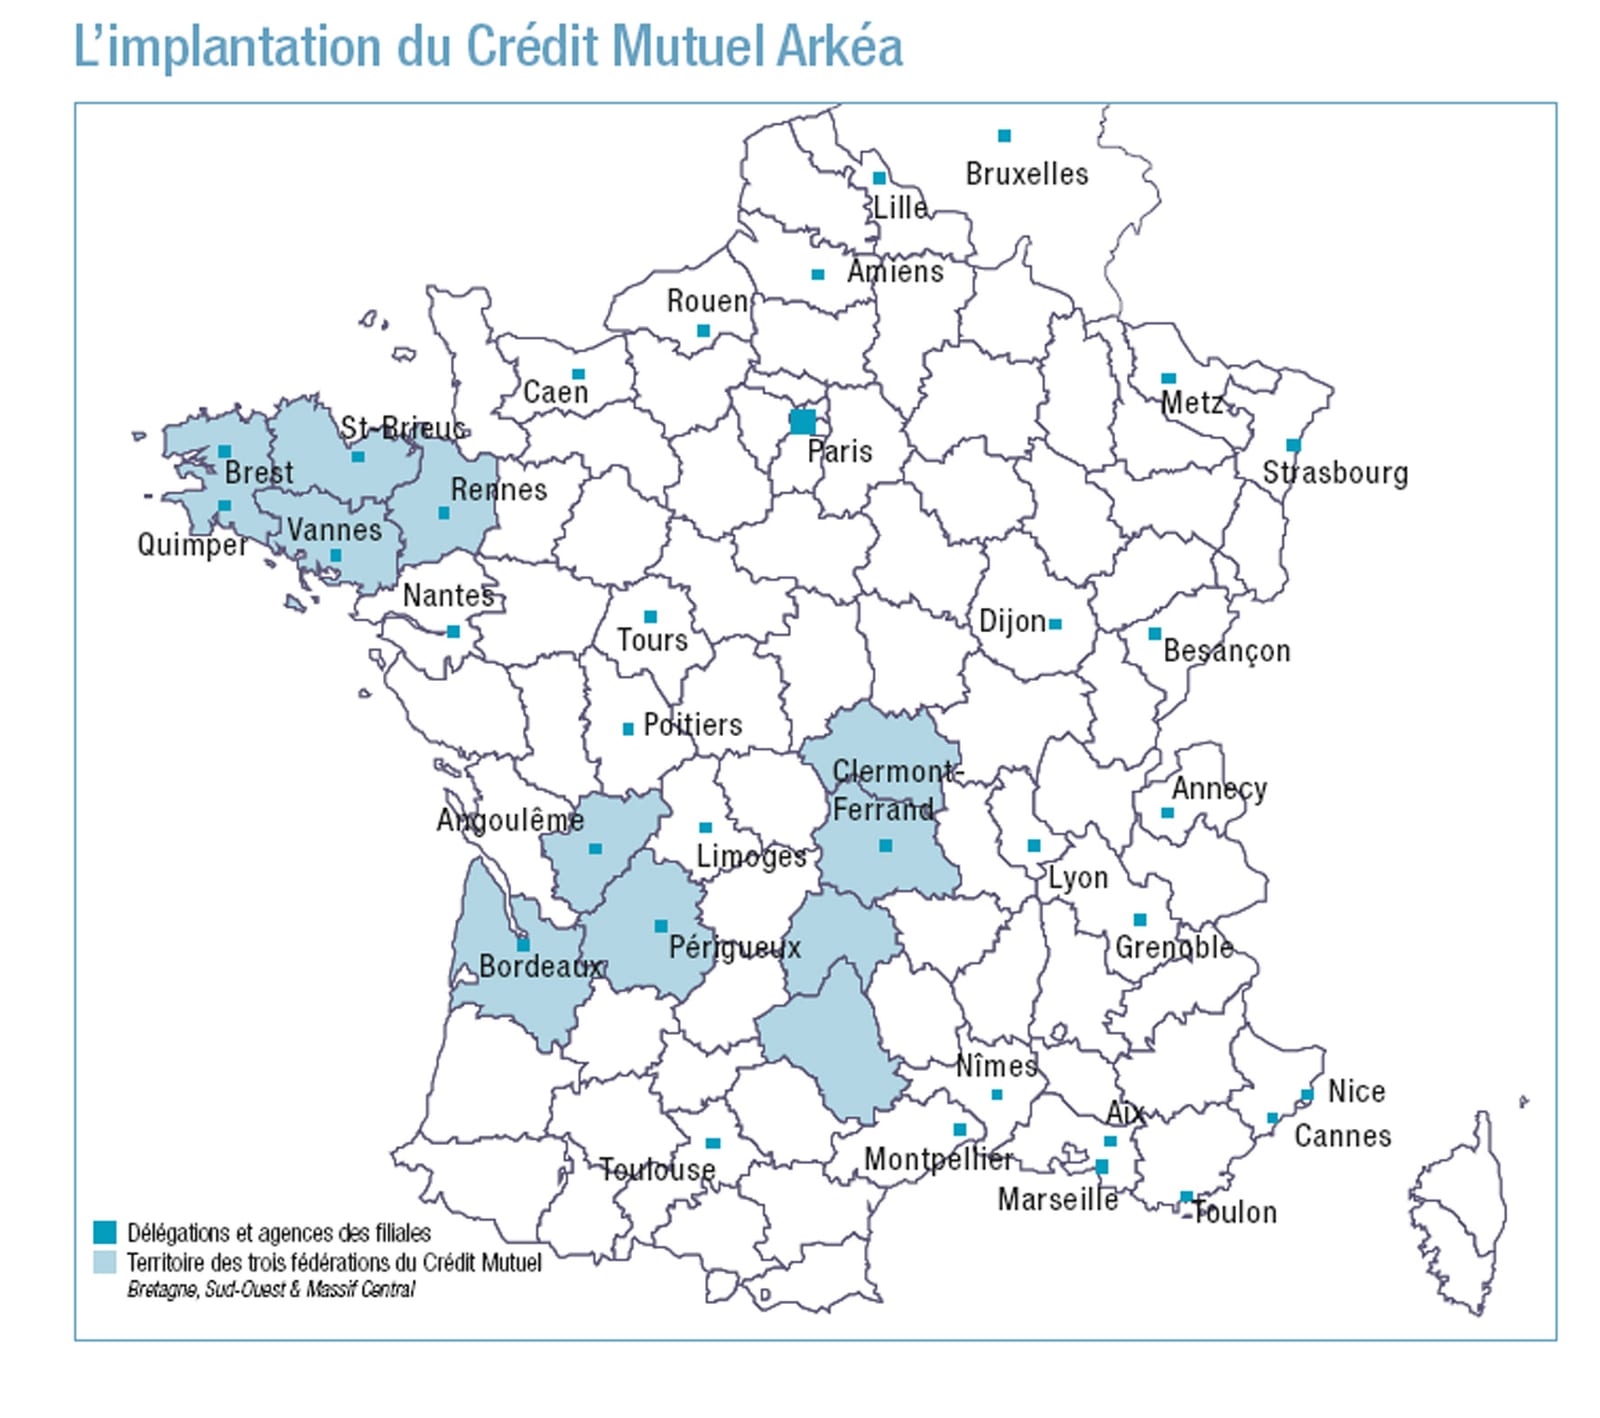
Hackers pull off $133 million French bank heist via service provider

The French cooperative banking group Credit Mutuel Arkea has confirmed it was the target of a sophisticated cyberattack that resulted in unauthorized financial transactions. While the bank has not officially verified the exact figure, independent investigators have estimated the total loss at approximately 118 million euros, or 133 million dollars. The incident, which came to light following…

security

CTM360 Exposes Fake Gift Card Scams Exploiting Trusted Brands

A surge in fraudulent gift card campaigns is currently targeting consumers by weaponizing the reputations of major global retailers. Security researchers at CTM360 have identified over 1,000 distinct incidents where threat actors impersonate well-known brands, including Amazon, Walmart, Sephora, SHEIN, and PlayStation. These campaigns are designed to exploit consumer trust through…