
LIVE · cybersecurity feed
Live wire
phishing

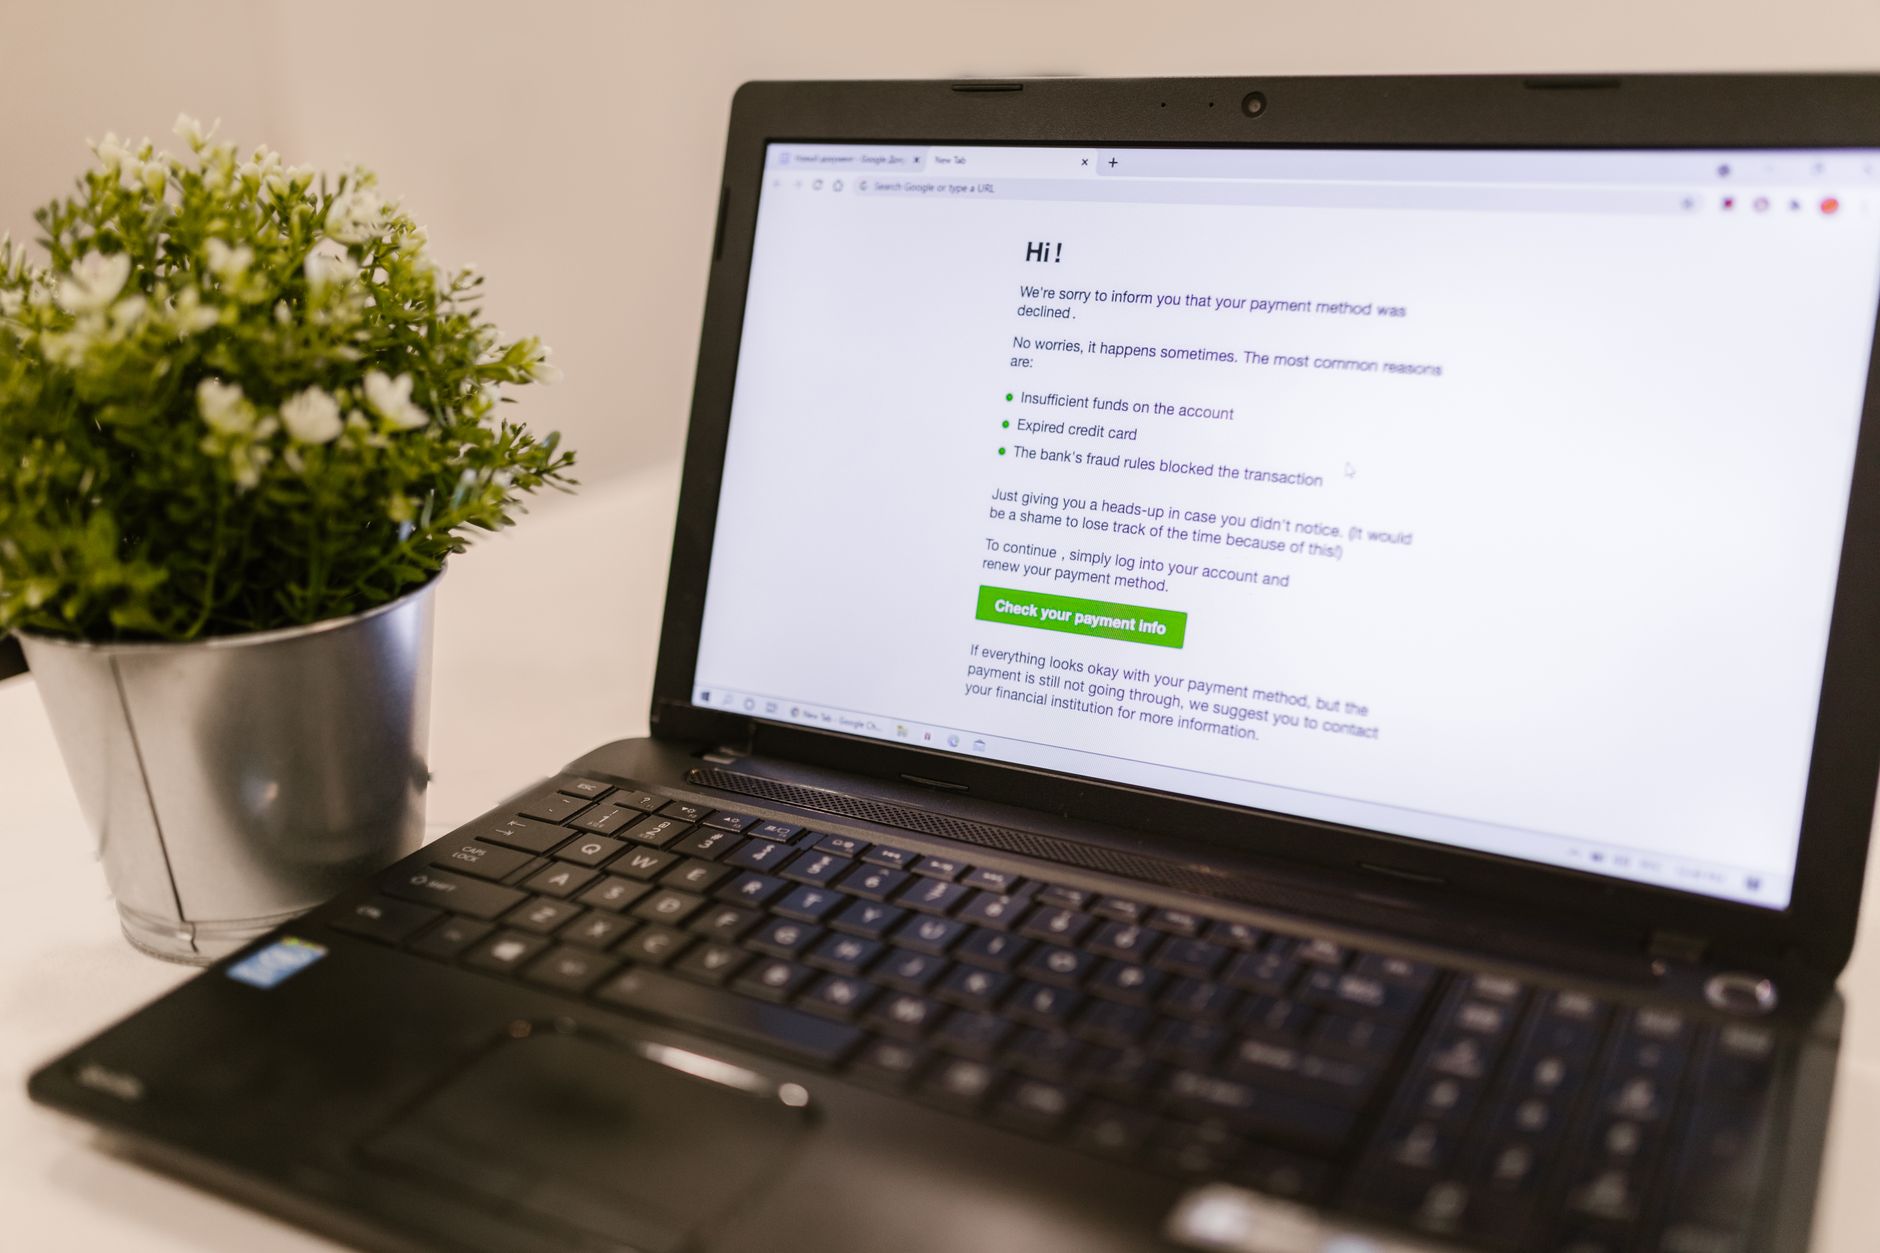
Year-long Russian attacks infect users as soon as they look at an email

A Russian state-sponsored threat group, identified as Laundry Bear or Void Blizzard, has been exploiting a cross-site scripting (XSS) vulnerability in the Zimbra web-based email and collaboration suite for at least a year. The attacks, which began in July 2025, allow adversaries to compromise victims simply by viewing a malicious email, without requiring any clicks or file openings.

ZeroDay News ·

Source: The Register — Security

A Russian state-sponsored threat group, identified as Laundry Bear or Void Blizzard, has been exploiting a cross-site scripting (XSS) vulnerability in the Zimbra web-based email and collaboration suite for at least a year. The attacks, which began in July 2025, allow adversaries to compromise victims simply by viewing a malicious email, without requiring any clicks or file openings.

This campaign targets CVE-2025-66376, an XSS flaw in Zimbra Collaboration Suite (ZCS) that was patched in November 2025. However, Laundry Bear began exploiting the vulnerability months before the patch was released. The attacks involve sending specially crafted HTML email messages that, when viewed, inject malicious JavaScript into the victim's web browser.

The objective of these intrusions is primarily to acquire sensitive information for the Russian Federation, with a focus on covertly obtaining email data. The campaign has targeted a wide range of Western organizations, including those in the defense industrial base, federal and local governments, education, energy, law enforcement, media, non-governmental organizations, and technology sectors.

Upon successful exploitation, the attackers exfiltrate a significant amount of data. This includes the victim's email communications from the last 90 days, email addresses and passwords, organizational email directories such as global address lists, two-factor authentication tokens, and newly generated application passcodes. The stolen credentials are then used to maintain persistent access to the victims' email, allowing the attackers to modify account preferences and continue collecting authentication information.

The stolen data is stored on an unattributable virtual private server (VPS) utilizing a custom collection framework named "Flowerbed." This framework is described as a Python project that leverages Docker for containerization. Analysis of the Flowerbed codebase suggests that artificial intelligence may have played a role in its development due to its simplistic nature.

Several email addresses have been identified as being used in this campaign, including ivanka.zurabishvili@proton[.]me, zmul1@buildandconsulting[.]com, garrysmithme@pinmx[.]net, and hostingclient@pinmx[.]net.

A joint security alert issued by 27 US, UK, and other international government agencies attributes these intrusions to Laundry Bear/Void Blizzard. The alert, spanning 31 pages, includes an extensive section detailing indicators of compromise (IOCs) to help organizations identify compromised individuals and systems.

Organizations are strongly advised to review these IOCs and to minimize employees' use of the ZCS webmail client until they have updated to a patched version that is no longer vulnerable to CVE-2025-66376.


phishing
ShareXLinkedInWhatsAppFacebook

More News

view all →
security

Canadian cybersecurity executive arrested in federal extortion case

A Canadian cybersecurity executive was arrested in Pennsylvania on Thursday, facing federal charges of conspiracy to commit extortion. Edward Dubrovsky, 54, a co-founder and former Chief Operating Officer of CYPFER, a firm specializing in ransomware negotiation, is charged with conspiring to threaten the confidentiality of information for extortion and conspiring to commit Hobbs Act extortion,…

breach

Criminal IP Introduces AITEM as the Next Evolution of Attack Surface Management

AI SPERA, the company behind the cyber threat intelligence platform Criminal IP, has announced AITEM (AI-Powered Threat Exposure Management), an expansion of its Attack Surface Management (ASM) offerings. AITEM aims to move beyond traditional asset discovery to provide a more comprehensive approach to understanding, prioritizing, and responding to security exposures. The platform is scheduled…

ai

AI Is Getting Really Good at Messing With Cybercriminals

Anti-cybercrime initiatives are increasingly deploying artificial intelligence to disrupt scammers by engaging them with lifelike bots, which the criminals mistake for genuine victims. This strategy aims to waste scammers' time and resources while gathering intelligence on their operations.

ransomware

FBI Arrests Ransomware Negotiation Firm Co-Founder in ShinyHunters Probe

The Federal Bureau of Investigation (FBI) has reportedly arrested Edward Dubrovsky, a co-founder of the ransomware negotiation firm Cypfer and currently associated with CyberSteward. The arrest is said to be part of the ongoing ShinyHunters investigation, specifically in connection with an incident involving FBI job applicant data.

ai

The Third-Party Agent Problem: Why Security Built for AI You Chose Misses the Agents You Didn't

A new report highlights a significant blind spot in enterprise security architectures concerning the proliferation of third-party AI agents. The forthcoming 2026 State of Agent Security Report indicates that current security models, often designed to protect AI systems directly chosen and deployed by an organization, frequently fail to account for AI capabilities embedded within third-party…

security

Insider Cyber Extortion Plot Against Industrial Firm Lands Engineer in Prison

A former core infrastructure engineer has been sentenced to prison for an attempted cyber extortion plot against an industrial firm. The engineer reportedly deleted administrative accounts and reset hundreds of user passwords, subsequently demanding a ransom of 20 Bitcoin to prevent further disruption to the company's servers.



