
india news
4 stories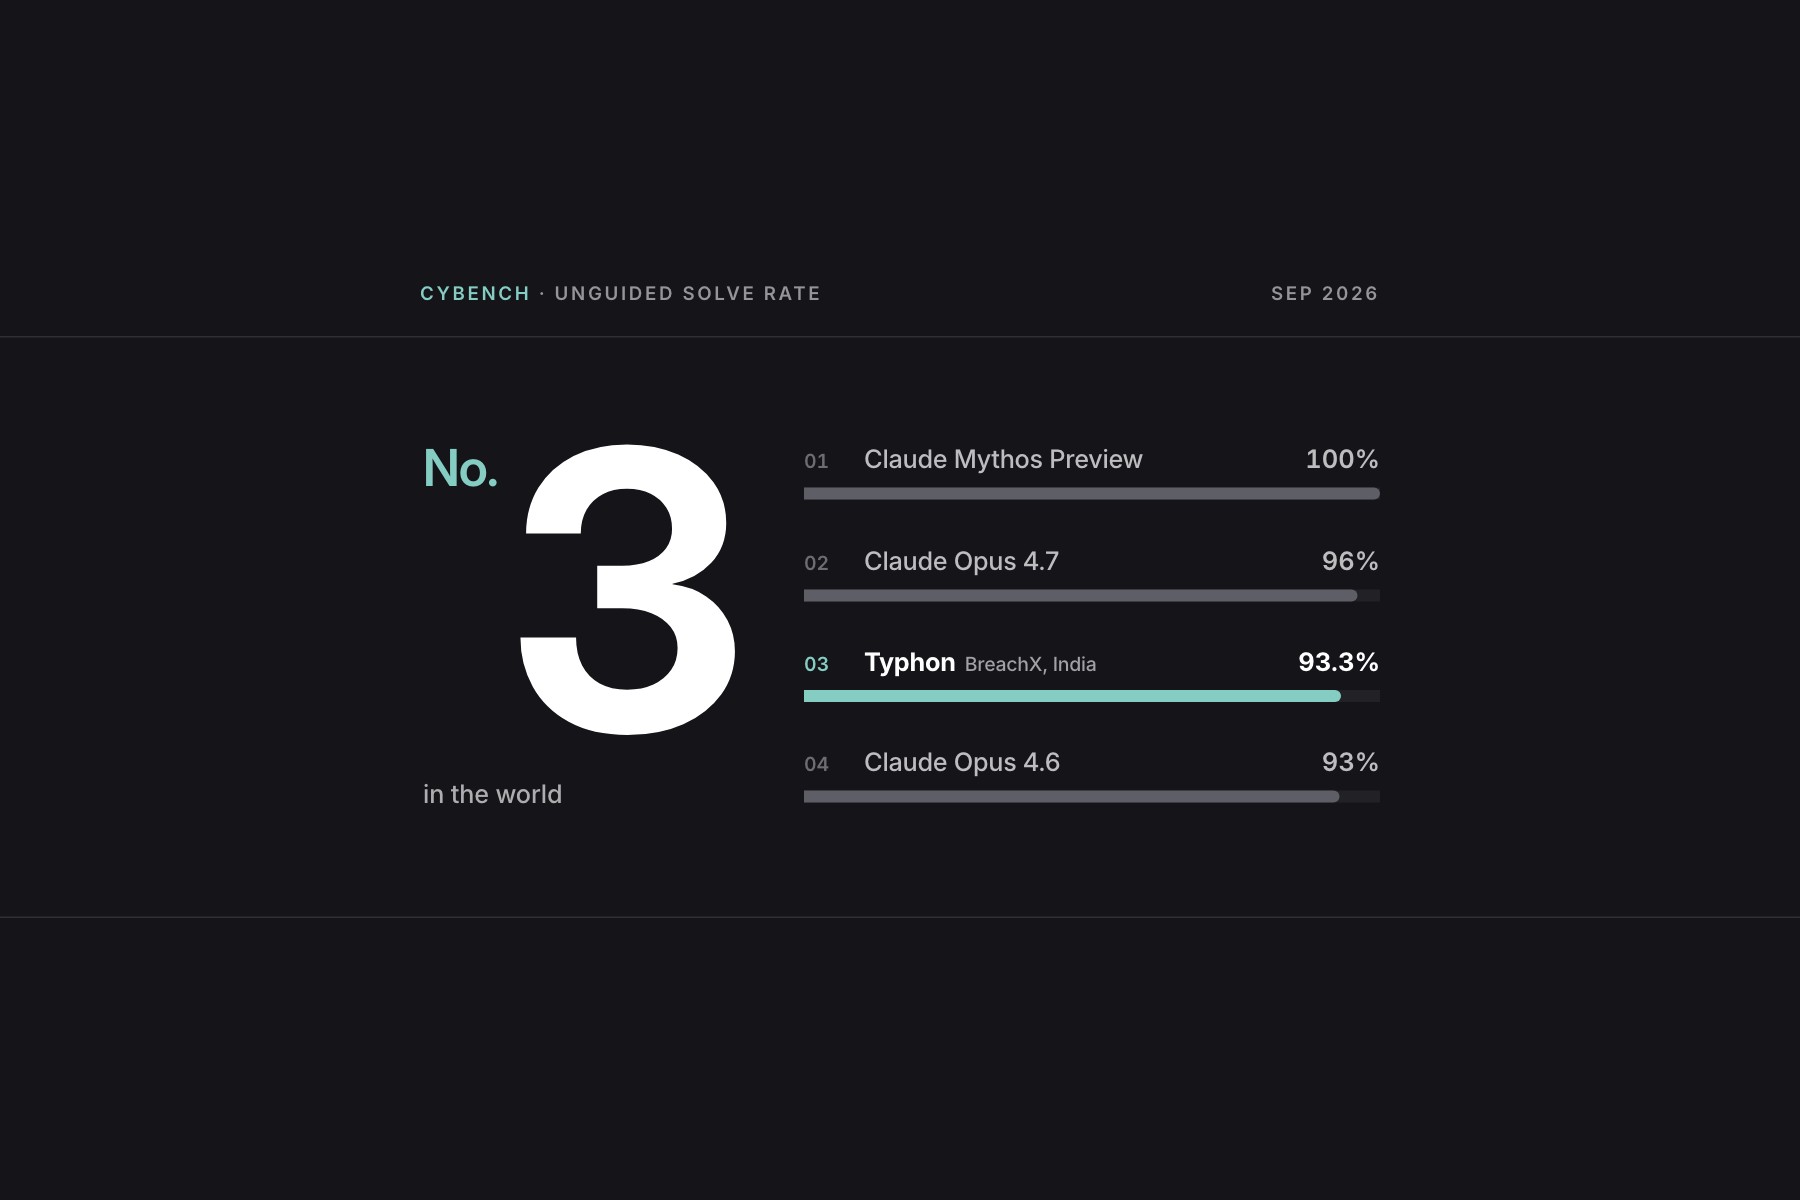
India's BreachX Puts Typhon Third on CyBench, Behind Only Anthropic's Mythos and Opus 4.7
Typhon scored 93.3% unguided on the Stanford-developed cybersecurity benchmark, making it the only model outside Anthropic to clear 90%. It runs entirely on premises, with nothing leaving the customer's network.
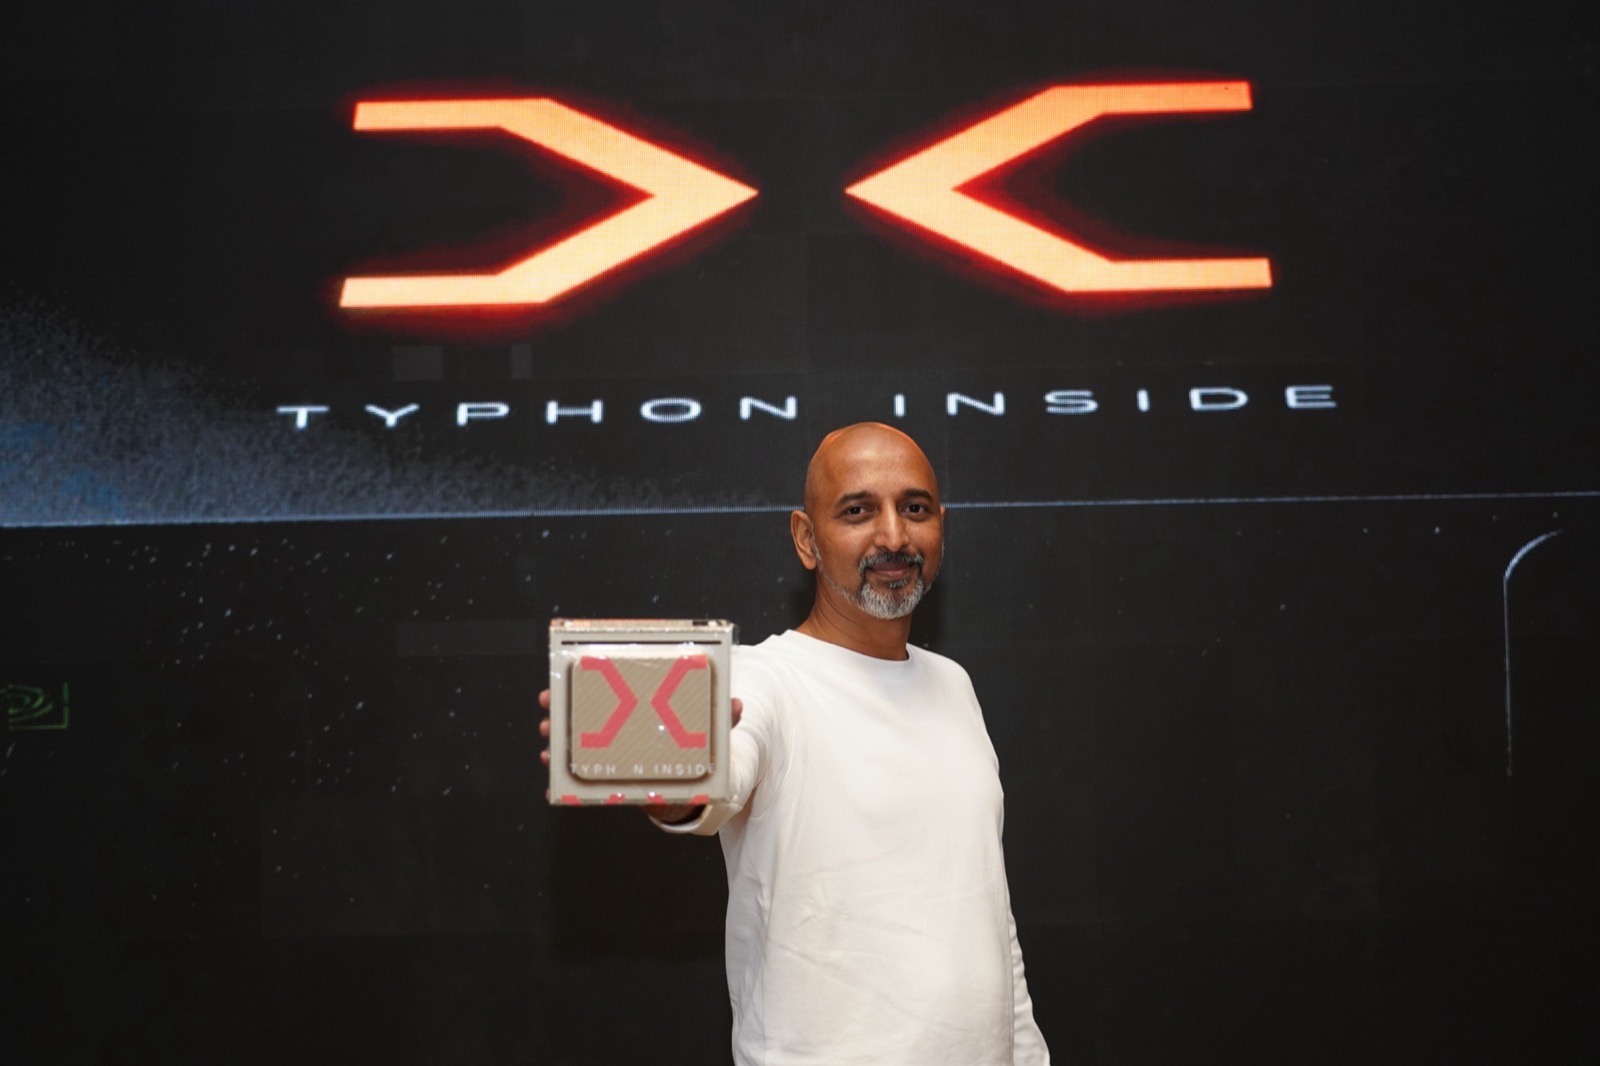
BreachX Launches Typhon, India-Built Sovereign Cybersecurity AI for Zero-Day Discovery and Defense
NEW DELHI, India, September 3, 2026: BreachX, an AI cybersecurity company and zero-day research lab, today unveiled Typhon, a family of sovereign cybersecurity AI models designed to discover previously unknown vulnerabilities, determine whether they can be exploited and generate protection, all within infrastructure controlled by the customer.
NIELIT Launches Cyber Kushti 2026, a National Hackathon That Scores Security Judgment Over Detection Speed
The National Institute of Electronics and Information Technology (NIELIT) used Independence Day to launch Cyber Kushti 2026, a national cybersecurity and artificial intelligence hackathon built around a question most competitions never ask: not whether a team can find security problems, but whether it can tell which reported problems are real, which matter most, and which deserve to be fixed…
CERT-In’s AI Vulnerability Blueprint: Why Indian CISOs Need Machine-Speed Risk Operations in the Post-Mythos Era
India's cybersecurity agency, CERT-In, has issued a new blueprint that significantly raises the bar for vulnerability remediation, demanding a shift from human-speed to machine-speed risk operations. This directive, released on May 25, 2026, mandates the containment of known exploited vulnerabilities on internet-facing and critical systems within 12 hours. This requirement stands in stark…