Critical5
High33
Medium3
Exploited (KEV)6

41 CVEs published in the last four months and 12 stories. Exploited flaws first.
Cisco has released patches addressing a dozen critical vulnerabilities across its product line. These security defects reportedly encompass a range of potential impacts, including unauthorized access, information leaks, privilege escalation, denial-of-service (DoS) attacks, and remote code execution (RCE). The widespread nature of these reported flaws suggests a significant security update…
Cisco has issued a warning regarding five critical vulnerabilities identified in its NX-OS data center network operating system, which could enable attackers to execute arbitrary code with root privileges on Nexus switches. In scenarios where remote code execution is not achievable, exploitation of these flaws could lead to process crashes and device reloads, resulting in denial-of-service…
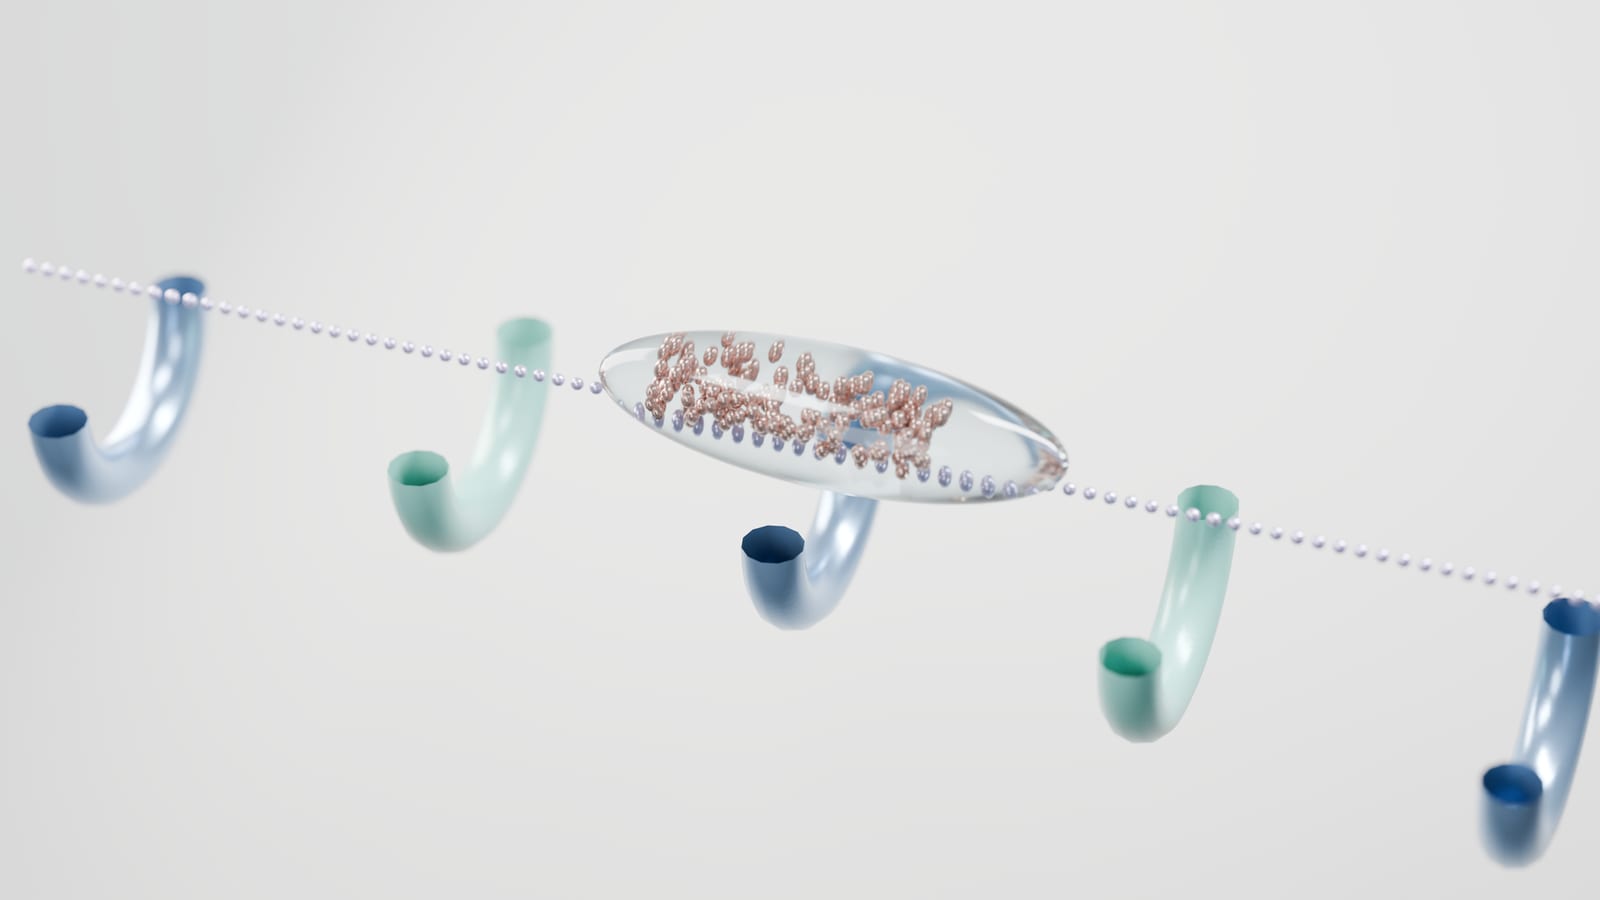
Cisco has unveiled a Quantum Network Controller, a research prototype designed to enable applications to request entanglement on demand from a quantum network, abstracting away the underlying hardware complexities. This controller manages the distribution of entanglement, a linked quantum state shared between distant points, which is a critical resource for quantum networks.
Cisco has confirmed that attackers are actively exploiting a zero-day SQL injection vulnerability, tracked as CVE-2026-76461, in its Secure Email Gateway appliances. The company's Product Security Incident Response Team became aware of the exploitation in September 2025 and has since provided indicators of compromise for organizations to check for potential breaches.
A critical authentication bypass vulnerability, designated CVE-2026-76460, has been reported in Cisco's Identity Services Engine (ISE). The flaw has been assigned a maximum CVSS score of 10.0, indicating its severe potential impact. This zero-day issue reportedly allows for an authentication bypass, highlighting significant concerns regarding API endpoint security within the affected product.
Cisco has issued an alert to customers regarding a second actively exploited zero-day vulnerability discovered within days, affecting its Identity Services Engine (ISE) product. The flaw, identified as CVE-2026-76460, carries a maximum severity rating of 10.0 and was exploited in the wild prior to Cisco's disclosure and subsequent patch release on Wednesday, September 17, 2026.
Cisco has issued an urgent warning regarding a maximum-severity zero-day vulnerability in its Identity Services Engine (ISE) and ISE Passive Identity Connector (ISE-PIC) products, which is actively being exploited in the wild. The flaw, identified as CVE-2026-76460, allows remote attackers to bypass authentication by exploiting an API weakness, regardless of the system's configuration.
Cisco has released an emergency security patch for a zero-day vulnerability affecting its Identity Services Engine (ISE) product, following reports of active exploitation. The flaw allows remote, unauthenticated attackers to bypass authentication mechanisms by sending specially crafted requests to affected ISE instances. This critical update addresses a significant security risk given the…
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical vulnerability in Cisco Secure Email Gateway, identified as CVE-2026-76461, to its Known Exploited Vulnerabilities (KEV) catalog. This addition mandates that federal civilian executive branch (FCEB) agencies address the flaw by September 17, 2026, to protect their networks from active exploitation.
Attackers have deployed a Linux rootkit on F5 BIG-IP APM devices, utilizing a method that hides a web shell in memory rather than writing it to disk. This technique makes detection more challenging for traditional security tools. F5 BIG-IP APM is a system designed for enforcing access policies.
Cisco has confirmed active exploitation of CVE-2026-20079, a critical authentication bypass vulnerability in its Secure Firewall Management Center (FMC) software. The flaw, which carries a maximum CVSS score of 10.0, allows unauthenticated, remote attackers to execute scripts and commands with root privileges on affected devices by sending specially crafted HTTP requests to the web interface.
Cisco has issued a warning to customers regarding several critical vulnerabilities across its product lines, including three rated as critical. Two of these impact the Cisco IOS XR operating system, which powers the company's carrier-grade equipment, while the third affects certain Nexus 9000 Series Switches.