
News Archive
1938 stories · page 26 of 81Every story we've published, newest first. Vulnerability records live in the CVE Tracker.
OpenAI Overhauls Model Security With Sandboxing, 30-Minute Alerts, and Training Pauses
The action taken by OpenAI comes in light of the Hugging Face incident and the discovery of the Astra model’s advanced capabilities. The post OpenAI Overhauls Model Security With Sandboxing, 30-Minute Alerts, and Training Pauses appeared first on SecurityWeek.
New Manic Android malware can exfiltrate data through nearby devices
A new Android malware named Manic targeting users in multiple European countries has a fallback data exfiltration mechanism that uses nearby infected devices. [...]
UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
The newly identified SPECTRE implant represents an evolution in commodity intrusion tooling, integrating cross-platform C2 operations, process injection, credential theft, anti-analysis protections, and kernel-level endpoint detection and response (EDR) bypass functionality.
UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Cisco Talos discovered a Chinese-speaking cybercrime group, tracked as UAT-10147, that targets a wide range of vulnerable web servers. This is an overview of the campaign, examining the countries affected, potential impact of BadIIS infections, the attack chain, and post-compromise tactics.
Attackers Exploit Collaboration Tools for Identity Theft
Researchers have identified a new attack vector where threat actors leverage enterprise collaboration platforms to conduct identity phishing and steal user credentials. The report outlines the methods used by attackers and provides actionable strategies for organizations to bolster their defenses against these evolving threats.
Updated ToxicPanda Variant Targets 140+ Banking and Crypto Apps
Zimperium lifts the lid on the ToxicPanda 2.0 Android banking Trojan
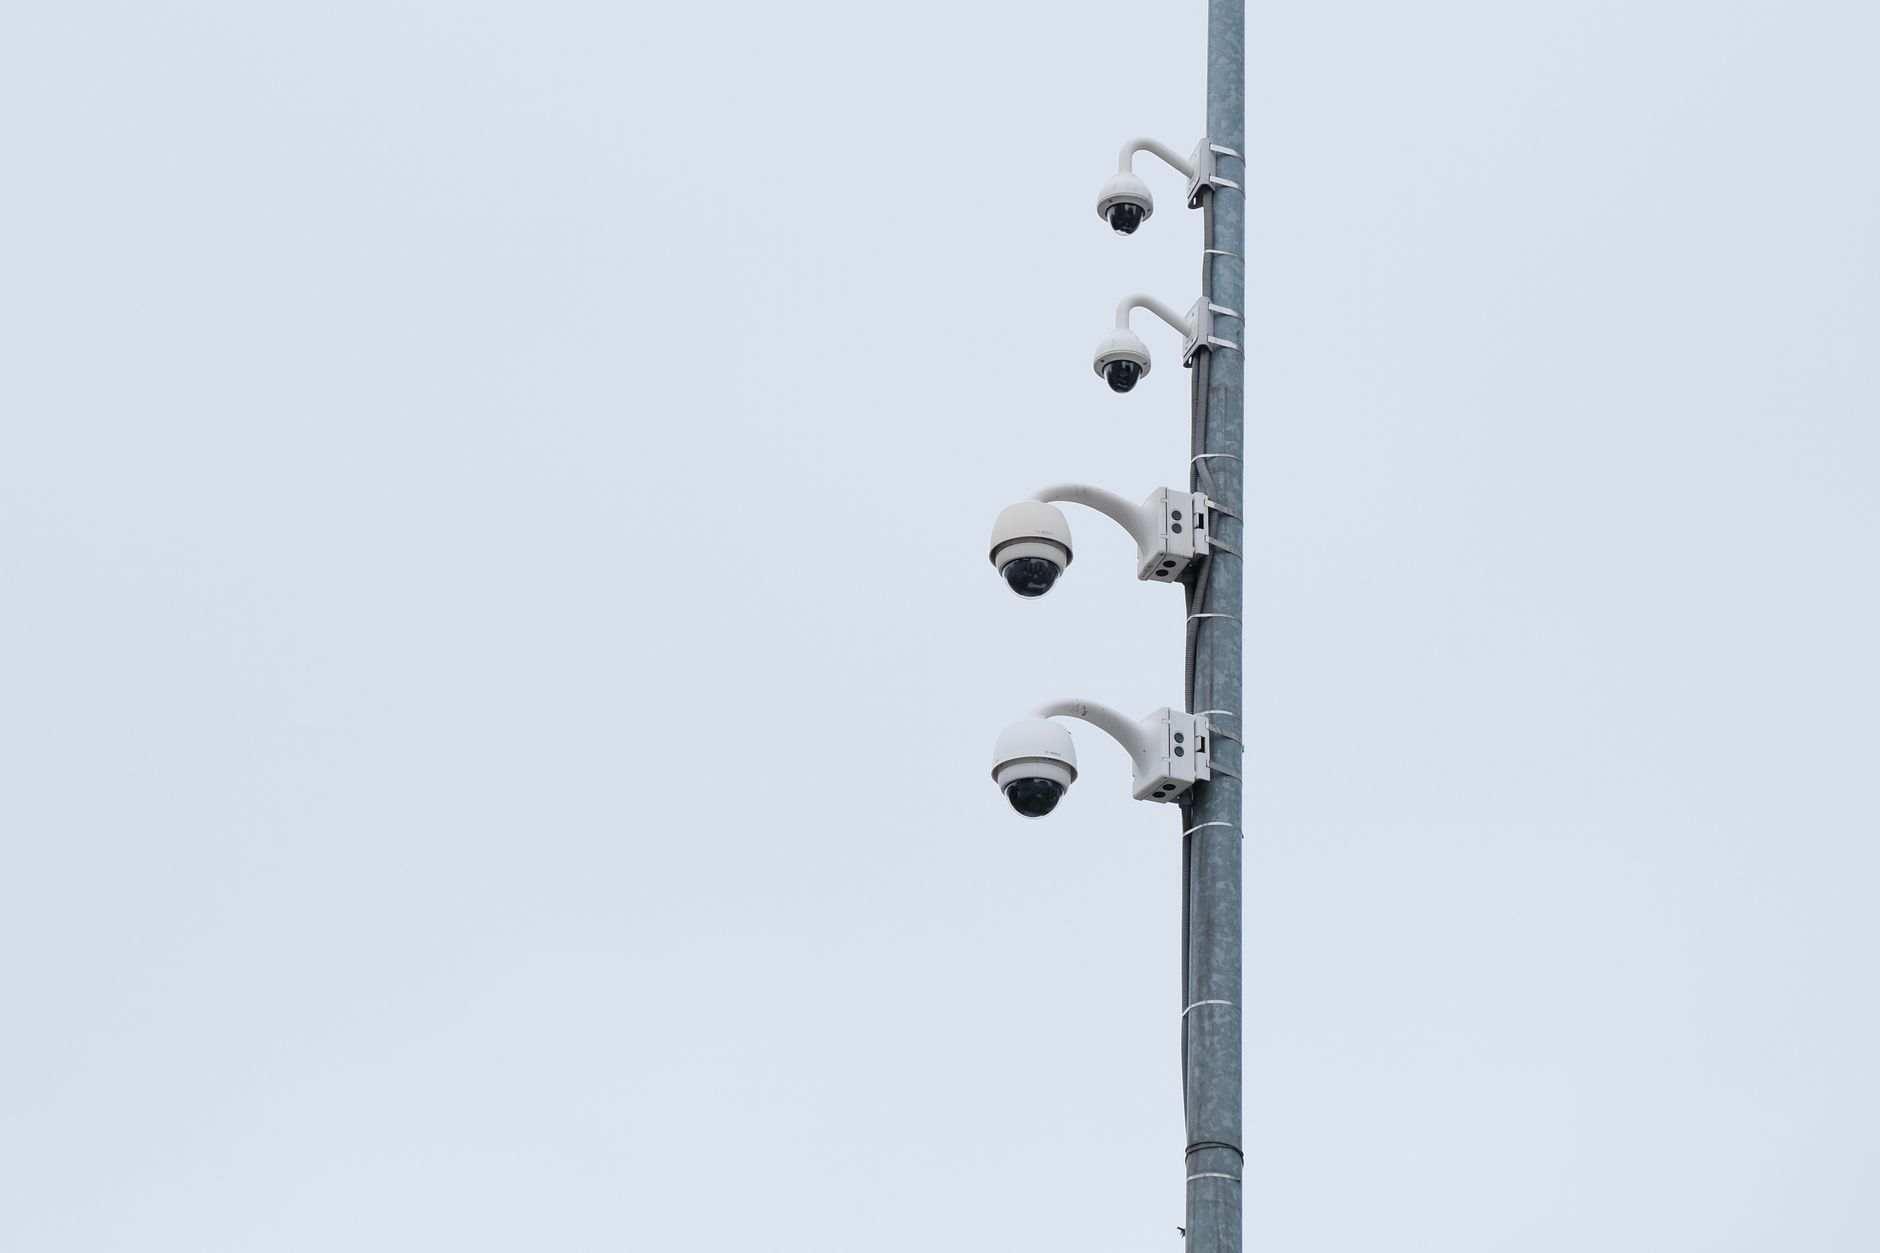
Police Are Hiding Their Use of Flock Surveillance Cameras
A usage policy for Flock license plate reader cameras tells police not to talk about the cameras: When cops use Flock to arrest someone in Wapello County, Iowa, they don’t want them to know. A usage policy for the automated license plate reader cameras in the county tells police, in no uncertain terms, to keep them a secret: “DO NOT MENTION ALPR USAGE TO THE OCCUPANTS OF THE VEHICLE,” the policy d
Critical Zimbra RCE flaw now actively exploited in attacks
CERT Polska, the Polish Computer Emergency Response Team (CERT), warned that attackers have begun exploiting a critical vulnerability in Zimbra Collaboration Suite (ZCS). [...]
Def Con Attendees Targeted by Persistent Phishing Campaign
Huntress researcher explains how they were targeted by an elaborate and persistent phishing scam following Def Con
OpenAI previews privacy-focused system for detecting AI misuse
OpenAI has introduced a new privacy-focused system called Private Safety Processing designed to detect misuse of its AI models without compromising user data. This system analyzes patterns across interactions while preventing OpenAI personnel from accessing sensitive content. The company plans a wider rollout in September, emphasizing collaboration with customers to refine its safety measures.
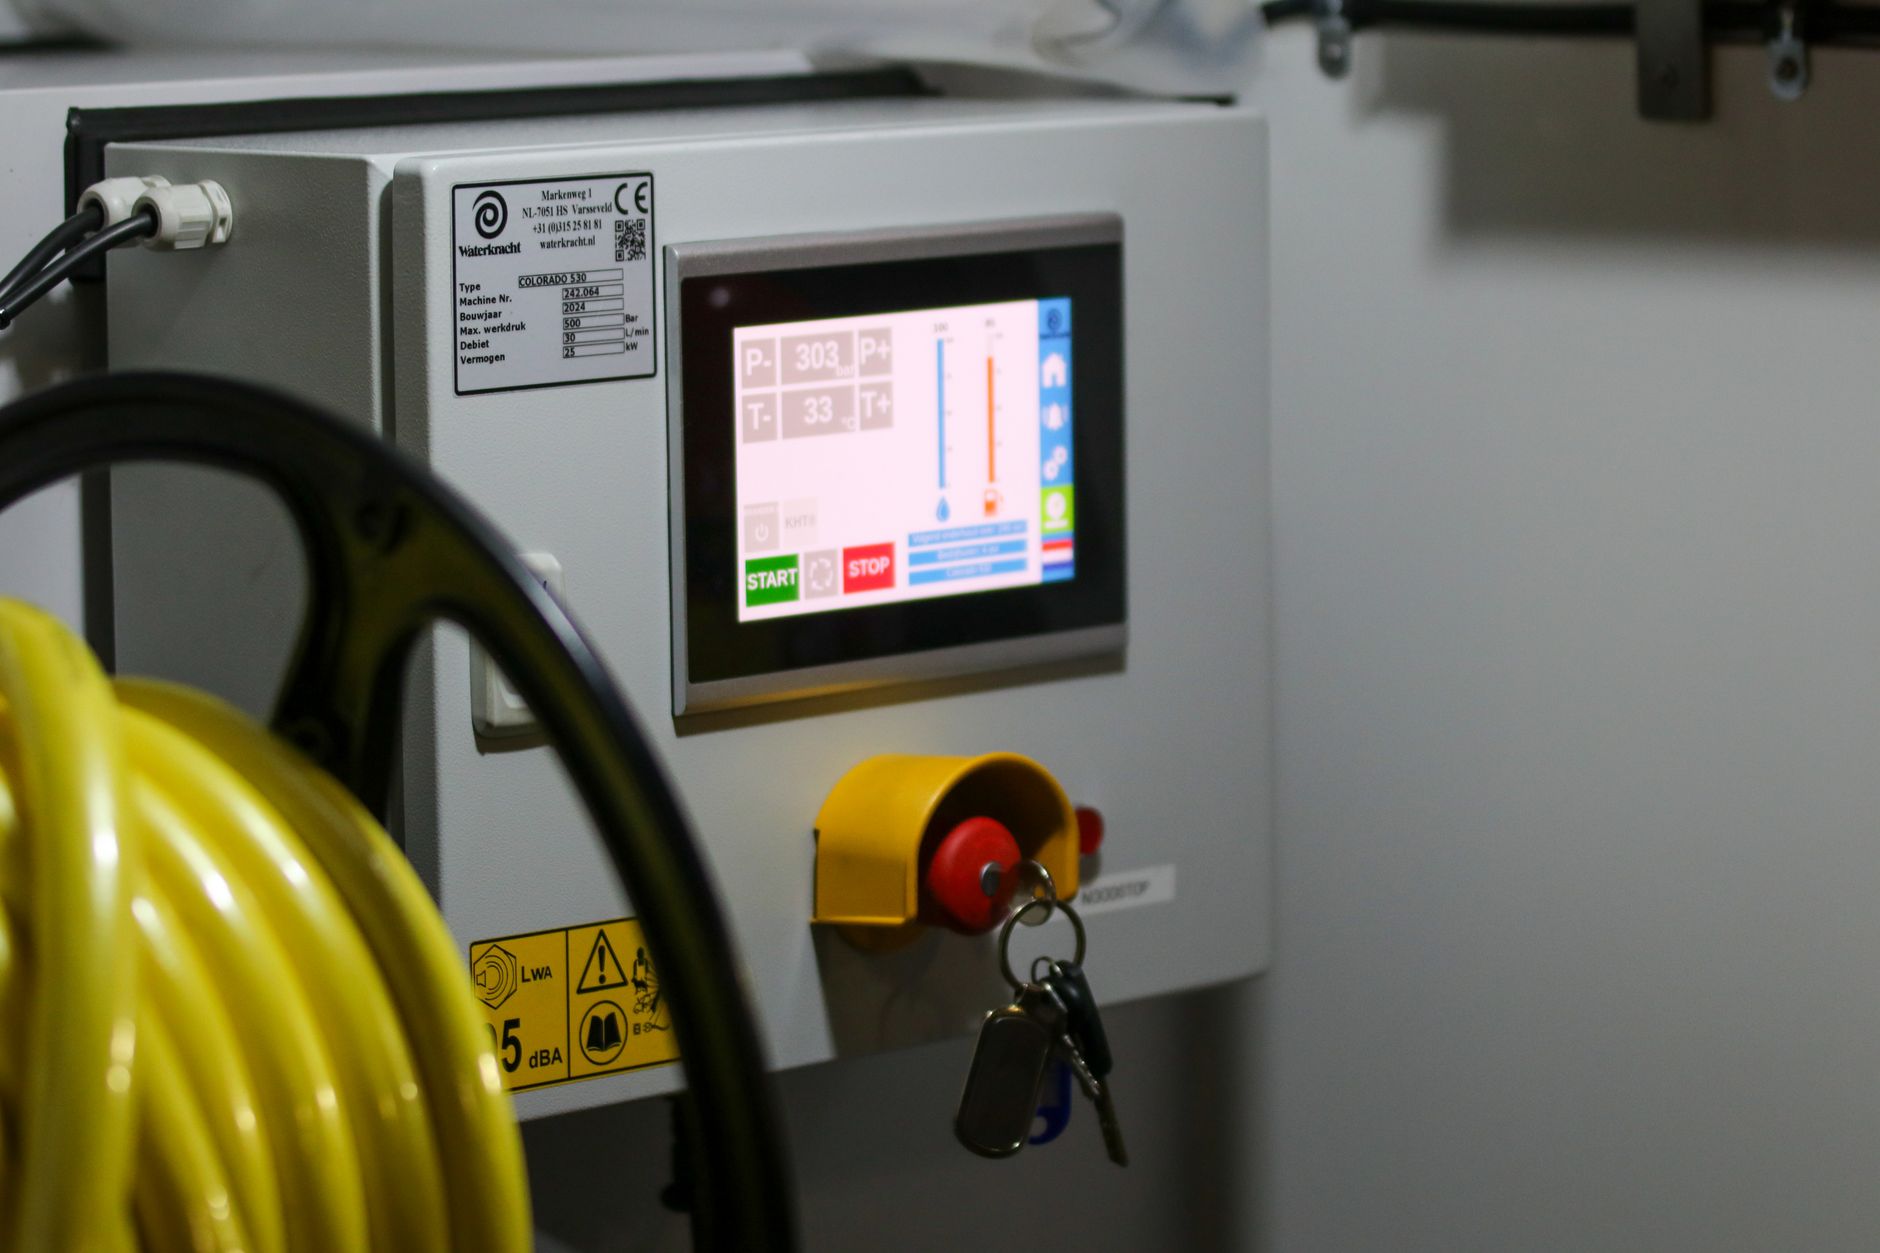
US agencies warn of AI-powered attacks on Siemens industrial controllers
US federal agencies, including the NSA and CISA, have issued a warning about threat actors using AI to develop exploit scripts targeting Siemens S7 Series programmable logic controllers (PLCs). These controllers are critical for infrastructure sectors like energy and water. The attackers leverage open-source libraries and AI to gain unauthorized access, mimicking legitimate monitoring tools to gather information and prepare for potential disruptions.
U.S. CISA adds an MLflow flaw to its Known Exploited Vulnerabilities catalog
CISA has added a critical server-side request forgery (SSRF) vulnerability in MLflow to its Known Exploited Vulnerabilities catalog. Tracked as CVE-2026-64849 with a CVSS score of 9.3, the flaw allows unauthenticated attackers to make requests from exposed MLflow servers to internal services, potentially stealing cloud credentials. Exploitation has been observed in the wild, with active scanning for vulnerable instances occurring shortly after the CVE was assigned.
US Indicts 17 Iranians Over Years-Long Cyber Espionage Campaign
The US charged 17 Iranians over a years-long hacking campaign that stole 31TB from universities, companies and government agencies worldwide. Eight years after the original indictment first went public, US prosecutors just added eight more names to the list. The Justice Department unsealed a superseding indictment this week charging 17 members of the Mabna Institute, […]
Exploitation Expected for Critical Authentication Bypass Patched in Citrix NetScaler
Remote, unauthenticated attackers could exploit the critical-severity flaw without user interaction. The post Exploitation Expected for Critical Authentication Bypass Patched in Citrix NetScaler appeared first on SecurityWeek.
Critical GitLab Flaw Exploited Shortly After Disclosure
CVE-2026-19478 can be exploited without authentication to modify or delete public projects and user data. The post Critical GitLab Flaw Exploited Shortly After Disclosure appeared first on SecurityWeek.
Tufin expands Unified Control Plane with AI intelligence and multi-vendor automation
Tufin has announced the availability of Tufin Orchestration Suite (TOS) 5.3, helping enterprises further simplify security operations and maintain consistent control across increasingly complex multi-vendor, hybrid environments. As enterprise security environments continue to expand across cloud, firewalls, SASE, SD-WAN, microsegmentation, and distributed infrastructure, organizations increasingly
US charges 17 Iranian hackers over 31-terabyte academic data theft
The U.S. has charged 17 alleged members of Mabna Institute, an Iranian hacking-for-hire company accused of running a years-long campaign that stole data from American universities, companies, and government agencies. The post US charges 17 Iranian hackers over 31-terabyte academic data theft appeared first on Help Net Security.
StopAndProtect Turns 2,000 Hacked WordPress Sites Into a Criminal Network
StopAndProtect turned nearly 2,000 hacked WordPress sites into a criminal network for malware delivery, data theft, surveillance and ransomware. Check Point Research uncovered a cybercrime operation, dubbed StopAndProtect, that has turned thousands of hacked WordPress websites into a shared platform for malware delivery, data theft, surveillance and ransomware. The operation is a good reminder tha
AI agent suggested installing a malware package. Engineer almost took its advice
Fortunately, the company had a policy of checking source code on GitHub first
Microsoft says August Windows updates may cause gaming issues
Microsoft is investigating a potential issue with the August 2026 updates that may prevent some games from launching or cause them to crash on affected Windows 11 systems. [...]
Elementor Pro Flaw Could Let Unauthenticated Attackers Upload PHP and Execute Code
Cybersecurity researchers have disclosed details of a critical flaw in the Elementor Pro WordPress plugin that, if successfully exploited, could lead to remote code execution. The vulnerability, tracked as CVE-2026-32475, carries a CVSS score of 9.0 out of 10.0. It has been described as a case of unrestricted upload of a file with a dangerous type. "The flaw lives in the Forms module's File
AI is making fraud harder to spot and identity harder to prove
Online fraud has become a routine concern for consumers and businesses that rely on digital accounts, payments and customer service. Experian’s 2026 U.S. Identity & Fraud Report describes a market where scams extend across messages, websites, documents, voices, images and account activity. Security measures that make consumers feel most secure (Source: Experian) Deception spreads across digital ch
Researchers find a loophole that lets expired credit cards make unauthorized payments
A team from the University of Massachusetts Amherst has shown that a contactless credit card keeps working past its printed expiration date, even after the cardholder gets a replacement. They named it the Zombie Card attack and presented the findings at USENIX Security 2026. The question behind the loophole “This work is motivated by documented patterns of improper expired card handling. Although
8,539 reasons to rethink how vulnerabilities get patched
The window for responding to newly disclosed security flaws is getting shorter. Exploit code can appear quickly, exploitability can be tested soon after disclosure, and organizations have a growing number of weaknesses to sort through. Rapid7’s Q2 2026 Threat Landscape Report counted 8,539 high- and critical-severity vulnerability disclosures, twice the number recorded a year earlier. Source: Rapi