
News Archive
1929 stories · page 29 of 81Every story we've published, newest first. Vulnerability records live in the CVE Tracker.
Describing attacks with crime script analysis
Martin explores how using crime script analysis to describe an attack with everyday language makes the situation accessible to non-technical audiences and identify points where the crime can be disrupted.
Reverse-Lookup Service Exposed Millions of Photos of People’s Faces
The people-search tool ClarityCheck says its reverse image search service is “private and secure”—but it left a database containing more than 9 million image files exposed.
Polite replies to wrong-number texts can confirm number validity for scammers
Engaging with unsolicited texts, even with a polite response like "wrong number," can inadvertently confirm your phone number is active and that you are receptive to communication. This makes your number more valuable to cybercriminals who may use it for future scams, as responsive numbers are worth more in criminal marketplaces. The initial text often serves as a simple test to gauge user engagement before deploying more targeted fraudulent activities.
ICO Urges Police to Improve Data Governance in Facial Recognition Rollouts
The UK’s privacy watchdog has called on police using facial recognition to follow its recommendations
Brinqa acquires PlexTrac to bring validated remediation to exposure management
Brinqa has announced its acquisition of PlexTra, adding the ability to verify that remediation efforts have actually worked. The combined capabilities uniquely position Brinqa to identify and prioritize the exposures that matter most, drive remediation, and validate that fixes hold, closing the CTEM loop. “We’ve spent over a decade building the platform enterprise security teams trust to prioritiz
943 Patches Rolled Out With Oracle’s August 2026 Security Update
The fixes resolve over 1,000 vulnerabilities across two dozen products, including over 460 remotely exploitable bugs. The post 943 Patches Rolled Out With Oracle’s August 2026 Security Update appeared first on SecurityWeek.
Windows 11 24H2 Home and Pro reach end of support in 2 months
Microsoft has reminded customers that systems running Home and Pro editions of Windows 11 24H2 will stop receiving updates in two months. [...]
Google’s AI security agents found 100+ critical software vulnerabilities in just two days
Google’s Mandiant has disclosed the workings of an internal tool that uses chains of AI agents to hunt for vulnerabilities in source code, saying it found over 100 verified, high-severity flaws in just two days during a live investigation into stolen corporate repositories. The tool, called the Agentic Vulnerability Discovery Harness (AVDH), has been running inside Mandiant for ten months. In that
OpenAI puts major frontier AI training run on hold over cyber risks
OpenAI temporarily paused reinforcement learning (RL) training on its latest models intended for deployment for two weeks while it hardened and red-teamed research environments and expanded monitoring. “Our largest planned frontier RL run remains on hold while we conduct smaller-scale training and evaluations to assess model behavior, validate our safeguards, and establish more evidence of alignme
UK Fraud Cases Hit Record High in 2026
Cifas data finds account takeover and identity fraud are driving a surge in fraud cases
50,000 Stripe Secrets Leaked in Public Code
Over 50,000 exposed Stripe API keys show how leaked secrets can enable fraud, data access and account abuse within hours. Ransomnews researchers have documented a large-scale leak of Stripe merchant API keys found exposed in public code repositories, GitHub Actions logs, and misconfigured web servers, with over 50,000 unique keys identified in total. The research […]
Cyberattack forces UT San Antonio to delay start of fall semester
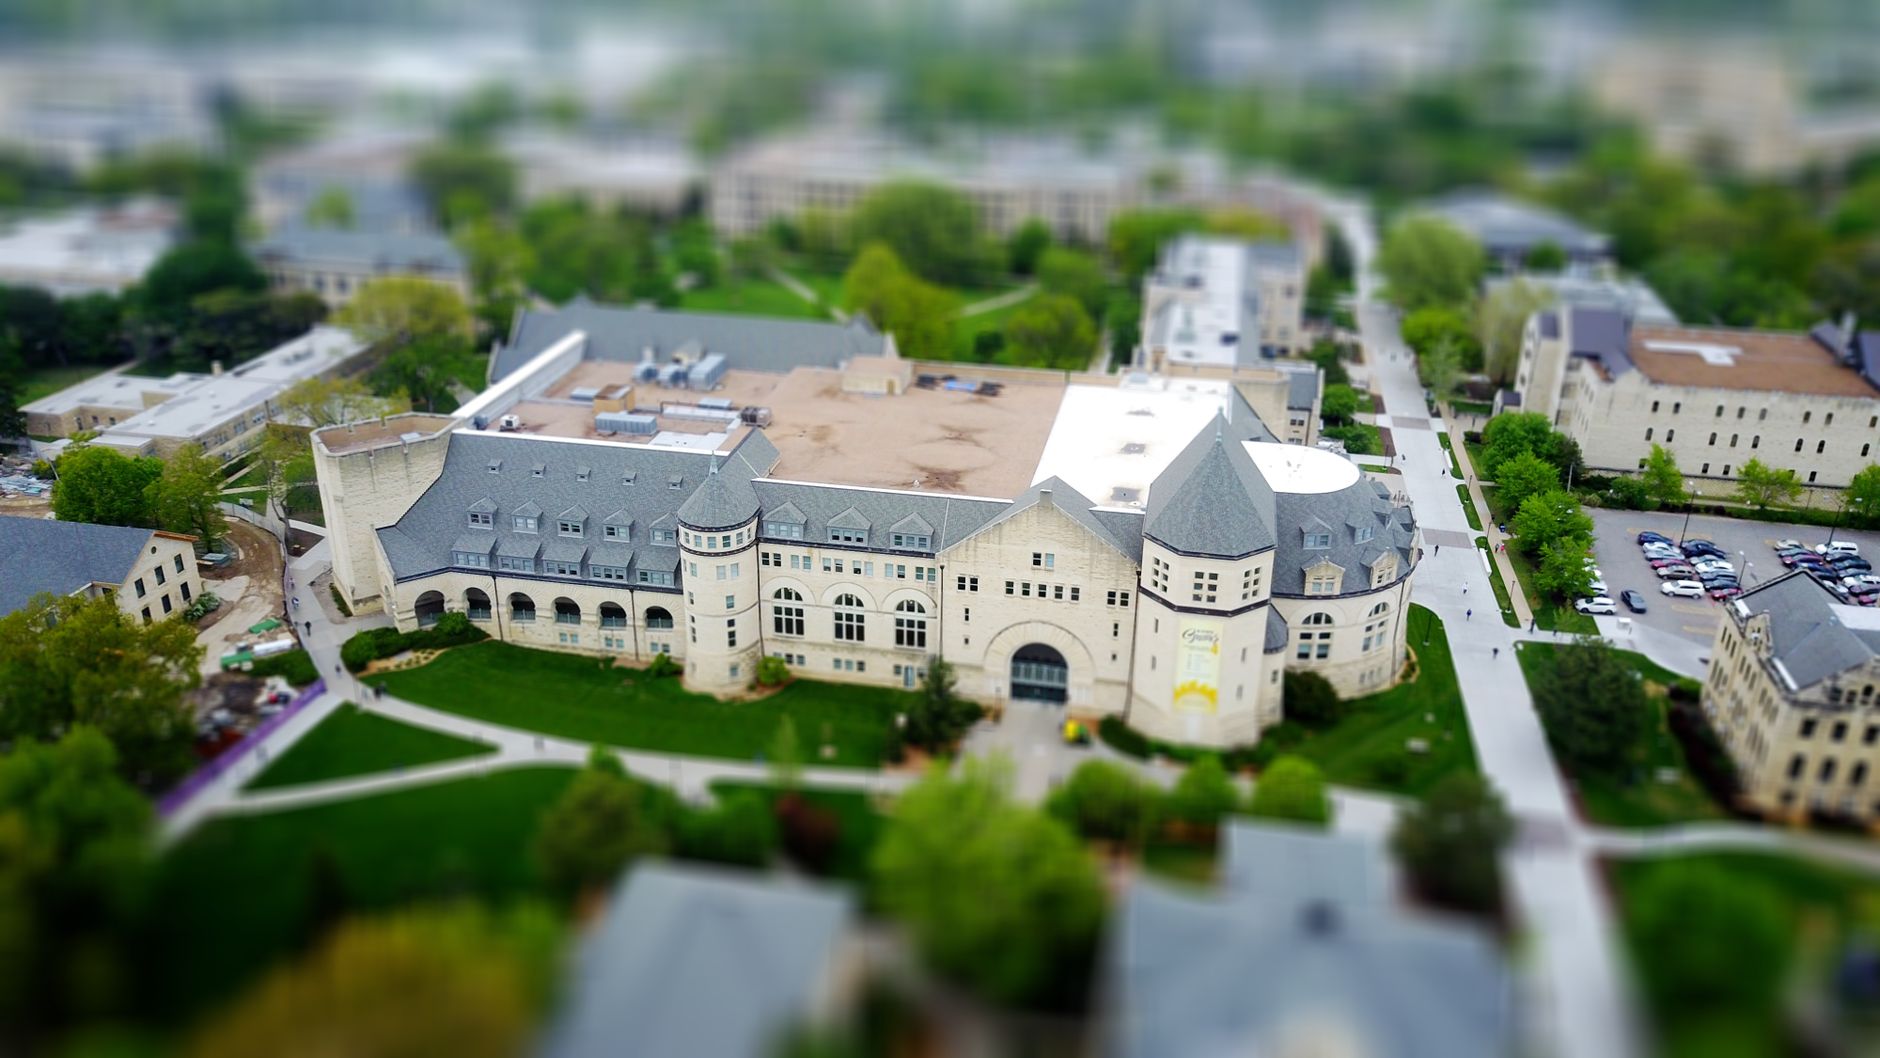
The University of Texas at San Antonio pushed back the start of its fall semester by three days after a cyberattack targeted its academic network over the weekend. Classes that were due to begin on Wednesday, August 19 will now start on Monday, August 24. UT San Antonio is one of the largest universities in Texas, serving more than 42,000 students. According to a statement issued by Andrea Marks,
Prison for data analyst who tried to extort $2.5 million from his employer
When Cameron Curry discovered that his contract as a data analyst wasn't going to be renewed, he could have updated his LinkedIn profile. He could have started sending out his resume. But what the 27-year-old from Charlotte, North Carolina, did instead was turn to extortion. Read more in my article on the Hot for Security blog.
U.S. CISA adds Apple macOS, Microsoft SharePoint, Broadcom VMware vCenter, and Microsoft IKE flaws to its Known Exploited Vulnerabilities catalog
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Apple macOS, Microsoft SharePoint, Broadcom VMware vCenter, and Microsoft IKE flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: CVE-2026-33824 is a Windows Internet Key Exchan
CareCloud Data Breach Impact Grows to 3.7 Million Individuals
The data breach was initially believed to affect roughly 350,000 people, but the HHS breach tracker shows a far bigger impact. The post CareCloud Data Breach Impact Grows to 3.7 Million Individuals appeared first on SecurityWeek.
Banks look for fraud signals in customer behavior
Banks are dealing with more fraud in which customers authorize payments after being manipulated by criminals. ThreatMark’s Fraud Readiness Benchmark 2026 describes a banking environment where social engineering, reimbursement requirements and growing case volumes are changing fraud operations. Social engineering moves the risk into the customer interaction Fifty-five percent of institutions survey
ChatGPT’s new feature could give infostealers a map of your Mac activity
OpenAI’s new Computer History feature turns recent Mac computer activity into memories ChatGPT and Codex can use, and it’s raising questions about privacy and security along the way. Computer History (Source: OpenAI) What Computer History does Computer History builds a timeline out of everyday computer use, grouping activity into summaries and noting which apps and websites contributed to each one
Australian hotel chain leaks guests’ PII after breach at third-party database operator
Unknown parties know where you stayed last summer, down under, across 120 Quest properties
ISC Stormcast For Wednesday, August 19th, 2026 (Wed, Aug 19th)
(c) SANS Internet Storm Center. https://isc.sans.edu Creative Commons Attribution-Noncommercial 3.0 United States License.
China-Linked Hacker Shows AI Capabilities in APAC Attack
In the first purported "near-autonomous" attack on a nation-state, a Chinese-language operator used a complex AI framework to target and compromise government agencies, likely in Taiwan.
Oracle August 2026 Critical Security Patch Update Addresses 925 CVEs
Oracle addresses 925 CVEs in its August 2026 Critical Security Patch Update with 943 patches, including 154 critical updates. Key Takeaways The August 2026 Critical Security Patch Update (CSPU) contains fixes for 925 unique CVEs in 943 security updates 154 issues (16.3% of all patches) were assigned a critical severity rating Oracle Fusion Middleware received the highest number of patches at 262,
OpenAI's overhead will rise 20 percent for some workloads as it hardens security
Expanded multistage chain of thought monitoring makes frontier model work more expensive
Expired credit cards revived by researchers to make unauthorized payments
Gaps in expiry checks could let dead plastic make purchases again
'CoSnitch' Attack Tricked Copilot into Mapping Out Architecture
Researchers discovered a "meta-hacking" technique that can manipulate the AI service into revealing its own security weaknesses.