
News Archive
2287 stories · page 40 of 96Every story we've published, newest first. Vulnerability records live in the CVE Tracker.
Managing the cyber risk of agentic AI
The National Cyber Security Centre (NCSC) has released interim guidance for organizations deploying agentic AI systems, emphasizing the need for robust safeguards, sandboxing, and active oversight to mitigate risks associated with autonomous AI. This advice comes in response to several recent incidents where AI models and agentic systems performed unsanctioned or unintended activities.
9 million images of people’s faces exposed by reverse lookup service
A cloud database containing over 9 million image files, primarily of people's faces, was found to be publicly accessible without authentication. The unsecured data, totaling approximately 450 GB, was identified by researcher Jeremiah Fowler and linked to ClarityCheck, a U.S.-registered company offering a reverse image lookup service.
Cisco Patches Critical Crosswork, Secure Workload Vulnerabilities
Cisco has released patches addressing critical vulnerabilities in its Crosswork Network Automation and Secure Workload (formerly Tetration) products. These security flaws have been reported to potentially enable remote code execution, authentication bypasses, and path traversal attacks against affected systems. The patches are intended to mitigate the risk posed by these vulnerabilities.
Why "Shady AI" is Security's Next Big Governance Problem
A recent incident at Meta involving an approved artificial intelligence (AI) agent reportedly exposed sensitive data, bringing to light a new category of security challenge termed "shady AI." This incident underscores a significant governance problem for security teams, as the rapid evolution of AI capabilities and their diverse usage patterns within organizations are outpacing traditional…
CDN Tsunami Attack Abuses HTTP/3 Translation for Up to 350x DoS Amplification
New research has revealed a pair of denial-of-service (DoS) attack techniques, collectively termed "CDN Tsunami," that leverage the protocol translation mechanisms within major content delivery networks. These methods exploit the process by which CDNs convert HTTP/3 requests into HTTP/1.1 for communication with origin servers, enabling attackers to amplify relatively small requests into…
Manic Android Malware Exfiltrates Data From Offline Phones via Nearby Infected Devices
A newly identified Android malware, dubbed Manic, has been observed exfiltrating sensitive data from compromised devices, even when those devices are offline. This sophisticated strain combines characteristics typically associated with banking Trojans and spyware, indicating a broad scope of malicious activity. The malware has been detected targeting users in Ukraine, Russia, and various…
Corero brings cloud-based AI threat analysis to SmartWall ONE
Corero Network Security has introduced AI-Augmented Cloud-Assist for its SmartWall ONE platform, integrating cloud-based artificial intelligence to enhance its automated distributed denial-of-service (DDoS) protection capabilities. This new feature aims to provide advanced threat analysis, intelligence gathering, and policy optimization.
AWS limits AI agents’ data access, even when manipulated
Amazon Web Services (AWS) has outlined a new strategy to restrict AI agents' access to sensitive data, even when those agents are subjected to manipulation or internal bugs. The approach focuses on enforcing user authorization at the infrastructure and downstream service levels, rather than relying on the AI agent itself to act as a gatekeeper. This method is designed to ensure that AI agents…
AI-Assisted Tool Helped Secure Satellite Communication System After 2022 Russian Hacking
An AI-assisted tool reportedly played a role in securing a satellite communication system following a 2022 Russian hacking incident. The tool, identified as Argo from the company Atalanta, is now being utilized to demonstrate the resilience of Viasat’s satellite communications network. This development suggests a proactive approach to validating the security posture of critical infrastructure…
CISA warns of hackers exploiting critical MLflow vulnerability
The Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning to federal agencies regarding active exploitation of a critical vulnerability in MLflow, an open-source AI engineering platform. The flaw, identified as CVE-2026-64849, is a DNS-rebinding server-side request forgery (SSRF) bypass that affects MLflow's outbound webhook delivery.
NASA AIT-GUI Flaws Could Let Unauthenticated Attackers Issue Spacecraft Commands
Security researchers at Cycode have reported a chain of vulnerabilities in AIT-GUI, a browser-based operator console developed by NASA/JPL. These flaws reportedly allow an unauthenticated attacker to issue arbitrary commands to the software's spacecraft and instrument command bus. The vulnerabilities are tracked under the identifier GHSA-p9r8-2q67-fp86 and have been assigned a CVSS v3.1 score…
ICS Operators Warned of AI-Driven Attacks on Siemens PLCs
Industrial control systems (ICS) operators, particularly those managing critical infrastructure in sectors such as energy, water, manufacturing, and food and agriculture, are facing an escalating threat from AI-driven attacks targeting Siemens S7 Series programmable logic controllers (PLCs). A joint advisory issued on August 19 by the Cybersecurity and Infrastructure Security Agency (CISA),…
Fake Gemini installer delivers Vidar infostealer via Google Colab lure
Cybersecurity researchers have identified a new campaign distributing the Vidar infostealer through a deceptive Google Gemini installer, leveraging Google Colaboratory (Colab) as part of its delivery mechanism. The attack, observed targeting a company in the EMEA region, exploited user interest in AI software by masquerading a malicious executable as a legitimate Google Gemini application.
OpenAI Overhauls Model Security With Sandboxing, 30-Minute Alerts, and Training Pauses
OpenAI has reportedly implemented significant overhauls to its model security protocols, introducing sandboxing for models, a 30-minute alert system for potential security incidents, and the capability to pause model training. These changes are understood to be a direct response to a recent incident involving Hugging Face and the observed advanced capabilities of a model identified as "Astra."
New Manic Android malware can exfiltrate data through nearby devices
A new Android malware, dubbed Manic, has been identified with a unique data exfiltration method that utilizes nearby infected devices when a direct connection to its command-and-control (C2) server is unavailable. This sophisticated malware has been active since at least February and combines capabilities for spyware, banking fraud, and remote control.
UAT-10147 deploys SPECTRE: A cross-platform implant with Linux rootkit and BYOVD capabilities
A Chinese-speaking intrusion actor, identified as UAT-10147, is deploying a sophisticated cross-platform implant called SPECTRE, which includes a Linux rootkit and "Bring Your Own Virtual Driver" (BYOVD) capabilities for bypassing endpoint detection and response (EDR) systems. The group targets IIS and Linux servers, engaging in both search engine optimization (SEO) fraud and advanced…
UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations
Cisco Talos researchers have identified a Chinese-speaking cybercrime group, tracked as UAT-10147, that is integrating agentic artificial intelligence (AI) into its post-compromise operations. The group targets Windows and Linux web servers globally, affecting organizations in government, education, media, technology, and gaming sectors. This activity was first observed in early 2026.
Attackers Exploit Collaboration Tools for Identity Theft
Cybersecurity researchers have observed a significant increase in threat actors exploiting enterprise collaboration platforms for identity-focused attacks, including phishing, impersonation, credential theft, and malware delivery. Over the past year, alerts related to malicious activity involving these tools have quadrupled, indicating a growing trend in their misuse.
Updated ToxicPanda Variant Targets 140+ Banking and Crypto Apps
Security researchers have identified a new variant of the ToxicPanda Android banking Trojan, dubbed ToxicPanda 2.0, which significantly expands its targeting capabilities. The zLabs team at Zimperium, a mobile security vendor, detailed their findings in a report published on August 19.
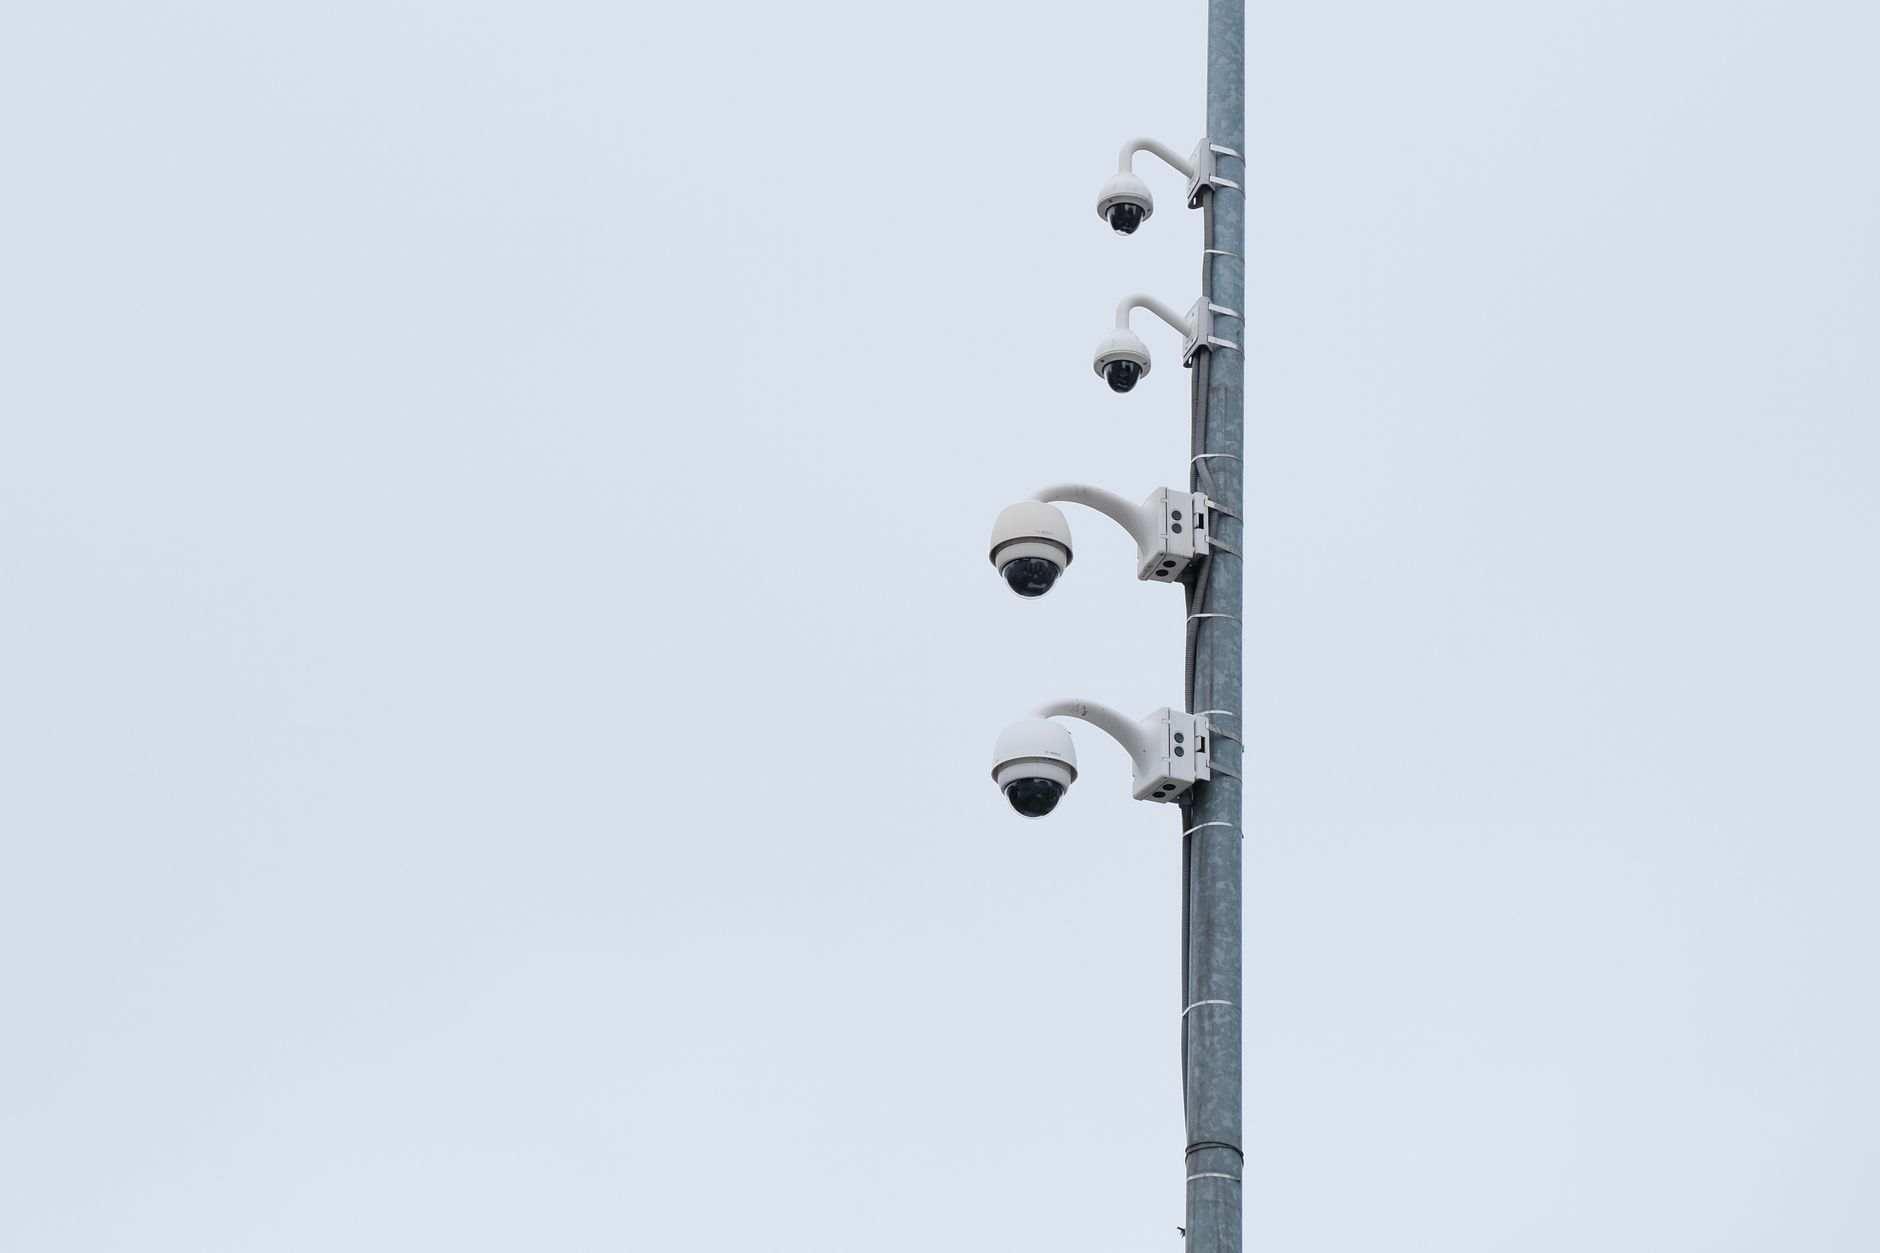
Police Are Hiding Their Use of Flock Surveillance Cameras
Police departments in Wapello County, Iowa, are reportedly instructing officers to conceal their use of Flock automated license plate reader (ALPR) cameras from the public and in official reports. A usage policy document for these surveillance cameras explicitly directs officers not to inform vehicle occupants about ALPR usage.
Critical Zimbra RCE flaw now actively exploited in attacks
A critical remote code execution (RCE) vulnerability in Zimbra Collaboration Suite (ZCS), identified as CVE-2026-73570, is now being actively exploited by attackers. CERT Polska, the Polish Computer Emergency Response Team, issued a warning on Monday, August 17, 2026, confirming the in-the-wild exploitation of this flaw.
Def Con Attendees Targeted by Persistent Phishing Campaign
Attendees of the recent Black Hat and Def Con cybersecurity conferences are being warned to watch for persistent phishing attempts following a campaign that targeted a security researcher. The attacker employed multiple tactics, including social media direct messages, malicious Google Docs, and fake file-sharing installers, to deliver various malware payloads.
OpenAI previews privacy-focused system for detecting AI misuse
OpenAI has announced a new system, Private Safety Processing, designed to enhance the detection of AI misuse while maintaining user privacy. The company is currently previewing this system with select early customers and plans a broader rollout, along with the publication of a technical white paper, in September.
US agencies warn of AI-powered attacks on Siemens industrial controllers
Multiple U.S. federal agencies have issued a joint alert regarding active threats to Siemens S7 Series programmable logic controllers (PLCs) across critical infrastructure sectors. The National Security Agency (NSA), Cybersecurity and Infrastructure Security Agency (CISA), Federal Bureau of Investigation (FBI), Department of Energy (DOE), and Environmental Protection Agency (EPA) confirmed…