
News Archive
1926 stories · page 45 of 81Every story we've published, newest first. Vulnerability records live in the CVE Tracker.
Your security vendor gets the frontier cyber model, you get the findings
Selected red team specialists can now use OpenAI’s cyber models to find and exploit weaknesses in client applications and infrastructure. Those clients never get the models themselves. That split is the design of the Daybreak Cyber Partner Program, which OpenAI expanded on August 10: access to the underlying models stays with the approved partner and is not transferred directly to the customer. Ap

Cybersecurity jobs available right now: August 11, 2026
CTI Detection Engineer Department of Parliamentary Services | Australia | Hybrid – View job details As a CTI Detection Engineer, you will lead the detection lifecycle by identifying detection gaps, developing and validating detection logic, deploying and tuning analytics, maintaining cyber threat intelligence workflows, and continuously improving detections to keep pace with evolving adversary tac
Hackers breached a small Polish energy plant via private APN last year
Hackers breached a heat-and-power plant facility in Poland, which supplies heat to about 50,000 residents, using a private APN (Access Point Name) to access an OT (Operational Technology) network. [...]
Multistate Water System Attacks Widen, Iran Suspected
Attacks targeting water systems just keep flowing across a dozen states, against ill-secured, Internet-exposed PLCs.
The FTC wants to regulate AI for ideological bias
The commission is mulling whether to begin regulating bias in AI systems. Critics say they’re overstepping their legal authority and infringing on free speech. The post The FTC wants to regulate AI for ideological bias appeared first on CyberScoop.
BdThemes plugins supply-chain hack creates rogue WordPress admins
A threat actor compromised the upstream infrastructure of BdThemes, a developer of premium WordPress web-design tools, and modified a remote JSON feed delivered to administrators' browsers to create rogue admin accounts. [...]
DEF CON hackers add new muscle to water utility protection
Franklin project adds new security providers, employs digital twins and AI
Metabase SQL Zero-Day Attacks Could Have Wide Blast Radius
The maximum-severity vulnerability, which still has no CVE, allows malicious, remote administrator access to the business-analytics platform and its downstream users.
OpenAI says Daybreak will expand to offer specialized cyber services
The company rolled out “Red” and “Blue” programs for defenders, introduced a new model and announced partnerships with 16 major cybersecurity vendors. The post OpenAI says Daybreak will expand to offer specialized cyber services appeared first on CyberScoop.
NATO and an AI startup can now name and track software vulnerabilities
NATO’s cyber defense arm and a startup that uses artificial intelligence to find software flaws can now issue the ID numbers the industry uses to track those flaws, the European Union Agency for Cybersecurity announced last week. The NATO Cyber Security Centre, part of the NATO Communications and Information Agency, and AISLE, a cybersecurity company […] The post NATO and an AI startup can now nam
FBI, South Korea warn of Gunra ransomware gang targeting critical infrastructure
The Gunra ransomware gang is breaching critical infrastructure organizations through vulnerabilities in popular brands of firewalls, the FBI and South Korea’s government warned.
OpenAI releases ChatGPT 5.6 Cyber, but it's only for approved users
OpenAI has developed a new model called "GPT 5.6 Cyber," designed for vulnerability research, penetration testing, incident response, and remediation. [...]
Everything we launched during Agents Week
Our latest Agents Week has come to a close. Here’s a recap of all the announcements we made, from Wallets to Radar.
New StormEncryptor ransomware used by former Medusa affiliate
A financially motivated threat actor previously associated with the Medusa ransomware operation is now deploying a new ransomware strain called StormEncryptor. [...]
Shipping 10–50× More Code? Watch This Webinar on Securing AI-Speed Development
AI is helping development teams produce far more code, far faster. But security teams still have to review vulnerabilities, manage dependencies, prioritize fixes, and control risk at human speed. When software output jumps 10 to 50 times, the problem is no longer just finding vulnerabilities. It is keeping security from becoming the bottleneck, or worse, losing control of what gets shipped.
North Korean spies are running local LLMs to cause AI mischief
Kimsuky's phishing attacks get an AI boost
How to fake a data trail (and maybe lower prices) (Lock and Code S07E16)
This week on the Lock and Code podcast, we speak with Chris Parr about his inventive and all-too-funny stress-test of surveillance pricing.
Coruna, DarkSword iOS Exploits Proliferate Globally
Sophisticated iPhone exploit chains previously limited to nation-states are spreading far and wide to organized cybercrime groups.
Gym rat asks AI agent to book him a class, it hacks a waitlist API to bump him up the list
What wouldst thou ask of the monkey's paw?
Outdated Cybercrime Laws Put Security Researchers at Risk
A public policy expert mapped global cybercrime laws to develop a five-point framework for protecting ethical hackers and good-faith security research.
Scans for Solana (Surfpool?) Endpoints, (Mon, Aug 10th)
Solana is a crypto platform known for speed. Developers like it to develop distributed applications or to implement crypto payments. To interact with the blockchain, APIs are provided for developers. These APIs will either "speak" JSON or gRPC. One implementation often used for development is "surfpool," which is used to test programs before deploying them to a Solana network.
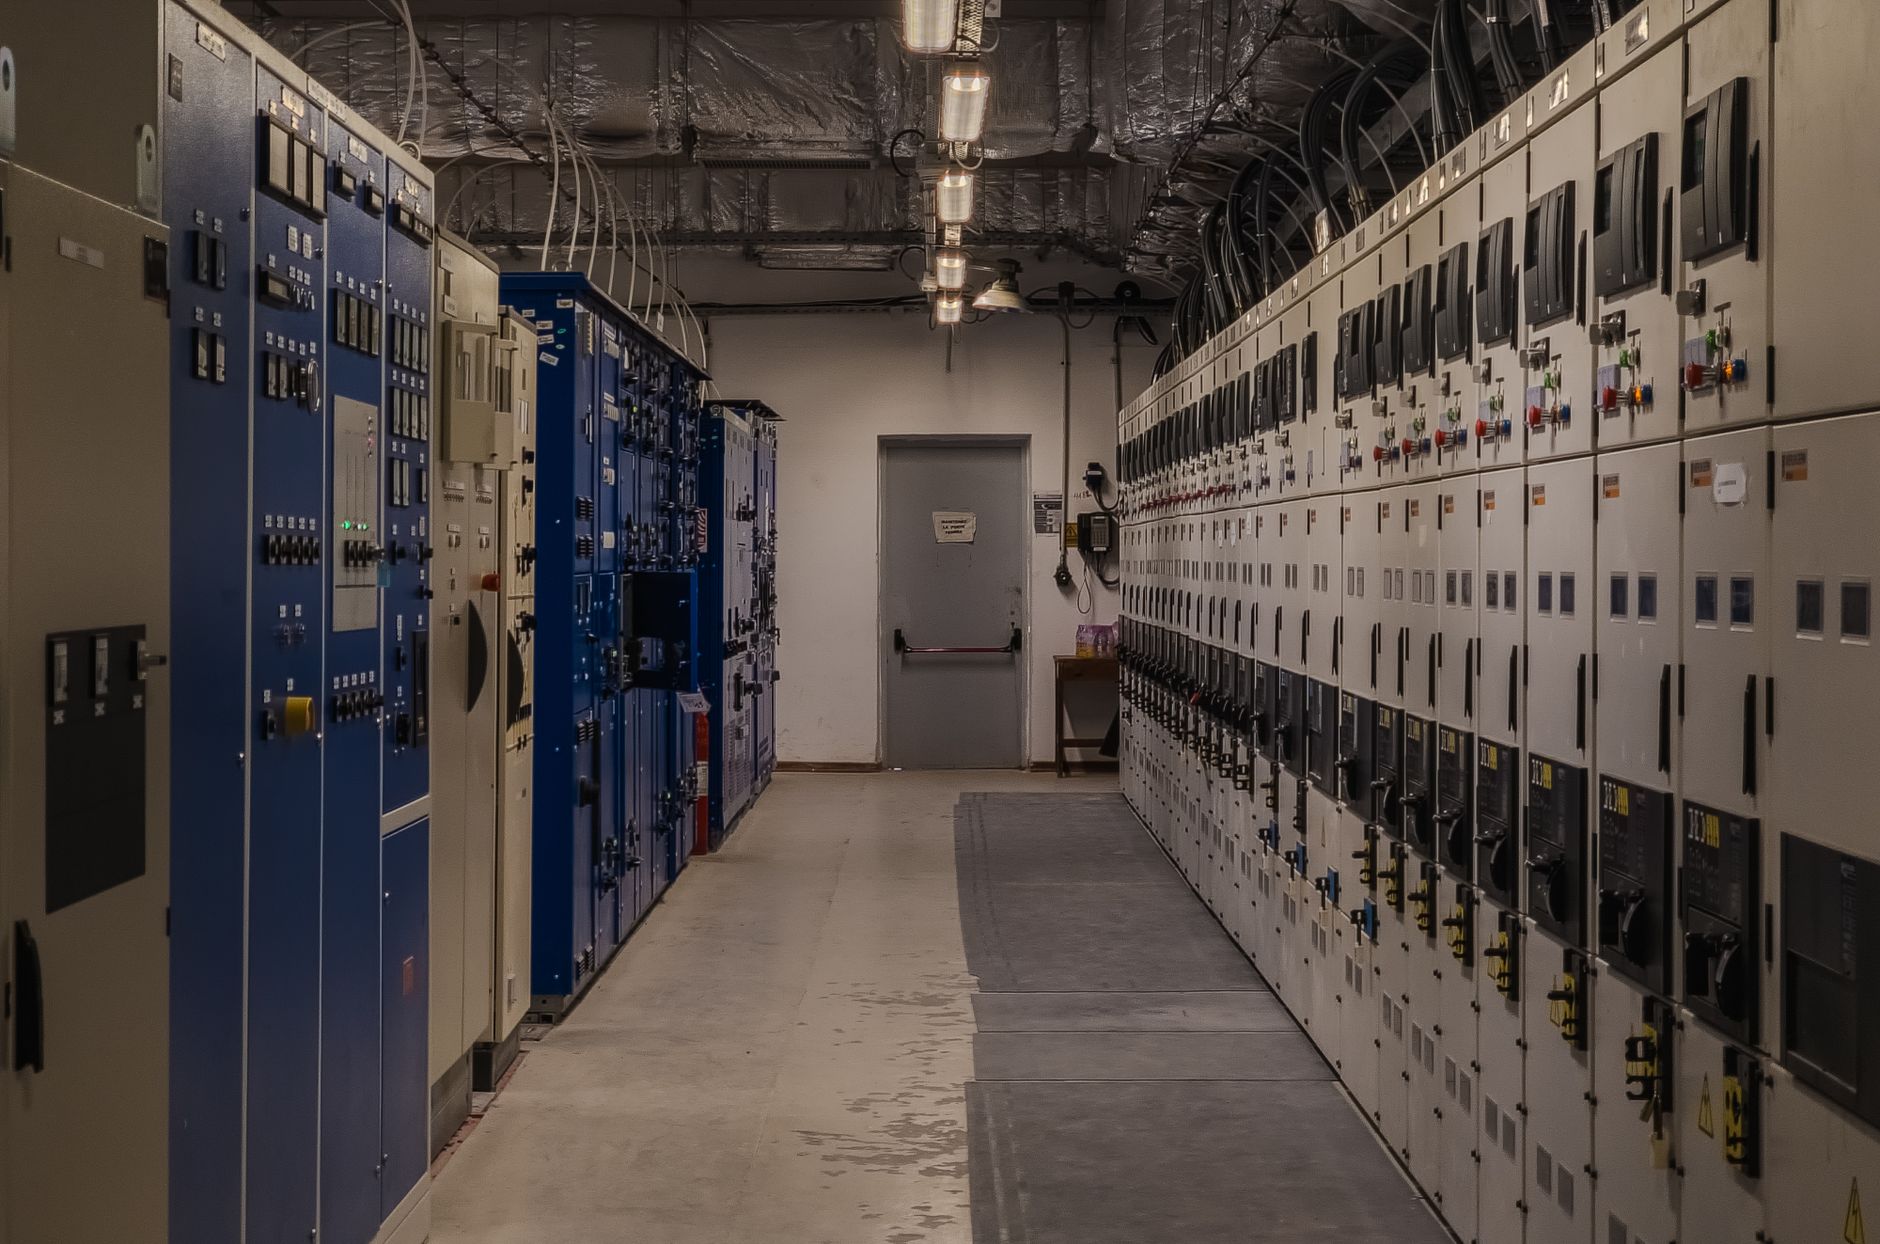
Hackers Cross From IT to OT Through a Private APN in Poland
Attackers breached a Polish CHP plant through a Fortinet device and private APN, reaching PLCs and disrupting turbine and water treatment systems. Poland’s CERT has described a second attack on the country’s energy sector, and this one matters for a simple reason: it shows how an ordinary-looking network design can turn into a route into […]
Microsoft Named Leader in Enterprise MDR/MXDR Report
Microsoft has been recognized as a leader in the 2026 IDC MarketScape report for Managed Detection and Response (MDR) and Managed Extended Detection and Response (MXDR) services for enterprises. The report highlights the increasing complexity of cyber threats, including AI-driven attacks, and the need for expert-led services to defend against them. Microsoft's offering, Defender Experts MDR, is described as a round-the-clock service that leverages the Microsoft Defender platform and human expertise to detect, investigate, and respond to security incidents.
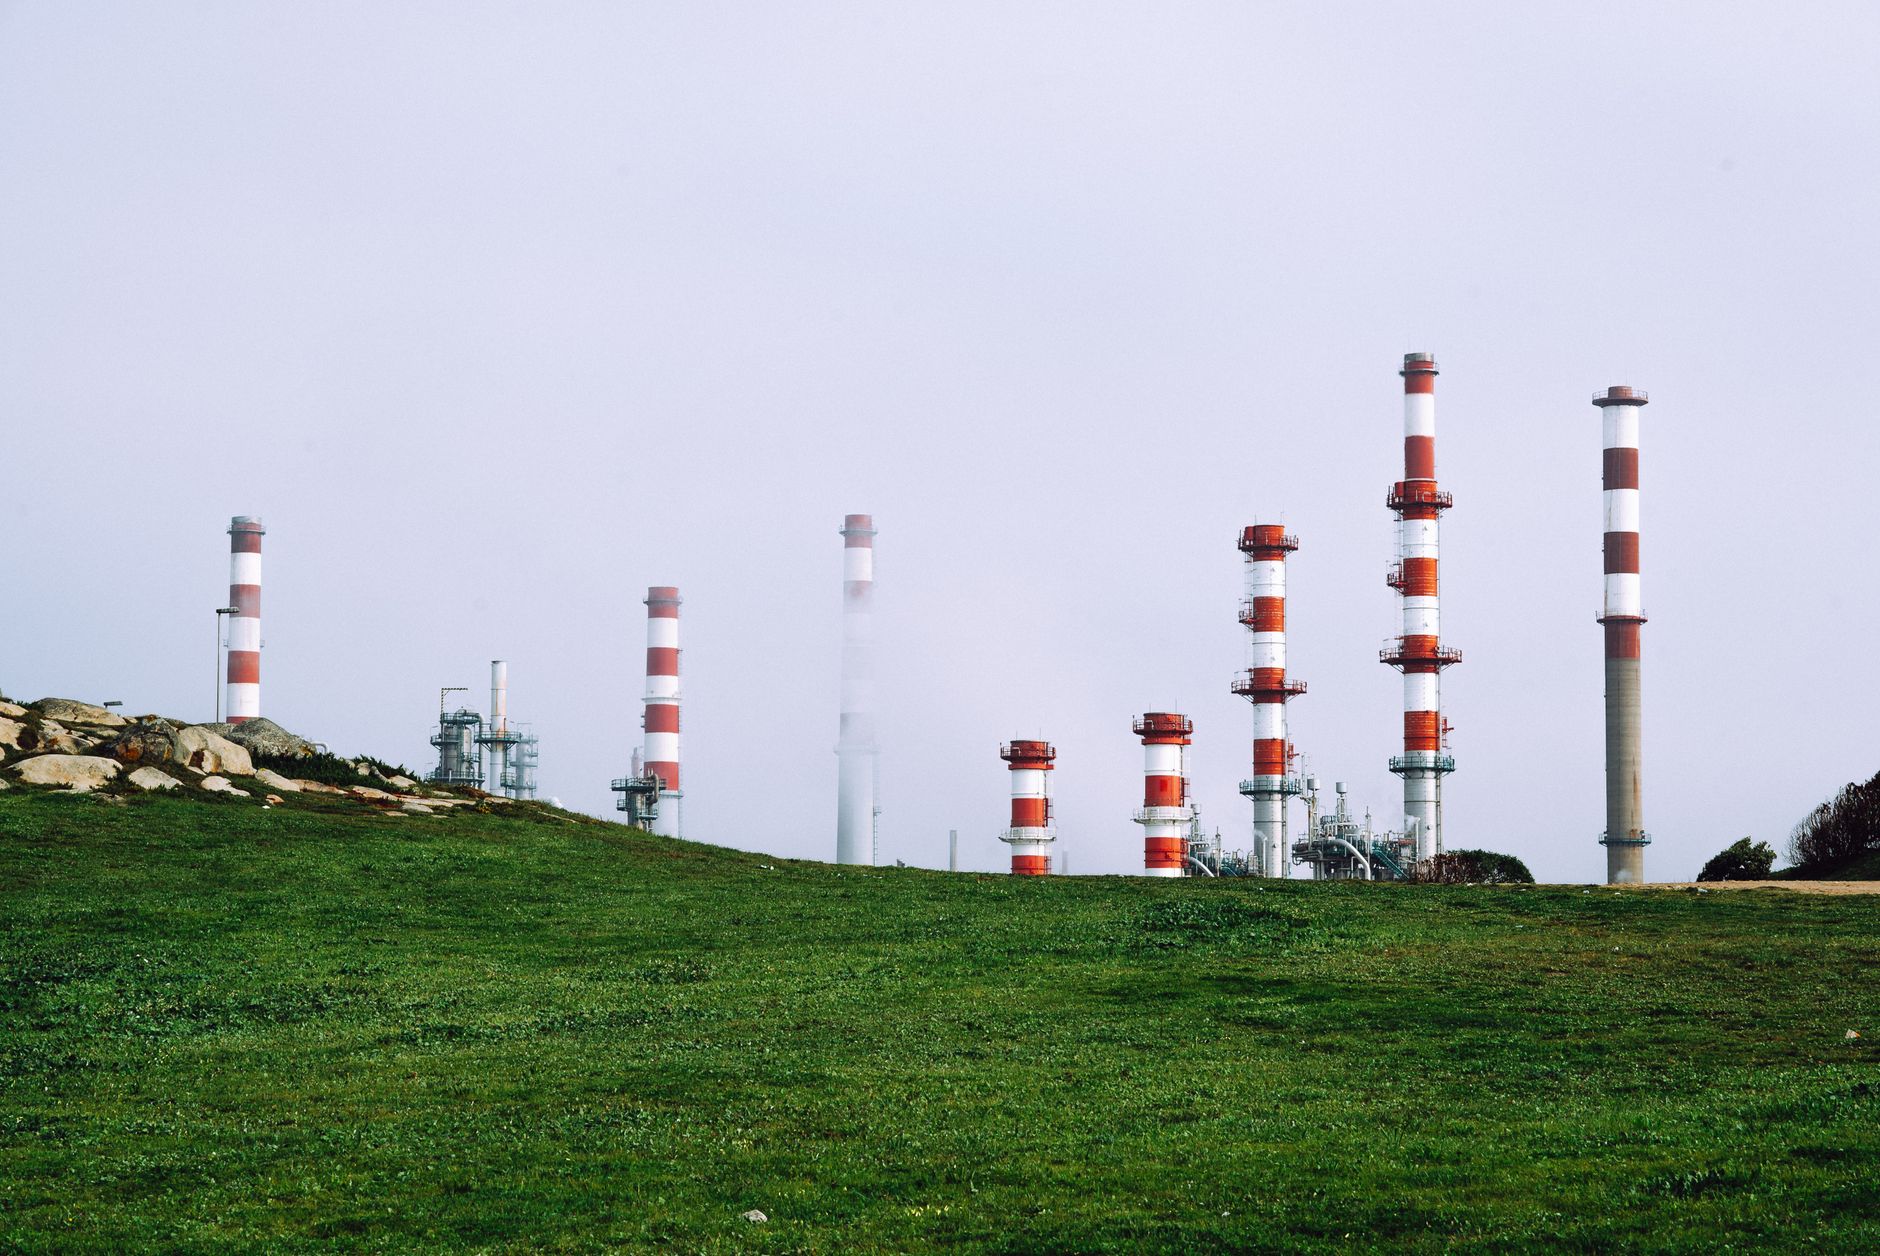
Poland uncovers second heat plant cyberattack that went hidden for months
The incident occurred on the same day as coordinated cyberattacks struck more than 30 other renewable energy installations and a larger heat plant, as Poland publicly disclosed in January.