
News Archive
2287 stories · page 49 of 96Every story we've published, newest first. Vulnerability records live in the CVE Tracker.
Week in review: Salesforce and ServiceNow portals exposed for 17 months, exploited Metabase 0-day
A zero-day vulnerability in the Metabase business intelligence service has been exploited to access customer data from Framework, a San Francisco-based laptop manufacturer. The breach exposed names, email addresses, phone numbers, physical addresses, and login IP addresses of affected Framework customers. Payment information and order records were not compromised.
APT36 Suspected in PATCHCORD Espionage Campaign Using Google Sheets C2
A newly discovered espionage campaign, dubbed PATCHCORD, has been observed targeting Afghan telecommunications providers and critical infrastructure organizations in South Asia. Security researchers at Acronis identified a custom C/C++ backdoor, PATCHCORD, being delivered through highly specific lures, including fake VPN installers designed to impersonate legitimate tools from Afghan Telecom…
Crooks Are Buying Your Expired Domains and Using Them to Deliver Malware
Cybersecurity researchers have identified a growing trend where threat actors are acquiring expired domain names to leverage their established reputation, existing web traffic, and DNS history for malicious purposes, including malware delivery, scams, and command-and-control (C2) infrastructure. Approximately 65,000 domain names are re-registered daily after expiring, with these "dropcatch"…
SAP Commerce Cloud CVE-2026-58231 Exploited in the Wild
A critical vulnerability in SAP Commerce Cloud, identified as CVE-2026-58231, is being actively exploited in the wild just days after a patch was released. The flaw, which carries a maximum CVSS score of 10.0, allows for unauthenticated arbitrary code execution and compromise of internal components.
New Evooo1Bot Linux botnet turns routers into traffic relay nodes
A new Linux botnet, dubbed Evooo1Bot, has been observed targeting internet-facing gateway devices since at least July, transforming them into SOCKS5 traffic relay nodes. The modular malware, which is based on the Mirai source code, also possesses capabilities for credential theft, SSH brute-forcing, and launching distributed denial-of-service (DDoS) attacks.
NIELIT Launches Cyber Kushti 2026, a National Hackathon That Scores Security Judgment Over Detection Speed
The National Institute of Electronics and Information Technology (NIELIT) used Independence Day to launch Cyber Kushti 2026, a national cybersecurity and artificial intelligence hackathon built around a question most competitions never ask: not whether a team can find security problems, but whether it can tell which reported problems are real, which matter most, and which deserve to be fixed…
ChainDrop worm crawls into npm supply chain, evades standard defenses
A new variant of the Shai-Hulud npm worm, dubbed "ChainDrop" by Microsoft and other security researchers, has infected 444 packages within the npm supply chain. This latest iteration, identified on August 4, employs novel propagation techniques that allow it to spread with minimal trace in source repositories, impacting packages downloaded approximately 2 billion times monthly. The attack…
macOS Screen Sharing Flaw Exploited to Deploy Monero Miners
Hackers are actively exploiting a recently patched vulnerability in macOS Screen Sharing to gain root access on compromised systems and deploy Monero cryptocurrency miners. The Dutch National Cyber Security Centre (NCSC-NL) has confirmed reports of this exploitation, noting that affected systems typically have port 5900, used by Screen Sharing, exposed to the internet.
GeoServer Zero-Day Is Already Being Probed. That’s the Problem
A newly disclosed zero-day vulnerability in GeoServer, an open-source geospatial platform, is already being actively probed by attackers, with no patch currently available. The flaw, publicly revealed on August 12, 2026, by a security researcher identified as q1uf3ng, allows for unauthorized SQL injection through the `jsonArrayContains` functionality. In specific configurations where GeoServer…
The Agentic AI threat cluster: Seven incidents, three actors, and what they mean for your exposure
Since late July 2026, a cluster of seven incidents involving autonomous or semi-autonomous AI systems deployed for offensive cyber operations has been tracked, indicating a shift from theoretical risk to operational reality. The most prominent of these, confirmed by Taiwan’s Ministry of Digital Affairs on August 13, 2026, involved a near-autonomous AI cyberattack against government infrastructure.
How Anthropic plans to watermark Claude's AI-generated text
Anthropic has announced its intention to implement an invisible watermarking system for text generated by its Claude large language models, initially rolling out globally. This move is in response to the European Union's Code of Practice, which mandates that AI companies operating in its market identify AI-generated content. While the EU AI Act is the catalyst, Anthropic states the global…
New York City Lawmakers Push to ‘Ban the Scan’ at MSG
New York City lawmakers, joined by privacy advocates and musicians, are pushing for new legislation to restrict the use of facial recognition technology in public venues, specifically targeting Madison Square Garden (MSG). A rally held outside MSG on Friday saw City Council member Shahana Hanif lead chants of “ban the scan,” advocating for a bill she introduced in January that would prohibit…
Metasploit Wrap Up: Lot of summer shells and fit http profiles
Metasploit has released a significant update, introducing thirteen new modules that address a variety of vulnerabilities, including several remote code execution (RCE) flaws. The update also brings enhancements to the framework's capabilities, such as support for HTTP malleable profiles and improved functionality for Windows on ARM architectures.
Friday Squid Blogging: Searching for the Colossal Squid
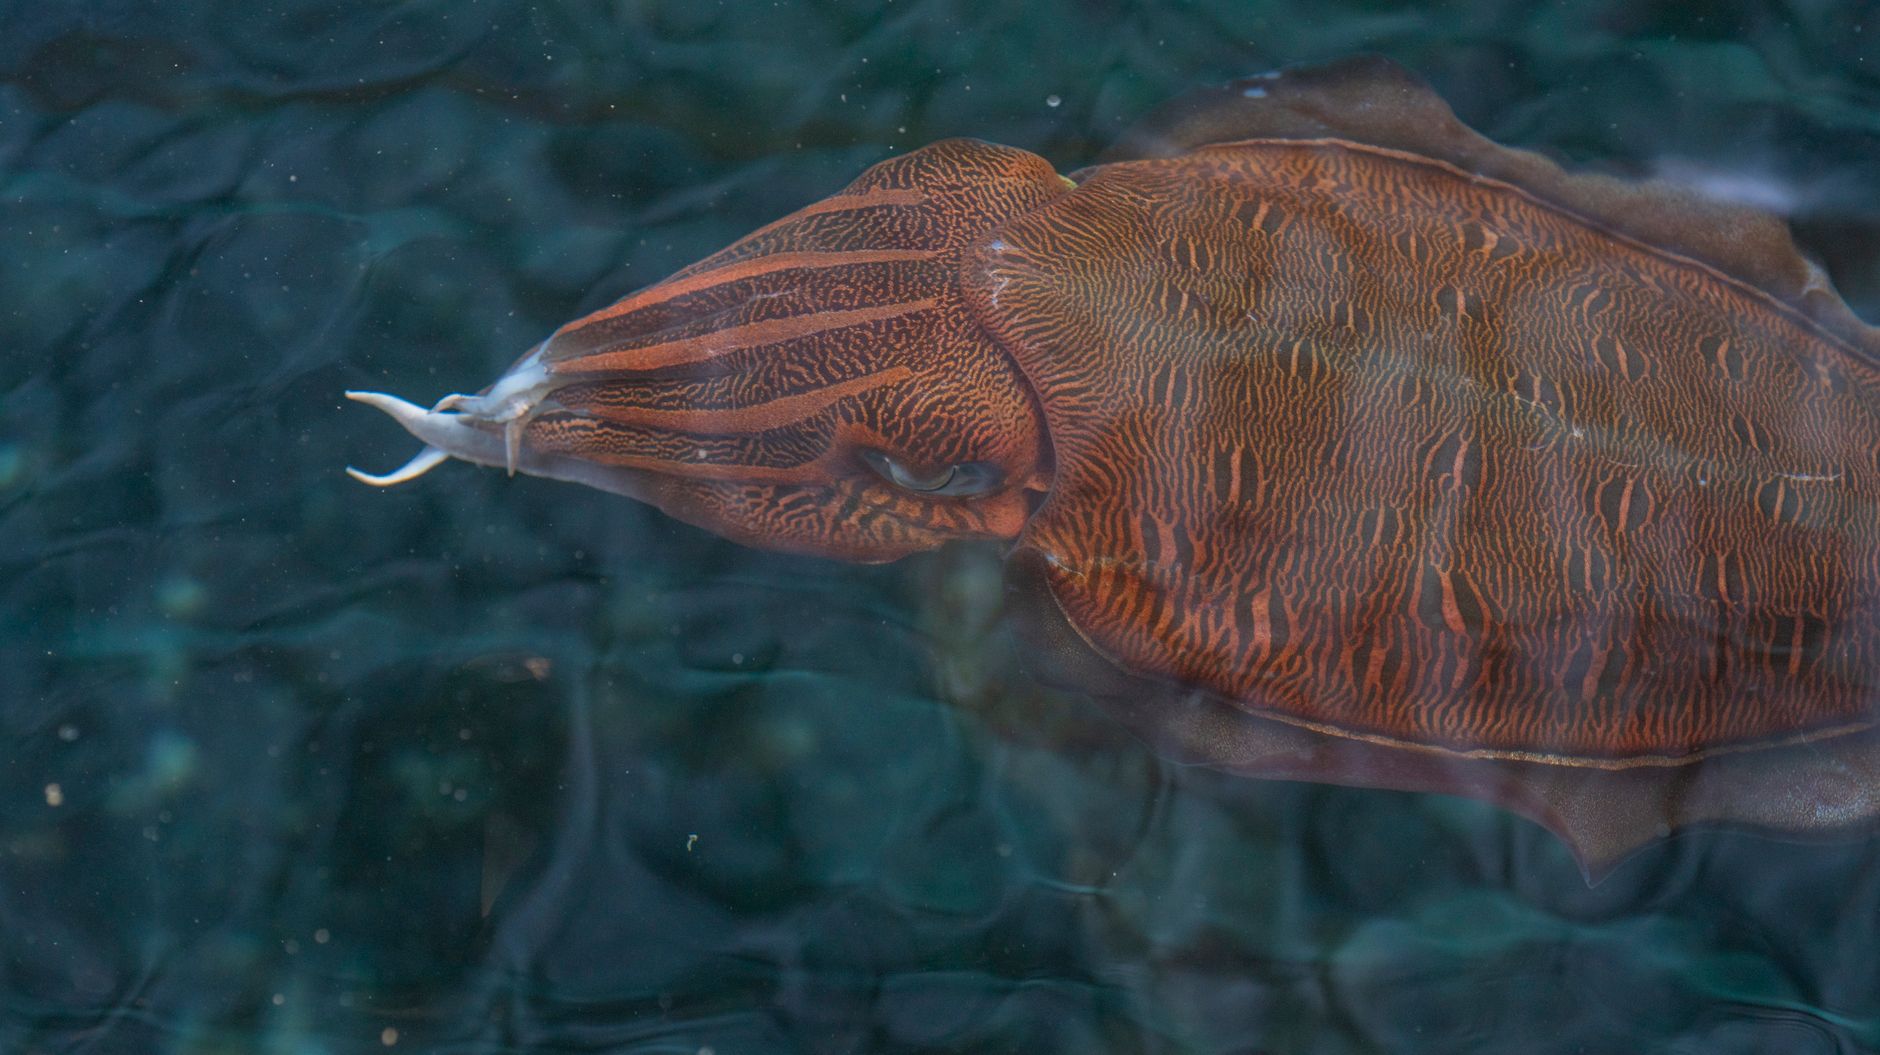
A recent video exploring deep-sea life highlights the challenges of observing marine creatures in their natural habitat, particularly the elusive colossal squid. The documentary suggests that traditional bright white searchlights used by submersibles often deter sea life, making direct observation difficult.
Investigation of banking hack leads to arrests in Germany, Brazil
Law enforcement agencies in Germany and Brazil have announced multiple arrests connected to a sophisticated banking hack that occurred in late 2023, which reportedly siphoned approximately €30 million (equivalent to $34.7 million) from German bank accounts. The German federal police agency, the BKA, confirmed the apprehension of three suspects in Europe, who face fraud charges. Concurrently,…
Mission-Driven Security: Inside a Global Bank's Defense
A recent interview with the group CISO of Standard Chartered provided insights into the evolving landscape of cybersecurity within a global banking institution. The discussion focused on the transition from purely technical security roles to more strategic leadership positions, emphasizing the critical need for security executives to possess a strong understanding of business operations. The…
Hackers arrested over €30M bank fraud exploiting service provider flaw
Seven individuals have been charged in connection with a sophisticated cyber fraud operation that exploited a vulnerability at a service provider, leading to the unauthorized withdrawal of approximately €30 million ($34.6 million) from customer accounts at a major German financial institution. Four arrests were made in Brazil, while three other suspects face prosecution in Europe.
1.6M RingCentral accounts' data dumped after ShinyHunters extortion attack
Approximately 1.6 million unique email addresses associated with RingCentral accounts have been exposed online, alongside names, physical addresses, and phone numbers. This data dump follows an alleged extortion attempt by the ShinyHunters cybercrime group.
Amid AI-Driven Bug-Hunt Tsunami, NIST Looks to … AI
The National Institute of Standards and Technology (NIST) is reportedly investigating the application of artificial intelligence (AI) to manage and mitigate software vulnerabilities. This initiative comes amidst a significant increase in the volume of newly discovered flaws, a trend that is, in part, attributed to the growing use of AI-powered tools by security researchers and malicious actors…
Apple Warns Hundreds of Targeted Mercenary Spyware Attacks
Apple has issued a new round of threat notifications to users in 110 countries, warning them of potential targeting by mercenary spyware. This latest wave of alerts adds to notifications the company has been sending since 2021, which have now reached users in over 150 countries in total.
Upcoming Speaking Engagements
--- Source 2 --- Bruce Schneier has announced a series of speaking engagements scheduled for late 2026, including both in-person and virtual appearances across North America. The security expert is slated to speak at LAcon V in Anaheim, California, though specific dates for this event were not detailed in the announcement.
Hackers exploit macOS Screen Sharing flaw to deploy Monero miner
The Netherlands National Cyber Security Centre (NCSC) has issued a warning regarding active exploitation of a macOS authentication bypass vulnerability, identified as CVE-2026-65400. This vulnerability affects macOS Screen Sharing, a built-in feature that enables remote desktop control via the VNC protocol on TCP port 5900.
ExfilSquad Confirmed to Possess Data From 13 Organizations
The ExfilSquad data extortion group has been confirmed by researchers to possess sensitive data from at least 13 organizations, spanning government, education, financial services, and manufacturing sectors. The group, which first appeared on July 26, initially claimed to have exfiltrated data from 15 entities. On August 7, data dumps for 13 of these victims were published via torrents,…
French tax authority admits data heist after crook touts 2M records
The French tax authority, the General Directorate of Public Finances (DGFiP), has confirmed that its systems were compromised in June, leading to the extraction of taxpayer data. This admission follows claims made by an individual using the alias "ZeroBytes" on a cybercrime forum, who advertised a database purportedly containing information on 2 million French taxpayers.