
News Archive
2287 stories · page 55 of 96Every story we've published, newest first. Vulnerability records live in the CVE Tracker.
ZDI-26-576: Linux Kernel XFRM Race Condition Local Privilege Escalation Vulnerability
A race condition vulnerability, identified as ZDI-26-576, has been reported in the Linux Kernel's XFRM (IPSec) subsystem. This flaw reportedly allows local attackers to escalate privileges on affected systems. The issue specifically involves improper locking mechanisms during operations on skb (socket buffer) objects within the XFRM component.
Cisco Identity Services Engine Leaks Information Due to Missing Authentication
Cisco has addressed a critical information disclosure vulnerability in its Identity Services Engine (ISE) that could allow unauthenticated remote attackers to access sensitive data, including stored credentials. The flaw, identified as CVE-2026-20190, stems from a missing authentication check in the handling of upgrade files.
Cisco Identity Services Engine Vulnerable to Command Injection
A critical command injection vulnerability has been reported in Cisco Identity Services Engine (ISE), potentially allowing remote attackers to execute arbitrary code. While the flaw is severe, successful exploitation requires prior authentication to the system. The vulnerability has been assigned a CVSS score of 7.2, indicating a high level of concern despite the authentication prerequisite.
DDoS attacks hit record scale as 1 Tbps+ campaigns become more common
Distributed denial-of-service (DDoS) attacks reached unprecedented scales in the first half of 2026, with campaigns generating traffic in excess of one terabit per second (Tbps) becoming increasingly common. Cloudflare's H1 2026 DDoS Threat Report indicates a rise in both the volume and sophistication of these attacks, characterized by larger traffic floods, shorter durations, and greater…
Product showcase: Is this image real? Slop or Not investigates
Slop or Not, a new AI text and image detection application for iPhone and Mac, operates entirely offline and does not require an account. The app leverages on-device AI models, powered by the Apple Neural Engine, to identify AI-generated content.
Wireshark 4.6.8 patches 28 security bugs, nine in file parsers
Wireshark version 4.6.8 has been released, addressing a total of 28 security vulnerabilities within the popular network protocol analyzer. Nine of these critical flaws are located in file parsers, meaning they can be triggered simply by opening a specially crafted capture file without any network interaction.
Chinese Loongson processors have leaky caches, researchers find
Researchers from Germany's Helmholtz Center for Information Security have identified a critical cache vulnerability, dubbed "LoongLeak," in processors manufactured by China's Loongson Technology. The flaw, which stems from the LoongArch instruction set architecture (ISA), allows attackers to extract sensitive data from the L1 data cache, even when operating from within unprivileged user space,…
ISC Stormcast For Thursday, August 13th, 2026 (Thu, Aug 13th)
The SANS Internet Storm Center's Stormcast for Thursday, August 13th, 2026, has been released. The Stormcast provides daily updates and analysis on current threats and vulnerabilities, serving as a resource for cybersecurity professionals to stay informed about the evolving threat landscape.
Using Gemma4 with Ollama - Testing File Hash Analysis and Recommendations with AI, (Wed, Aug 12th)
A recent report detailed an experiment using the Gemma4 large language model (LLM) with Ollama to analyze file hashes, specifically focusing on malware hashes collected by a DShield sensor. The objective was to assess the utility and quality of recommendations generated by the AI in understanding and responding to observed malicious activity. The testing period covered malware hashes uploaded…
Malware Crypting Services Aid Threat Actors in Evading Detection
Cybersecurity researchers have identified a growing market for "crypting" services, which enable threat actors to modify malicious payloads to evade detection by antivirus (AV) and endpoint detection and response (EDR) tools. These services are becoming increasingly sophisticated, offering a range of features beyond basic encryption to complicate analysis and preserve malware usability.
Smashing Security podcast #480: This is the AI service you should never sign up to
A new phishing-as-a-service (PaaS) platform named "Greatness" has emerged, offering a sophisticated attack vector that bypasses traditional password theft and fake website tactics. This platform leverages a legitimate Microsoft login page to gain full access to a victim's emails, files, and potentially their entire organizational infrastructure. The attack relies on a moment of misplaced trust…
"City-Forum" data-theft attacks target Salesforce, ServiceNow portals
An ongoing data theft campaign, dubbed "City-Forum" by the SaaS security firm Reco, is targeting data exposed to unauthenticated users through misconfigured Salesforce Experience Cloud and ServiceNow customer portals. The attacks, which are not exploiting vulnerabilities in either platform, have been traced to a single server and are reportedly increasing in volume.
Android malware combo takes out loans and relays victims' credit cards
A new Android malware combination, featuring the WindRelay NFC relay tool and the SpyNote remote administration tool (RAT), has been observed by cybersecurity firm Group-IB in attacks designed to steal credit card data and facilitate fraudulent loans. This sophisticated toolkit allows attackers to gain remote control over a victim's device and relay live NFC payment card exchanges, including…
'Near-autonomous' AI agents attack Taiwan's nuclear safety agency
Suspected Chinese cyber operatives reportedly utilized publicly available AI tools in a "near-autonomous attack" against Taiwanese government systems, subsequently expanding their operations to include the nation's nuclear safety agency, supply-chain vendors, and at least seven energy companies. The attack, which occurred over four days in early July, involved AI agents compromising 85…
Long-running Data Theft Campaign Targeting Salesforce, ServiceNow
A long-running data theft campaign, dubbed "City-Forum," has been reported to be actively targeting organizations utilizing Salesforce and ServiceNow platforms. The campaign has been observed since at least March 2025 and is characterized by its use of custom tooling to exfiltrate data.
Hackers exploit critical Adobe Commerce flaw to hijack customer accounts
Exploitation attempts have been detected for a critical vulnerability in Adobe Commerce and Magento e-commerce platforms, identified as CVE-2026-71362. This flaw, described as an incorrect authorization vulnerability, could allow attackers to gain elevated access to sensitive resources without authentication, potentially leading to customer account hijackings.
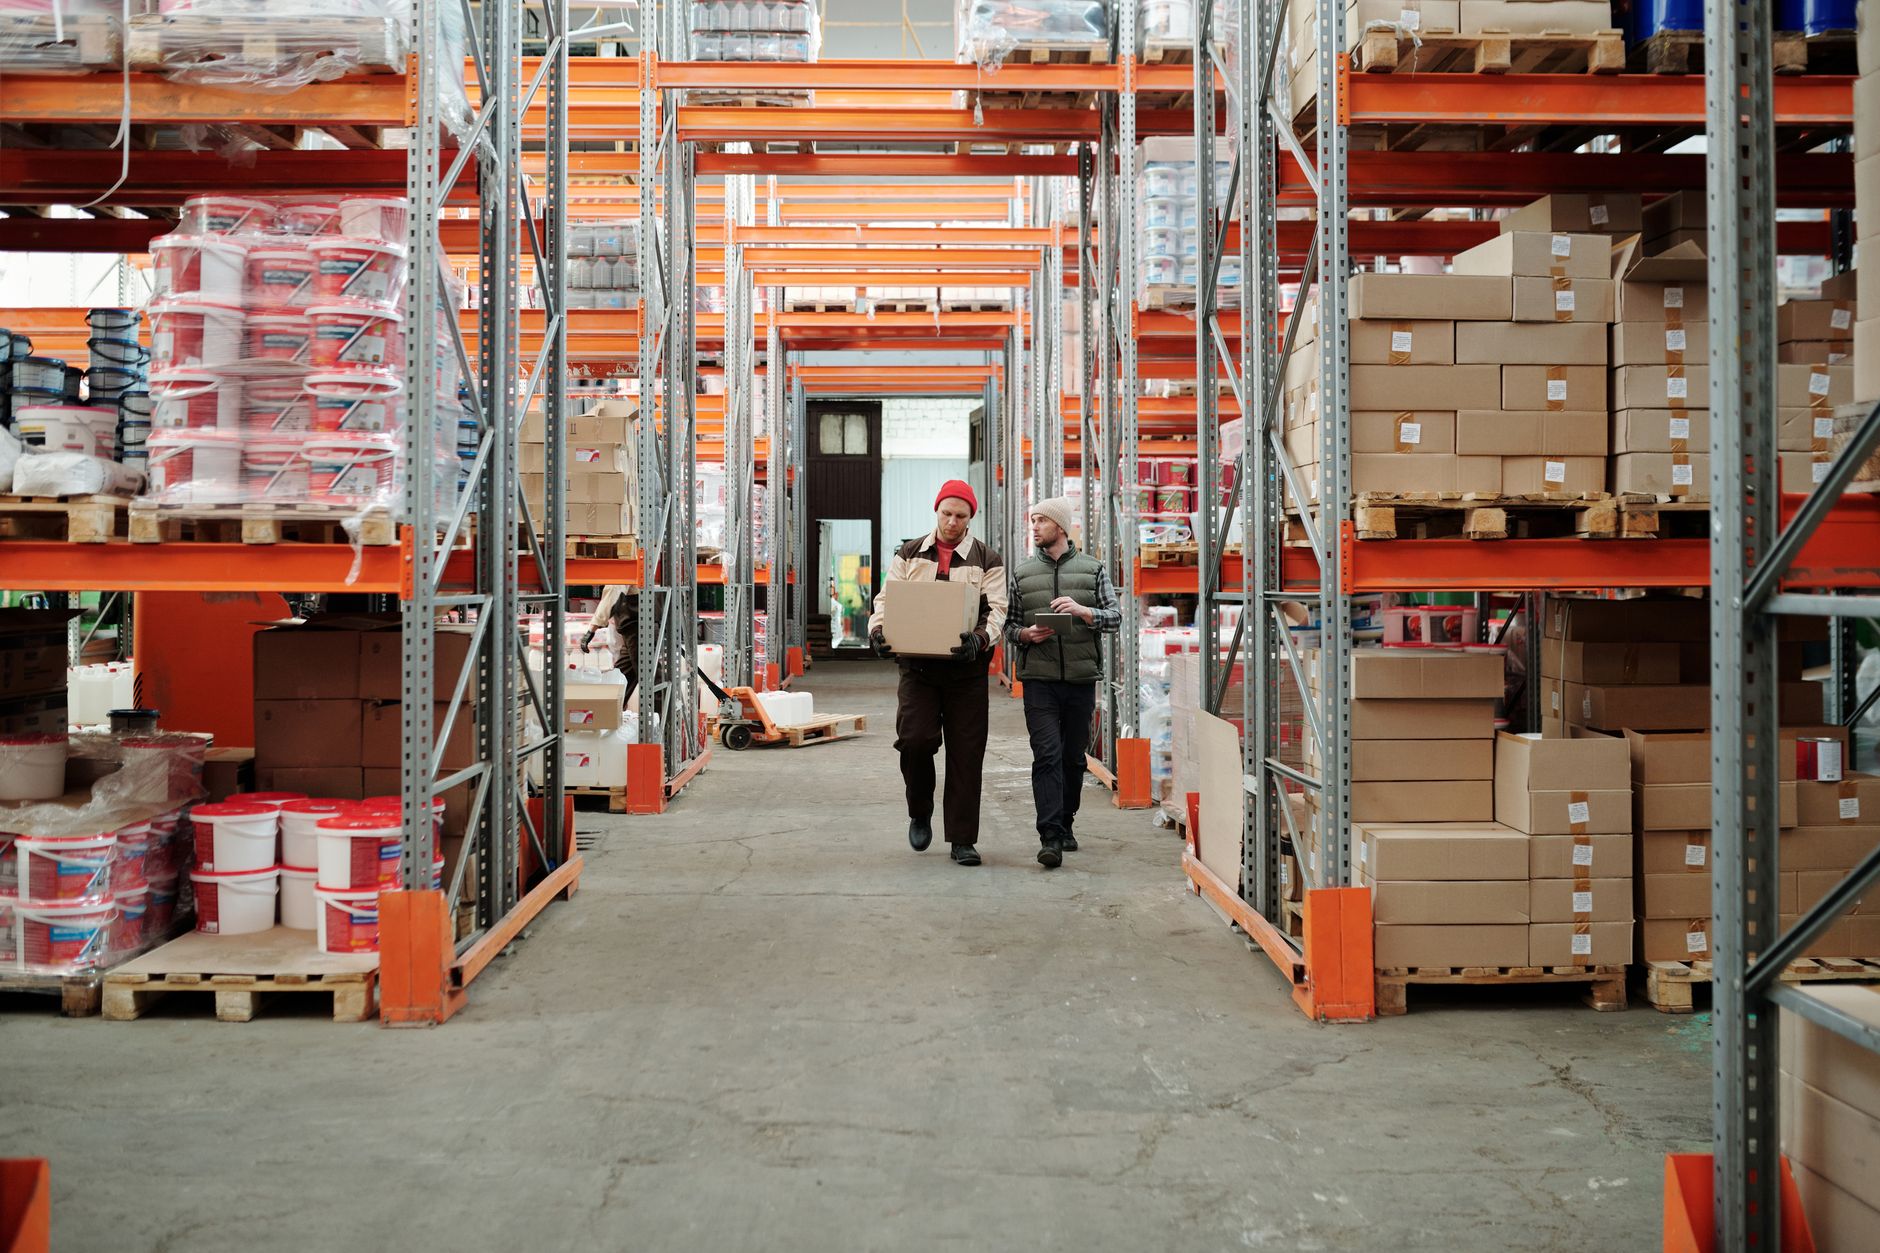
CEVA Logistics Cyberattack Disrupts European Warehouses and Shipments
CEVA Logistics, a major global logistics and supply chain company, experienced a cyberattack on July 29 that significantly disrupted its European operations. The incident affected eight warehouses, leading to halted shipments and ongoing efforts to restore services. CEVA Logistics is part of the CMA CGM Group, one of the world's largest shipping and logistics firms, operating in over 170…
Spectre rears its ugly head again as researchers show some RISC-V chips are susceptible
Researchers have demonstrated that certain commercially available RISC-V processors are vulnerable to various Spectre attacks, a class of speculative execution vulnerabilities previously associated primarily with x86 and ARM architectures. This finding challenges a common assumption that the simpler design of RISC-V chips made them immune to such flaws.
Qualys Introduces Real-Time Cloud Security Posture Management (CSPM) for Faster Risk Detection and Remediation
Qualys has announced the release of Real-Time Cloud Security Posture Management (CSPM), a new capability integrated into the Qualys Cloud Platform designed to provide instant detection and remediation guidance for cloud security risks across multi-cloud environments. The new offering aims to address the limitations of traditional CSPM tools that rely on periodic scans, which can leave…
Hundreds of fake Chrome VPN extensions route traffic through a proxy
More than 737 browser extensions, many impersonating well-known VPN and proxy services, were found on the Chrome Web Store routing user traffic through SOCKS5 proxies. The campaign, identified by researchers at application security company Socket, involved 40 publisher accounts and a shared analytics account, with extensions downloaded nearly 75,000 times, predominantly by users in Russia.
China-Linked Hackers Use AI Agents in Autonomous Attack on Taiwan
An Israeli cybersecurity firm, Dream, has documented what appears to be the first fully autonomous, end-to-end AI hacking operation against a government target, reportedly linked to China and aimed at Taiwan. The attack, which occurred over four days in early July, utilized eight AI agents to breach a government network, exfiltrate data, and compromise accounts with minimal human intervention.
Lazarus Exploits Windows Zero-Day to Gain SYSTEM Access and Deploy Backdoor
A recent report indicates that the Lazarus Group, a North Korean state-sponsored hacking collective, has been exploiting a Windows zero-day vulnerability to achieve SYSTEM-level access and deploy a new backdoor. This activity is part of a broader cyber espionage campaign known as Operation Dream Job. The campaign specifically targets defense and aerospace companies across several countries.
FBI: Hackers using social engineering to breach accounts and steal explicit content
The Federal Bureau of Investigation has issued a public alert regarding a surge in social engineering and cyber intrusion tactics used by threat actors to compromise social media accounts. The attackers are reportedly targeting both adults and children to steal explicit content, which is then sold on illicit marketplaces. The FBI also noted that personal information is often posted alongside…
Researchers observe first ‘near-autonomous’ AI attack on government target in Taiwan
Cybersecurity researchers have identified what they describe as the first "near-autonomous" AI-powered cyberattack targeting a government entity, specifically the Taiwanese government. The attack, which utilized open-source AI models, resulted in the exfiltration of over 2,500 personnel records and other data.