
News Archive
1920 stories · page 73 of 80Every story we've published, newest first. Vulnerability records live in the CVE Tracker.
Weekly Metasploit Update: Modules for SMB-to-Meterpreter, Peyara Remote Mouse RCE exploit, and more
Metasploit has released its weekly update, introducing several new modules and enhancements. Notably, a new module allows for the upgrade of SMB sessions to Meterpreter using PsExec. Additionally, the update includes an exploit for an unauthenticated remote code execution vulnerability in Peyara Remote Mouse 1.0.1 and a new command payload for LoongArch64 Linux systems. Several bug fixes and authentication support improvements for the MCP server's HTTP transport are also part of this release.
Unpatched Flaws Disclosed in Filesystem Bundled Into Millions of Embedded Devices
Security firm runZero has disclosed seven vulnerabilities in FatFs, a small filesystem library that lets a device read and write the FAT and exFAT formats used on USB drives and SD cards. The flaws matter because FatFs is nearly everywhere.
New "Bad Epoll" Linux Kernel Flaw Lets Unprivileged Users Gain Root, Hits Android
A newly disclosed Linux kernel flaw called Bad Epoll (CVE-2026-46242) lets an ordinary user with no special access take full control of a machine as root. It affects Linux desktops, servers, and Android, and a fix is out. Bad Epoll sits in
New Avalon Malware Framework Packs CrownX Ransomware Capabilities
Cybersecurity researchers have discovered a previously undocumented modular malware framework codenamed Avalon that's distributed by means of a multi-stage phishing chain capable of bypassing traditional security controls. Avalon combines c
North Korea-Linked npm Packages Mimic Rollup Polyfills to Steal Developer Secrets
Threat actors with ties to North Korea have been linked to a fresh set of malicious npm packages that masquerade as Rollup polyfill tooling to facilitate remote access and data theft. According to JFrog, the packages "rollup-packages-polyfi
Armored Likho Targets Government Agencies, Power Sector with BusySnake Stealer
A previously undocumented threat actor known as Armored Likho has been attributed to cyber attacks targeting government agencies and the electric power sector across Russia, Brazil, and Kazakhstan. "Armored Likho blends financially motivate
Chinese LLMs Broaden the Gap Between Attackers & Defenders
Two new models from Chinese firms compete with top US mainstream and frontier models. Should cyber-defenders be worried?
SMBs urged to focus on cyber basics amid AI-driven threats
Small and medium-sized businesses are reminded that fundamental cybersecurity practices remain crucial, even as artificial intelligence transforms the landscape of cybercrime. Addressing common vulnerabilities is key to improving overall readiness against evolving threats.
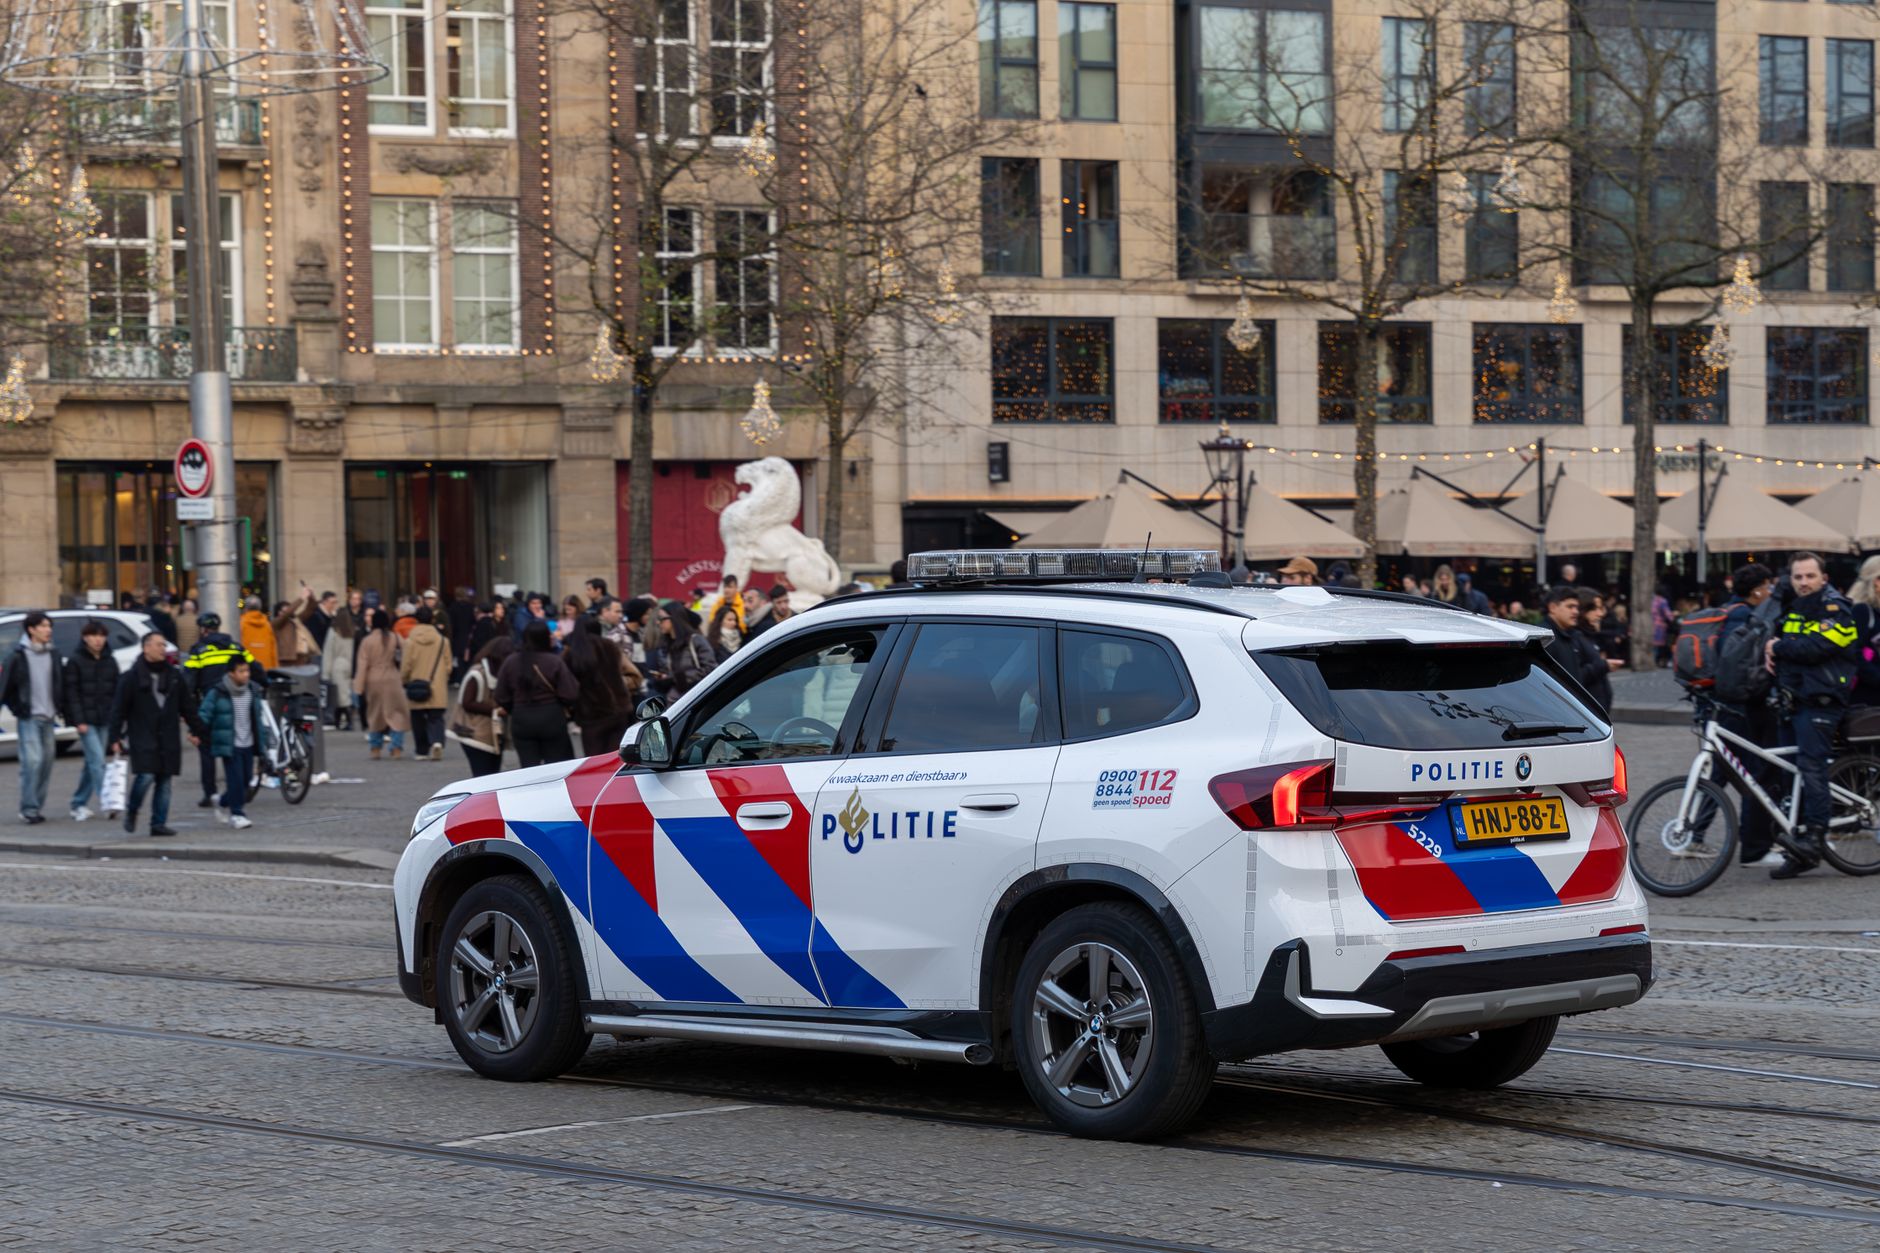
Flock Cameras Can Surveil Cars Without License Plates
This is from a 2024 company presentation: Officers can also tap into data showing a car’s decals, bumper stickers, back and top racks—along with temporary and unique state tags. Flock calls it a “Vehicle Fingerprint” and it’s touted as a wa
European Parliament Member Investigating Spyware Was Hacked With Pegasus
A new report from the Citizen Lab has revealed that former Member of the European Parliament Stelios Kouloglou had his mobile device repeatedly hacked with the notorious Pegasus spyware while serving on a committee that was tasked with inve
Armored Likho digging a snake pit: inside the covert BusySnake Stealer campaign
A new phishing campaign has been identified, attributed to a previously unknown APT group named Armored Likho. This group targets government agencies and the electric power sector in Russia, Brazil, and Kazakhstan. They employ a diverse toolkit, including a new Python-based infostealer called BusySnake Stealer, and utilize AI-generated payloads to evade detection and complicate attribution.
PamStealer Uses Fake Maccy Sites and PAM Checks to Steal Mac Login Passwords
Cybersecurity researchers have flagged a new macOS information stealer called PamStealer that employs a series of clever tricks to infect systems and siphon sensitive data. The stealer, discovered by Jamf Threat Labs, is distributed as a co

Swimming Pools, Pee, and Trying to Delete Your Data From the Internet
I can't recall if someone else originally came up with this saying or if I said it in some off-the-cuff comment and it just propagated, but since it's often attributed back to me, I'll relay it here regardless: Trying to delete yourself
Aussies Face Reduced Cybercrime Risk, as Pressure Shifts to SMBs
Improved institutional safeguards and stricter regulations have pushed the burdens of protection and risk reduction on to Australian businesses.
WebAuthn Added to Browser-Based RDP Client
Researchers have successfully integrated WebAuthn authentication into a browser-based Remote Desktop Protocol (RDP) client. This involved a significant reverse-engineering effort to enable the client, which operates outside of the Windows ecosystem, to support WebAuthn redirection.
Apple Reverses Age-Old Patch Policy to Keep Up With AI
Expect more compressed patching cycles from Apple going forward, as attackers leverage artificial intelligence to reduce time to exploit.
FBI Seizes NetNut Proxy Platform, Popa Botnet
The Federal Bureau of Investigation (FBI) said today it worked with industry partners to seize hundreds of domains associated with NetNut, a sprawling residential proxy service operated by the publicly-traded Israeli company Alarum Technolo
FortiBleed Actors Collaborating With Inc, Lynx Ransomware Gangs
After gaining a foothold in thousands of Fortinet firewalls, the attackers are starting to monetize that access, and are also piling on a Nextcloud zero-day bug.
Google Disrupts NetNut Residential Proxy Network Spanning 2 Million Home Devices
Google has significantly degraded NetNut, one of the biggest networks that turns home devices into rented relays for other people's traffic. Working with the FBI, Lumen, and others, Google's Threat Intelligence Group (GTIG) said this week i
Ransomware Groups Turn to Citrix Bleed 2, BYOVD, and Supply Chain Credentials
Threat actors associated with the Anubis ransomware operation have been observed exploiting the Citrix Bleed 2 (CVE-2025-5777) vulnerability to obtain initial access. "Although tactics differ between affiliates, common patterns emerged in t
Ransomware Thugs Masquerade as Interpol to Entice Small Biz
The ransomware campaign relies on basic social engineering and stretches across multiple regions, including the US, Europe, Middle East, and elsewhere.
Catan and Mouse
What do board games and cybersecurity have in common? Pattern recognition. Strategy. Adaptation. In this week’s Threat Source Bill explores why curiosity may be a defender’s most valuable skill.
The Gentlemen ransomware: what you need to know
Who Are The Gentlemen? Despite the impeccably polite name, there is nothing polite or refined about this particular gang of cybercriminals. Read more in my article on the Fortra blog.
Improving security posture across the Microsoft partner ecosystem
Microsoft is detailing its strategy for enhancing security within its partner ecosystem, particularly focusing on Cloud Solution Providers (CSPs). These partners are crucial for deploying and managing Microsoft cloud services like Azure and Microsoft 365. The company aims to ensure the partner network remains healthy, compliant, and effective to deliver optimal customer outcomes.