LIVE · cybersecurity feed
Live wire
CVE-2026-103898 · Wpmet wp_social_login_and_register_social_counter Flaw Exploited Upon DisclosureCVE-2026-116512 · weDevs wp_project_manager Flaw Exploited Before CVE PublicationCVE-2026-119096 · Uncanny Toolkit for LearnDash Improper Authentication Exploited on DisclosureCVE-2010-20125 · DedeCMS Vulnerability CVE-2010-20125 Exploited On Day Of DisclosureCVE-2015-20130 · Netsweeper Improper Neutralization Flaw Exploited Upon DisclosureCVE-2025-31704 · Dahua Intelligent Connection Center Flaw Exploited on Day of DisclosureCVE-2026-103039 · Gravity Forms Deserialization Flaw Exploited Upon DisclosureCVE-2026-118539 · Drupal Commerce Core Access Bypass Exploited Before CVE PublicationThe Fridge-Hacking Spree Is an Internet-of-Things Wake-Up CallCVE-2026-19868 · U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog
vulnerabilitycritical

CISA alerts of active exploitation of three Linux kernel flaws

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning regarding the active exploitation of three distinct vulnerabilities within the Linux kernel, one of which is rated critical. These security issues were added to CISA's catalog last week, with severity ratings ranging from medium to critical. Federal agencies have been mandated to apply available security…

ZeroDay News ·

Source: BleepingComputer

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning regarding the active exploitation of three distinct vulnerabilities within the Linux kernel, one of which is rated critical. These security issues were added to CISA's catalog last week, with severity ratings ranging from medium to critical. Federal agencies have been mandated to apply available security updates and mitigations for these flaws by the end of today.

One of the vulnerabilities, identified as CVE-2025-39964, is a race condition found in the kernel's AF_ALG cryptographic socket interface. This flaw, which has existed in the Linux kernel for 14 years, allows concurrent writes to corrupt per-socket state, potentially leading to system crashes or alterations of cryptographic results. Offensive security company STAR Labs discovered this issue, demonstrating its potential for privilege escalation and container escape within Google's kernelCTF environment.

Another critical vulnerability is CVE-2026-53266, an out-of-bounds write flaw in the Linux kernel's ebtables SNAT implementation. This defect can cause an ARP address rewrite to modify shared file-backed memory without first ensuring the affected packet range is writable. Red Hat has confirmed the existence of a known exploit for this vulnerability. Researcher Kimmo Suominen has published a technical analysis and patch-status tracker on GitHub, outlining a potential privilege-escalation path, though this specific exploitation chain is inferred by analogy with the "Dirty Pipe" vulnerability and has not been publicly demonstrated.

The third vulnerability, CVE-2025-39682, is a logic flaw in the Linux kernel's TLS receive-path. It mishandles zero-length records queued for later processing, which could allow different TLS record types to be processed together when kTLS is in use. Public exploits for this flaw are available, a fact also confirmed by Red Hat in its security bulletin.

CISA has confirmed that all three vulnerabilities are actively being exploited in attacks, though the agency has not provided specific details about the incidents or the nature of the threat actors involved. The agency has marked all three flaws as requiring forensic triage, meaning federal agencies must examine affected assets for any signs of prior exploitation. As of now, none of these vulnerabilities are flagged as being exploited by ransomware groups.
vulnerabilitycloud
ShareXLinkedInWhatsAppFacebook

More News

view all →
CVE-2026-103898high

Wpmet wp_social_login_and_register_social_counter Flaw Exploited Upon Disclosure

The Wpmet wp_social_login_and_register_social_counter plugin vulnerability CVE-2026-103898 was identified as exploited on the same day it was published.

CVE-2026-116512high

weDevs wp_project_manager Flaw Exploited Before CVE Publication

The weDevs wp_project_manager plugin was identified as under exploitation one day before the CVE was officially published, leaving users with no patch window.

CVE-2026-119096high

Uncanny Toolkit for LearnDash Improper Authentication Exploited on Disclosure

The Uncanny Toolkit for LearnDash plugin was identified as exploited on the same day its CVE was published, leaving no window for remediation.

CVE-2010-20125high

DedeCMS Vulnerability CVE-2010-20125 Exploited On Day Of Disclosure

The DedeCMS vulnerability CVE-2010-20125 was identified as exploited on the same day it was published, leaving no window for remediation.

breach

Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches

A series of cyberattacks between late September and early October 2026 resulted in the compromise of seven South Korean financial institutions. The breaches led to the exposure of sensitive personal, employment, income, and loan-related data belonging to approximately 66,000 individuals and 2,200 corporations. Security researchers have linked these incidents to the use of an open-source…

finance

Hackers pull off $133 million French bank heist via service provider

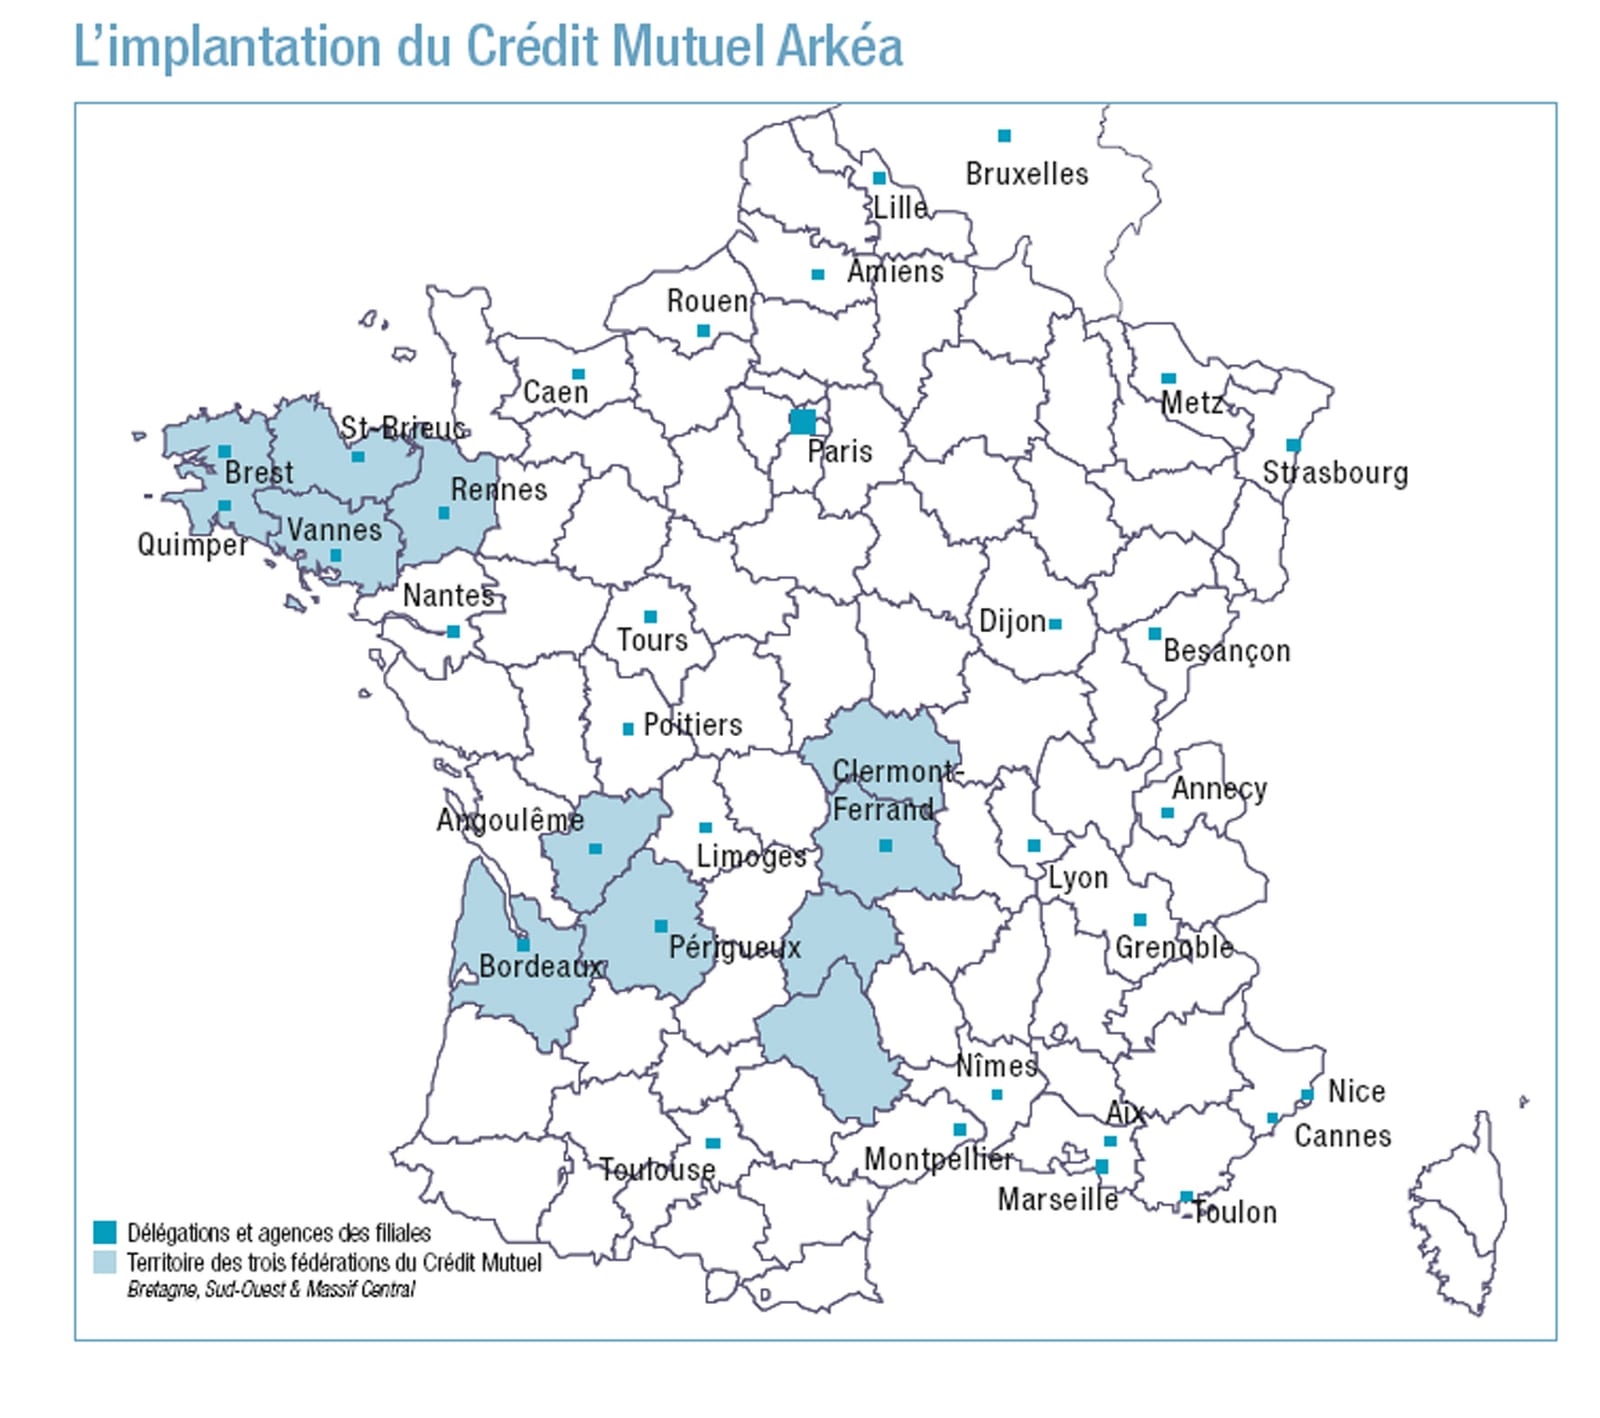
The French cooperative banking group Credit Mutuel Arkea has confirmed it was the target of a sophisticated cyberattack that resulted in unauthorized financial transactions. While the bank has not officially verified the exact figure, independent investigators have estimated the total loss at approximately 118 million euros, or 133 million dollars. The incident, which came to light following…