LIVE · cybersecurity feed
Live wire
How Cloudflare WAF helps protect against phpAfterShell and other critical PHP flawsCVE-2026-114938 · A Technical Guide to Mitigate Java4Shell with TruRisk EliminateCVE-2026-104995 · Dontdream BP Profile Search Vulnerability Listed As Exploited In VulnCheck KEVCVE-2026-54836 · YMC Filter SQL Injection Vulnerability Added to VulnCheck KEVCVE-2026-7542 · Slider Revolution Sensitive Information Exposure Added To VulnCheck KEVCVE-2024-8517 · SPIP External Control Vulnerability CVE-2024-8517 Added To VulnCheck KEVSean Cairncross out as national cyber directorVMware patches vCenter zero-day exploited in attacks since SeptemberASUS warns of critical hard-coded key flaw in Control Center ExpressCVE-2026-123890 · CVE-2026-123890: Critical Authentication Bypass in VMware vCenter
security

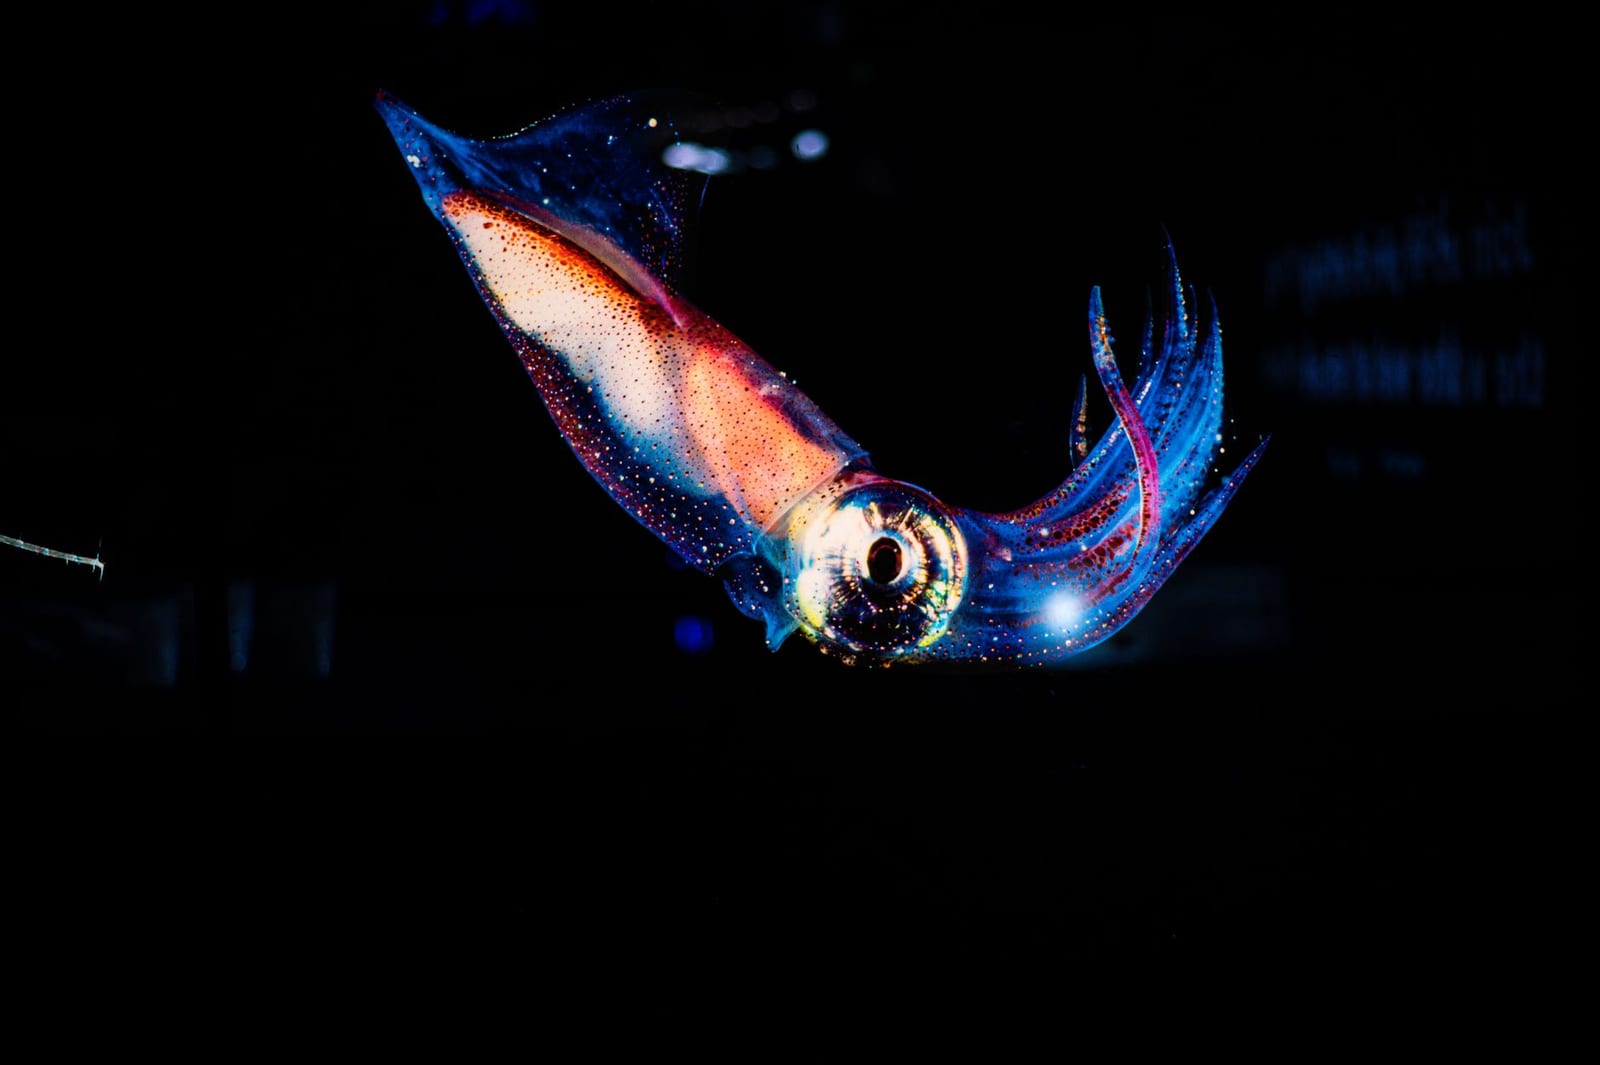
Friday Squid Blogging: The Largest Squid Ever Filmed

Researchers have documented the capture of the largest squid ever filmed, an event that occurred in December 2006 near Japan’s Ogasawara Islands. The footage provides a rare look at a giant cephalopod in its natural deep-sea habitat, marking a significant milestone in marine biology and observational science.

ZeroDay News ·

Source: Schneier on Security

Researchers have documented the capture of the largest squid ever filmed, an event that occurred in December 2006 near Japan’s Ogasawara Islands. The footage provides a rare look at a giant cephalopod in its natural deep-sea habitat, marking a significant milestone in marine biology and observational science.

While the specifics of this biological encounter are unique, the challenges of monitoring deep-sea environments often mirror the difficulties of maintaining visibility in complex, remote technical systems. In both domains, the ability to observe and record activity in environments that are difficult to access is essential for understanding baseline behaviors and identifying anomalies.

In the context of information security, the difficulty of monitoring "deep" or obscure system layers often leads to gaps in visibility. When security teams lack the telemetry required to observe activity in remote or legacy segments of a network, they are effectively operating in the dark. This lack of visibility is a common hurdle when attempting to detect sophisticated, low-frequency threats that may persist for long periods without triggering standard alerts.

For organizations managing large-scale infrastructure, the primary mitigation strategy for these visibility gaps involves the implementation of robust logging and continuous monitoring solutions. By ensuring that telemetry is collected from all layers of the stack, security operations centers can better identify the "large" or unusual events that might otherwise go unnoticed. This class of issue typically requires a combination of behavioral analytics and improved sensor placement to ensure that even the most elusive activity is captured.

The documentation of this squid serves as a reminder that the most significant events often occur in the most difficult-to-reach environments. As security professionals continue to navigate an increasingly complex landscape, the focus remains on improving the tools and techniques used to observe, analyze, and secure the infrastructure that supports modern global operations.
ShareXLinkedInWhatsAppFacebook

More News

view all →
malware

Fake GTA VI Streaming Client Installs Data-Stealing Malware on Windows PCs

Security researchers at Bitdefender have issued an alert regarding a malicious campaign that leverages the high anticipation for the upcoming Grand Theft Auto VI title to distribute data-stealing malware. The campaign targets Windows gamers by enticing them to download a fake streaming client that purports to provide early access to the game. Once executed, the software functions as a vehicle…

ai

Signal Blocks AI Agents From Reading Private Chats via Screenshots on Android and iOS

Signal has announced a new security measure designed to prevent artificial intelligence agents from accessing private chat content via screen capture on both Android and iOS platforms. The messaging service is implementing a default restriction on screenshots to mitigate the risk of automated systems scraping sensitive user data. While the company has framed this as a necessary defensive step…

patch

PHP 8.6: Things are gonna get a lot more strict around here

The PHP development team has officially released PHP 8.6, marking the latest iteration of the widely used server-side scripting language. This release arrives following a turbulent period for the platform, which has faced a surge of security vulnerabilities since October. These flaws, which allowed unauthenticated attackers to trigger remote code execution (RCE) or crash PHP workers,…

security

4 Best XRP Lending Platforms Compared by Security, LTV, and Speed

A recent comparative analysis has evaluated four prominent platforms facilitating XRP lending, focusing on the trade-offs between security protocols, loan-to-value (LTV) ratios, and transaction speeds. The review examines CoinRabbit, Arch, Nexo, and Coinbase, providing a technical overview of how these services manage collateralized digital asset lending.

CVE-2026-23871

CVE-2026-23871: WhatsApp Bug Helped Scammers Make Messages Look Legitimate

WhatsApp has released security updates addressing three vulnerabilities, one of which was actively exploited in a scam campaign designed to increase the perceived legitimacy of fraudulent messages. The company identified this specific flaw, tracked as CVE-2026-23871, while investigating and disrupting an ongoing fraud operation.

cloud

Dialing for Data: Inside the Com’s High-Profile Heists

Security researchers have identified a persistent and evolving campaign of vishing-led cyberattacks targeting data-intensive industries across the United States, the United Kingdom, and Australia. Since August 2026, a network of threat actors associated with the Com collective has conducted a series of data theft and extortion operations. These attacks primarily target the financial,…



