LIVE · cybersecurity feed
Live wire
CVE-2026-103898 · Wpmet wp_social_login_and_register_social_counter Flaw Exploited Upon DisclosureCVE-2026-116512 · weDevs wp_project_manager Flaw Exploited Before CVE PublicationCVE-2026-119096 · Uncanny Toolkit for LearnDash Improper Authentication Exploited on DisclosureCVE-2010-20125 · DedeCMS Vulnerability CVE-2010-20125 Exploited On Day Of DisclosureCVE-2015-20130 · Netsweeper Improper Neutralization Flaw Exploited Upon DisclosureCVE-2025-31704 · Dahua Intelligent Connection Center Flaw Exploited on Day of DisclosureCVE-2026-103039 · Gravity Forms Deserialization Flaw Exploited Upon DisclosureCVE-2026-118539 · Drupal Commerce Core Access Bypass Exploited Before CVE PublicationThe Fridge-Hacking Spree Is an Internet-of-Things Wake-Up CallCVE-2026-19868 · U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog
cloud

Grindr settles privacy lawsuit tied to disclosure of users’ HIV statuses for $35 million

Grindr, the LGBTQ+ dating application, has agreed to a settlement of £26 million, equivalent to approximately $35.2 million, to resolve a UK lawsuit. The legal action alleged that the company shared sensitive user data, including HIV statuses, with advertisers.

ZeroDay News ·

Source: The Record

Grindr, the LGBTQ+ dating application, has agreed to a settlement of £26 million, equivalent to approximately $35.2 million, to resolve a UK lawsuit. The legal action alleged that the company shared sensitive user data, including HIV statuses, with advertisers.

The settlement was formalized in a regulatory filing with the Securities and Exchange Commission (SEC) on September 4, indicating that the payment will be made in two installments. The first payment is due by the end of December, with the second scheduled for the end of March.

The lawsuit, initiated by UK users in April 2024, claimed violations of the country's privacy laws. The alleged data sharing incidents occurred before early 2020, during a period when Grindr was under the ownership and management of a Chinese company, Kuntun.

While Grindr maintains that the settlement includes no findings or admission of liability, the company acknowledged in its SEC filing "the distress and loss of trust expressed by some of its UK users regarding that pre-2020 period." The company spokesperson declined further comment, directing inquiries to the regulatory filing.

According to the filing, Grindr has "overhauled its privacy program with a keen focus on the unique needs of its community" since new ownership took over in 2020. The company stated it "is and remains a safe space for users, committed to transparency, user control, and responsible data practices."

In May 2024, Kelly Peterson Miranda, then Grindr's chief privacy officer, refuted the lawsuit's central claims. She stated that the company never sold health information, specifically HIV last-tested dates, for advertising purposes. She clarified that health-related information was never used for advertising.

Peterson Miranda explained that the information was shared with two service providers to facilitate the development of a new feature. This feature allowed users to include their HIV status in a dedicated profile field. She emphasized that the sharing was not a breach and was not done unknowingly, but rather in encrypted formats for the purpose of rolling out and monitoring the feature.

The lawsuit reportedly involved approximately 12,000 class members.
cloud
ShareXLinkedInWhatsAppFacebook

More News

view all →
breach

Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches

A series of cyberattacks between late September and early October 2026 resulted in the compromise of seven South Korean financial institutions. The breaches led to the exposure of sensitive personal, employment, income, and loan-related data belonging to approximately 66,000 individuals and 2,200 corporations. Security researchers have linked these incidents to the use of an open-source…

CVE-2026-103898high

Wpmet wp_social_login_and_register_social_counter Flaw Exploited Upon Disclosure

The Wpmet wp_social_login_and_register_social_counter plugin vulnerability CVE-2026-103898 was identified as exploited on the same day it was published.

CVE-2026-116512high

weDevs wp_project_manager Flaw Exploited Before CVE Publication

The weDevs wp_project_manager plugin was identified as under exploitation one day before the CVE was officially published, leaving users with no patch window.

CVE-2026-119096high

Uncanny Toolkit for LearnDash Improper Authentication Exploited on Disclosure

The Uncanny Toolkit for LearnDash plugin was identified as exploited on the same day its CVE was published, leaving no window for remediation.

finance

Hackers pull off $133 million French bank heist via service provider

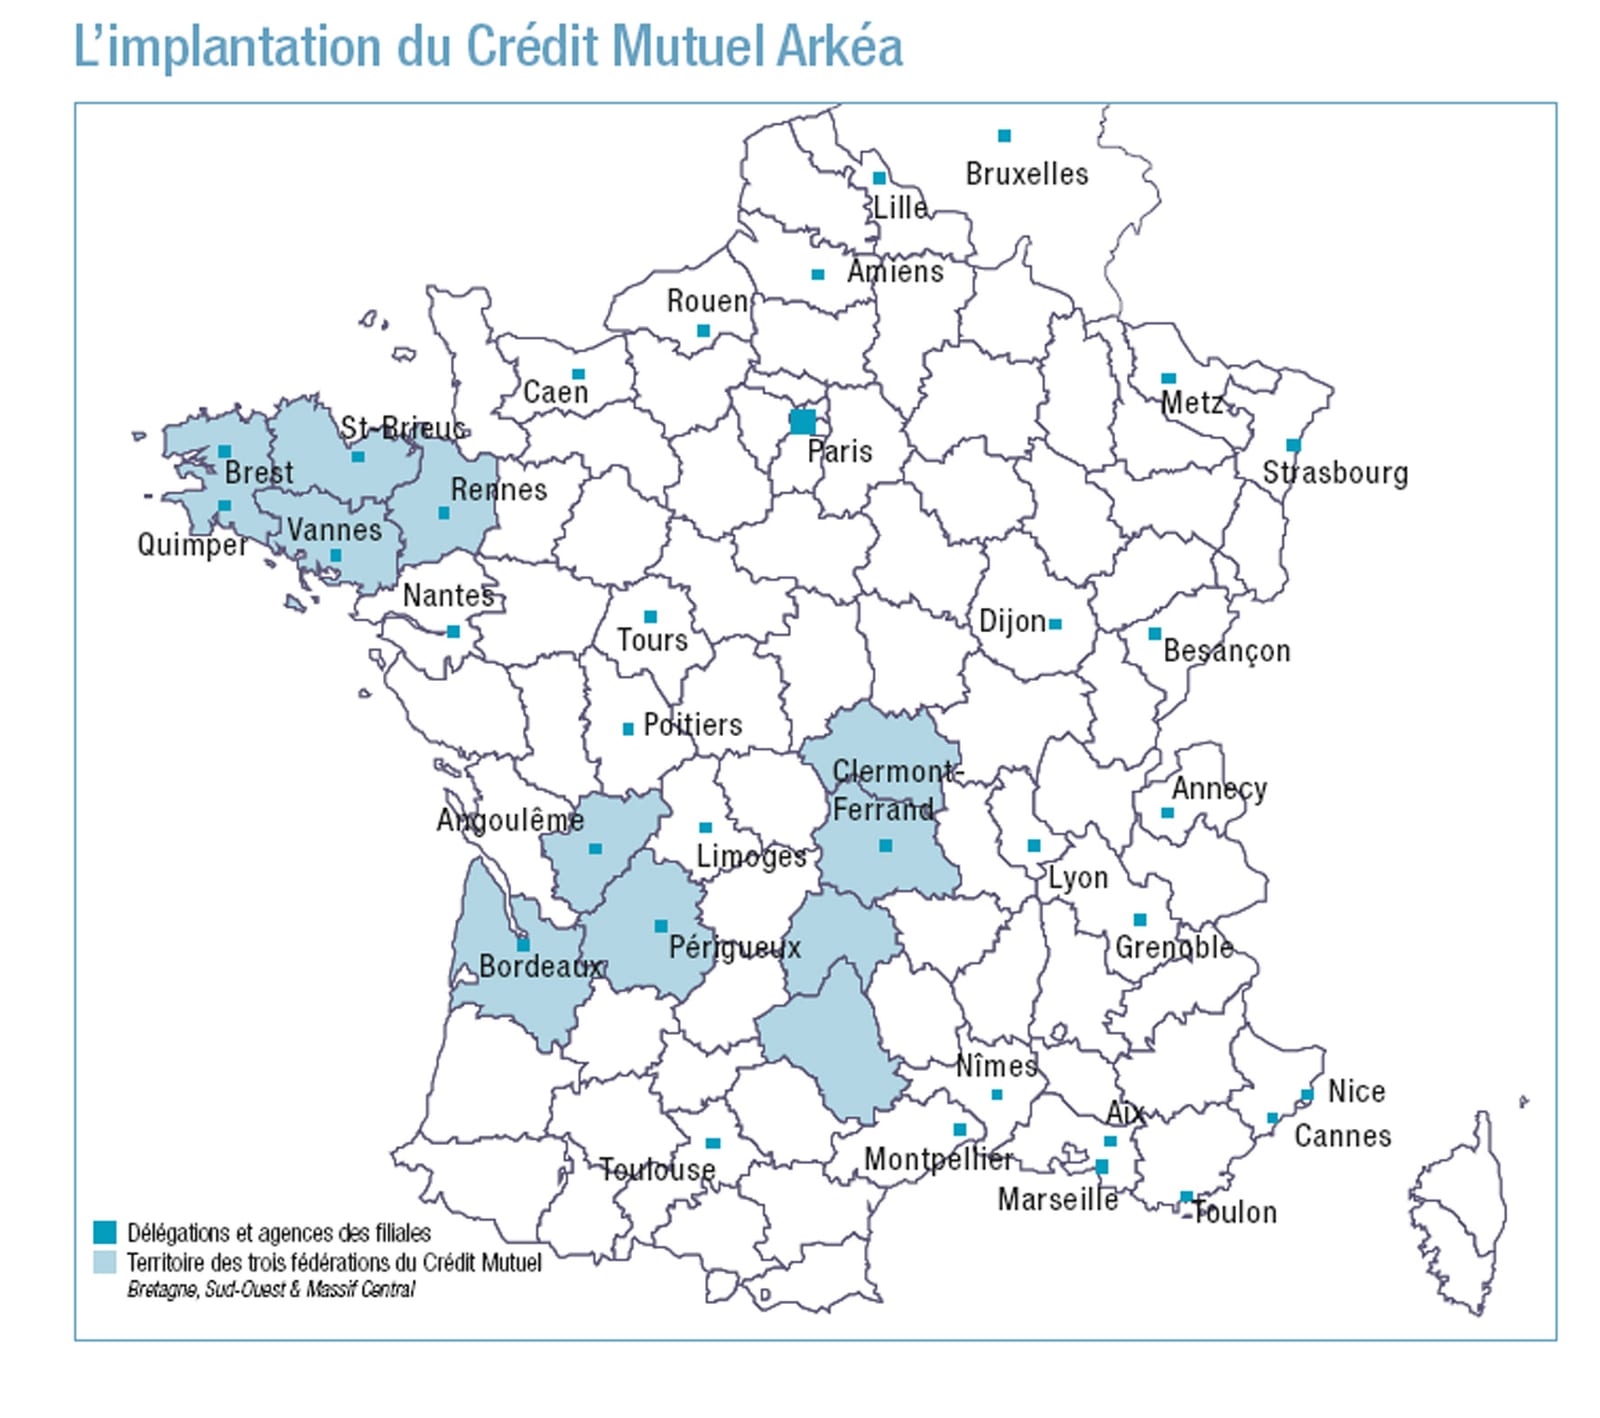
The French cooperative banking group Credit Mutuel Arkea has confirmed it was the target of a sophisticated cyberattack that resulted in unauthorized financial transactions. While the bank has not officially verified the exact figure, independent investigators have estimated the total loss at approximately 118 million euros, or 133 million dollars. The incident, which came to light following…

security

CTM360 Exposes Fake Gift Card Scams Exploiting Trusted Brands

A surge in fraudulent gift card campaigns is currently targeting consumers by weaponizing the reputations of major global retailers. Security researchers at CTM360 have identified over 1,000 distinct incidents where threat actors impersonate well-known brands, including Amazon, Walmart, Sephora, SHEIN, and PlayStation. These campaigns are designed to exploit consumer trust through…