LIVE · cybersecurity feed
Live wire
CVE-2026-103898 · Wpmet wp_social_login_and_register_social_counter Flaw Exploited Upon DisclosureCVE-2026-116512 · weDevs wp_project_manager Flaw Exploited Before CVE PublicationCVE-2026-119096 · Uncanny Toolkit for LearnDash Improper Authentication Exploited on DisclosureCVE-2010-20125 · DedeCMS Vulnerability CVE-2010-20125 Exploited On Day Of DisclosureCVE-2015-20130 · Netsweeper Improper Neutralization Flaw Exploited Upon DisclosureCVE-2025-31704 · Dahua Intelligent Connection Center Flaw Exploited on Day of DisclosureCVE-2026-103039 · Gravity Forms Deserialization Flaw Exploited Upon DisclosureCVE-2026-118539 · Drupal Commerce Core Access Bypass Exploited Before CVE PublicationThe Fridge-Hacking Spree Is an Internet-of-Things Wake-Up CallCVE-2026-19868 · U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog
vulnerability

The vulnpocalypse rains iBugs down on Apple with record-setting number of patches

Apple has released a substantial security update across its operating systems and software, addressing over 260 Common Vulnerabilities and Exposures (CVEs). This marks the largest single patch cycle in the company's history. While no vulnerabilities are currently reported as being under active exploitation, the disclosure of these flaws often prompts attackers to attempt to exploit them.

ZeroDay News ·

Source: The Register — Security

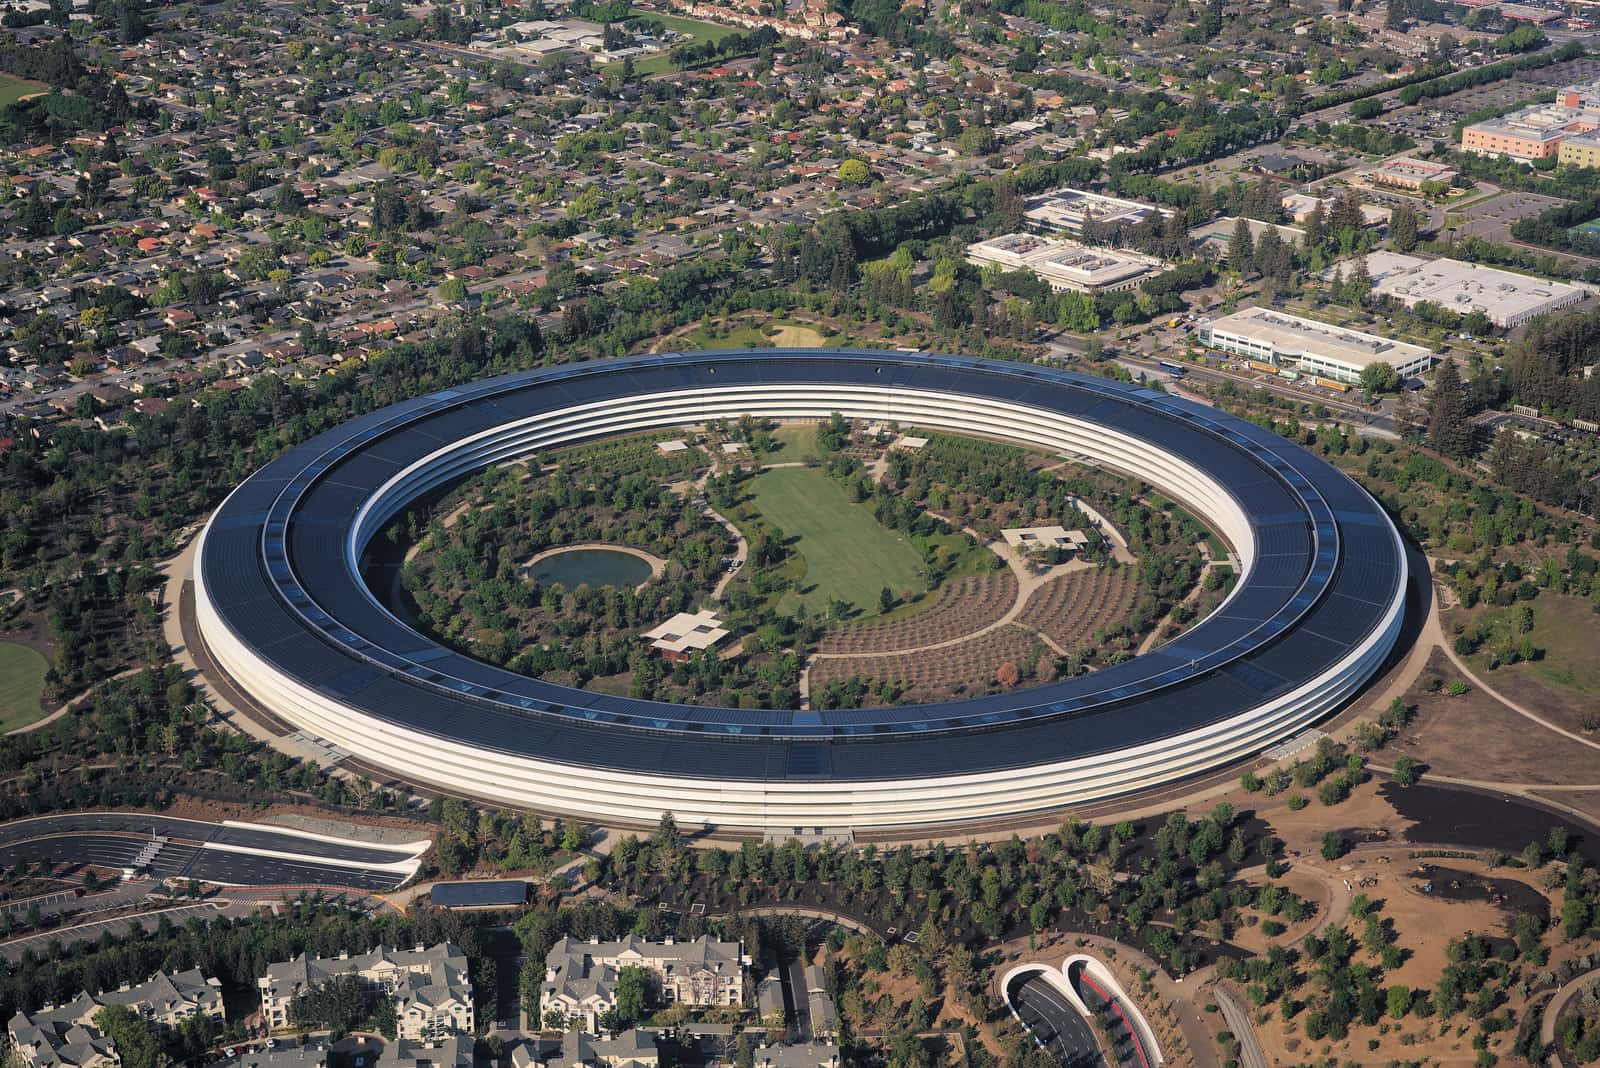
Photo: Daniel L. Lu (user:dllu) (CC BY-SA 4.0) via Wikimedia Commons

Apple has released a substantial security update across its operating systems and software, addressing over 260 Common Vulnerabilities and Exposures (CVEs). This marks the largest single patch cycle in the company's history. While no vulnerabilities are currently reported as being under active exploitation, the disclosure of these flaws often prompts attackers to attempt to exploit them.

The updates include iOS 27 and macOS 27 Golden Gate, which were released on Monday. iOS 27 resolves 122 security vulnerabilities affecting iPhones and iPads, while macOS 27 addresses 204 vulnerabilities across Mac computers.

Among the hundreds of patched CVEs, Apple has credited artificial intelligence (AI) with the discovery of ten. Two of these AI-discovered flaws affect both iOS and macOS: CVE-2026-65410, a vulnerability in AVE video encoders that could cause unexpected system termination, and CVE-2026-65409, a type-confusion issue in the Foundation framework that could lead to a denial of service. Both were reported by Calif, in collaboration with Claude and Anthropic Research, with human researcher Bruce Dang specifically noted for CVE-2026-65409.

Additional AI-assisted discoveries in macOS 27 include several critical vulnerabilities. CVE-2026-43692, a validation issue in the CUPS printer interface, could allow a remote user to terminate an application or execute arbitrary code. CVE-2026-64790, also in CUPS, could lead to elevated privileges. Aaron Grattafiori and the Nvidia AI Red Team are credited with disclosing both of these CUPS flaws.

Other AI-identified issues in macOS include CVE-2026-43791, a StorageKit validation issue that could allow file reading, reported by Grattafiori, the Nvidia AI Red Team, Meridian Miftari, and Amy from amys.website. Several vulnerabilities were found in the Server Message Block (SMB) network communication protocol: CVE-2026-43690, a race-condition bug allowing local users to read kernel memory, reported by Calif's Bruce Dang with Claude and Anthropic Research; CVE-2026-43719, an SMB use-after-free bug discovered by Calif's Dang and Jakob Pammer, Claude, and Anthropic, which could lead to system termination when mounting a malicious SMB share; and CVE-2026-65376, an out-of-bounds-read flaw reported by Dang, Claude, Anthropic, and 재영 정.

The WebDAV protocol also had several AI-discovered vulnerabilities patched in macOS. CVE-2026-65374, a memory-corruption issue, could lead to code execution, reported by Dang, Claude, Anthropic, and He Wei (ギカク). CVE-2026-65375 could cause unexpected system termination, credited to Dang, Claude, Anthropic, and Devcore Research Team’s YingMuo. CVE-2026-43677, an out-of-bounds write issue, was reported by a larger group including Dang, Claude, Anthropic, bubu, Omar Cerrito, HE WEI(ギカク), Roman Zabicki, Richard Zana, Chris Bailey - Short Circuit, Aswin Kumar Gokulakannan, and Surya Narayan Kushwaha.

Beyond the AI-assisted discoveries, other significant vulnerabilities were addressed. In iOS 27, CVE-2026-43689 is a privilege-escalation flaw that could grant an application root access, reported by Nosebeard Labs’ Andreas Jaegersberger and Ro Achterberg. CVE-2026-65406, a logic issue in Background Assets due to improper validation, could allow access to sensitive user data and was reported by Baidu Security researcher Ye Zhang.
vulnerabilitypatch
ShareXLinkedInWhatsAppFacebook

More News

view all →
CVE-2026-103898high

Wpmet wp_social_login_and_register_social_counter Flaw Exploited Upon Disclosure

The Wpmet wp_social_login_and_register_social_counter plugin vulnerability CVE-2026-103898 was identified as exploited on the same day it was published.

CVE-2026-116512high

weDevs wp_project_manager Flaw Exploited Before CVE Publication

The weDevs wp_project_manager plugin was identified as under exploitation one day before the CVE was officially published, leaving users with no patch window.

CVE-2026-119096high

Uncanny Toolkit for LearnDash Improper Authentication Exploited on Disclosure

The Uncanny Toolkit for LearnDash plugin was identified as exploited on the same day its CVE was published, leaving no window for remediation.

CVE-2010-20125high

DedeCMS Vulnerability CVE-2010-20125 Exploited On Day Of Disclosure

The DedeCMS vulnerability CVE-2010-20125 was identified as exploited on the same day it was published, leaving no window for remediation.

breach

Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches

A series of cyberattacks between late September and early October 2026 resulted in the compromise of seven South Korean financial institutions. The breaches led to the exposure of sensitive personal, employment, income, and loan-related data belonging to approximately 66,000 individuals and 2,200 corporations. Security researchers have linked these incidents to the use of an open-source…

finance

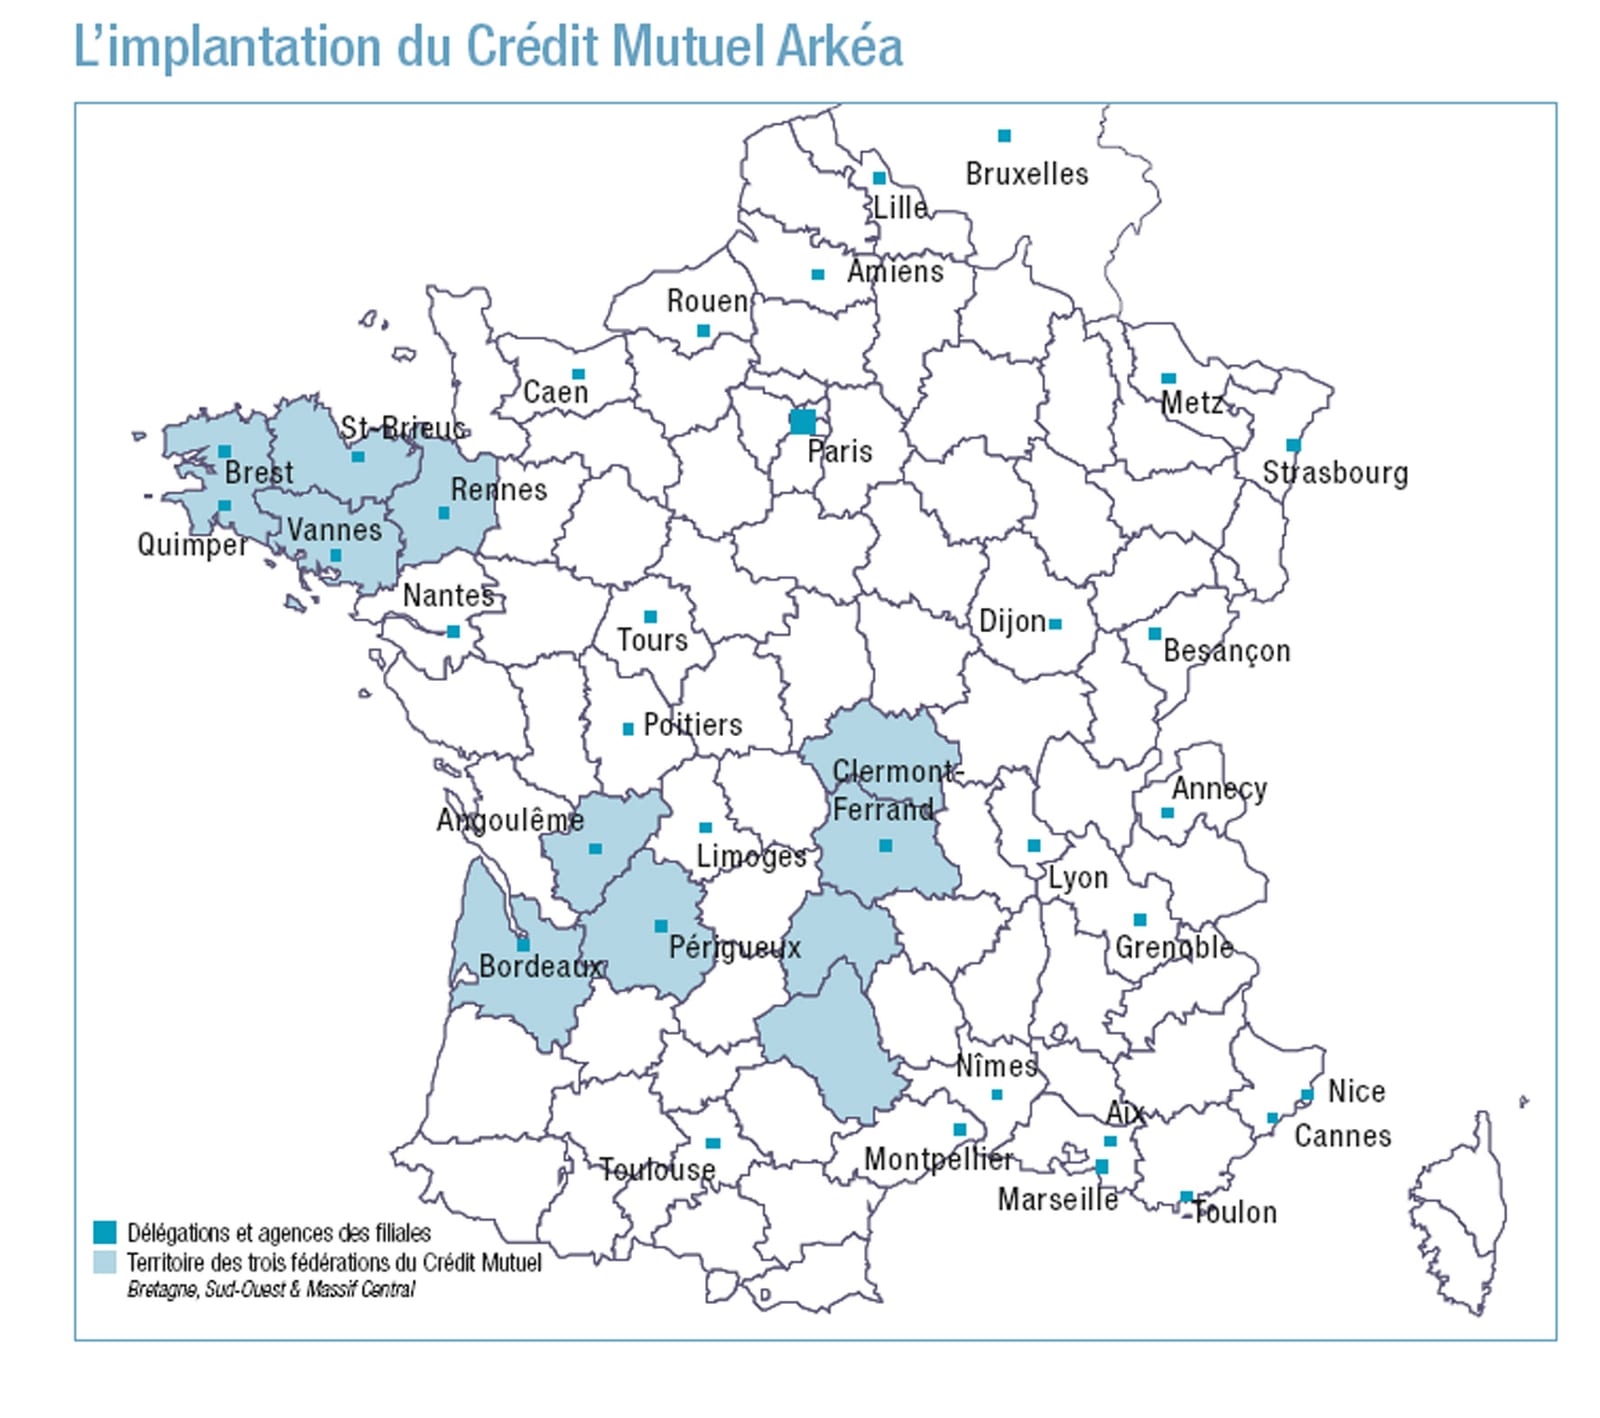
Hackers pull off $133 million French bank heist via service provider

The French cooperative banking group Credit Mutuel Arkea has confirmed it was the target of a sophisticated cyberattack that resulted in unauthorized financial transactions. While the bank has not officially verified the exact figure, independent investigators have estimated the total loss at approximately 118 million euros, or 133 million dollars. The incident, which came to light following…