
LIVE · cybersecurity feed
Live wire
vulnerabilityhigh

Microsoft discloses two actively exploited zero-days among 974 vulnerabilities

Microsoft has released its monthly Patch Tuesday security update, addressing a record 974 vulnerabilities across its product suite. This extensive update includes fixes for two actively exploited zero-day vulnerabilities, CVE-2026-81963 and CVE-2026-85880, both of which allow for privilege escalation and have a CVSS rating of 7.8.

ZeroDay News ·

Source: CyberScoop

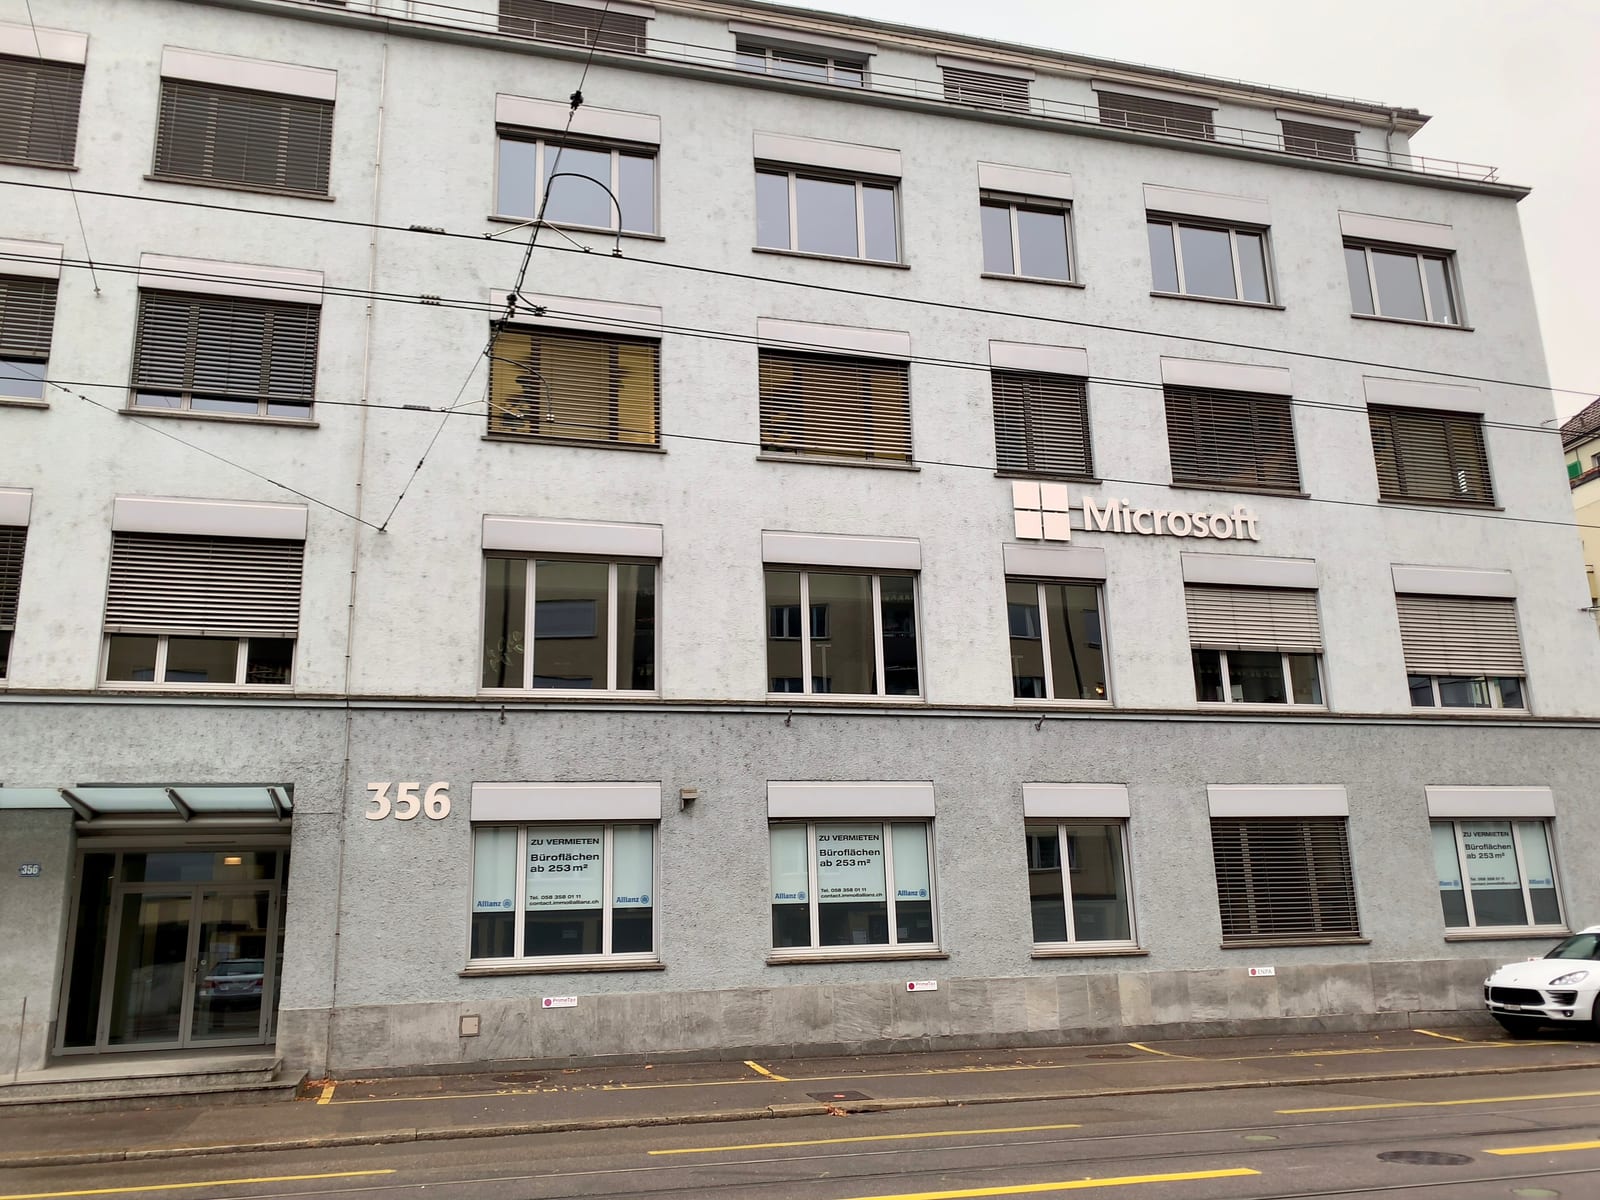
Photo: Ank Kumar (CC BY-SA 4.0) via Wikimedia Commons

Microsoft has released its monthly Patch Tuesday security update, addressing a record 974 vulnerabilities across its product suite. This extensive update includes fixes for two actively exploited zero-day vulnerabilities, CVE-2026-81963 and CVE-2026-85880, both of which allow for privilege escalation and have a CVSS rating of 7.8.

The vulnerability CVE-2026-81963 impacts the Windows Update Stack, while CVE-2026-85880 affects Windows Advanced Local Procedure Call. These zero-days were being actively exploited prior to Microsoft's disclosure and subsequent patching.

The sheer volume of vulnerabilities disclosed this month marks Microsoft's largest ever, a trend attributed by some researchers to the increasing use of artificial intelligence in vulnerability discovery. Despite this record number of disclosures, there has not been a corresponding surge in actively exploited zero-days.

More than 10% of the defects addressed in this update are rated as critical. The patches span a wide range of Microsoft products, with 723 vulnerabilities found in Windows, 111 in Office, 111 in Office 2016, 62 in SQL, and 22 across various developer tools.

Security experts advise organizations not to be overwhelmed by the total number of vulnerabilities, but rather to prioritize remediation based on their specific risk exposure. The increasing number of disclosed vulnerabilities, particularly with AI assistance, means a larger overall pool of potential issues, but not necessarily a higher number of immediately actionable threats for every organization.

It is crucial for security teams to identify which vulnerabilities are applicable to their systems, assess their exploitability and reachability, and then prioritize patching efforts accordingly. The challenge lies in discerning which vulnerabilities demand immediate attention versus those that can follow a standard deployment cycle.

The full list of vulnerabilities addressed in this month's update is available through Microsoft's Security Response Center.


vulnerabilityzero-day
ShareXLinkedInWhatsAppFacebook

More News

view all →
security

Canadian cybersecurity executive arrested in federal extortion case

A Canadian cybersecurity executive was arrested in Pennsylvania on Thursday, facing federal charges of conspiracy to commit extortion. Edward Dubrovsky, 54, a co-founder and former Chief Operating Officer of CYPFER, a firm specializing in ransomware negotiation, is charged with conspiring to threaten the confidentiality of information for extortion and conspiring to commit Hobbs Act extortion,…

breach

Criminal IP Introduces AITEM as the Next Evolution of Attack Surface Management

AI SPERA, the company behind the cyber threat intelligence platform Criminal IP, has announced AITEM (AI-Powered Threat Exposure Management), an expansion of its Attack Surface Management (ASM) offerings. AITEM aims to move beyond traditional asset discovery to provide a more comprehensive approach to understanding, prioritizing, and responding to security exposures. The platform is scheduled…

ai

AI Is Getting Really Good at Messing With Cybercriminals

Anti-cybercrime initiatives are increasingly deploying artificial intelligence to disrupt scammers by engaging them with lifelike bots, which the criminals mistake for genuine victims. This strategy aims to waste scammers' time and resources while gathering intelligence on their operations.

ransomware

FBI Arrests Ransomware Negotiation Firm Co-Founder in ShinyHunters Probe

The Federal Bureau of Investigation (FBI) has reportedly arrested Edward Dubrovsky, a co-founder of the ransomware negotiation firm Cypfer and currently associated with CyberSteward. The arrest is said to be part of the ongoing ShinyHunters investigation, specifically in connection with an incident involving FBI job applicant data.

security

Insider Cyber Extortion Plot Against Industrial Firm Lands Engineer in Prison

A former core infrastructure engineer has been sentenced to prison for an attempted cyber extortion plot against an industrial firm. The engineer reportedly deleted administrative accounts and reset hundreds of user passwords, subsequently demanding a ransom of 20 Bitcoin to prevent further disruption to the company's servers.

ai

The Third-Party Agent Problem: Why Security Built for AI You Chose Misses the Agents You Didn't

A new report highlights a significant blind spot in enterprise security architectures concerning the proliferation of third-party AI agents. The forthcoming 2026 State of Agent Security Report indicates that current security models, often designed to protect AI systems directly chosen and deployed by an organization, frequently fail to account for AI capabilities embedded within third-party…



