LIVE · cybersecurity feed
Live wire
How Cloudflare WAF helps protect against phpAfterShell and other critical PHP flawsCVE-2026-114938 · A Technical Guide to Mitigate Java4Shell with TruRisk EliminateCVE-2026-104995 · Dontdream BP Profile Search Vulnerability Listed As Exploited In VulnCheck KEVCVE-2026-54836 · YMC Filter SQL Injection Vulnerability Added to VulnCheck KEVCVE-2026-7542 · Slider Revolution Sensitive Information Exposure Added To VulnCheck KEVCVE-2024-8517 · SPIP External Control Vulnerability CVE-2024-8517 Added To VulnCheck KEVSean Cairncross out as national cyber directorVMware patches vCenter zero-day exploited in attacks since SeptemberASUS warns of critical hard-coded key flaw in Control Center ExpressCVE-2026-123890 · CVE-2026-123890: Critical Authentication Bypass in VMware vCenter
security

Microsoft now automatically installs Windows 11 26H2 on unmanaged devices

Microsoft has initiated the automatic deployment of Windows 11 version 26H2 for unmanaged devices. This transition marks the next phase in the rollout of the update, which was originally released as an enablement package in September 2026. The automatic installation process began on November 18, 2026, targeting systems currently running Windows 11 versions 24H2 and 25H2 that are not under the…

ZeroDay News ·

Source: BleepingComputer

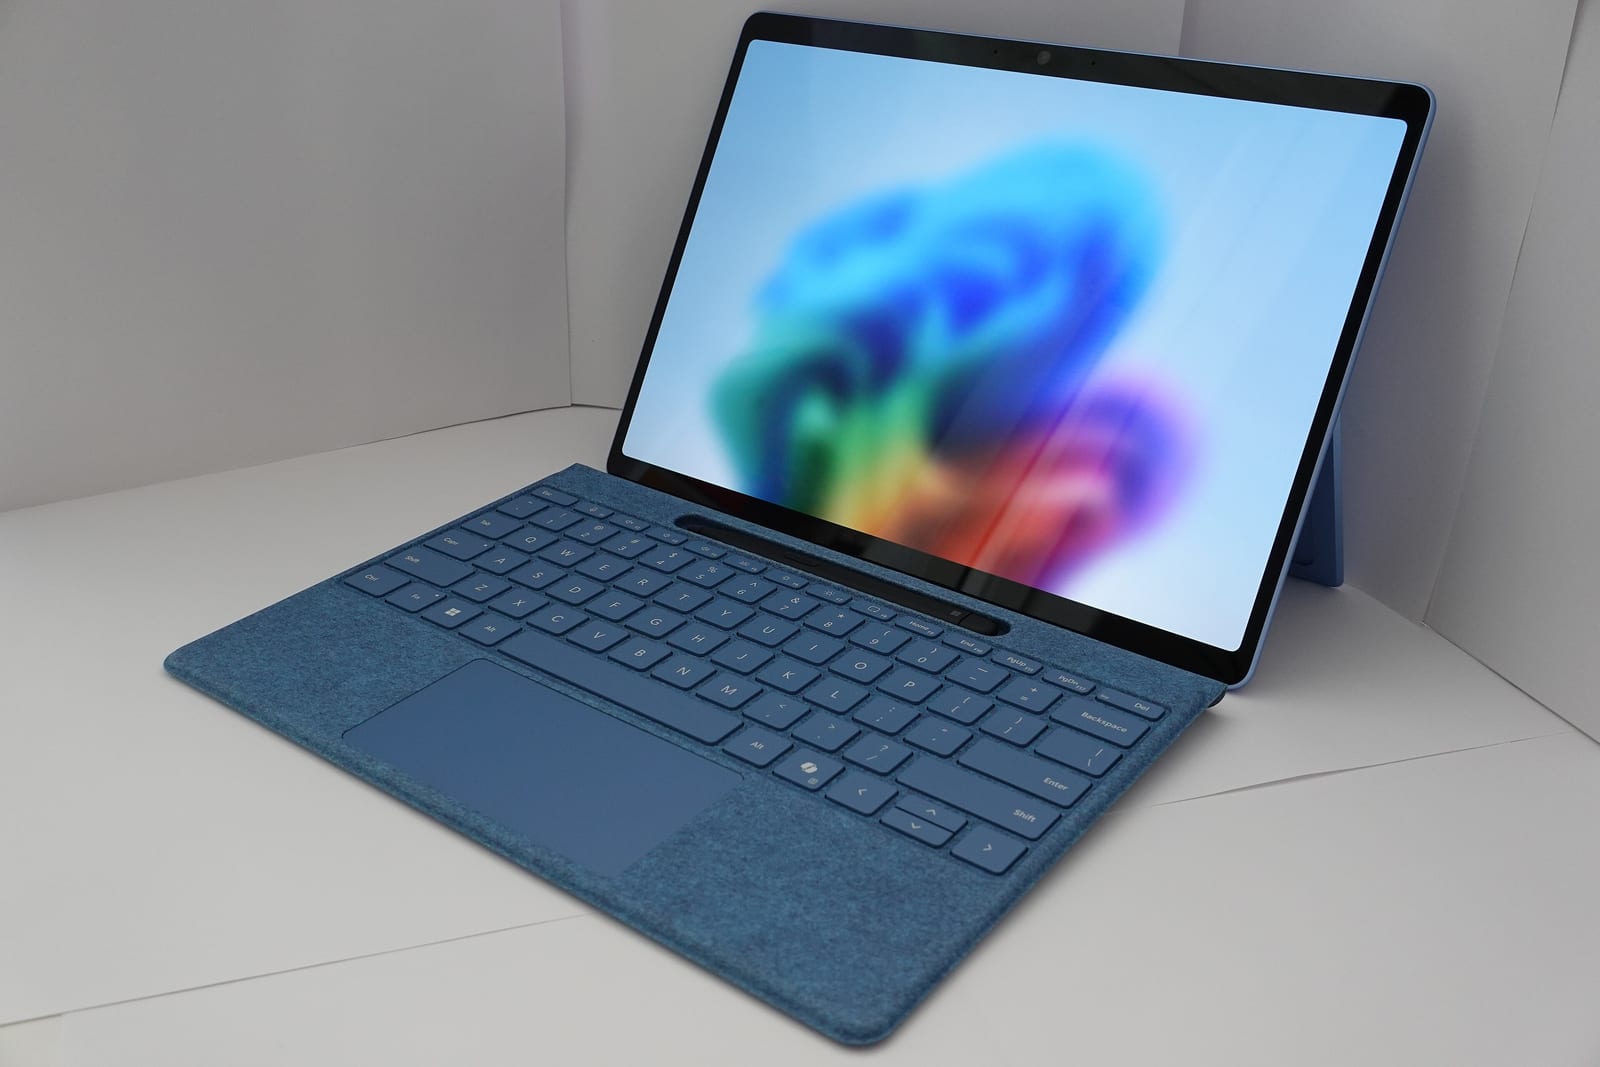
Photo: KK IN HK (CC BY-SA 4.0) via Wikimedia Commons

Microsoft has initiated the automatic deployment of Windows 11 version 26H2 for unmanaged devices. This transition marks the next phase in the rollout of the update, which was originally released as an enablement package in September 2026. The automatic installation process began on November 18, 2026, targeting systems currently running Windows 11 versions 24H2 and 25H2 that are not under the oversight of an IT department.

The company confirmed that this phased rollout is intended to simplify the upgrade process for personal and non-managed business hardware. While the update is now being pushed automatically, users can still choose to trigger the installation manually by navigating to the Windows Update section within the system settings and selecting the check for updates option. To accelerate the process, users may also toggle the setting that prioritizes the delivery of the latest updates as soon as they become available.

Known formally as the Windows 11 2026 Update, version 26H2 integrates features previously introduced in the 24H2 and 25H2 iterations. Microsoft utilizes its existing servicing technology to deliver this update, which is designed to function as a fast installation package. The lifecycle for this version is set to conclude in October 2029, providing users with a support window of less than three years.

Microsoft has emphasized the importance of maintaining current software, warning that devices running unsupported versions of the operating system will cease to receive security updates following a scheduled certificate rotation next year. Users are encouraged to verify their specific version’s support status through the official lifecycle policy search tool or the dedicated Windows lifecycle documentation.

Despite the rollout of this new version, the company is concurrently addressing technical challenges within its ecosystem. Microsoft recently acknowledged that a hotpatch released this month for Windows 11 24H2 and subsequent versions is causing significant issues for users. Specifically, the patch has been linked to problems regarding the installation and launching of both Microsoft Office and various third-party applications.

These recent developments coincide with a series of stability concerns that have affected the Windows platform in recent weeks. Microsoft has had to issue emergency updates to resolve activation failures and has been managing reports of various bugs following the release of the KB5132057 update, which included a wide array of fixes and changes. As the 26H2 rollout continues to expand, the company maintains that it is monitoring device eligibility and system performance to ensure a stable transition for the broader user base.


ShareXLinkedInWhatsAppFacebook

More News

view all →
patch

PHP 8.6: Things are gonna get a lot more strict around here

The PHP development team has officially released PHP 8.6, marking the latest iteration of the widely used server-side scripting language. This release arrives following a turbulent period for the platform, which has faced a surge of security vulnerabilities since October. These flaws, which allowed unauthenticated attackers to trigger remote code execution (RCE) or crash PHP workers,…

security

4 Best XRP Lending Platforms Compared by Security, LTV, and Speed

A recent comparative analysis has evaluated four prominent platforms facilitating XRP lending, focusing on the trade-offs between security protocols, loan-to-value (LTV) ratios, and transaction speeds. The review examines CoinRabbit, Arch, Nexo, and Coinbase, providing a technical overview of how these services manage collateralized digital asset lending.

CVE-2026-23871

CVE-2026-23871: WhatsApp Bug Helped Scammers Make Messages Look Legitimate

WhatsApp has released security updates addressing three vulnerabilities, one of which was actively exploited in a scam campaign designed to increase the perceived legitimacy of fraudulent messages. The company identified this specific flaw, tracked as CVE-2026-23871, while investigating and disrupting an ongoing fraud operation.

cloud

Dialing for Data: Inside the Com’s High-Profile Heists

Security researchers have identified a persistent and evolving campaign of vishing-led cyberattacks targeting data-intensive industries across the United States, the United Kingdom, and Australia. Since August 2026, a network of threat actors associated with the Com collective has conducted a series of data theft and extortion operations. These attacks primarily target the financial,…

phishing

Visa, Mastercard theft included info useful for phishing, but not draining bank accounts, say researchers

Visa, Mastercard, and JPMorgan Chase have confirmed they are investigating data breaches involving third-party service providers. The incidents came to light after a ransomware and extortion group known as n0n claimed responsibility for the thefts and began publishing samples of the exfiltrated data to pressure the financial institutions.

zero-day

China's 'Armory Castle' Lays Siege to VMware vCenter Zero-Day

A China-nexus threat actor identified as Armory Castle has been linked to the exploitation of a zero-day vulnerability affecting VMware vCenter. The activity was observed during the most recent cycle of security updates for the platform, suggesting the group maintained access to the vulnerability while the vendor was actively patching other known flaws in the software.



