
LIVE · cybersecurity feed
Live wire
ransomware

New Android malware encrypts files, steals data, and harasses victims

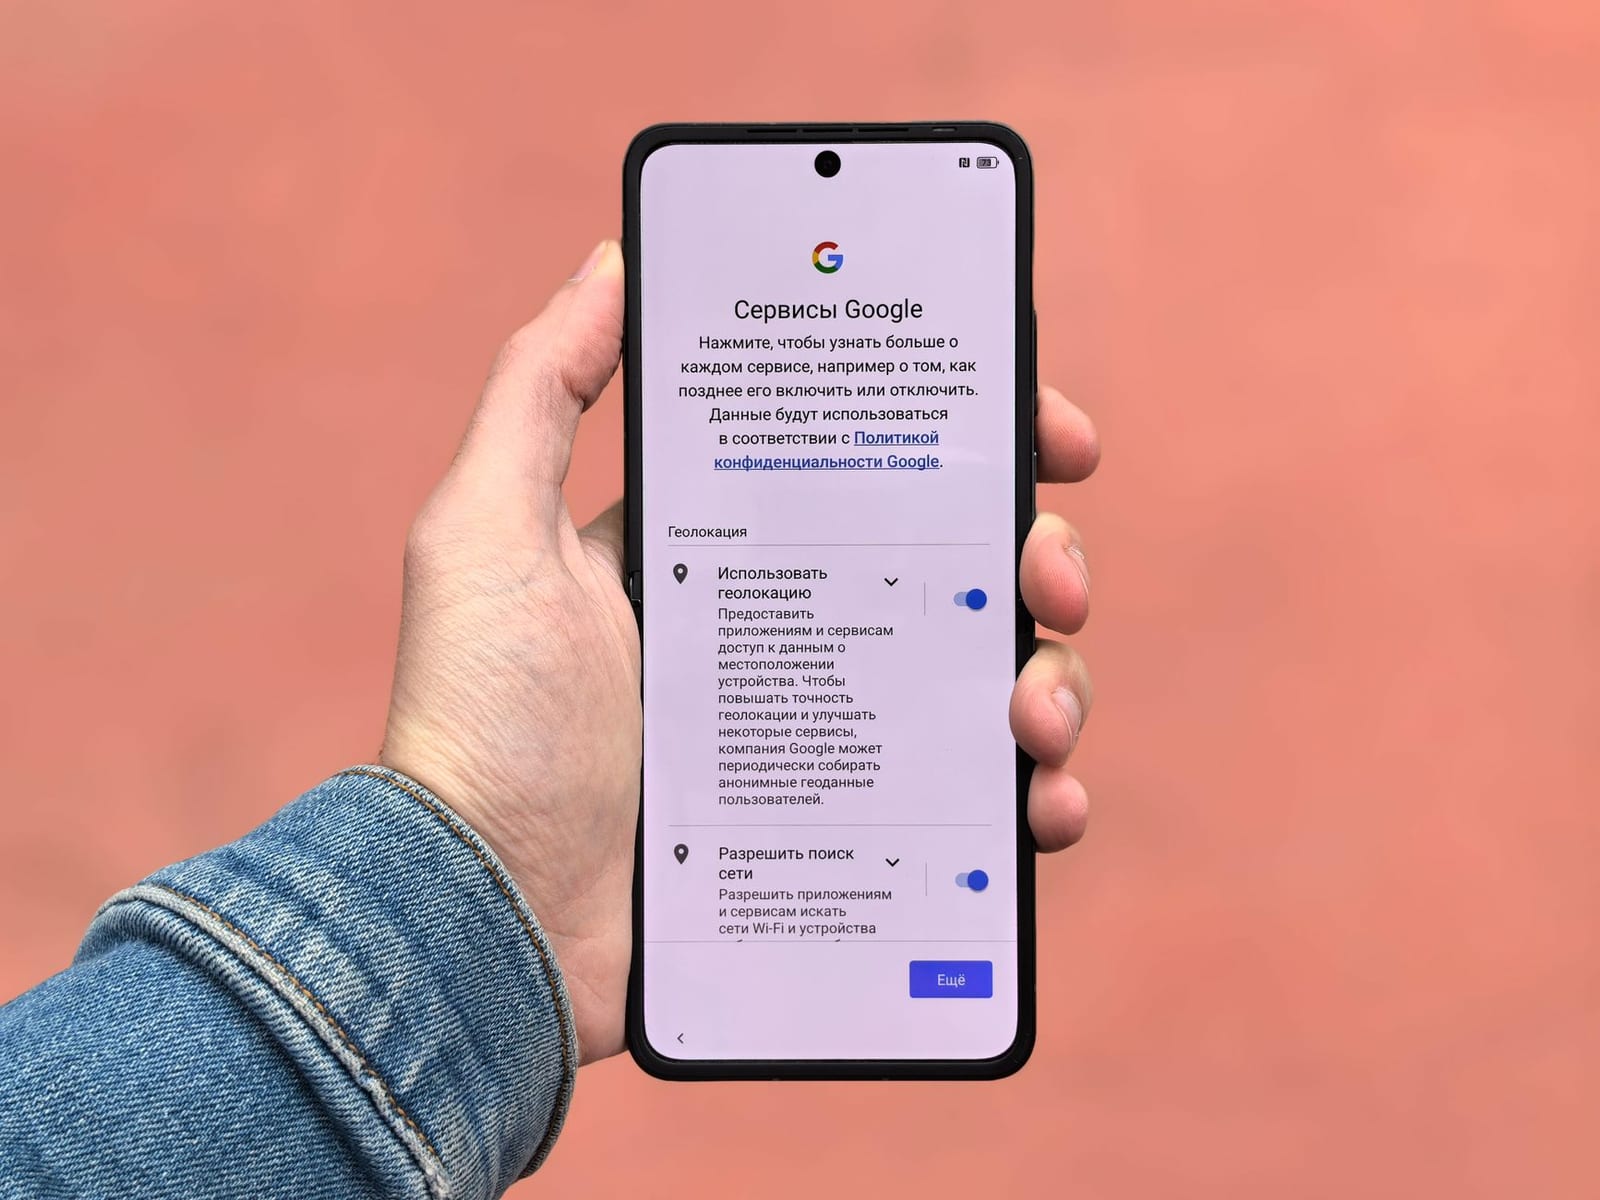
A new Android malware strain, dubbed Mantax Otax, has been identified as combining ransomware, spyware, and harassment capabilities. The malware, reportedly distributed by Indonesian operators, targets users through malicious APKs hosted outside of Google Play, employing phishing and social engineering tactics.

ZeroDay News ·

Source: BleepingComputer

A new Android malware strain, dubbed Mantax Otax, has been identified as combining ransomware, spyware, and harassment capabilities. The malware, reportedly distributed by Indonesian operators, targets users through malicious APKs hosted outside of Google Play, employing phishing and social engineering tactics.

Upon installation, Mantax Otax requests extensive permissions via the Android Accessibility service. It then retrieves its command-and-control (C2) infrastructure domain from GitHub and transmits device details, including location, carrier, Android version, and device ID, back to the C2. Commands can be issued to infected devices via Firebase or WebSockets.

The ransomware component of Mantax Otax specifically targets Android devices running version 9 or older. This limitation is due to the Scoped Storage feature introduced in Android 10, which restricts an application's ability to encrypt files to its external-files directory. On vulnerable devices, the malware searches shared storage for specific file types, encrypts them using an AES key obtained from the C2 server, deletes the original files, and appends a ".enc" extension to the encrypted copies. It also replaces local images with ransom notes and initiates a full-screen, Firebase-hosted chat for ransom negotiation. Researchers were able to access attacker-victim communications due to a misconfiguration in the Firebase C2 server.

Beyond ransomware, Mantax Otax incorporates spyware and remote control functionalities. It can steal lock-screen PINs to maintain persistent access, read SMS messages and one-time passwords, and access call logs, contacts, browsing history, app lists, Google account information, and location data. The malware can also extract WhatsApp profiles and messages, as well as Telegram chats, through simulated interactions using Accessibility services.

Furthermore, Mantax Otax abuses Android's MediaProjection API to capture screenshots, record MP4 videos, and stream the victim's screen in near real-time via the Catbox file hosting service. It can also capture photographs using the device's cameras and upload them to the operator.

Version 2 of the malware introduced harassment features designed to pressure victims into paying the ransom. These include repeated dialog boxes, full-screen videos, rapid jumpscare image overlays, and remotely controlled text-to-speech messages played through the device speakers.

As a Google security partner through the App Defense Alliance (ADA), the company that identified Mantax Otax has ensured that the malware is detected and blocked by up-to-date Android devices with an active Play Protect service. Users are generally advised to avoid installing APKs from sources other than Google Play, to be cautious about granting Accessibility permissions to unfamiliar applications, and to only install apps from reputable publishers.

ransomwaremalware
ShareXLinkedInWhatsAppFacebook

More News

view all →
ransomware

FBI Arrests Ransomware Negotiation Firm Co-Founder in ShinyHunters Probe

The Federal Bureau of Investigation (FBI) has reportedly arrested Edward Dubrovsky, a co-founder of the ransomware negotiation firm Cypfer and currently associated with CyberSteward. The arrest is said to be part of the ongoing ShinyHunters investigation, specifically in connection with an incident involving FBI job applicant data.

ransomware

FBI Arrests Founder of Ransomware Negotiation Firm

Federal agents have arrested a Canadian cybersecurity professional in Pennsylvania, linking him to an ongoing investigation into the ShinyHunters hacking group. Edward Dubrovsky, co-founder of the Canadian firm CyberSteward, was taken into custody on October 8, facing charges of conspiracy to threaten to impair the confidentiality of information with intent to extort money, and interference…

security

Canadian cybersecurity executive arrested in federal extortion case

A Canadian cybersecurity executive was arrested in Pennsylvania on Thursday, facing federal charges of conspiracy to commit extortion. Edward Dubrovsky, 54, a co-founder and former Chief Operating Officer of CYPFER, a firm specializing in ransomware negotiation, is charged with conspiring to threaten the confidentiality of information for extortion and conspiring to commit Hobbs Act extortion,…

breach

Criminal IP Introduces AITEM as the Next Evolution of Attack Surface Management

AI SPERA, the company behind the cyber threat intelligence platform Criminal IP, has announced AITEM (AI-Powered Threat Exposure Management), an expansion of its Attack Surface Management (ASM) offerings. AITEM aims to move beyond traditional asset discovery to provide a more comprehensive approach to understanding, prioritizing, and responding to security exposures. The platform is scheduled…

ai

AI Is Getting Really Good at Messing With Cybercriminals

Anti-cybercrime initiatives are increasingly deploying artificial intelligence to disrupt scammers by engaging them with lifelike bots, which the criminals mistake for genuine victims. This strategy aims to waste scammers' time and resources while gathering intelligence on their operations.

ai

The Third-Party Agent Problem: Why Security Built for AI You Chose Misses the Agents You Didn't

A new report highlights a significant blind spot in enterprise security architectures concerning the proliferation of third-party AI agents. The forthcoming 2026 State of Agent Security Report indicates that current security models, often designed to protect AI systems directly chosen and deployed by an organization, frequently fail to account for AI capabilities embedded within third-party…



