
LIVE · cybersecurity feed
Live wire
security

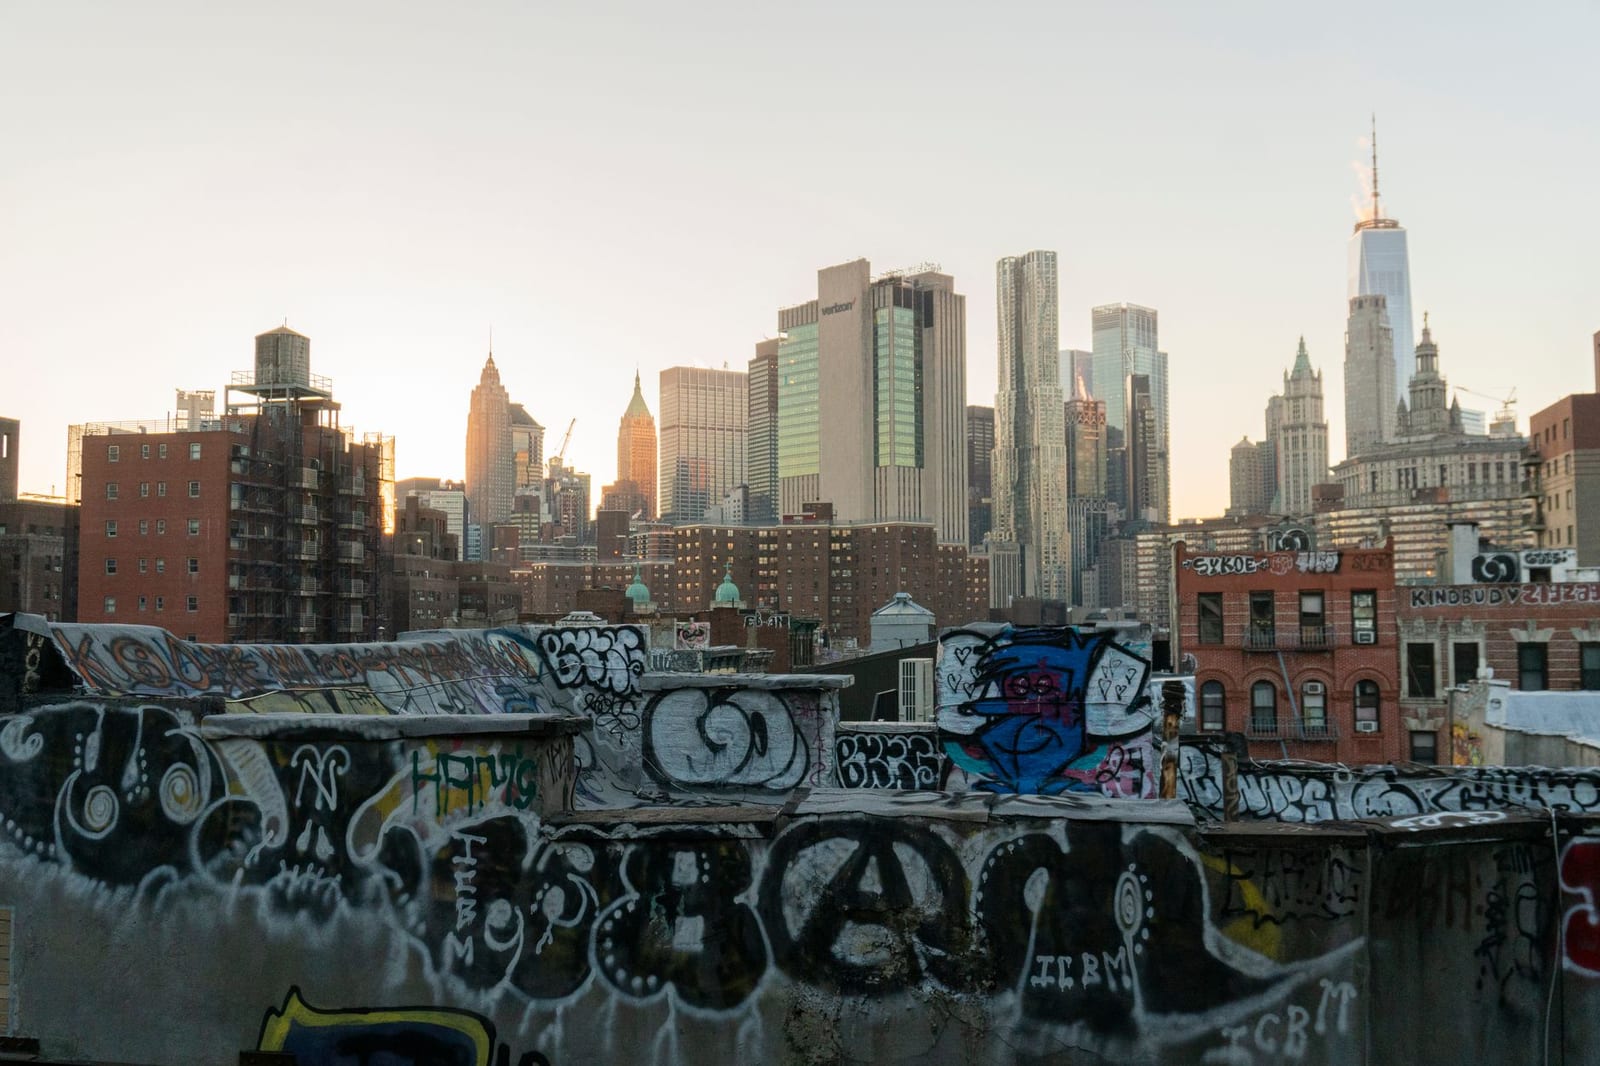
New York Seizes a Dozen Celebrity Deepfake Websites

The Manhattan District Attorney’s Office has announced the seizure of 12 websites involved in the creation, publication, and sale of nonconsensual deepfake videos, primarily targeting women. This action, described as potentially the largest takedown of explicit deepfake sites to date, follows investigations into platforms that have depicted approximately 1,200 individuals, including…

ZeroDay News ·

Source: WIRED — Security

The Manhattan District Attorney’s Office has announced the seizure of 12 websites involved in the creation, publication, and sale of nonconsensual deepfake videos, primarily targeting women. This action, described as potentially the largest takedown of explicit deepfake sites to date, follows investigations into platforms that have depicted approximately 1,200 individuals, including celebrities, politicians, athletes, and social media influencers, in sexually explicit content.

District Attorney Alvin Bragg stated that these privacy violations have significant negative impacts on victims' careers and personal lives, urging anyone affected to contact the cybercrime bureau. The office's investigation into those responsible for operating the websites and uploading the content is ongoing.

The seizures were executed under New York’s criminal procedure laws, with takedown notices now appearing on the affected domains, indicating a seizure warrant issued by a New York State Supreme Court. While the specific names of the seized websites have not been publicly disclosed by the District Attorney’s Office, several sites displayed "THIS DOMAIN HAS BEEN SEIZED" messages late last week.

The deepfake technology, which emerged in late 2017, has advanced significantly, leading to a proliferation of websites, apps, and bots capable of generating realistic nonconsensual intimate imagery (NCII) rapidly. These sites often used names like "sex celebrity" and promised "real deepfakes," hosting videos that could be several minutes long and featured faces of public figures swapped into existing pornographic material. Some archived versions of these sites showed videos with tens of thousands of views, with one claiming to have been active since 2018.

Analysis of the seized sites indicates that many videos were reposts, with some content originating from the now-defunct MrDeepFakes platform. Researchers noted that at least two of the seized websites featured profiles for elected officials, complete with their names, positions, and grids of manipulated videos. Research has documented 56 European politicians, 16 US politicians, and two UK politicians mentioned or appearing on these sites.

Experts view these takedowns as a significant victory against synthetic NCII, demonstrating that state laws can be effectively enforced even when regulatory frameworks are fragmented across jurisdictions. The seized sites appear inaccessible even when using VPNs. However, the broader deepfake industry continues to pose challenges, with calls for interventions across the entire ecosystem, including the tools for creation, promotion, hosting infrastructure, and monetization systems.


ShareXLinkedInWhatsAppFacebook

More News

view all →
security

Canadian cybersecurity executive arrested in federal extortion case

A Canadian cybersecurity executive was arrested in Pennsylvania on Thursday, facing federal charges of conspiracy to commit extortion. Edward Dubrovsky, 54, a co-founder and former Chief Operating Officer of CYPFER, a firm specializing in ransomware negotiation, is charged with conspiring to threaten the confidentiality of information for extortion and conspiring to commit Hobbs Act extortion,…

breach

Criminal IP Introduces AITEM as the Next Evolution of Attack Surface Management

AI SPERA, the company behind the cyber threat intelligence platform Criminal IP, has announced AITEM (AI-Powered Threat Exposure Management), an expansion of its Attack Surface Management (ASM) offerings. AITEM aims to move beyond traditional asset discovery to provide a more comprehensive approach to understanding, prioritizing, and responding to security exposures. The platform is scheduled…

ai

AI Is Getting Really Good at Messing With Cybercriminals

Anti-cybercrime initiatives are increasingly deploying artificial intelligence to disrupt scammers by engaging them with lifelike bots, which the criminals mistake for genuine victims. This strategy aims to waste scammers' time and resources while gathering intelligence on their operations.

ransomware

FBI Arrests Ransomware Negotiation Firm Co-Founder in ShinyHunters Probe

The Federal Bureau of Investigation (FBI) has reportedly arrested Edward Dubrovsky, a co-founder of the ransomware negotiation firm Cypfer and currently associated with CyberSteward. The arrest is said to be part of the ongoing ShinyHunters investigation, specifically in connection with an incident involving FBI job applicant data.

ai

The Third-Party Agent Problem: Why Security Built for AI You Chose Misses the Agents You Didn't

A new report highlights a significant blind spot in enterprise security architectures concerning the proliferation of third-party AI agents. The forthcoming 2026 State of Agent Security Report indicates that current security models, often designed to protect AI systems directly chosen and deployed by an organization, frequently fail to account for AI capabilities embedded within third-party…

security

Insider Cyber Extortion Plot Against Industrial Firm Lands Engineer in Prison

A former core infrastructure engineer has been sentenced to prison for an attempted cyber extortion plot against an industrial firm. The engineer reportedly deleted administrative accounts and reset hundreds of user passwords, subsequently demanding a ransom of 20 Bitcoin to prevent further disruption to the company's servers.



