LIVE · cybersecurity feed
Live wire
CVE-2026-20320 · Cisco BroadWorks and Openwave Flaws Actively Exploited Despite Available PatchesEU cyber scores look healthy, but 45% of surveyed IT providers take months to patchCVE-2026-120043 · SliceWP Affiliate Program Suite SQL Injection Exploited Before DisclosureCVE-2026-86596 · CLavaque s2Member Improper Control of Generation of Code Flaw Exploited Upon DisclosureCVE-2026-124194 · Microsoft Office Outlook Vulnerability Exploited Same Day as DisclosureCVE-2026-114432 · Rocklobster Contact Form 7 Flaw Exploited Same Day as DisclosureCVE-2026-123751 · Revmakx WP Duplicate Flaw Exploited Before CVE PublicationDetecting sleeper agents hiding in AI model neuronsNovember Patch Tuesday: An Overflowing Cornucopia of CVEsU.S. urges critical infrastructure orgs to secure refrigeration systems ASAP after EU supermarket and blood bank attacks
patch

Red Hat OpenShift 5 brings autonomous troubleshooting to hybrid clouds

Red Hat has announced the general availability of OpenShift 5, an update to its hybrid cloud application platform that introduces autonomous troubleshooting and enhanced security features. Designed to operate across data centers, cloud environments, and disconnected or edge deployments, the platform allows IT teams to manage virtual machines, containerized workloads, and artificial…

ZeroDay News ·

Source: Help Net Security

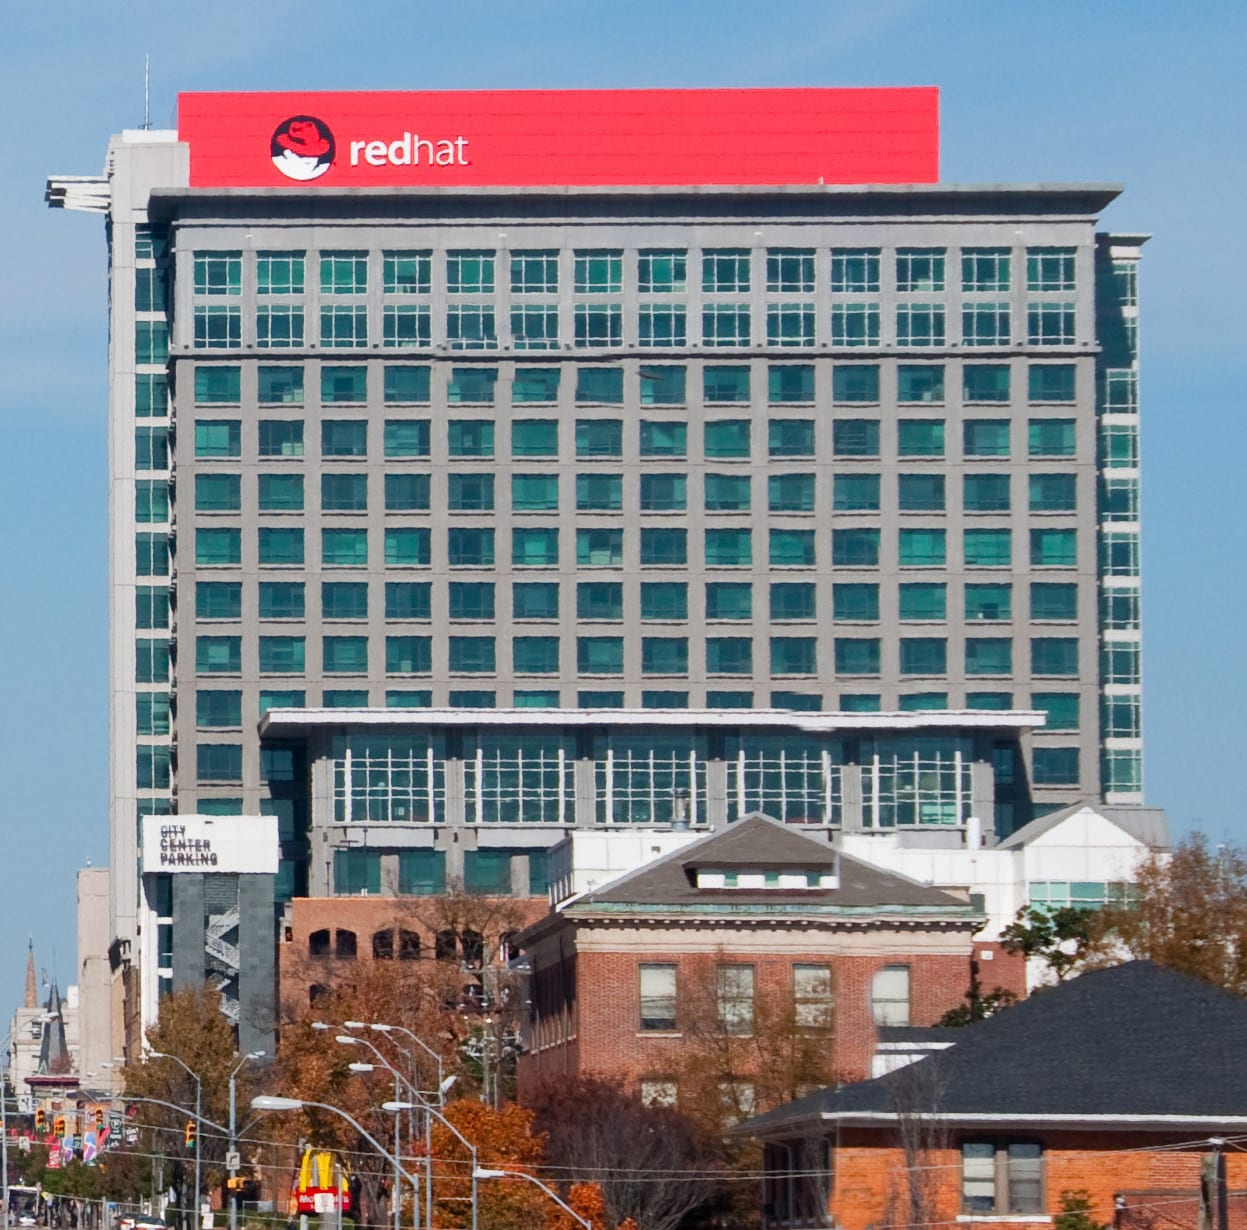
Photo: Bz3rk (CC BY-SA 3.0) via Wikimedia Commons

Red Hat has announced the general availability of OpenShift 5, an update to its hybrid cloud application platform that introduces autonomous troubleshooting and enhanced security features. Designed to operate across data centers, cloud environments, and disconnected or edge deployments, the platform allows IT teams to manage virtual machines, containerized workloads, and artificial intelligence applications within a unified environment. The release is available as an in-place update for organizations currently running Red Hat OpenShift 4.

A primary focus of this release is the integration of Red Hat OpenShift Lightspeed, which has been upgraded from a conversational assistant to an autonomous agent. This tool is intended to reduce the manual burden of cluster maintenance by utilizing natural language interaction and AI-driven reasoning loops. The platform provides automated root-cause analysis, allowing administrators to isolate anomalies and examine log streams directly within the management console.

To mitigate the risks associated with platform maintenance, OpenShift 5 includes automated pre-flight readiness checks. These tools analyze API compatibility and perform risk assessments on optional operators before an update is executed. Red Hat confirms that these features are designed to facilitate zero-downtime maintenance windows and provide context-aware guidance to operations teams.

Security improvements in this release center on zero-trust principles and long-term data protection. Red Hat has implemented hardened multi-tenancy capabilities, which are intended to support sovereign and highly regulated deployments. Furthermore, the platform now includes support for post-quantum cryptography (PQC) for control plane communications, a measure aimed at safeguarding infrastructure against future decryption threats posed by quantum computing.

The platform also introduces support for the Model Context Protocol (MCP), enabling better integration with AI interfaces. By combining these AI-driven tools with existing features like Red Hat OpenShift Virtualization and GitOps pipelines, the vendor aims to provide a more efficient way to manage hardware resources, including automated GPU compute slicing for AI inference tasks.

Red Hat has committed to a five-year predictable lifecycle for this version, which the company states is intended to provide stability for long-term IT investments. This extended support window is designed to assist organizations that must balance the demands of legacy virtual machine workloads with the rapid scaling requirements of modern AI-driven infrastructure.

The platform is specifically marketed toward environments with strict regulatory or connectivity constraints. By enhancing native support for disconnected deployments and automating certificate lifecycle management, the release aims to satisfy the requirements of sectors such as telecommunications, where consistent, carrier-grade foundations are necessary for network innovation and automated service delivery.

patchaicloud
ShareXLinkedInWhatsAppFacebook

More News

view all →
vulnerability

Microsoft Fixes 1235 Flaws in Another Record Patch Tuesday

Microsoft has released its November security updates, addressing a total of 1,235 vulnerabilities across its product ecosystem. This release marks the fourth time in 2026 that the company has set a new record for the number of patches issued in a single month, following similar milestones in July, September, and October.

CVE-2026-20320high

Cisco BroadWorks and Openwave Flaws Actively Exploited Despite Available Patches

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added two security vulnerabilities affecting Cisco BroadWorks and the Openwave Messaging Webtop Media Transcoder to its Known Exploited Vulnerabilities (KEV) catalog. The agency’s inclusion of these flaws indicates that they are currently being leveraged in active, real-world attacks. Organizations utilizing these platforms…

vulnerabilitycritical

EU cyber scores look healthy, but 45% of surveyed IT providers take months to patch

The European Union’s cybersecurity landscape presents a significant disconnect between high-level national policy scores and the operational realities of service providers, according to the 2026 assessment released by the European Union Agency for Cybersecurity (ENISA). While the agency’s revised EU Cybersecurity Index reports an average score of 71.53 out of 100 across member states, a…

ai

Druva helps restore AI agents without rolling back entire environments

Druva has announced a new suite of capabilities under its AI Resilience initiative, specifically designed to facilitate the recovery of AI agents without the need to revert entire digital environments. This development addresses the growing operational reliance on AI agents, which are increasingly utilized by a significant majority of Fortune 500 companies. Previously, if an agent was deleted…

ai

Fingerprint trains specialized models to detect distinct fraud types

Fingerprint has introduced a new predictive tool called Fraud Score, designed to help organizations identify and mitigate specific types of fraudulent activity. The service utilizes machine learning to create specialized models that are trained on an individual company’s unique fraud outcomes, rather than relying on a generalized, one-size-fits-all risk score. By combining a client's…

security

A CISO’s guide to trimming waste from a flat security budget

Chief Information Security Officers facing stagnant financial resources are increasingly turning to operational consolidation as a primary strategy for maintaining security posture. Ken Leeser, the CISO at Y Meadows, suggests that a frozen budget should be viewed as an opportunity to audit and simplify an organization's existing security stack rather than a purely negative constraint. This…