LIVE · cybersecurity feed
Live wire
AI found more critical bugs in another widely used technology running 225M websitesCVE-2026-129448 · Apache Roller RCE Flaw CVE-2026-129448 Under Active AttackCognizant and Qualys Redefine AI-Era Managed Security ServiceJava4Shell Vulnerability Allows Remote Attacks on Major Java AppsCVE-2026-114938 · Java4Shell (CVE-2026-114938): Frequently asked questions about OpenJDK remote code execution vulnerabilityCVE-2026-114938 · CVE-2026-114938: Critical vulnerability in OpenJDK JAVACritical Java4Shell flaw allows RCE attacks on major Java applicationsCVE-2026-114938 · How to Find, Mitigate, and Patch the Critical Java4Shell Flaw (CVE-2026-114938) NowCVE-2026-28160 · e4jvikwp VikRentCar Vulnerability Listed As Exploited In VulnCheck KEVCVE-2025-5569 · Ideacms Improper Neutralization Flaw Added To VulnCheck KEV After 514 Days
patch

Trump administration officials size-up a bad stretch for tech

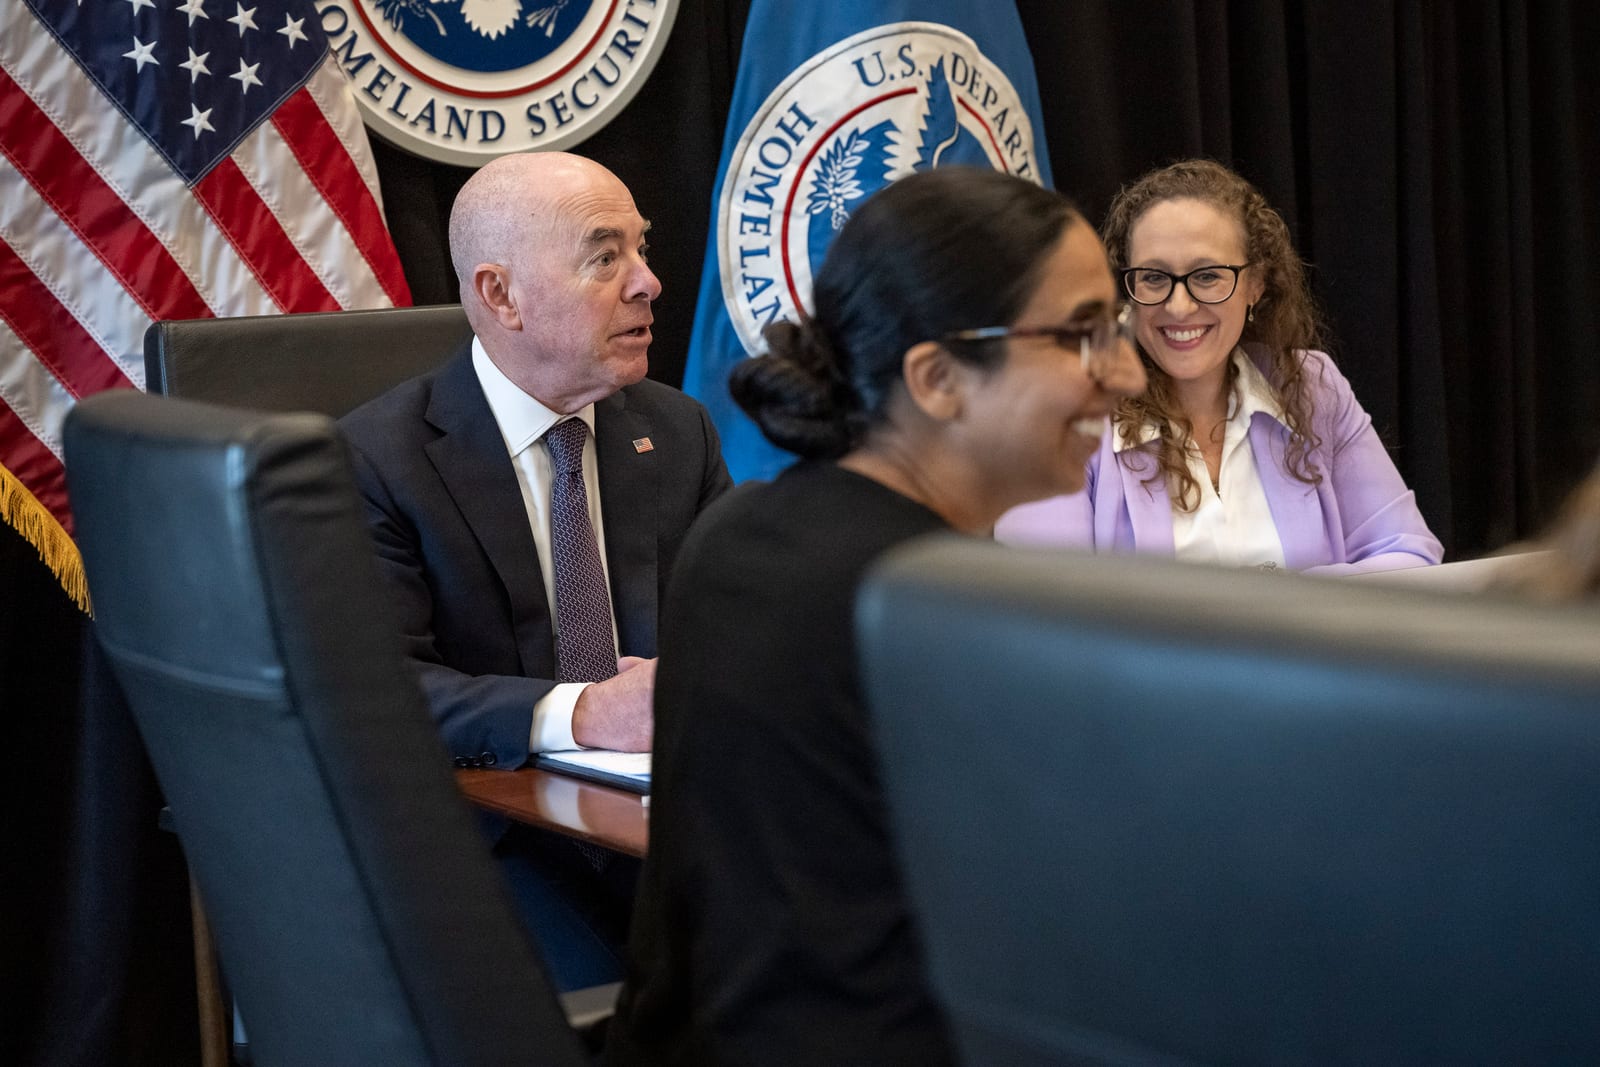
Senior Trump administration officials testified before the House Homeland Security Committee on November 18, 2026, to address a wave of high-profile service disruptions that have affected both public infrastructure and national security agencies over the past ten days. During the hearing, Director of National Intelligence Jay Clayton, Homeland Security Secretary Markwayne Mullin, and FBI…

ZeroDay News ·

Source: The Record

Photo: DHSgov (Public domain) via Wikimedia Commons

Senior Trump administration officials testified before the House Homeland Security Committee on November 18, 2026, to address a wave of high-profile service disruptions that have affected both public infrastructure and national security agencies over the past ten days. During the hearing, Director of National Intelligence Jay Clayton, Homeland Security Secretary Markwayne Mullin, and FBI Deputy Director Christopher Raia collectively rejected the theory that these incidents were the result of a coordinated digital offensive by foreign adversaries.

The recent string of failures includes a global outage affecting Microsoft products, a nationwide ground stop issued by the Federal Aviation Administration, and technical glitches impacting the banking sector and the National Security Agency. These events have prompted significant concern among policymakers and the general public, with many questioning whether the simultaneous nature of the disruptions points to a clandestine attack by a hostile state actor.

FBI Deputy Director Raia confirmed that the bureau’s cyber teams have been involved in investigating these incidents since they began. He stated that, to date, there is no evidence of malicious cyber activity linked to any of the failures. Raia emphasized that the FBI continues to coordinate with the Department of Homeland Security and the Office of the Director of National Intelligence to ensure the findings remain comprehensive and accurate.

Secretary Mullin, who had previously suggested in media appearances that artificial intelligence might have played a role in the disruptions, adopted a more measured tone during his testimony. He expressed a high degree of confidence that the events were not the result of foreign hacking. Mullin announced that the administration intends to initiate discussions with private sector leaders to encourage better communication regarding system upgrades, noting that the current lack of transparency often fuels unnecessary public alarm.

Director Clayton provided technical context for the disruptions, specifically attributing an internal NSA network outage to maintenance work involving PHP. He explained that the broader pattern of failures is largely a byproduct of an environment where the frequency of system patching and upgrades is accelerating. According to Clayton, this increase is driven by rapid advancements in computing and software applications, which necessitate more frequent updates to maintain security and performance.

The intelligence chief highlighted the inherent difficulties of managing modern digital infrastructure, noting that many networks currently rely on a complex, often incompatible mix of equipment spanning multiple decades. He argued that while these legacy systems make the integration of new patches and upgrades inherently challenging, the process is a necessary evolution. Clayton maintained that the country is currently undergoing a transition that will ultimately result in more resilient infrastructure.

Despite the administration’s unified stance, the messaging has faced scrutiny due to earlier, conflicting explanations provided by officials. The administration’s efforts to reassure the public were previously complicated by varying accounts regarding the cause of the four-hour FAA ground stop. Officials are now attempting to pivot toward a narrative that emphasizes the necessity of system modernization and the need for better industry-wide communication protocols.

Looking forward, the administration acknowledged that malicious actors are increasingly leveraging advanced computing to scan for and exploit system vulnerabilities. Clayton noted that sophisticated financial institutions are already utilizing enhanced defensive capabilities to counter these automated threats. The administration’s stated goal is to leverage similar technological advancements to secure domestic systems, even as the country navigates the immediate, disruptive phase of widespread infrastructure upgrades.


patch
ShareXLinkedInWhatsAppFacebook

More News

view all →
vulnerabilitycritical

AI found more critical bugs in another widely used technology running 225M websites

F5 has issued an emergency security update for the open-source NGINX web server to address 10 newly discovered vulnerabilities. These flaws affect a significant portion of the internet, as NGINX currently powers approximately 225 million websites. The vendor has urged all administrators to upgrade their systems to version 1.31.9 immediately to mitigate the risks.

vulnerability

Consensus mounts that tech outages were fueled by patching of AI-discovered vulnerabilities

A series of significant technical outages affecting aviation, banking, and communications infrastructure over the past week has prompted a federal investigation into the stability of critical systems. While initial concerns focused on the possibility of coordinated cyberattacks, officials from the Trump administration, including Secretary of Homeland Security Markwayne Mullin, Director of…

CVE-2026-129448critical

Apache Roller RCE Flaw CVE-2026-129448 Under Active Attack

The Apache Software Foundation has issued an urgent security advisory regarding a critical remote code execution (RCE) vulnerability in Apache Roller, an open-source Java-based blogging platform. The flaw, assigned the identifier CVE-2026-129448 and carrying a maximum CVSS severity score of 9.8, is currently being exploited in the wild.

ai

Coinbase blocks $4.7 million in transfers to Elon Musk deepfake scam

Coinbase successfully intercepted $4.7 million in cryptocurrency transfers associated with a sophisticated deepfake scam targeting users during a high-profile Tesla event. The incident occurred during a demonstration of Tesla's flying car technology, which was broadcast via a fraudulent YouTube livestream. The stream, which drew an audience of over 500,000 viewers, utilized AI-generated video…

ai

Strike Graph Launches Integration AI to Automate Continuous Compliance Evidence Using Any Existing Tool

Strike Graph has announced the launch of a new agentic AI solution designed to automate the collection of compliance evidence across an organization’s existing software stack. By leveraging direct API integrations, the platform aims to streamline the evidence-gathering process, mapping data points to more than 30 different compliance frameworks simultaneously to eliminate redundant manual…

ai

Judge signs off on sale of Spirit Airlines’ data to Google

A federal bankruptcy judge in New York has officially approved the sale of Spirit Airlines’ corporate data to Google, a transaction valued at $10 million. The deal, which follows the airline’s cessation of operations in May, involves the transfer of a massive dataset to the tech giant for the stated purpose of training artificial intelligence models. The repository includes approximately 100…


