CVSS—
Severityhigh
Weakness—
EPSS12.7%96.0th percentile
Exploited3 KEV sources
Ransomware useUnknown
Federal fix dueMay 2, 2022
patch window
Called exploited 21 days after disclosure.
Measured from the CVE publication date to the earliest of 3 KEV catalogues that list it.
The life of this vulnerability
- CVE published
- First KEV listing21d
- Last KEV listing25d
- Last sighting10mo
Gaps are compressed to equal steps. The elapsed time is printed under each.
Which catalogues call it exploited
- CISA KEVUS federallisted Apr 11, 2022
- EUVDENISA, European Unionlisted Apr 11, 2022
- VulnCheck KEVcommercial researchlisted Mar 17, 2022
- CIRCLaggregator, mirrors the abovelisted Apr 11, 2022, not counted
Sources3 of 3
Listings differ by25 d
Strongest claimconfirmed
3 catalogues list it. CIRCL aggregates the others and is shown but not counted.
Public exploitation evidence
- reported exploitationhub.dragos.com/hubfs/312-Year-in-Review/2022/Dragos_Year-In-
- reported exploitationwww.prio-n.com/a-year-in-review-2022-100-vulnerabilities-you
- reported exploitationwww.cisa.gov/sites/default/files/feeds/known_exploited_vulne
- reported exploitationarstechnica.com/information-technology/2022/04/watchguard-fa
4 public reports collected from VulnCheck and CIRCL, first on Mar 17, 2022. Each links to its original source. We have not verified them.
Description
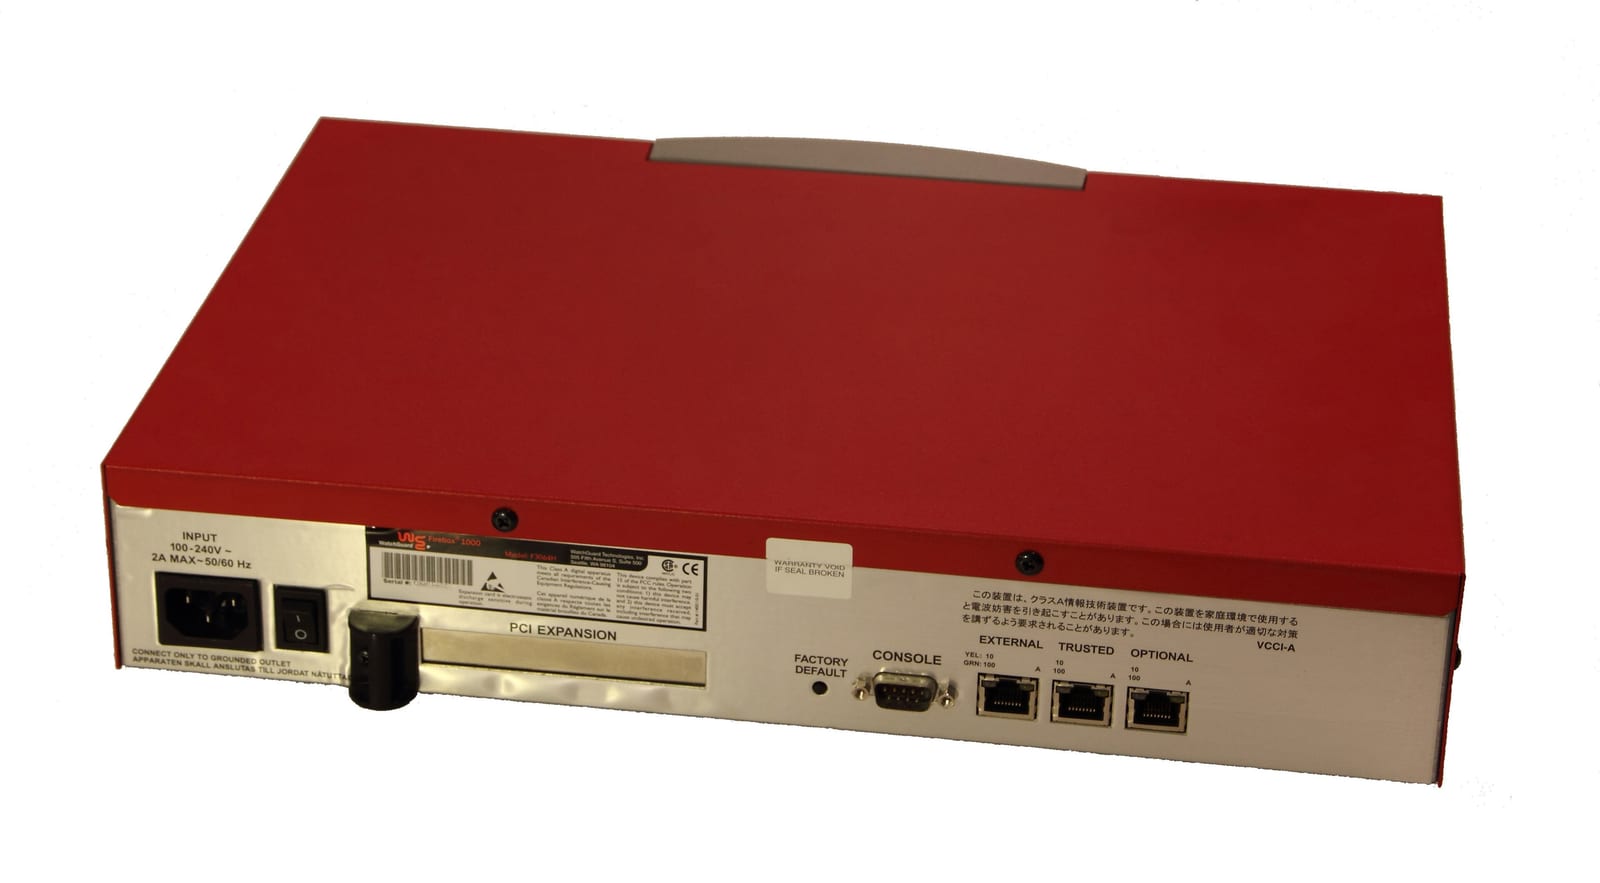
WatchGuard Firebox and XTM appliances allow a remote attacker with unprivileged credentials to access the system with a privileged management session via exposed management access.
Required action (CISA)
Apply updates per vendor instructions.