
LIVE · cybersecurity feed
Live wire
CVE-2025-14733critical

CISA: WatchGuard RCE flaw now exploited in ransomware attacks

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has confirmed that a critical remote code execution (RCE) vulnerability in WatchGuard Firebox firewalls, tracked as CVE-2025-14733, is now being exploited by ransomware groups. CISA added this flaw to its Known Exploited Vulnerabilities (KEV) catalog in December, at which point it was already being actively exploited.

ZeroDay News ·

Source: BleepingComputer

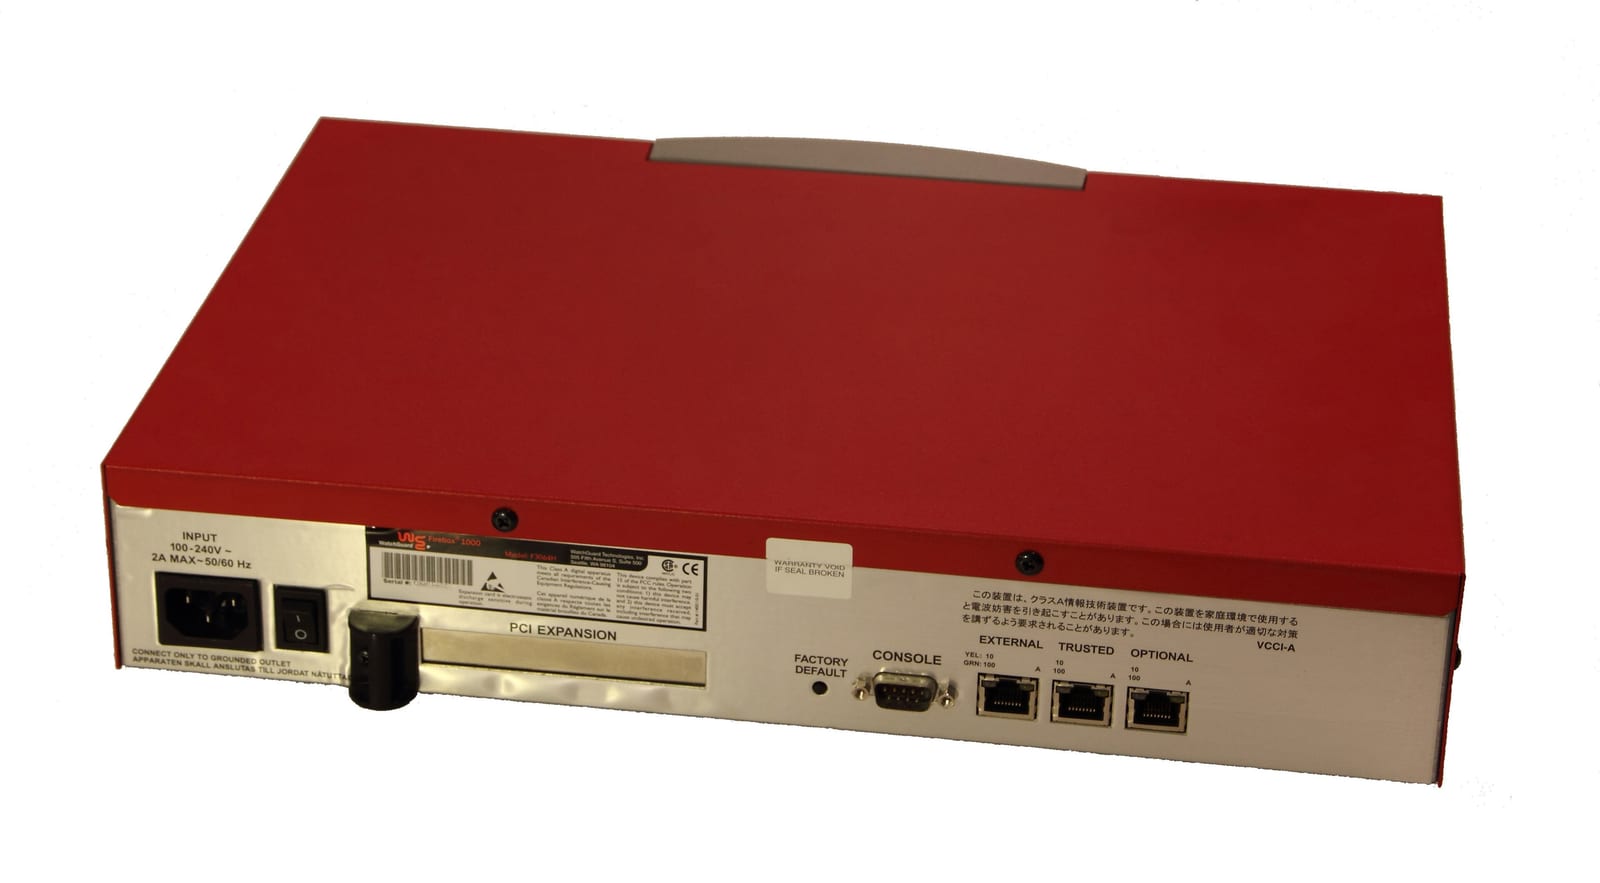
Photo: Jakez (CC BY-SA 3.0) via Wikimedia Commons

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has confirmed that a critical remote code execution (RCE) vulnerability in WatchGuard Firebox firewalls, tracked as CVE-2025-14733, is now being exploited by ransomware groups. CISA added this flaw to its Known Exploited Vulnerabilities (KEV) catalog in December, at which point it was already being actively exploited.

The vulnerability is an out-of-bounds write issue that allows unauthenticated attackers to execute arbitrary code remotely with low complexity. It affects Fireware OS versions 11.x and later, including 11.12.4_Update1; 12.x and later, including 12.11.5; and versions 2025.1 through 2025.1.3.

When WatchGuard released patches for CVE-2025-14733 in December, the company stated that unpatched Firebox firewalls were vulnerable if configured to use IKEv2 VPN. However, WatchGuard also cautioned that devices might still be compromised even if vulnerable configurations had been removed, particularly if a branch office VPN to a static gateway peer remained configured. The vendor also confirmed active exploitation at that time and provided indicators of compromise to help customers detect potential breaches.

In December, the internet security watchdog group Shadowserver identified over 115,000 unpatched Firebox firewalls exposed online. Nine months later, nearly 9,000 of these instances reportedly remain unsecured.

CISA's update to its KEV catalog on Thursday specifically noted the involvement of ransomware gangs in exploiting CVE-2025-14733, though the agency did not release further details regarding these attacks. When the flaw was initially added to the KEV catalog in December, CISA issued a directive requiring U.S. federal agencies to secure their systems against it within one week, in accordance with Binding Operational Directive (BOD) 22-01.

This is not the first WatchGuard vulnerability to be highlighted by CISA. Two years prior, the agency mandated government agencies to patch another actively exploited WatchGuard flaw, CVE-2022-23176, which affected both Firebox and XTM firewalls. More recently, in September 2025, WatchGuard patched CVE-2025-9242, an RCE vulnerability in Firebox firewalls described as almost identical to CVE-2025-14733. CISA subsequently tagged CVE-2025-9242 as actively exploited one month later, with Shadowserver finding over 75,000 Firebox firewalls vulnerable to attacks at that time.

WatchGuard provides services to over 250,000 small and mid-sized businesses globally through a network of more than 17,000 security resellers and service providers.


vulnerabilities in this storyCVE-2025-14733CVE-2022-23176CVE-2025-9242
watchguardrceransomwarecisavulnerability
ShareXLinkedInWhatsAppFacebook

More News

view all →
security

Canadian cybersecurity executive arrested in federal extortion case

A Canadian cybersecurity executive was arrested in Pennsylvania on Thursday, facing federal charges of conspiracy to commit extortion. Edward Dubrovsky, 54, a co-founder and former Chief Operating Officer of CYPFER, a firm specializing in ransomware negotiation, is charged with conspiring to threaten the confidentiality of information for extortion and conspiring to commit Hobbs Act extortion,…

breach

Criminal IP Introduces AITEM as the Next Evolution of Attack Surface Management

AI SPERA, the company behind the cyber threat intelligence platform Criminal IP, has announced AITEM (AI-Powered Threat Exposure Management), an expansion of its Attack Surface Management (ASM) offerings. AITEM aims to move beyond traditional asset discovery to provide a more comprehensive approach to understanding, prioritizing, and responding to security exposures. The platform is scheduled…

ai

AI Is Getting Really Good at Messing With Cybercriminals

Anti-cybercrime initiatives are increasingly deploying artificial intelligence to disrupt scammers by engaging them with lifelike bots, which the criminals mistake for genuine victims. This strategy aims to waste scammers' time and resources while gathering intelligence on their operations.

ransomware

FBI Arrests Ransomware Negotiation Firm Co-Founder in ShinyHunters Probe

The Federal Bureau of Investigation (FBI) has reportedly arrested Edward Dubrovsky, a co-founder of the ransomware negotiation firm Cypfer and currently associated with CyberSteward. The arrest is said to be part of the ongoing ShinyHunters investigation, specifically in connection with an incident involving FBI job applicant data.

security

Insider Cyber Extortion Plot Against Industrial Firm Lands Engineer in Prison

A former core infrastructure engineer has been sentenced to prison for an attempted cyber extortion plot against an industrial firm. The engineer reportedly deleted administrative accounts and reset hundreds of user passwords, subsequently demanding a ransom of 20 Bitcoin to prevent further disruption to the company's servers.

ai

The Third-Party Agent Problem: Why Security Built for AI You Chose Misses the Agents You Didn't

A new report highlights a significant blind spot in enterprise security architectures concerning the proliferation of third-party AI agents. The forthcoming 2026 State of Agent Security Report indicates that current security models, often designed to protect AI systems directly chosen and deployed by an organization, frequently fail to account for AI capabilities embedded within third-party…



