CVSS—
Severityhigh
Weakness—
Exploited3 KEV sources
Ransomware useUnknown
Federal fix dueDec 3, 2025
patch window
Called exploited 34 days after disclosure.
Measured from the CVE publication date to the earliest of 3 KEV catalogues that list it.
The life of this vulnerability
- CVE published
- First KEV listing34d
- Last KEV listing22d
- Last sighting6mo
Gaps are compressed to equal steps. The elapsed time is printed under each.
Which catalogues call it exploited
- CISA KEVUS federallisted Nov 12, 2025
- EUVDENISA, European Unionlisted Nov 12, 2025
- VulnCheck KEVcommercial researchlisted Oct 21, 2025
- CIRCLaggregator, mirrors the abovelisted Nov 12, 2025, not counted
Sources3 of 3
Listings differ by22 d
Strongest claimconfirmed
3 catalogues list it. CIRCL aggregates the others and is shown but not counted.
Public exploitation evidence
- reported exploitationctrlaltintel.com/research/Qilin/
- reported exploitationwww.loginsoft.com/reports/annually/vulnerability-intelligenc
- reported exploitationcyble.com/resources/research-reports/global-cybersecurity-re
- reported exploitationwww.recordedfuture.com/blog/november-2025-cve-landscape
- reported exploitationwww.cisa.gov/sites/default/files/feeds/known_exploited_vulne
- reported exploitationwww.watchguard.com/wgrd-psirt/advisory/wgsa-2025-00015
6 public reports collected from VulnCheck and CIRCL, first on Oct 21, 2025. Each links to its original source. We have not verified them.
Description
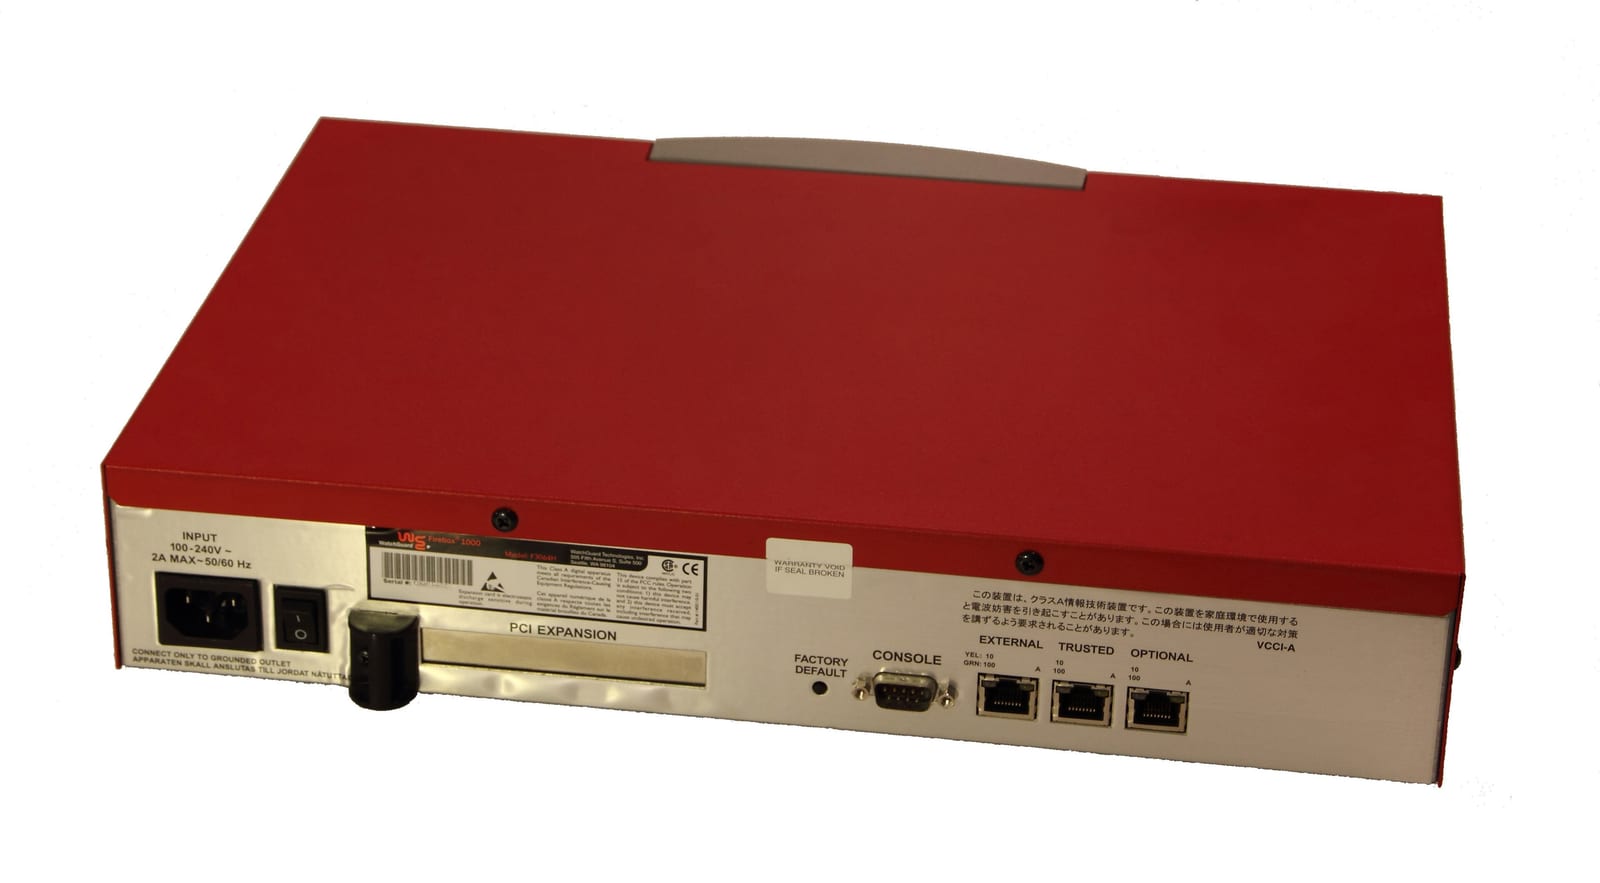
WatchGuard Firebox contains an out-of-bounds write vulnerability in the OS iked process that may allow a remote unauthenticated attacker to execute arbitrary code.
Required action (CISA)
Apply mitigations per vendor instructions, follow applicable BOD 22-01 guidance for cloud services, or discontinue use of the product if mitigations are unavailable.