
cloud news
210 stories · page 5 of 5
New InfraTrust report reveals infrastructure flaws admins should patch first
A new report from Eclypsium, titled InfraTrust Pulse, has identified critical vulnerabilities in infrastructure, firmware, networking, and edge devices that organizations should prioritize for patching. The inaugural July 2026 report, part of Eclypsium's new InfraTrust knowledge base, analyzed 61 infrastructure advisories from 14 vendors, highlighting six critical advisories and 26 remotely…
AWS wants GuardDuty to automate the first steps of threat investigations
Amazon Web Services (AWS) has launched a public preview of its new Amazon GuardDuty investigation agent, a feature designed to automate the initial stages of threat investigations using AI. This agent aims to reduce the time security teams spend on investigations by providing structured assessments of GuardDuty findings, AWS accounts, and entire AWS organizations.
SonicWall SMA1000 flaws exploited as zero-days to push custom malware
SonicWall's SMA1000 Secure Mobile Access appliances were targeted in zero-day attacks for several weeks, with threat actors exploiting two vulnerabilities to install custom malware. The company confirmed the exploitation of these previously undisclosed flaws, urging customers to apply patches immediately.
Malicious cloud customers can bring down the power grid
Researchers in China have identified a novel cyber-physical vulnerability, dubbed Bit2Watt, that could allow malicious cloud tenants to destabilize data centers and the broader electrical grid by manipulating GPU workloads. The attack, detailed in a preprint paper by Zhouhao Ji, Kaikai Pan, and Wenyuan Xu from Zhejiang University, highlights a potential pathway for adversaries to cause…
More alerts are making your team slower, and an outcome-based SOC fixes that
--- Source 2 --- Rapid7 Unveils AI-Powered SOC Platform to Combat Alert Fatigue and Accelerate Threat Response
Week in review: High severity WordPress vulnerabilities, fake OAuth IDs bypass sign-in logs
Attackers are reportedly bypassing Microsoft Entra ID sign-in logs by spoofing OAuth client IDs during account enumeration against Microsoft cloud tenants. This technique involves manipulating the `client_id` parameter in authentication requests, which Entra ID records as the application ID. The way the system handles unfamiliar identifiers creates a blind spot that threat actors are…
Attackers Can Take Over WordPress Sites Using Newly Released wp2shell Exploits
Public exploits are now available for a pair of critical vulnerabilities in WordPress Core, which, when chained, allow attackers to achieve pre-authentication remote code execution on affected installations. The flaws, collectively dubbed "wp2shell," impact WordPress versions 6.9.0 through 6.9.4 and 7.0.0 through 7.0.1.
WordPress Core "wp2shell" RCE flaws get public exploits, patch now
Publicly available exploits have emerged for a pair of critical remote code execution (RCE) vulnerabilities in WordPress Core, collectively dubbed "wp2shell." These flaws, identified as CVE-2026-63030 and CVE-2026-60137, can be chained together to allow pre-authentication RCE on affected WordPress installations. Administrators are strongly advised to update their sites immediately.
FalconStor Cloud Clean Room enables validated recovery without dedicated infrastructure
FalconStor has introduced FalconStor Cloud Clean Room, a new platform designed to allow organizations to conduct validated recovery tests in a secure, on-demand environment. This solution aims to address the persistent challenge of ensuring data recoverability without the significant cost and complexity of maintaining dedicated recovery infrastructure.
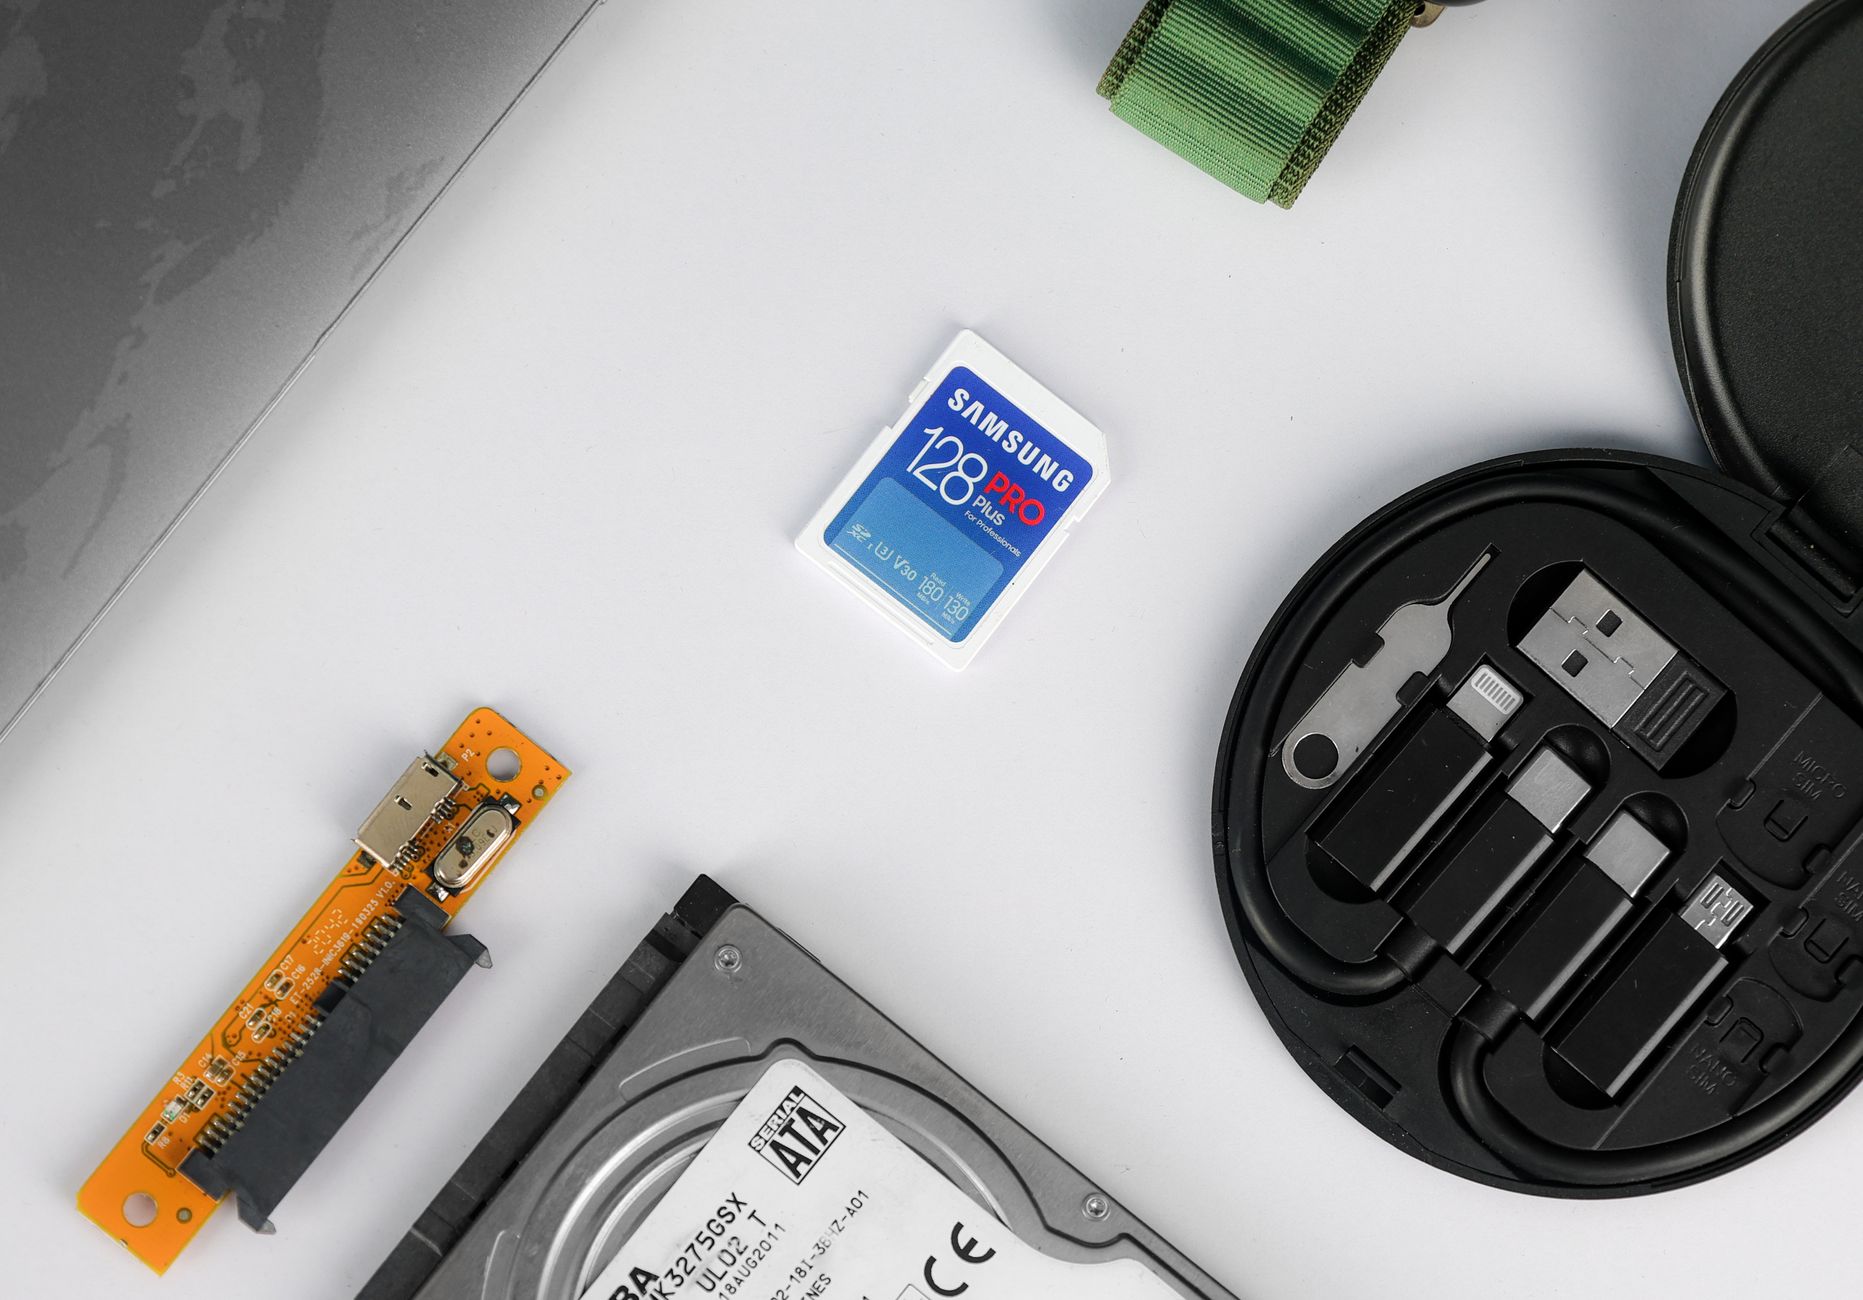
Unpatched Flaws Disclosed in Filesystem Bundled Into Millions of Embedded Devices
A cybersecurity firm has revealed seven security weaknesses in FatFs, a widely deployed filesystem library. FatFs is used by millions of embedded devices to read and write data on FAT and exFAT formatted storage media, such as USB drives and SD cards. The vulnerabilities were disclosed by the security firm runZero.
FortiBleed Actors Collaborating With Inc, Lynx Ransomware Gangs
Threat actors who previously compromised numerous Fortinet firewalls are now reportedly collaborating with ransomware groups, including those behind the INC and LYNX ransomware strains. This collaboration appears to be a strategy to monetize the initial access gained through exploiting vulnerabilities in Fortinet devices.
Cybersecurity Mission Creep in the US
A growing trend in the United States involves policymakers increasingly framing a wide range of societal problems as cybersecurity issues, a phenomenon described as "cybersecuritization." This reframing transforms diverse policy challenges, including misinformation, social media safety for children, antitrust regulations, allegations of journalist misconduct, and anti-sex trafficking laws,…
'Djinn' Stealer Targets Cloud, AI Credentials
A newly identified information-stealing malware, dubbed "Djinn," is actively targeting credentials that bridge cloud environments, artificial intelligence platforms, and broader enterprise systems. The malware's initial distribution vector exploits a critical authentication bypass vulnerability, identified as CVE-2026-48558, present in the remote support software SimpleHelp.
Amazon Q VS Extension Flaw Leads to Cloud Credential Theft
A security flaw has been discovered that could allow attackers to steal cloud credentials by planting a malicious repository. This vulnerability affects Amazon's Q, a generative AI assistant, and highlights the increasing risks associated with multi-cloud platform (MCP) environments.
Lawmakers Demand Answers as CISA Tries to Contain Data Leak
Lawmakers on Capitol Hill are demanding answers from the U.S. Cybersecurity & Infrastructure Security Agency (CISA) following a report that a contractor intentionally exposed a significant amount of sensitive agency data, including AWS GovCloud keys, on a public GitHub account. The breach has prompted an inquiry from both houses of Congress as CISA works to mitigate the fallout and revoke the…
CISA Admin Leaked AWS GovCloud Keys on Github
A contractor for the Cybersecurity & Infrastructure Security Agency (CISA) inadvertently exposed highly privileged credentials for AWS GovCloud accounts and numerous internal CISA systems through a public GitHub repository. Security experts have described the leak as one of the most significant government data exposures in recent history, containing details on CISA's internal software…
On the Effectiveness of Mutational Grammar Fuzzing
Mutational grammar fuzzing, a technique that uses predefined grammars to guide sample mutation while preserving structural integrity, faces significant challenges that can hinder bug discovery despite its proven effectiveness. While the approach ensures generated samples adhere to structural rules, leading to the discovery of complex issues in areas like XSLT implementations and JIT engines,…
Bypassing Windows Administrator Protection
Microsoft's Administrator Protection feature, intended to replace User Account Control (UAC) with a more secure system for granting administrator privileges in Windows 11, has been found to be bypassable. The feature, introduced in Windows 11 version 25H2, aims to allow local users to access administrative rights only when necessary, creating a more robust security boundary. However, security…