
finance news
71 stories · page 2 of 2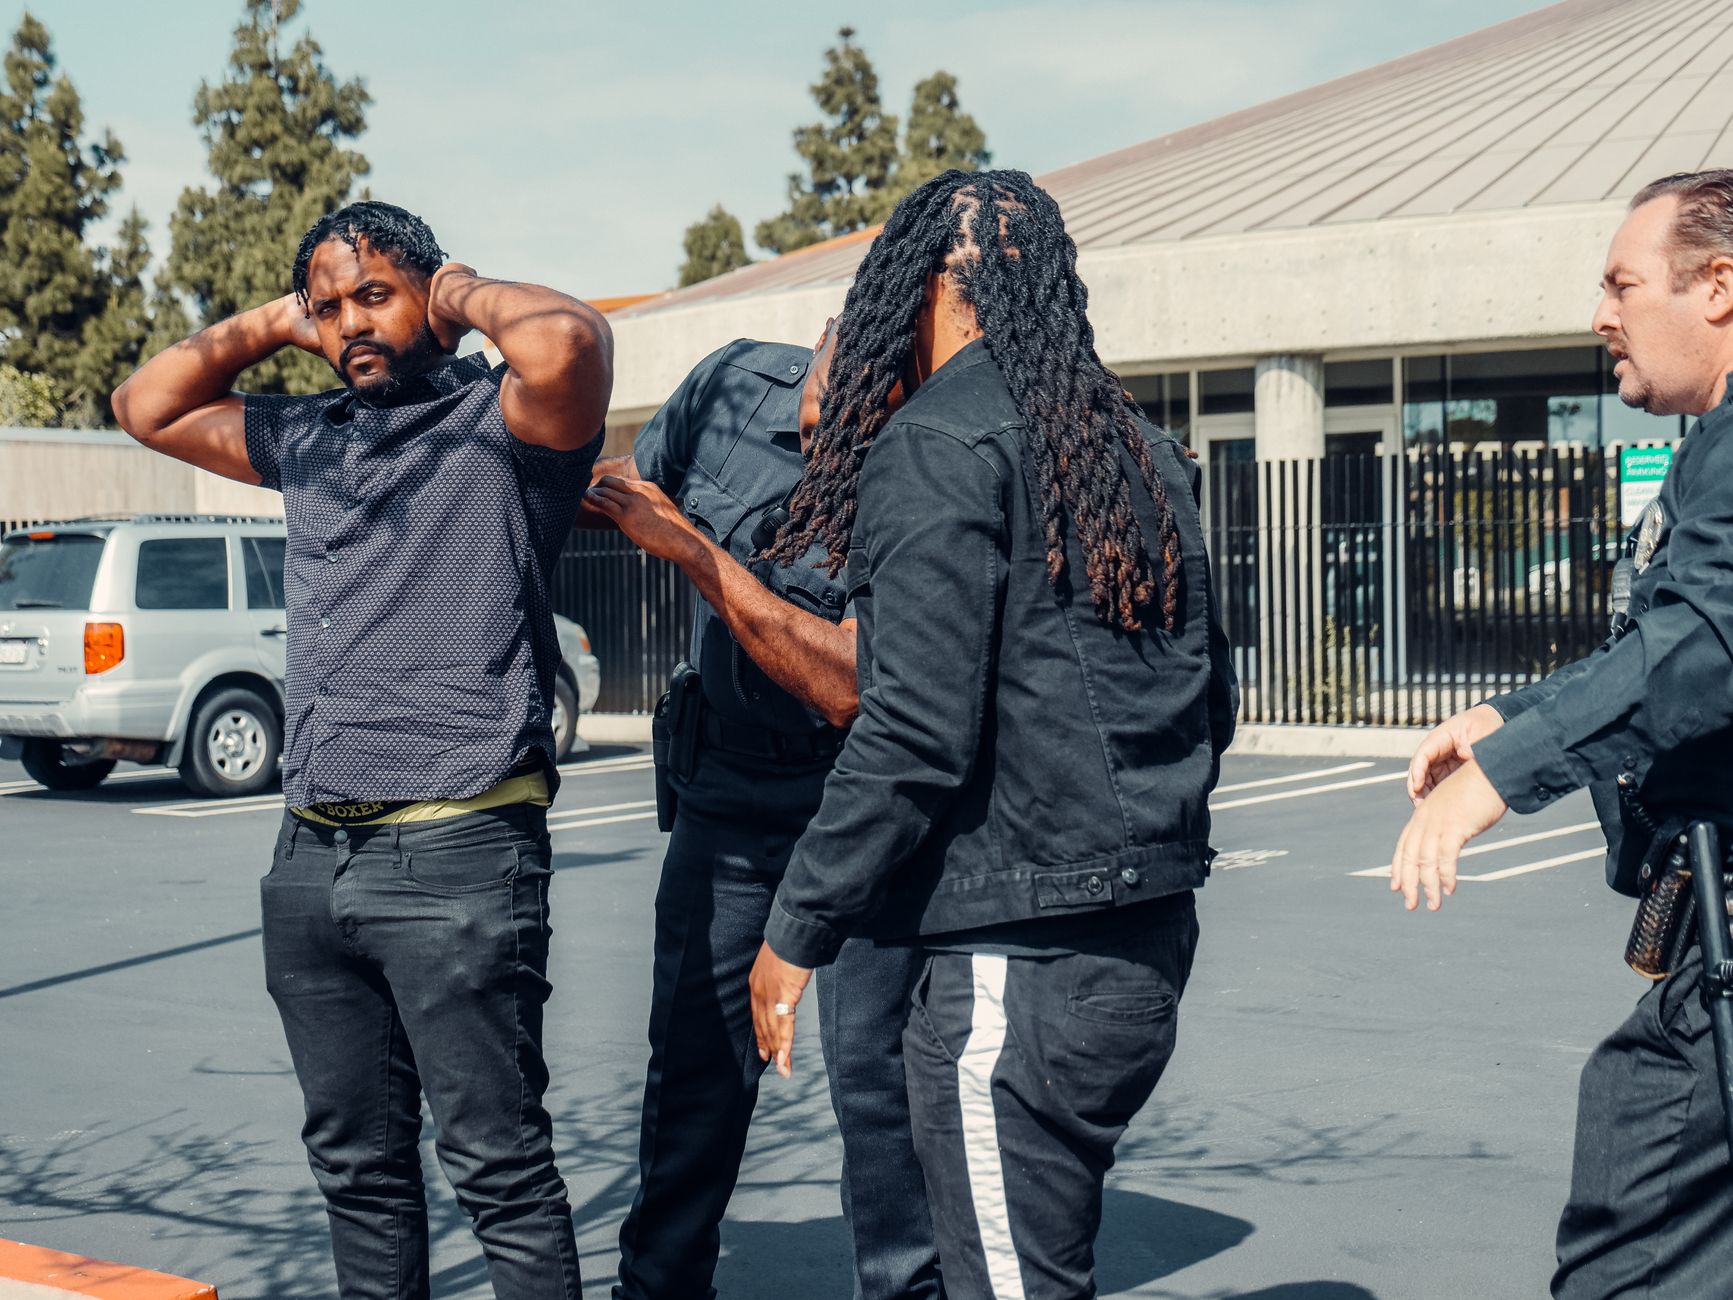
Ukrainian police raid 94 fraudulent call centers, seize $2 million
Ukrainian law enforcement agencies have dismantled 94 fraudulent call centers across the country in a large-scale operation that involved over 400 searches and resulted in the seizure of approximately $2 million in various currencies and assets. The raids targeted operations engaged in a range of scams, including impersonating bank employees, offering fake investment opportunities, and…
Ukraine shuts down 94 fraudulent call centers, seize millions in cash
Ukrainian authorities have dismantled 94 fraudulent call centers across the country, seizing significant assets and apprehending suspects in an operation that involved the National Police, Ukraine's Security Service, the Prosecutor General's Office, and German police. The crackdown, which occurred this week, involved 411 searches and targeted various schemes designed to defraud individuals…
New Android malware lets criminals use your bank card in real time
Cybersecurity researchers at Group-IB have identified a new Android malware family, dubbed WindRelay, designed to facilitate real-time contactless payment card fraud. This malware operates by capturing live NFC (Near Field Communication) data from a victim's physical bank card and relaying it instantly to an attacker-controlled device, which can then be used for fraudulent purchases or ATM…
'Jewelbug' APT Balances State Espionage & Cryptocurrency Theft
Researchers have reported the activities of an Advanced Persistent Threat (APT) group dubbed "Jewelbug," which appears to be engaging in a dual operational model. This group has been observed conducting both state-sponsored cyber espionage activities and financially motivated cryptocurrency theft. The unusual aspect of this operation, as highlighted by the researchers, is that both types of…
Storm-1175 Replaces Medusa With New StormEncryptor Ransomware
Microsoft Threat Intelligence has confirmed that the China-linked, financially motivated threat actor known as Storm-1175 has adopted a new ransomware strain, StormEncryptor, replacing its previous use of Medusa ransomware. The shift was observed beginning August 2, 2026, marking the first recorded activity of Storm-1175 deploying this new malware.
Post-quantum migration gets harder when every user holds a key
The transition to post-quantum cryptography presents significant challenges, particularly in systems where individual users manage their own cryptographic keys, such as blockchains. Experts note that the increased key and signature sizes required by new algorithms can break assumptions in older protocols and systems, while the decentralized nature of user-held keys complicates large-scale…
Ready-made $500 kit puts a crypto scam within anyone’s reach
A cybercrime forum vendor is offering a comprehensive scam kit for $500, enabling individuals with minimal technical skills to execute sophisticated cryptocurrency fraud. The kit, discovered by Malwarebytes researchers on May 16, provides a complete "scam-in-a-box" solution, integrating social engineering, phishing, and financial fraud into a single, ready-to-use package.
New StormEncryptor ransomware used by former Medusa affiliate
A financially motivated threat actor, previously linked to the Medusa ransomware operation, has been observed deploying a new ransomware strain named StormEncryptor. Microsoft Threat Intelligence, which tracks this actor as Storm-1175, indicates that recent attacks likely leveraged an authentication-bypass vulnerability, CVE-2026-18577, in the N-central remote monitoring and management (RMM) tool.
IT threat evolution in Q2 2026. Mobile statistics
In the second quarter of 2026, cybersecurity researchers observed a continued decline in the overall number of attacks on mobile devices, with just under 2 million incidents blocked. Despite this decrease, new and evolving threats, particularly mobile banking Trojans and sophisticated droppers, remained a significant concern for Android and iOS users.
Critical Flaws Discovered in Belgian eID Software Used by 2 Million People
Critical vulnerabilities have been reported in the Belgian eID software, a system utilized by an estimated two million individuals. These flaws reportedly impact applications across a significant portion of Belgium's financial sector, specifically affecting software used by eight of the ten largest banks, as well as over 60 government agencies. The widespread adoption of this software suggests…
Hackers Impersonate IT Support to Breach Leading Financial Companies
A sophisticated hacking campaign has targeted over 200 firms, including major financial institutions, by impersonating IT support staff to steal multi-factor authentication (MFA) credentials. The campaign, tracked by Google Threat Intelligence Group (GTIG) as UNC6671, has operated under several names, including Redact, Pink, Falcon, and Helix, and has been linked to the BlackFile extortion brand.
Microsoft 365 AitM Phishing Hijacks Accounts to Collect Payroll and Finance Emails
Cybersecurity researchers have reported an active and widespread email-driven phishing campaign targeting Microsoft 365 accounts. This campaign leverages adversary-in-the-middle (AitM) techniques to compromise accounts, with the ultimate goal of identifying key personnel involved in financial workflows and exfiltrating related email communications. The observed activity indicates a focused…
Ransomware Surges in July After Q2 Lull
Ransomware attacks saw a significant increase in July, rising by 19% compared to June, according to an analysis published on August 5. This surge followed a period of relative calm in April, May, and June, making July the second most active month for ransomware in 2026 and the third highest in the past 17 months. A total of 799 claimed ransomware attacks were observed during July.
Hedge fund cyberattacks tied to BlackFile-linked UNC6671 extortion group
A recent wave of cyberattacks targeting hedge funds, private equity firms, and other financial organizations has been attributed to UNC6671, an extortion group that has previously operated under the name BlackFile. The attacks reportedly leveraged voice phishing (vishing) to gain unauthorized access to corporate systems.
Pre-auth RCE in enterprise Java hits Bonita and OFBiz servers
Vulnerability researchers have uncovered critical pre-authentication remote code execution (RCE) flaws in two widely used enterprise Java platforms, Bonita BPM and Apache OFBiz. These vulnerabilities, which allow an attacker to execute arbitrary code on a server without prior authentication, were detailed at Black Hat USA 2026 by researchers from Novee. The findings are part of a broader audit…
Brown Health Medical Group-MA Data Breach Exposes Information of 311,000 Individuals
Brown Health Medical Group-MA has confirmed a data breach affecting over 311,000 individuals, exposing personal, medical, and financial information after unauthorized access to a legacy file server. The healthcare provider identified the security incident on December 16, 2025, and an investigation determined that the unauthorized access occurred between December 15 and 16, 2025.
311,000 Impacted by Brown Health Medical Group-MA Data Breach
Brown Health Medical Group-MA has reportedly experienced a data breach impacting 311,000 individuals. The incident involved unauthorized access to the organization's servers, leading to the theft of personal information, medical records, and financial information.
CareCloud Breach Exposes Medical and Financial Data of 345,000
CareCloud, a New Jersey-based health technology company, has confirmed a data breach affecting approximately 345,000 individuals, with the number potentially increasing as more state filings are processed. The incident involved unauthorized access to one of the company's electronic health record (EHR) data stores hosted on Amazon Web Services (AWS).
South Korea Warns of State-Backed Watering Hole Attacks
South Korean authorities have issued a joint advisory warning citizens and businesses about ongoing state-backed cyberattacks employing both phishing and watering hole techniques. The National Intelligence Service, National Police Agency, Korea Internet & Security Agency, and Financial Security Institute collaborated on the alert, which details how attackers are silently compromising systems.
Charities remain locked out of CAF Bank online accounts
CAF Bank's 14,000 UK charity customers remain locked out of their online banking accounts, a week after the service was suspended due to detected attempted fraud. The bank has not provided a timetable for restoring access, leaving many charities unable to make essential payments, including staff payroll and supplier invoices.
Hermes AI agent used to automate attack on Thai Finance Ministry
A threat actor allegedly utilized the open-source Hermes AI agent in an unattended "YOLO" mode to automate post-exploitation activities during a purported breach of Thailand's Ministry of Finance. This activity was uncovered by the threat intelligence firm Hunt.io and security researcher Bob Diachenko, who identified several exposed web directories containing files related to the operation.…
Upbound says hack caused $13 million in fraudulent Acima leases
Upbound Group, a fintech company, has disclosed that a cybersecurity incident led to approximately $13 million in fraudulent lease-to-own agreements through its Acima Leasing segment. The company, formerly known as Rent-A-Center, stated in a U.S. Securities and Exchange Commission (SEC) filing that unauthorized actors obtained certain non-sensitive customer information and other documents from…
Oracle July 2026 Critical Patch Update Addresses 1235 CVEs
Oracle released its July 2026 Critical Patch Update (CPU), addressing 1,235 unique Common Vulnerabilities and Exposures (CVEs) across 32 product families. This quarterly update, the third for 2026, includes a total of 1,449 security patches, making it the largest CPU release to date.