
nation-state news
140 stories · page 2 of 3
Interpol's Jackal IV Disrupts West African Crime Infrastructure
Interpol has reported the successful disruption of crime-as-a-service (CaaS) networks and their supporting infrastructure in West Africa, an operation dubbed "Jackal IV." The international law enforcement effort specifically targeted groups such as Black Axe, indicating a focus on organized cybercrime syndicates operating within the region. This operation marks a significant push to dismantle…
Nigeria Looks to Sovereign Cloud for Cyber, National Security
Nigeria is reportedly advancing its sovereign cloud initiative, implementing new policies around financing, procurement, and infrastructure. This strategic move is aimed at bolstering the nation's cybersecurity posture and enhancing its overall national security, while simultaneously cultivating domestic technical expertise.
Hackers abuse npm mirrors to host phishing redirect pages
Threat actors are leveraging the npm package registry and its mirroring services to host malicious HTML pages, effectively turning these platforms into free web hosting for phishing redirects. This technique, distinct from typical supply-chain attacks that infect developer systems, uses npm as a validated storage mechanism for attacker-controlled content.
58 arrested in international cybercrime crackdown
Fifty-eight individuals have been arrested across 22 countries as part of an eight-month international cybercrime operation, Interpol announced. The arrests are the latest phase of Operation Jackal, a multi-year effort to dismantle cybercriminal organizations globally. This specific leg, dubbed Operation Jackal IV, ran from November 2025 to June 2026.
Interpol targets Black Axe’s illicit financial web in latest international sting
An international law enforcement operation, dubbed Operation Jackal IV, has resulted in 58 arrests and the identification of 263 suspects globally, targeting the financial networks of West African organized crime groups, including Black Axe. The operation, announced by Interpol, aimed to disrupt money laundering activities, locate high-value targets, seize assets, and support prosecutions.
Cybersecurity jobs available right now: August 25, 2026
The cybersecurity job market continues to show a diverse range of opportunities across various specializations and geographies as of August 25, 2026. Roles are available from entry-level internships to senior counsel positions, spanning compliance, identity and access management (IAM), security architecture, and incident response.
US sanctions Iranian cyber actors as UK discloses power plant attack
The United States has imposed sanctions on several Iranian nationals for their alleged involvement in cyberattacks targeting critical infrastructure, following reports of a cyber intrusion at a small power plant in the United Kingdom. Treasury Secretary Scott Bessent announced the new sanctions on Monday, August 24, 2026, as part of efforts to pressure the Iranian government and facilitate the…
Criminal Deception in Silicon Valley
A recent academic paper has analyzed entrepreneurial fraud cases in Silicon Valley from 2000 to 2023, identifying a systematic process dubbed "façading" used by founders to deceive investors and other audiences. The research, which examined court data from prosecuted fraud cases, describes façading as the construction, performance, and protection of illusory appearances that project…
Slovakia Warns of Cyber Risks in Road Speed Cameras
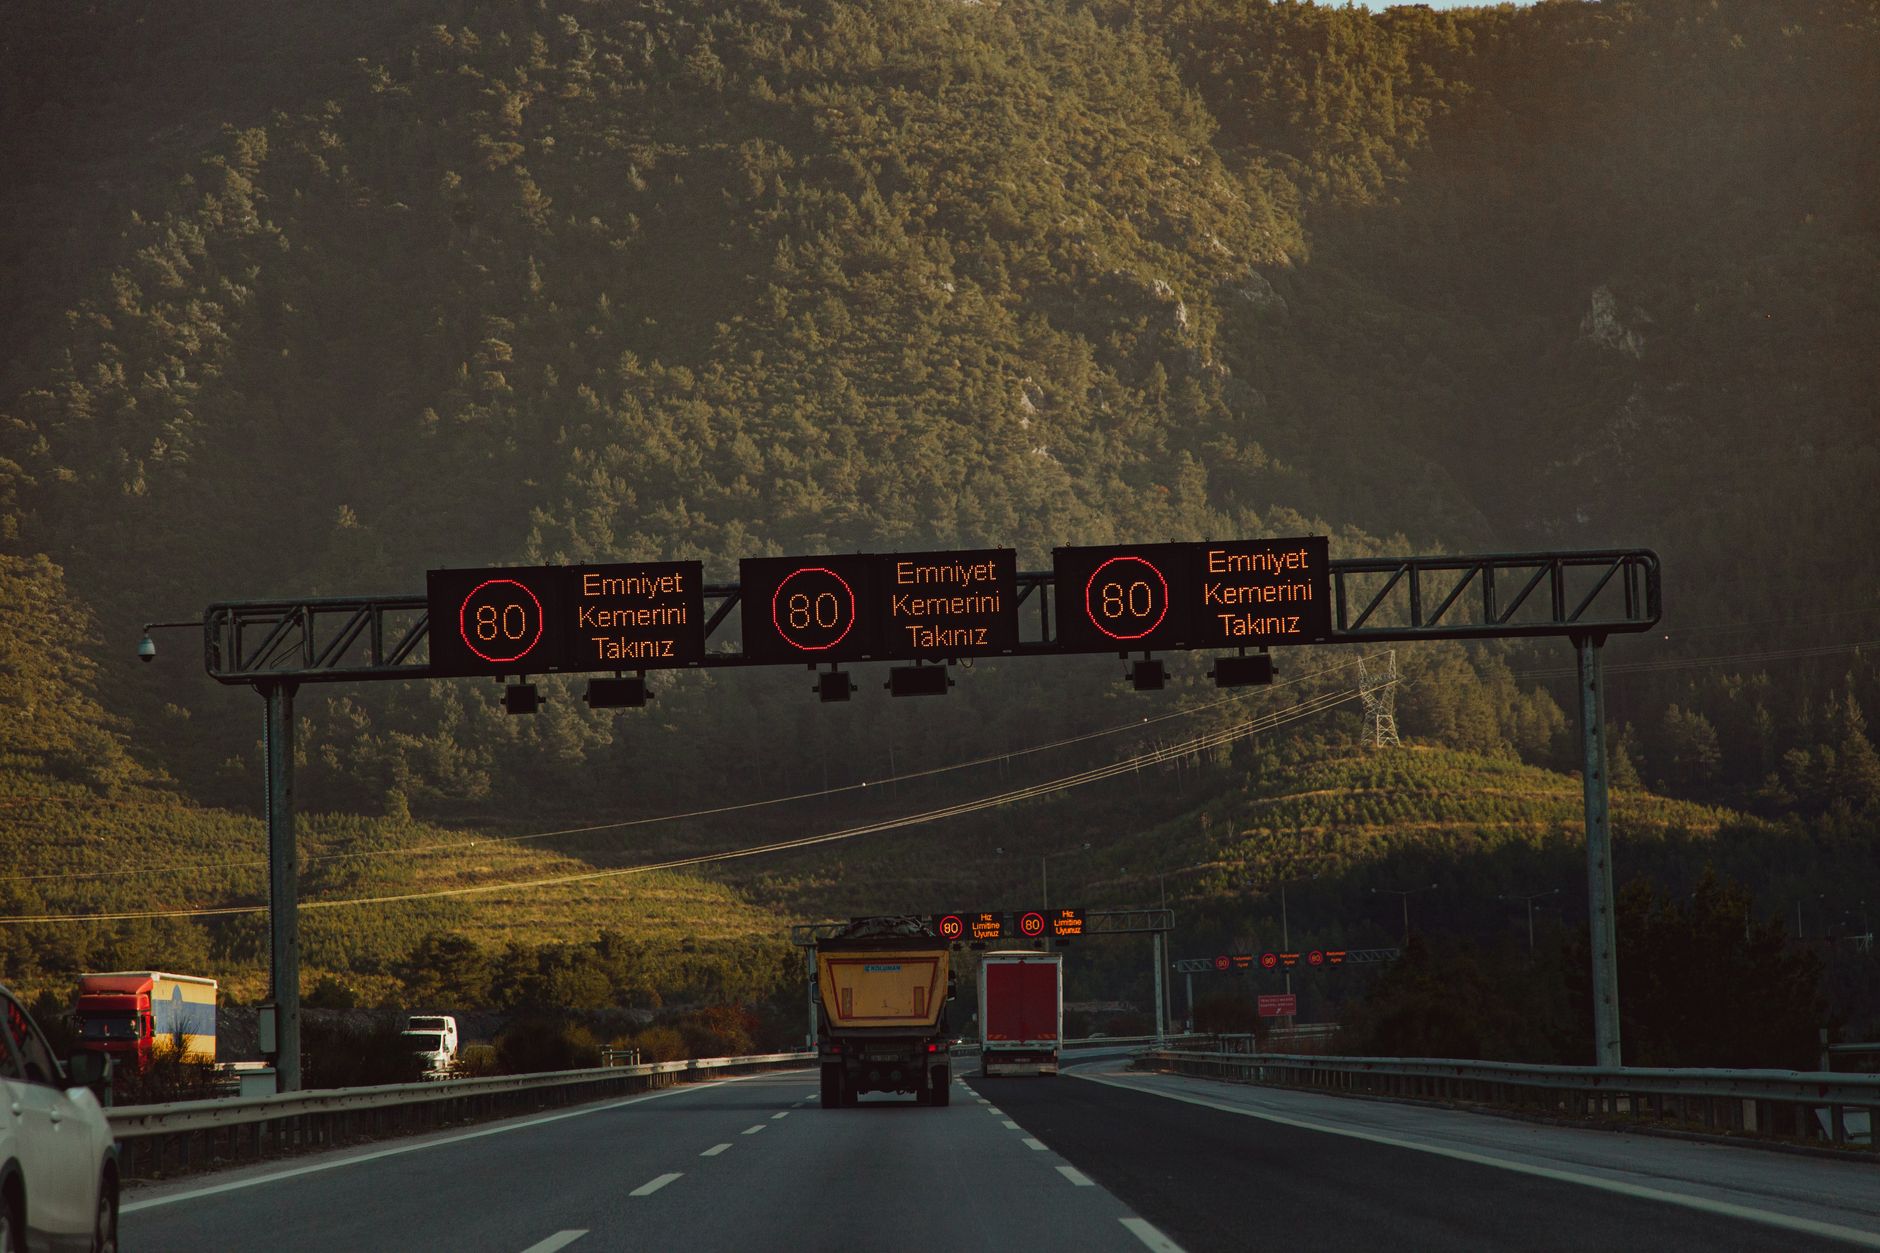
Slovakia's National Security Authority (NBÚ) has issued a warning regarding significant cybersecurity risks associated with several types of road speed cameras, identifying them as potential threats to public networks and sensitive vehicle data. The alert, prompted by a request from the Interior Ministry, focuses on connected devices that collect vehicle information, communicate with other…
Friday Squid Blogging: Neon Flying Squid
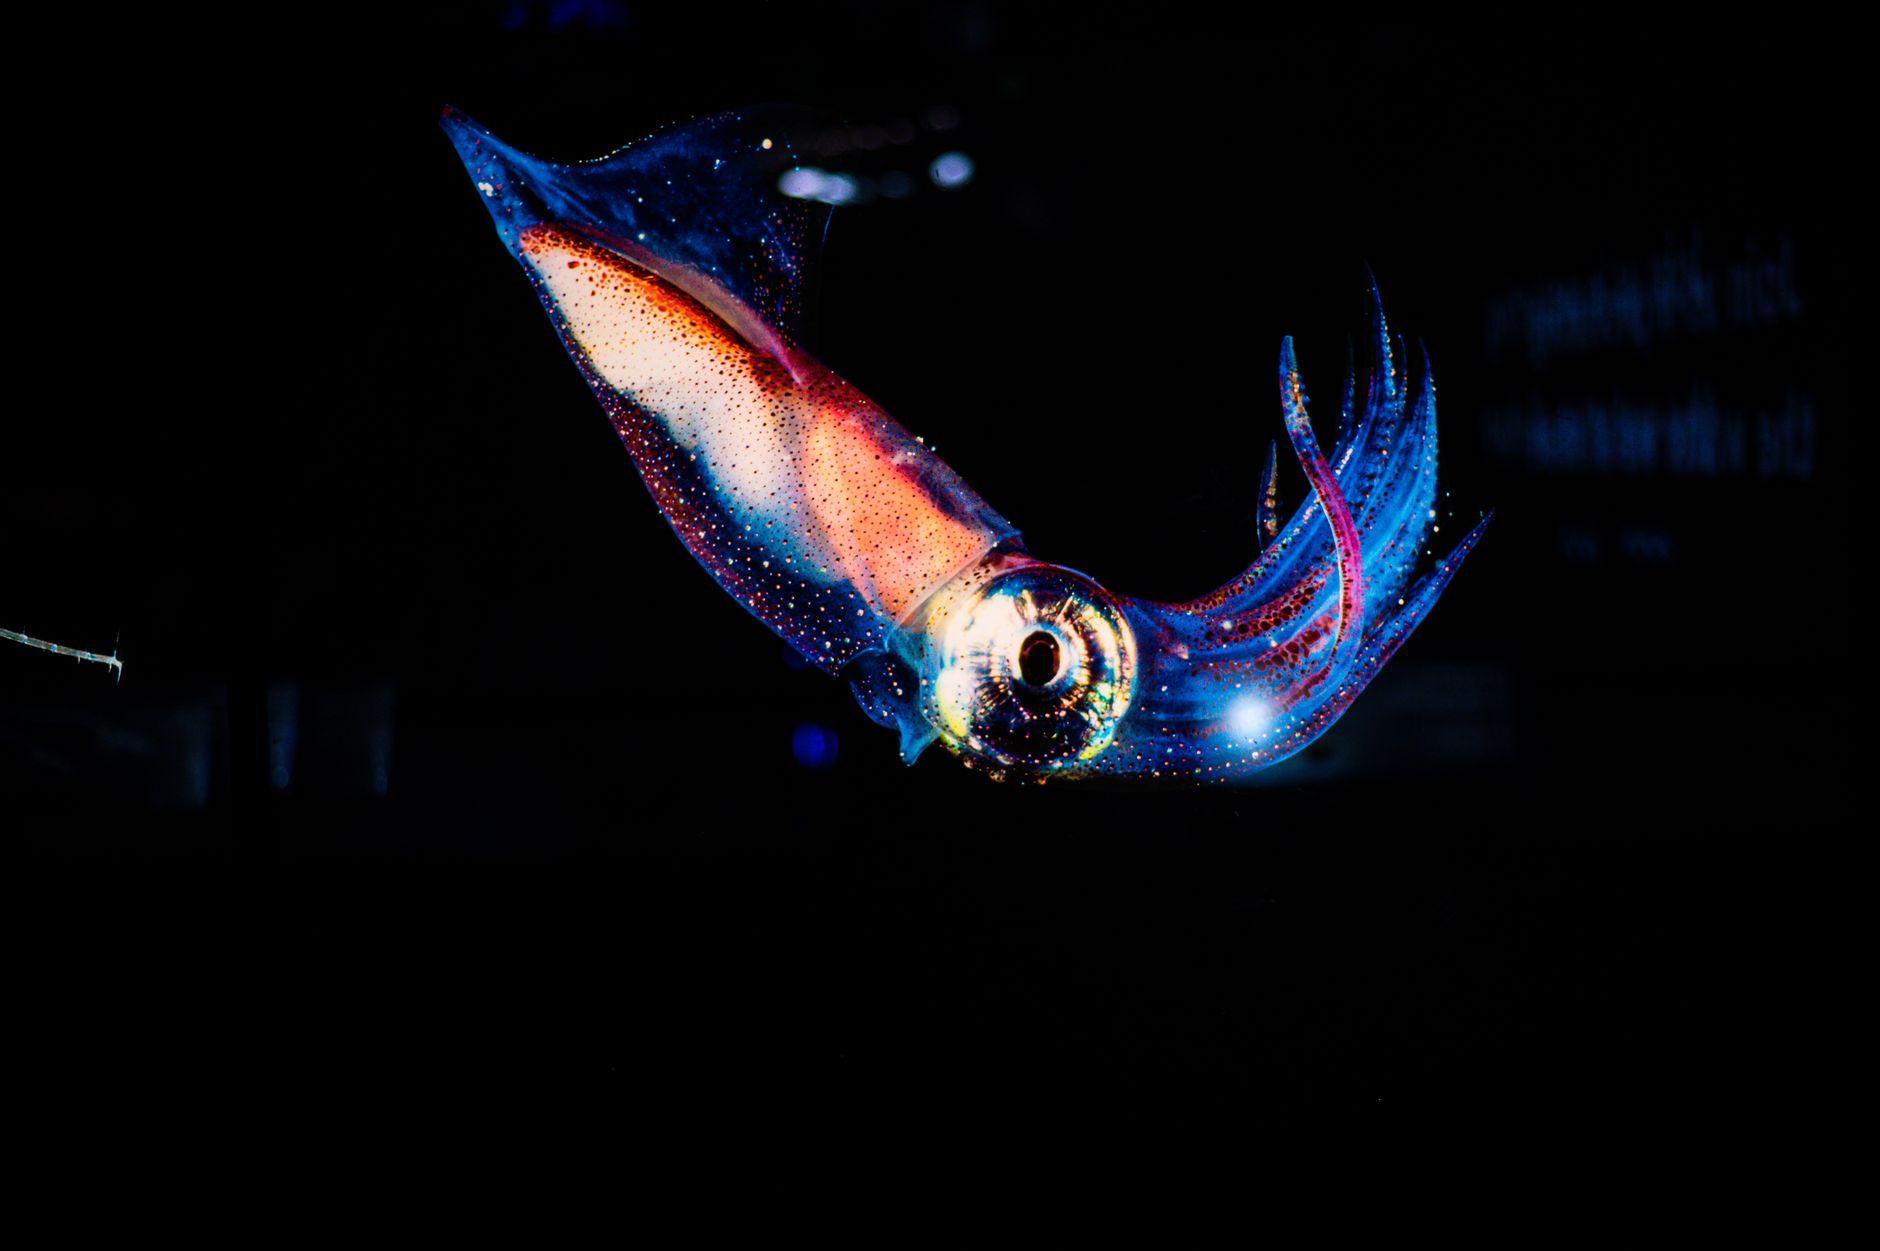
A research team has captured the first photographic evidence of neon flying squid (Ommastrephes bartramii) gliding above the surface of the Pacific Ocean. The observation, made approximately 370 miles from Tokyo, involved a shoal of about 100 squid that emerged from the water and glided for roughly 30 meters near the researchers' boat.
Former NSA Director Paul Nakasone Launches National Security Advisory Firm
Former National Security Agency (NSA) Director General Paul Nakasone has reportedly launched a new national security advisory firm, named the Nakasone Group. The firm is positioned to offer strategic counsel to a diverse clientele, including government leaders, corporations, prominent families, and other private clients. Its stated focus areas encompass cybersecurity, geopolitical challenges,…
Poland’s CERT Warns of Active Exploitation of Critical Zimbra Collaboration Suite Flaw
CERT Polska has confirmed active exploitation of a critical unauthenticated remote code execution vulnerability in Zimbra Collaboration Suite, identified as CVE-2026-73570. The flaw, which allows attackers to execute arbitrary shell commands with the privileges of the `zimbra` user, was patched by Zimbra on July 20, 2026, in version 10.1.20. Active exploitation was confirmed less than a month…
Suspected Russian Hackers Abuse Google OAuth and WhatsApp Linking to Hijack Accounts
Suspected Russian cyber espionage groups have been observed exploiting legitimate Google OAuth and WhatsApp linking mechanisms to compromise accounts belonging to individuals in sensitive sectors. The activity targets individuals in academia, aerospace and defense, government, and think tanks across Europe, as well as academia and think tanks in the United States. Three distinct threat…
Pakistan's Transparent Tribe Refreshes Toolset for Afghan Cyberattacks
Reports indicate that Transparent Tribe, a threat actor widely associated with Pakistan, has updated its cyberattack toolkit, primarily targeting organizations within Afghanistan. The group's recent activities appear to focus on less mature entities, particularly those associated with the Taliban, while demonstrating less success against more robust government agencies in India.
Frequently asked questions about the active threat to Siemens S7 Series PLCs
Multiple U.S. government agencies have issued a joint cybersecurity advisory warning of active threats targeting Siemens S7 Series programmable logic controllers (PLCs) across critical infrastructure sectors. The advisory, designated AA26-231A, was released on August 19, 2026, by the National Security Agency (NSA), the Cybersecurity and Infrastructure Security Agency (CISA), the Federal Bureau…
The push to designate AI as the next critical infrastructure sector
A new report advocates for the designation of artificial intelligence (AI) and its supporting infrastructure as the 17th critical infrastructure sector in the United States. This move would unlock federal resources and services for an industry increasingly vital to national and economic security, according to the report.
NSA, FBI warns of hackers using AI-generated tools in attacks on critical infrastructure technology
Federal agencies have issued an urgent warning regarding an active threat targeting critical infrastructure organizations, noting an evolution in attacker capabilities driven by the use of AI-generated exploit scripts. The National Security Agency (NSA) and the FBI, among other federal bodies, advised organizations to prioritize response efforts, particularly concerning programmable logic…
SilkParasite Threatens Central Asian Orgs With Flurry of RATs
A new spear-phishing campaign, dubbed "SilkParasite," has been observed targeting organizations in Central Asia. The campaign, attributed to a Chinese-nexus threat group with reported links to FamousSparrow, is notable for deploying a variety of Remote Access Trojans (RATs). This activity provides a window into the evolving geopolitical, technical, and strategic operational patterns of certain…
China-Linked Hacker Shows AI Capabilities in APAC Attack
A recent report indicates that a China-linked threat actor has demonstrated advanced artificial intelligence capabilities in a targeted attack against government agencies, likely within the Asia-Pacific (APAC) region, specifically Taiwan. This incident is being characterized as the first purported "near-autonomous" nation-state attack, suggesting a significant evolution in the sophistication…
UK Legal Regulator Raises AI Misuse Concerns
The Solicitors Regulation Authority (SRA), the regulatory body for the UK's legal sector, issued a warning notice on August 17, reminding solicitors and law firms of their obligations regarding the safe and responsible use of artificial intelligence. The SRA highlighted two primary areas of concern: AI-generated "hallucinations" in legal work and court submissions, and the potential for data…
Apple Screen Sharing Security, (Mon, Aug 17th)
A recent report has highlighted long-standing security characteristics of Apple's Screen Sharing feature, noting its reliance on the Virtual Network Computing (VNC) protocol. The report indicates that Apple's implementation, introduced with macOS 10.5 (Leopard) approximately two decades ago, largely retained the fundamental nature of VNC, which is described as a simple, unencrypted protocol…
Police bust cybercrime ring accused of stealing €30 million in four-day spree
An international law enforcement operation has dismantled a cybercrime ring accused of stealing €30 million from a German financial institution over a four-day period in late 2023. Authorities in Brazil arrested four individuals and are pursuing three additional suspects in Spain and Bulgaria.
Africa’s Cybersecurity Challenge Is Bigger Than Access to Technology
A recent report highlights that the primary cybersecurity challenge facing organizations in Africa extends beyond mere access to technology, according to Gopan Sivasankaran, Rapid7's Regional Director for the Middle East & Africa. The observation focuses on the expanding technological landscape across key nations including Egypt, Nigeria, South Africa, and Kenya, where organizations are…
Product showcase: ScamNet looks for warning signs in suspicious calls and shady links
Synaptrex Technologies has released ScamNet: Anti-Scam Suite, a consumer security application designed to detect and block various scams across phone calls, text messages, and websites. The application is available for iPhone, iPad, and Mac, with specific features varying by platform. While call protection is exclusive to iPhone, tools like Visual Intelligence are supported on both iPhone and…
SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 110
A new multi-stage Rust-based macOS information stealer, dubbed AmnesiaStealer, has been identified as capable of hijacking Chromium-based browsers to give attackers live control over victims' sessions. This malware is part of a broader trend of evolving cyber threats, which includes the Kimsuky APT group integrating artificial intelligence into its attack operations, from generating decoy…
APT36 Suspected in PATCHCORD Espionage Campaign Using Google Sheets C2
A newly discovered espionage campaign, dubbed PATCHCORD, has been observed targeting Afghan telecommunications providers and critical infrastructure organizations in South Asia. Security researchers at Acronis identified a custom C/C++ backdoor, PATCHCORD, being delivered through highly specific lures, including fake VPN installers designed to impersonate legitimate tools from Afghan Telecom…
Hackers exploit macOS Screen Sharing flaw to deploy Monero miner
The Netherlands National Cyber Security Centre (NCSC) has issued a warning regarding active exploitation of a macOS authentication bypass vulnerability, identified as CVE-2026-65400. This vulnerability affects macOS Screen Sharing, a built-in feature that enables remote desktop control via the VNC protocol on TCP port 5900.
If the Markets Reject OpenAI and Anthropic, the US Should Nationalize Them
OpenAI and Anthropic, two prominent artificial intelligence development companies, are facing market headwinds that could challenge their long-term financial viability, leading some observers to suggest their potential nationalization if they fail as private enterprises. Both companies were founded by AI developers who expressed concerns about the unchecked development of AI by large…
APT group HoneyMyte upgrades CoolClient: the backdoor gets a kernel-level Windows rootkit
A sophisticated backdoor known as CoolClient, attributed to the HoneyMyte APT group (also referred to as Mustang Panda), has undergone a significant evolution, now incorporating a signed kernel-mode driver to enhance its stealth capabilities. This updated variant has been observed in cyber-espionage campaigns targeting organizations across Asia, specifically in Pakistan, Mongolia, and Myanmar,…
Ukrainian police raid 94 fraudulent call centers, seize $2 million
Ukrainian law enforcement agencies have dismantled 94 fraudulent call centers across the country in a large-scale operation that involved over 400 searches and resulted in the seizure of approximately $2 million in various currencies and assets. The raids targeted operations engaged in a range of scams, including impersonating bank employees, offering fake investment opportunities, and…
Researchers Link 'Jewelbug' Chinese APT to Hack-for-Hire Operations
A threat group known as Jewelbug, previously associated with Chinese state-sponsored cyber espionage, has been linked to hack-for-hire operations and financially motivated cryptocurrency fraud campaigns. Researchers from Broadcom’s Threat Hunter Team, including experts from Symantec and Carbon Black, published a report on August 13 detailing how Jewelbug uses shared infrastructure for both…
US Authorizes Private Cyber Firms to Hack Transnational Criminal Networks
The U.S. government has formally authorized private cybersecurity firms to conduct offensive cyber operations against transnational criminal networks, acting under government direction and oversight. President Trump signed a national security memorandum on August 13, establishing a program to leverage the private sector's capabilities in combating cybercrime.
White House authorizes private US companies to hack foreign criminal networks
The White House has authorized private U.S. companies to conduct offensive cyber operations against foreign criminal networks, under the direct control and oversight of the U.S. government. President Trump signed a National Security Presidential Memorandum on August 12, allowing vetted private entities to engage in such activities.
White House taps security firms for offensive hack-back operations
The White House has initiated a new program that will allow private security firms to apply for approval to conduct offensive cyber operations against foreign cybercrime organizations. A national security presidential memorandum (NSPM), signed by President Donald Trump on Wednesday, directs the National Coordination Center (NCC) to establish this framework.
Attackers exploit critical SharePoint flaw after PoC goes public (CVE-2026-55040)
Attackers are actively exploiting a critical vulnerability in Microsoft SharePoint, tracked as CVE-2026-55040, following the public release of proof-of-concept (PoC) exploit code. The flaw, which allows for authentication bypass and impersonation, was addressed by Microsoft in its July 2026 Patch Tuesday updates.
Separating AI’s Technological Problems from Its Capitalism Problems
The rapid advancement of artificial intelligence (AI) is creating a societal transformation comparable to the Industrial Revolution, yet public distrust in AI is widespread, with many Americans believing it is progressing too quickly and will negatively impact society. This confluence of technological revolution and public apprehension necessitates a clear distinction between the inherent…
'Jewelbug' APT Balances State Espionage & Cryptocurrency Theft
Researchers have reported the activities of an Advanced Persistent Threat (APT) group dubbed "Jewelbug," which appears to be engaging in a dual operational model. This group has been observed conducting both state-sponsored cyber espionage activities and financially motivated cryptocurrency theft. The unusual aspect of this operation, as highlighted by the researchers, is that both types of…
Wireshark 4.6.8 patches 28 security bugs, nine in file parsers
Wireshark version 4.6.8 has been released, addressing a total of 28 security vulnerabilities within the popular network protocol analyzer. Nine of these critical flaws are located in file parsers, meaning they can be triggered simply by opening a specially crafted capture file without any network interaction.
Researchers observe first ‘near-autonomous’ AI attack on government target in Taiwan
Cybersecurity researchers have identified what they describe as the first "near-autonomous" AI-powered cyberattack targeting a government entity, specifically the Taiwanese government. The attack, which utilized open-source AI models, resulted in the exfiltration of over 2,500 personnel records and other data.
NIST Seeks Public Input on AI-Ready NVD Modernization
The U.S. National Institute of Standards and Technology (NIST) has initiated a public consultation to modernize its National Vulnerability Database (NVD), aiming to integrate artificial intelligence (AI) and automation workflows. This effort, announced in a Request for Information (RFI) published in the Federal Register on August 12, seeks to adapt the NVD to a cybersecurity landscape…
Sandworm-Linked UAC-0145 Uses Fake Job Interviews to Push VPN That Can Run Commands
The Computer Emergency Response Team of Ukraine (CERT-UA) has reported a new social engineering campaign attributed to Russian nation-state threat actors. The campaign, tracked by CERT-UA as UAC-0145, a subgroup of Sandworm (also known as APT44), targets IT workers in Ukraine through fake job interviews. The objective is to trick victims into installing malicious software disguised as a VPN…
US and South Korea warn of Gunra ransomware targeting govt agencies
Government agencies and critical infrastructure organizations globally are being urged by U.S. federal agencies and South Korea's National Policy Agency to bolster their defenses against Gunra ransomware attacks. A joint advisory issued Monday, August 11, 2026, details that the Gunra ransomware group, which first appeared in April 2025, utilizes a variant of malware based on the Conti…
Coruna, DarkSword iOS Exploits Proliferate Globally
Reports indicate a significant proliferation of sophisticated iPhone exploit chains, specifically "Coruna" and "DarkSword," which were previously understood to be the exclusive domain of nation-state actors. These advanced iOS exploits are now reportedly being adopted and utilized by organized cybercrime groups on a global scale, marking a notable shift in the landscape of mobile device threats.
Metabase zero-day exploited to access Framework customer data
Framework, a San Francisco-based laptop manufacturer, has confirmed a data breach stemming from a zero-day vulnerability in the Metabase business intelligence service. The incident led to unauthorized access to customer names, email addresses, phone numbers, physical addresses, and login IP addresses. Framework clarified that payment information and order records were not compromised.
How to report an AI Act violation in the EU
The European Union's AI Act, a landmark legal framework for artificial intelligence systems, entered its enforcement phase on August 2, 2026. This legislation aims to establish common rules for AI systems used or sold within the EU, balancing innovation with the protection of fundamental rights and safety. The European Commission's AI Office, in conjunction with national authorities, is now…
SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 109
A critical zero-day vulnerability in Metabase, an open-source business intelligence platform, has been actively exploited in the wild, potentially granting attackers administrative access and exposing sensitive data. The flaw, which was publicly disclosed on August 8, 2026, allows for unauthorized access to the platform's backend.
Security Affairs newsletter Round 589 by Pierluigi Paganini – INTERNATIONAL EDITION
Palo Alto Networks is currently undergoing a cybersecurity review in China, a development that coincides with escalating technological tensions between the two nations. The specifics of the review, including its scope and duration, have not been publicly detailed by either Palo Alto Networks or Chinese authorities.
Water utilities group partners with DEF CON offshoot for Water Watch Center
The National Rural Water Association (NRWA) has announced a new initiative, the Water Watch Center (WWC), aimed at bolstering the cybersecurity defenses of small, often underfunded, water and wastewater systems across the United States. This program is a collaborative effort with DEF CON Franklin, an organization that emerged two years ago from veterans of the DEF CON security conference, and…