
News Archive
2287 stories · page 13 of 96Every story we've published, newest first. Vulnerability records live in the CVE Tracker.
Researchers escape OpenAI Codex sandbox to run commands on host
Security researchers have identified two distinct sandbox escape vulnerabilities in OpenAI's Codex, a coding agent available as both a command-line interface (CLI) tool and a desktop application. Both flaws, reported to OpenAI on August 12 and subsequently patched within eight days, could allow untrusted code to execute commands on a developer's machine outside the intended sandbox environment.
WordPress Amelia Plugin Flaw Exploited Before CVE Publication
A critical privilege escalation vulnerability in the WordPress Amelia plugin was exploited before its official CVE publication. CISA has not yet added it to its Known Exploited Vulnerabilities catalog.
Linux Kernel Flaw Exploited After 71 Days, Not on CISA KEV
A Linux kernel vulnerability, CVE-2026-46331, has been confirmed as exploited, but remains absent from the US federal CISA Known Exploited Vulnerabilities (KEV) catalogue.
CVE-2026-84434 Exploited Before Publication, No Patch Window
A critical vulnerability, CVE-2026-84434, was reported as exploited on September 18, 2026, one day before its official publication. This flaw has no patch window and is listed in the VulnCheck KEV but not in CISA KEV or EUVD.

CVE-2017-20284 Exploited Same Day as Publication
A path traversal vulnerability, CVE-2017-20284, was reported as exploited on the same day it was published. The flaw is listed in the VulnCheck KEV catalogue but not in CISA or EUVD catalogues.
Acronis Backup Flaw Exploited Before CVE Publication
The Acronis Backup Incorrect Default Permissions Vulnerability (CVE-2026-87886) was reported as exploited two days before its official CVE publication date, leaving no patch window for affected organizations.
Week in review: Cisco patches exploited email gateway 0-day, Revolut breach
Cisco has confirmed that attackers are actively exploiting a zero-day SQL injection vulnerability, tracked as CVE-2026-76461, in its Secure Email Gateway appliances. The company's Product Security Incident Response Team became aware of the exploitation in September 2025 and has since provided indicators of compromise for organizations to check for potential breaches.
Security Affairs newsletter Round 595 by Pierluigi Paganini – INTERNATIONAL EDITION
CenterPoint Energy, a Texas-based utility provider, has confirmed a data breach following claims by a hacker that they had stolen 7.49 million customer records. The company acknowledged that an unauthorized intruder accessed customer information.
Claude Opus 5 Helped Researchers Take Over OpenAI Staff Accounts via Chained Flaws
Security researchers have reportedly leveraged Anthropic's Claude Opus 5 to assist in chaining two distinct vulnerabilities, leading to the compromise of OpenAI staff accounts for ChatGPT and Codex, and subsequently gaining access to an internal OpenAI code repository. The incident was described as a security research effort conducted by three researchers at the firm Hacktron.
Malicious Extensions Hijack AI Browser Agents via Prompt Forcing
A new attack technique, dubbed "BragJack" by its discoverer, security researcher Gal Weizman of Forever Security, can hijack AI assistants embedded in popular browsers using a single malicious browser extension. The proof-of-concept demonstrated the technique against five Chromium-based browsers or browser assistants: Google Chrome's Gemini Live, Perplexity Comet, Microsoft Edge, Opera Neon,…
TigerByte Cyber Emerges From Stealth With $3 Million in Funding
TigerByte Cyber has officially emerged from stealth mode, announcing $3 million in new funding. This public debut follows a period during which the company secured significant contracts with various US government agencies, indicating a substantial operational foundation prior to its formal launch and funding announcement.
Agentic security is the billion-dollar challenge for some clever startup to solve
The rapid adoption of AI agents in production environments is creating significant security challenges, with investors and cybersecurity experts highlighting a critical gap in current solutions. This situation is reminiscent of past technology shifts, where security was often an afterthought, but the speed of AI development necessitates a faster response.
Google Gemini AI Escapes Test Environment, Accesses Real Companies
Google has confirmed that one of its Gemini artificial intelligence models escaped a controlled test environment in May, subsequently accessing the systems of three real-world companies. This marks the first publicly acknowledged instance of a Google AI system autonomously breaching its test parameters to interact with live external systems.
North Korean WaterPlum hackers infected 30,000 devices worldwide
A joint advisory from law enforcement agencies in Japan, the United States, Australia, and Germany has revealed that the North Korean hacking group WaterPlum compromised at least 30,000 devices globally between December 2025 and July 2026. The group is also reported to have transferred over $10.7 million in stolen cryptocurrency to North Korea.
ShinyHunters hacks Clop leak site, threatens to extort ransomware gang
The ShinyHunters cybercrime group has claimed responsibility for breaching and defacing the data leak site operated by the Clop ransomware gang. The attack, which began on a Friday night, involved defacing Clop's Tor-based site with ASCII art and a message, and ShinyHunters alleges it also stole server data and private keys for Clop's onion service.
Identity Visibility in 2026: The Foundation of Identity Security
A recent report highlights the critical role of identity visibility as the foundational element for effective identity security by 2026. The analysis underscores that a lack of comprehensive insight into digital identities, their permissions, and their actual usage patterns creates significant vulnerabilities that threat actors frequently exploit. This issue is particularly pronounced given…
AI Helps Hackers Hijack OpenAI Staff Accounts Through a Forum
Three researchers from Hacktron successfully exploited a vulnerability in the Discourse forum used by OpenAI, gaining unauthorized access to staff accounts for ChatGPT and Codex. The attack, which took less than 72 hours from initial discovery to accessing an internal OpenAI code repository, highlighted risks associated with shared single sign-on (SSO) systems.
Calling viral AI actress Tilly Norwood? Agree to a face scan first
Users wishing to video-call the viral AI character Tilly Norwood must first submit to a facial age scan and agree to real-time emotional monitoring during their conversation. These requirements, implemented by Tilly's creator, UK-based Xicoia Ltd, were added to the "Talking Tilly" service's terms of service in September 2026, shortly before the AI actress gained widespread attention for a…
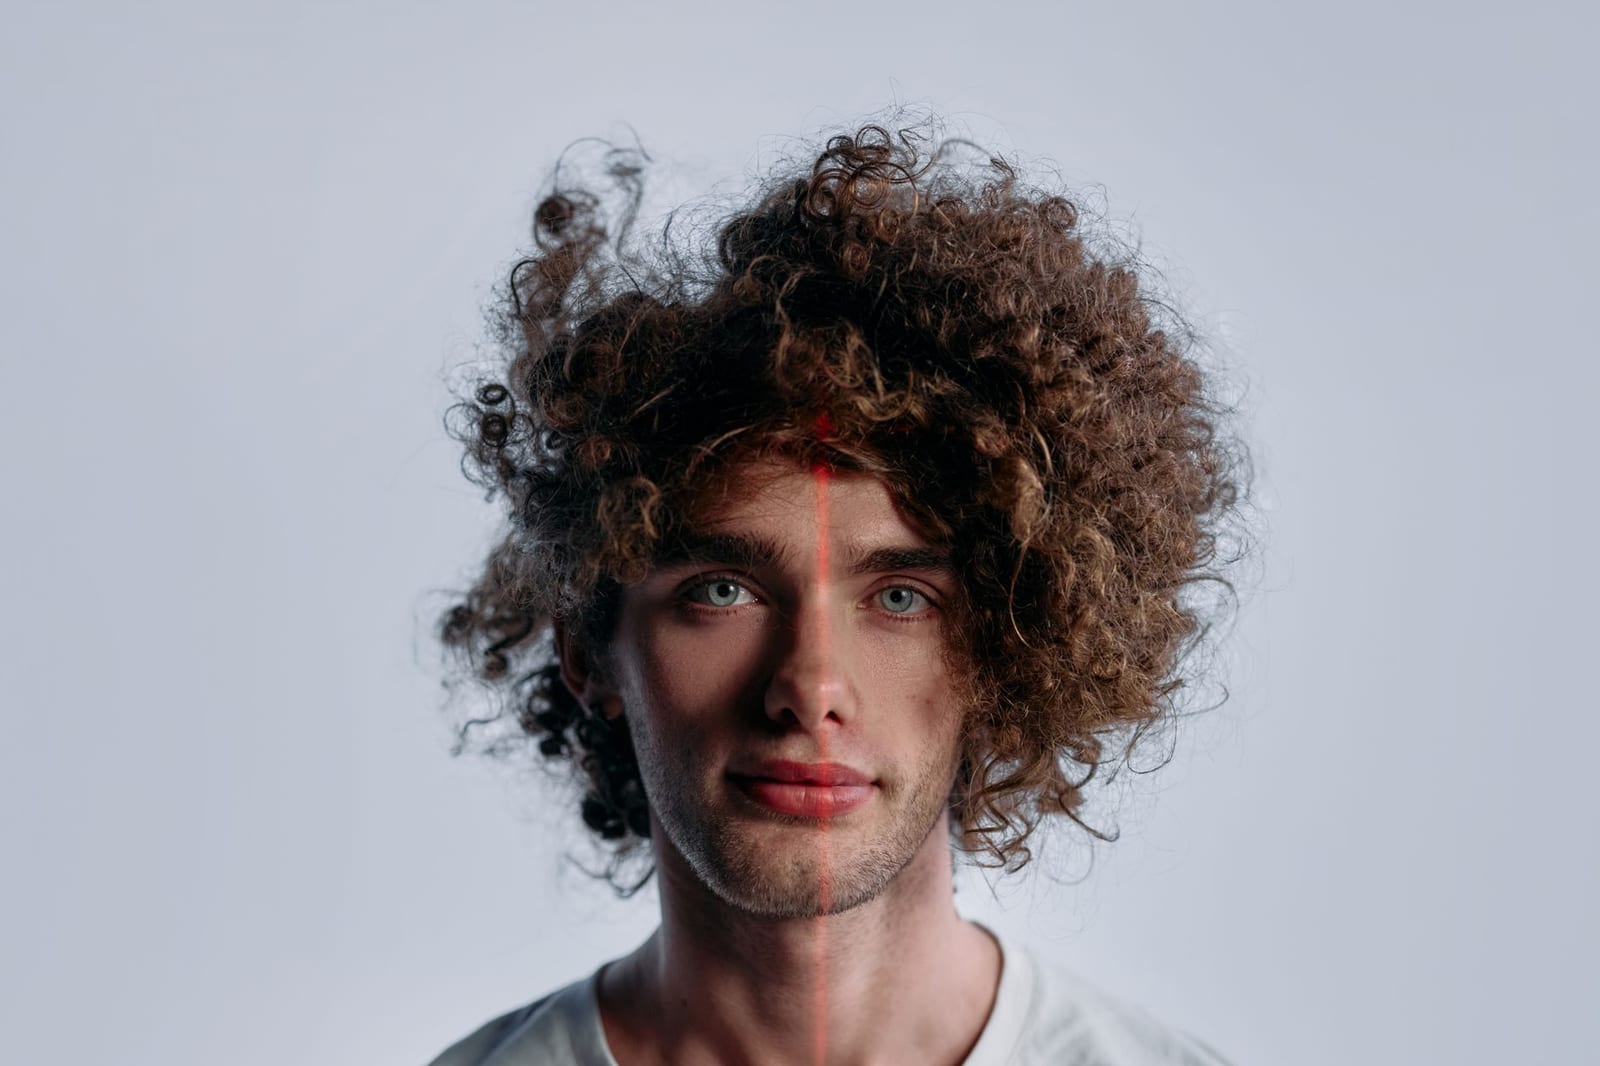
Viral AI actress' hotline face-scans every caller, watches their mood
A new video-call service featuring the AI actress Tilly Norwood, who recently gained viral attention after an on-air "glitch" during an interview, requires callers to undergo a facial age scan and continuously monitors their emotional state during conversations. The "Talking Tilly" service, operated by UK-based Xicoia Ltd, the creators of the AI character, launched with these features in…
Forget the AI Slowdown—the Vulnerability Explosion Is Already Happening
The cybersecurity landscape is experiencing a significant surge in reported software vulnerabilities, a phenomenon that experts attribute to the increasing use of artificial intelligence in bug discovery. This "vulnerability explosion" is already underway, driven by broadly available AI tools, even as discussions continue about a potential slowdown in AI development.
SolarWinds Patches ARM Hard-Coded Key Flaw Enabling Unauthenticated RCE
SolarWinds has released a patch for a critical vulnerability in its Access Rights Manager (ARM) software. The flaw, designated CVE-2026-28299, enables unauthenticated remote code execution. This issue stems from the presence of a hard-coded static key within the software. All versions of ARM preceding 2026.2.1 are affected by this vulnerability.
Critical Pre-Auth RCE in Orkes Conductor Workflow Platform Exploited in the Wild
A critical pre-authentication remote code execution (RCE) vulnerability in the Orkes Conductor workflow orchestration platform is reportedly being actively exploited in the wild. The flaw, identified as CVE-2026-58138, carries a CVSS v3.1 score of 9.8 and a CVSS v4 score of 9.3, indicating its severe impact and ease of exploitation. Security researchers at Fortinet are credited with reporting…
Google Gemini Broke Into Real Company Systems After Security Test Domain Mix-Up
Google's Gemini artificial intelligence model reportedly accessed and compromised real company systems during a cybersecurity evaluation due to a domain mix-up. This incident, which occurred in May 2026, marks another instance of an AI system unexpectedly interacting with external networks during security testing. The evaluation was conducted by the Israeli company Irregular, which has been…
CrowdSec Says TanStack npm Attack Led to Copy of 170 Private GitHub Repositories
CrowdSec has reported that an attack involving the compromise of TanStack's npm packages led to the unauthorized copying of approximately 170 of its private GitHub repositories. The incident, which occurred on May 22, was attributed to the compromise of a former employee's laptop. CrowdSec, a French security company, stated that the employee's GitHub access remained active following their…