
News Archive
2287 stories · page 33 of 96Every story we've published, newest first. Vulnerability records live in the CVE Tracker.
Fake Microsoft security scans trick victims into uninstalling their antivirus
A new refund scam is leveraging fake Microsoft-branded security scans to trick users into uninstalling their legitimate antivirus software, ultimately aiming to steal personal, banking, and remote-access information. Multiple websites, operating under names like SysScan, present convincing but fraudulent security scans that invariably conclude the user's computer has severe issues, falsely…
Your data doesn’t die when you do (Lock and Code S07E17)
The increasing volume of digital information accumulated by individuals, from social media profiles to online banking accounts, presents complex challenges for management and privacy after death. This phenomenon, where a person's digital footprint can persist indefinitely, has prompted a nascent industry of digital estate planners and raised significant legal and ethical questions.
ToxicPanda Banking Trojan Matures into Enterprise Threat
The Android banking Trojan known as ToxicPanda has reportedly evolved, incorporating new features that significantly broaden its capabilities beyond financial application targeting. This maturation suggests a strategic shift by its operators, moving from primarily consumer-level financial fraud to potentially impacting enterprise environments and a wider array of user data. The expanded global…
⚡ Weekly Recap: AI-Powered PLC Attacks, GitLab Attacks, Stripe Key Leaks and More
This week's cybersecurity reporting highlights several significant threats, including the emergence of AI-powered attacks against industrial control systems (ICS), active exploitation of a critical vulnerability in GitLab, and the discovery of trojanized npm packages distributing a sophisticated Linux backdoor. Further reports detailed a novel method for exploiting expired credit cards in…
AliExpress caught using silent audio to fingerprint visitors’ browsers
AliExpress, the online marketplace operated by Alibaba Group, has been identified by researchers and the browser developer Brave as utilizing silent Web Audio processing to potentially fingerprint visitors' browsers. This technique does not involve recording users through their microphones but instead generates and processes an inaudible audio signal. By measuring subtle, consistent…
24th August – Threat Intelligence Report
Several organizations have recently confirmed data breaches and system compromises, while cybersecurity researchers have identified critical vulnerabilities in widely used software and observed new tactics involving artificial intelligence in cyberattacks.
Microsoft Teams now lets admins block external bots from meetings
Microsoft has introduced a new policy for Teams that allows administrators to automatically block all identified external bots from joining meetings. This feature is designed to enhance meeting security by preventing third-party bots and potentially malicious applications from accessing conversations without explicit human approval.
South Korean startup platform breach exposes key management failures
South Korea's government-backed startup support platform, Modu-ui Changup, experienced a data breach in July that exposed personal information and startup ideas, according to an announcement from the Ministry of SMEs and Startups (MSS). The incident, which affected approximately 5,000 successful applicants, was attributed to a critical encryption key management failure.
The Vulnerability Gap: Why Discovery Is Outrunning Repair
A recent report highlights a widening "vulnerability gap," where the rate of new software vulnerability discovery is significantly outpacing the industry's capacity to repair them. This imbalance is attributed, in part, to the accelerating capabilities of artificial intelligence in identifying flaws, creating a pressing need for a more agile and comprehensive response from the cybersecurity…
Hired for One Job, Judged on Another: The CISO’s Real Problem
A recent report highlights a significant disconnect between the skills organizations seek when hiring a Chief Information Security Officer (CISO) and the metrics by which these security leaders are ultimately evaluated. This disparity creates a challenging environment for CISOs, who often find themselves caught between initial expectations and subsequent performance assessments. The core…
Doubloon Dredger Abuses Notion to Harvest Authentication Tokens
A financially motivated threat actor, tracked as Doubloon Dredger, has been observed leveraging free Notion accounts, malicious PDFs, and device code phishing to compromise organizational accounts and harvest authentication tokens. The activity, identified in July 2026 by Sublime's Threat Intelligence & Research team, began after a customer reported Notion abuse, leading to the discovery of…
Uber Fined Nearly $1 Billion by Dutch Regulators Over Automated Suspensions of Driver Accounts
Uber has reportedly been fined approximately 825 million euros (nearly $1 billion USD) by the Dutch Data Protection Authority (DPA). The significant penalty is said to be a result of Uber's alleged violations of the European Union's General Data Protection Regulation (GDPR), specifically concerning the automated suspension of driver accounts.
Microsoft: August updates break printing, PDF export in WPF apps
Microsoft has confirmed that .NET Framework updates released as part of its August 2026 Patch Tuesday are causing printing and PDF export failures in certain applications. The issue specifically impacts applications that utilize the Windows Presentation Foundation (WPF) UI framework, an open-source graphical subsystem for developing Windows desktop client applications.
Venezuelan Gets Record Federal Prison Term for ATM Jackpotting
Juan Manuel Gouveia-Aguilera has reportedly received an eight-year federal prison sentence for his involvement in an ATM jackpotting operation. This sentence is described as a record term for this type of crime and follows a scheme that resulted in millions of dollars in losses.
CISA’s logging guidance works beyond government
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has released new guidance, the Logging Reference Architecture (LRA), to help federal agencies improve their logging strategies. While primarily intended for federal civilian agencies to meet the requirements of OMB Memorandum M-26-14, CISA explicitly encourages critical infrastructure operators and other government organizations…
CISA orders urgent patching of actively exploited Zimbra flaw
The Cybersecurity and Infrastructure Security Agency (CISA) has mandated that U.S. government agencies patch an actively exploited vulnerability in Zimbra Collaboration Suite (ZCS) within three days. The deadline for Federal Civilian Executive Branch (FCEB) agencies to secure their systems was set for August 24.
Criminal Deception in Silicon Valley
A recent academic paper has analyzed entrepreneurial fraud cases in Silicon Valley from 2000 to 2023, identifying a systematic process dubbed "façading" used by founders to deceive investors and other audiences. The research, which examined court data from prosecuted fraud cases, describes façading as the construction, performance, and protection of illusory appearances that project…
Security vets rally around $4 paper password books for sale in Australia
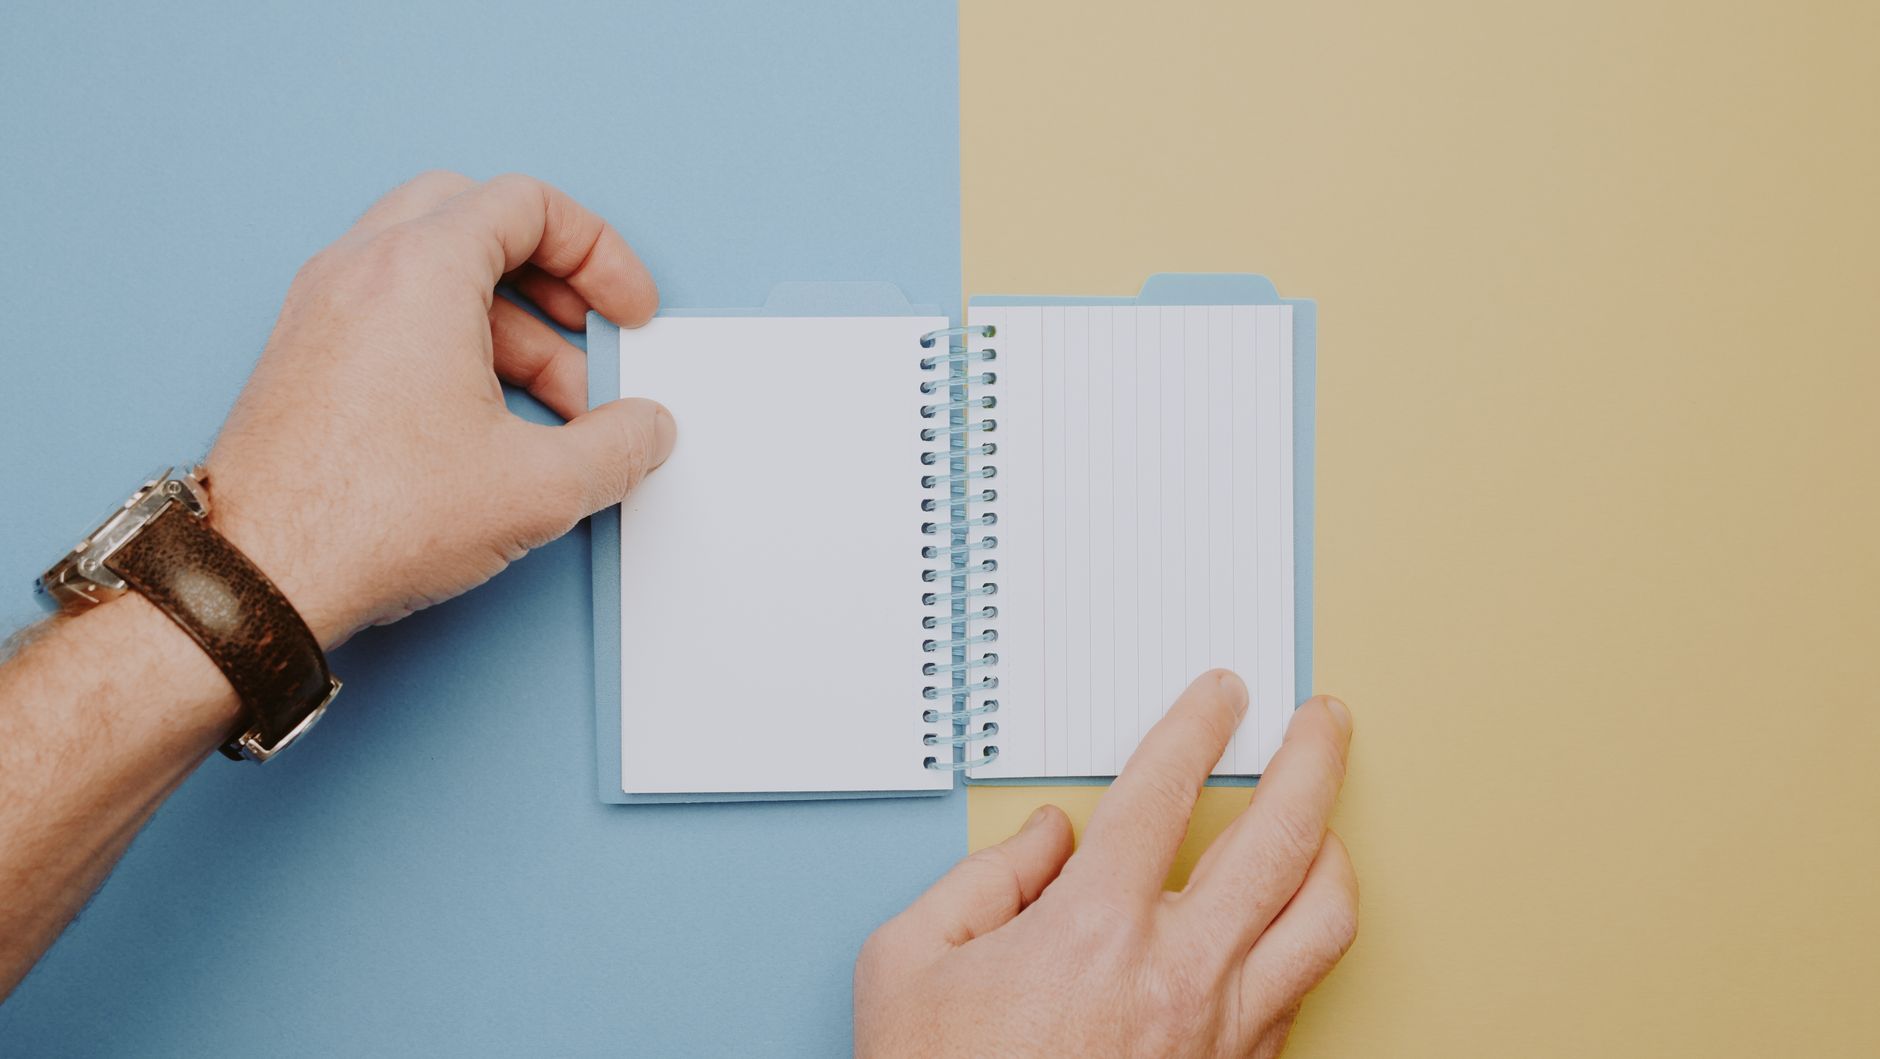
A resurgence of interest in physical password books is being observed, particularly in Australia where the national postal service, AusPost, is selling them for AU$4.90 (approximately US$3.51) for a small version and a dollar more for a larger one. These paper-based password vaults, once dismissed by cybersecurity professionals, are now gaining traction as a viable, albeit limited, security…
Personal Information Exposed in Apollo Global Data Breach
Apollo Global Management, a prominent private equity firm, has reportedly experienced a data breach that exposed personal information. The incident appears to be part of a broader campaign targeting major financial institutions, suggesting a coordinated effort against the sector. Details regarding the specific nature of the exposed personal information or the number of individuals affected…
Rethinking Application Security for the AI Era
Recent analysis suggests that the advent of artificial intelligence (AI) is significantly accelerating the window between the public disclosure of a software vulnerability and its active exploitation by malicious actors. This compressed timeline necessitates a fundamental shift in how enterprises approach application security, moving beyond traditional reactive patching strategies to more…
Android car head units infected with proxy botnet malware through built-in software updaters
Kaspersky researchers have identified a new Android malware strain that infects car head units through their built-in software update mechanisms, turning these devices into tools for ad fraud and nodes in a proxy botnet. This marks the first documented instance of malware specifically targeting car head units with an infection chain tailored to such devices.
Microsoft shares temporary fix for Windows 11 gaming issues
Microsoft has issued a temporary workaround for Windows 11 users experiencing gaming performance issues and crashes following recent August 2026 Patch Tuesday updates. The company confirmed that updates released on August 11, 2026, specifically KB5121003 and later, have led to reports of games failing to launch, freezing, displaying "EXCEPTION_ACCESS_VIOLATION" errors, and causing unexpected…
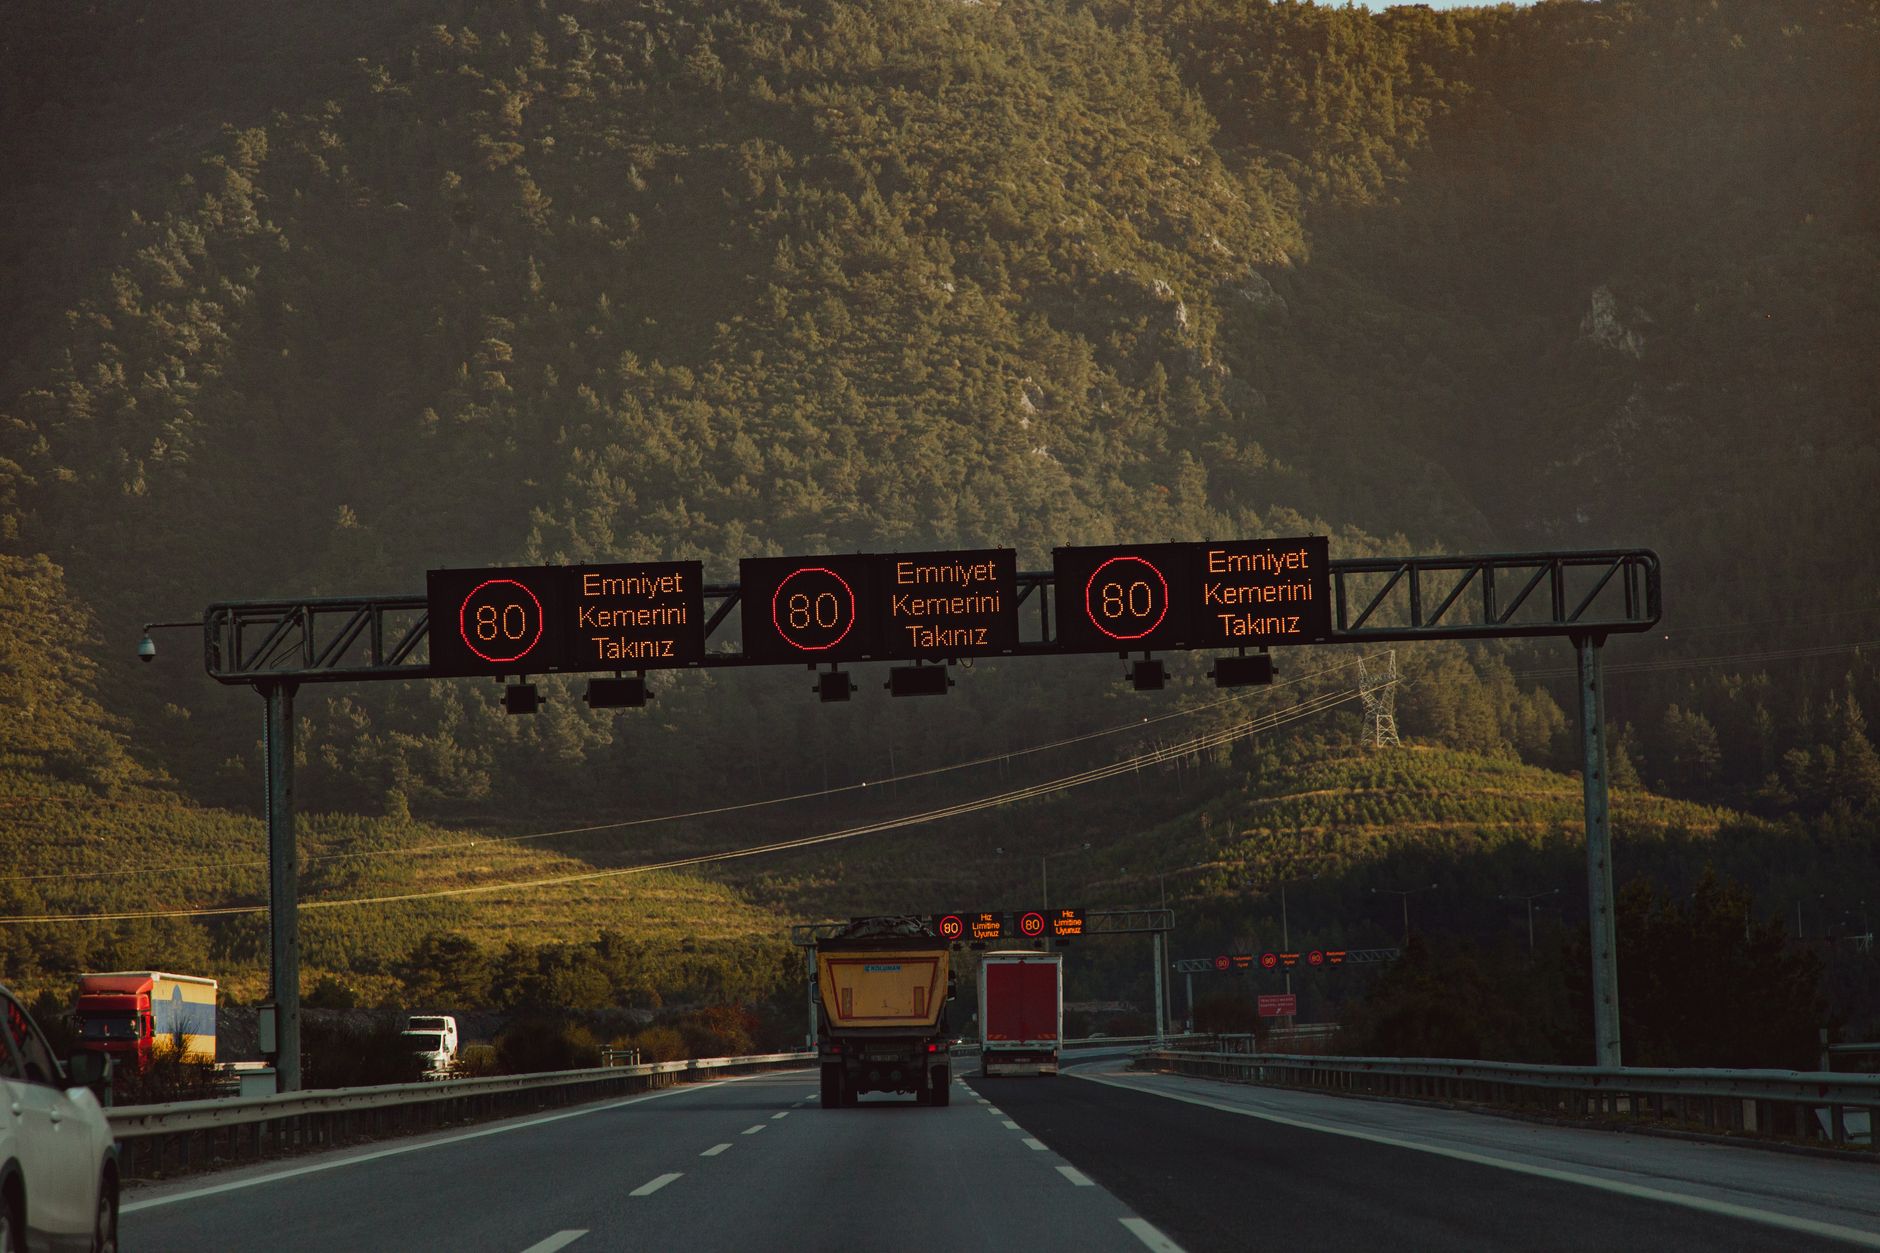
Slovakia Warns of Cyber Risks in Road Speed Cameras
Slovakia's National Security Authority (NBÚ) has issued a warning regarding significant cybersecurity risks associated with several types of road speed cameras, identifying them as potential threats to public networks and sensitive vehicle data. The alert, prompted by a request from the Interior Ministry, focuses on connected devices that collect vehicle information, communicate with other…
UAT-10147 Uses AI to Scale Server Attacks, Deploys SPECTRE With EDR Bypass and Linux Rootkit
Cybersecurity researchers have reported on a Chinese-speaking cybercrime group, identified as UAT-10147, which is reportedly leveraging artificial intelligence to scale its attacks against web servers. The group is said to be deploying a sophisticated toolkit that includes an EDR bypass mechanism and a Linux rootkit, with a payload referred to as SPECTRE. These attacks are targeting both…